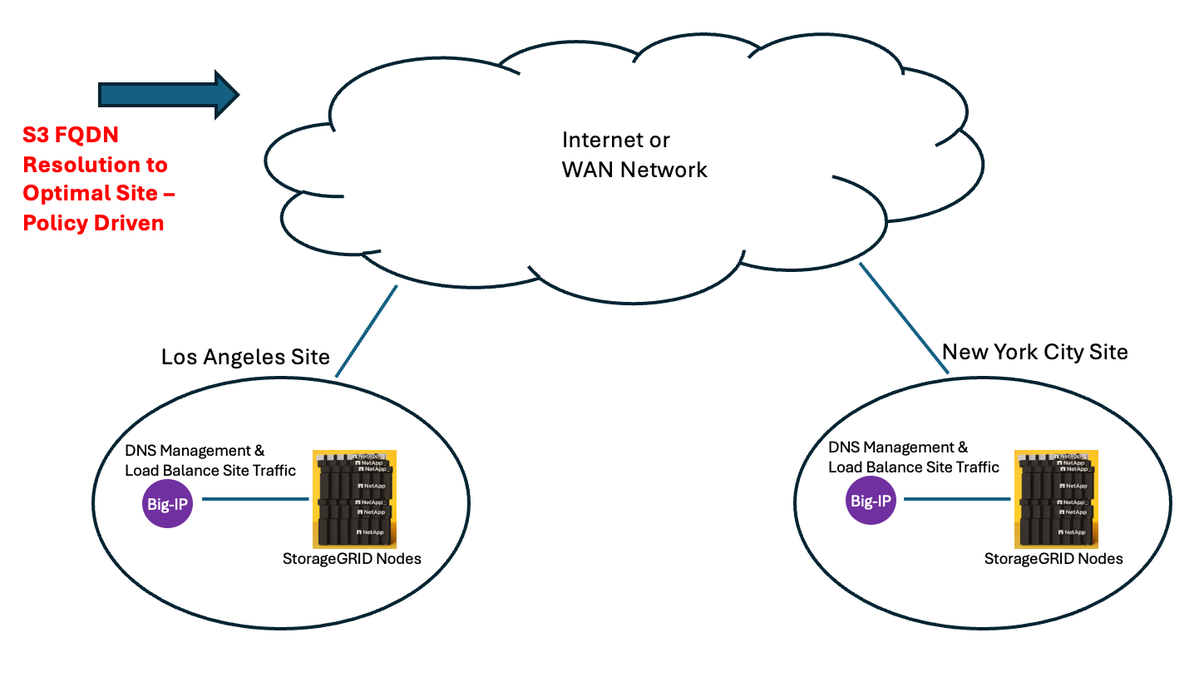
Multi-site StorageGRID has to decide which site an S3 transaction lands on. Steve Gorman on F5 BIG-IP DNS steering across active-active HA groups by probing, ratio, or topology, written up on the NetApp community. #NetAppINSIGHT
https://t.co/nS6HRmEF7c
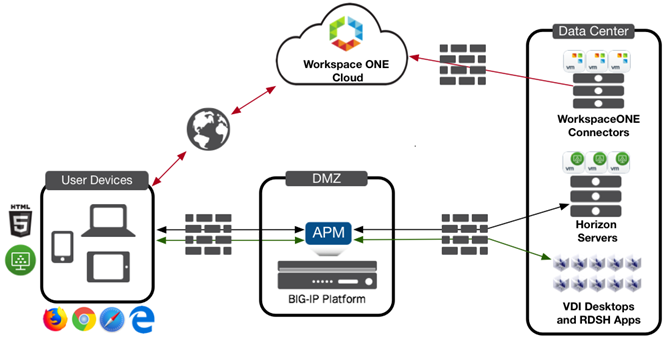
Workspace ONE Access as the SAML identity provider, F5 BIG-IP as the service provider, Horizon 23.12 ESB behind it, one gateway to secure. Matt Mabis has the step by step, including the PCoIP and Blast proxy path.
https://t.co/e2JIRO1vki
#OmnissaONE#OmnissaCommunity
The data worth giving an LLM is usually already on-prem. Steve Gorman SnapMirrors NetApp volumes into a VPC and binds them to Amazon Bedrock over F5 Distributed Cloud Services, with AD permissions carried into the RAG answers. #NetAppINSIGHT
https://t.co/zOSH8drklv
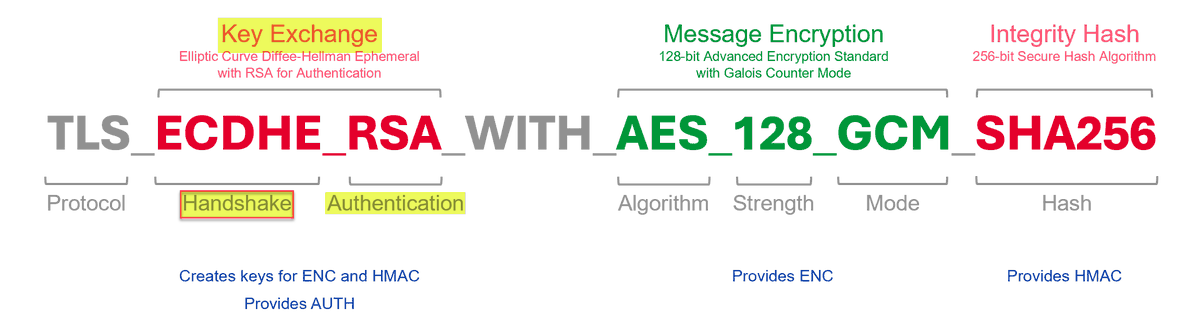
Harvest now, decrypt later needs a network position and patience. Steve Gorman terminates S3 to NetApp StorageGRID and ONTAP with post-quantum algorithms on F5 BIG-IP, plus a client compatibility table worth reading. #NetAppINSIGHT
https://t.co/EPtH9CTyz5
Omnissa Unified Access Gateway (UAG) scales horizontally, so a Horizon deployment that grows across pods or data centers has load balancing to design alongside it.
https://t.co/fvrWjVunfF
#OmnissaONE#OmnissaCommunity
S3 custom metadata arrives as an HTTP header and usually goes unread. Steve Gorman reads it with F5 iRules and steers writes to the right StorageGRID nodes, so an SSD-latency workload lands on SSD. #NetAppINSIGHT
https://t.co/b3Jb5JQXZx
Standing up NetApp StorageGRID behind F5 BIG-IP: three-node pool, HTTP health checks, content synced so any node serves any read. Steve Gorman on the setup. #NetAppINSIGHT
https://t.co/UAfPZAbD7Q
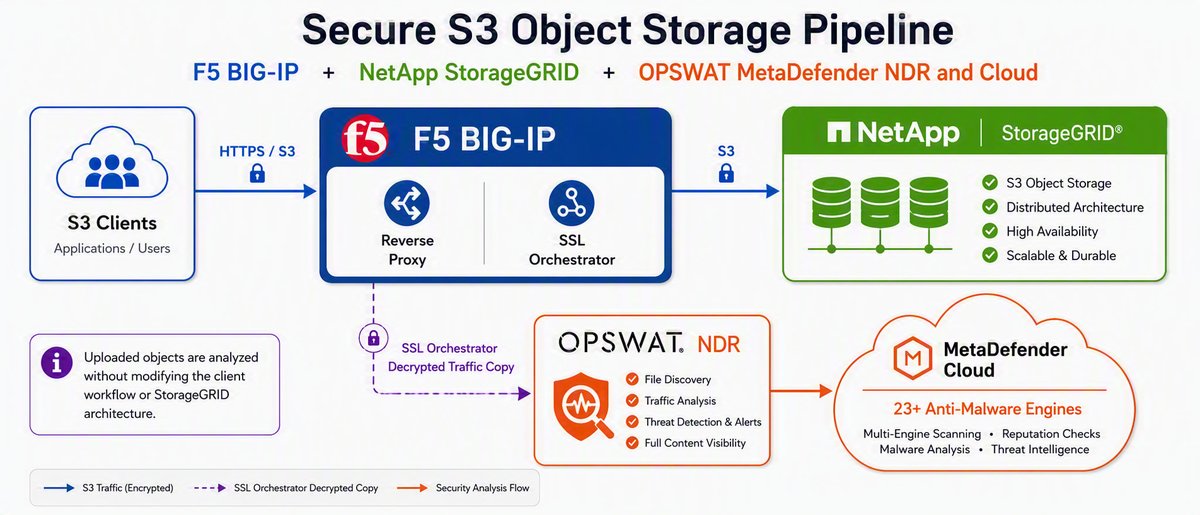
S3 uploads arrive over TLS, so nobody sees what lands in the bucket. Steve Gorman fronts NetApp StorageGRID with F5 BIG-IP SSL Orchestrator and mirrors the decrypted flow to OPSWAT MetaDefender NDR. Inspection beside the upload. #NetAppINSIGHT
https://t.co/qmyJqUFMsi
Four ways to put Omnissa Horizon behind F5 BIG-IP, each with its own config. Matt Mabis has templated all four in iApp v2.0.0: internal LTM, DMZ with Unified Access Gateways, and Zero Trust Access via AD or OAuth/JWT.
https://t.co/8QkC7JW4hk
#OmnissaONE#OmnissaCommunity
F5 Distributed Cloud enhances platform usability while respecting existing workflows.Our latest Load Balancer UX update reorganizes the configuration screen to better reflect a proxy framework, grouping foundational settings at the top for quicker access.
https://t.co/DDuGVQCNzD
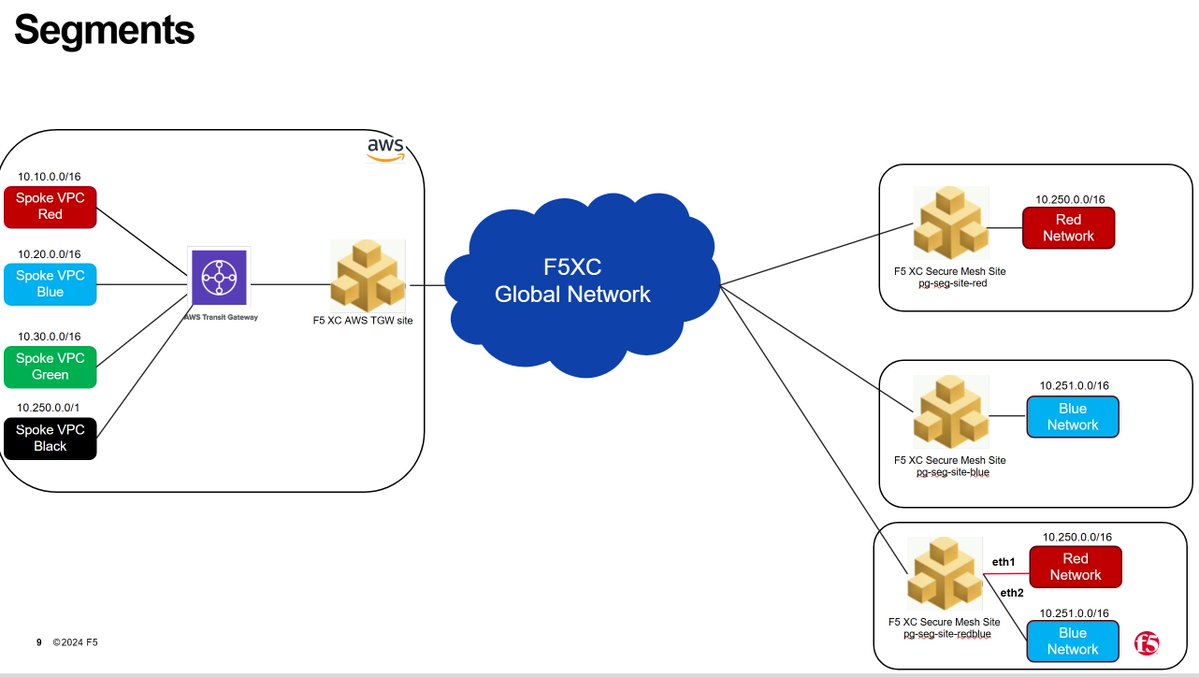
The F5 Distributed Cloud Multi-Site model transforms this landscape by deploying Customer Edge (CE) nodes at each site, enabling secure, optimized communication without traditional VPNs or MPLS circuits.
https://t.co/aWzJJDQXpU
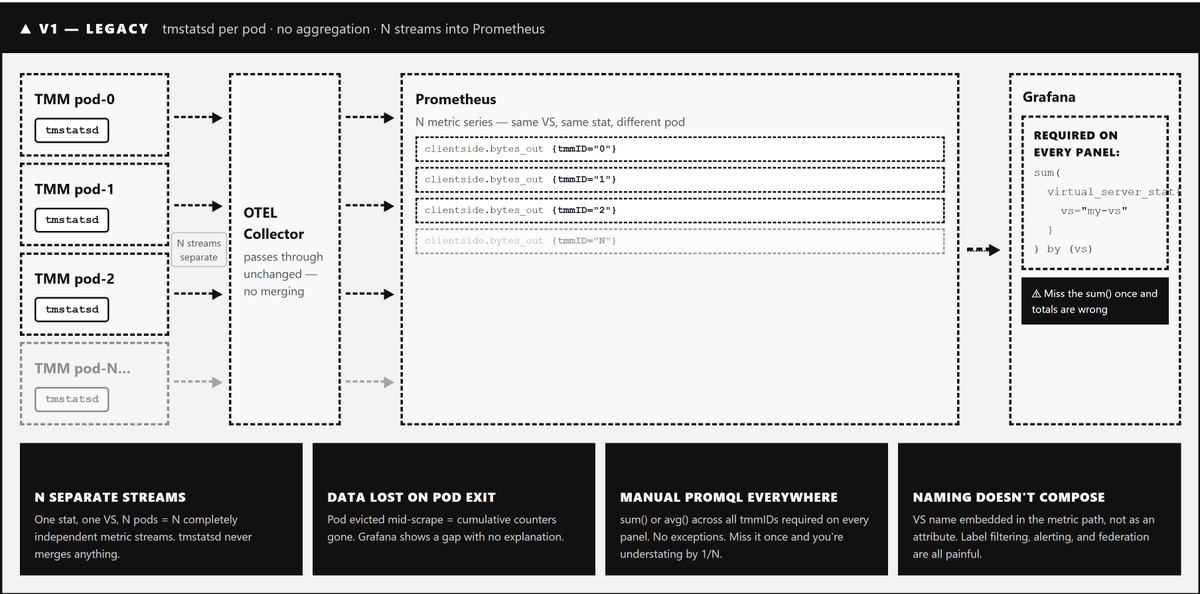
In cloud-native deployments, scattered telemetry from TMM pods can hinder visibility across your dataplane. F5’s TODA architecture addresses this with a model—TMM Scraper, Receiver, Observer, and Operator—that aggregates metrics for a unified view.
https://t.co/SA4Jm3lN1D
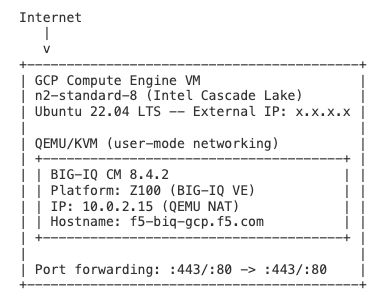
Running F5 BIG-IQ natively on Google Cloud Platform has been a challenge—until now. This solution leverages nested KVM virtualization on GCP’s Intel Cascade Lake CPUs, enabling a fully functional BIG-IQ VE instance with active licensing and full features.
https://t.co/TvjwJhTbmG
DNS is the backbone of seamless application delivery, yet it often goes unnoticed until issues arise. Leveraging solutions like F5 BIG-IP enhances DNS security with DNSSEC and optimizes performance through intelligent query handling.
https://t.co/uztcGIFiSu
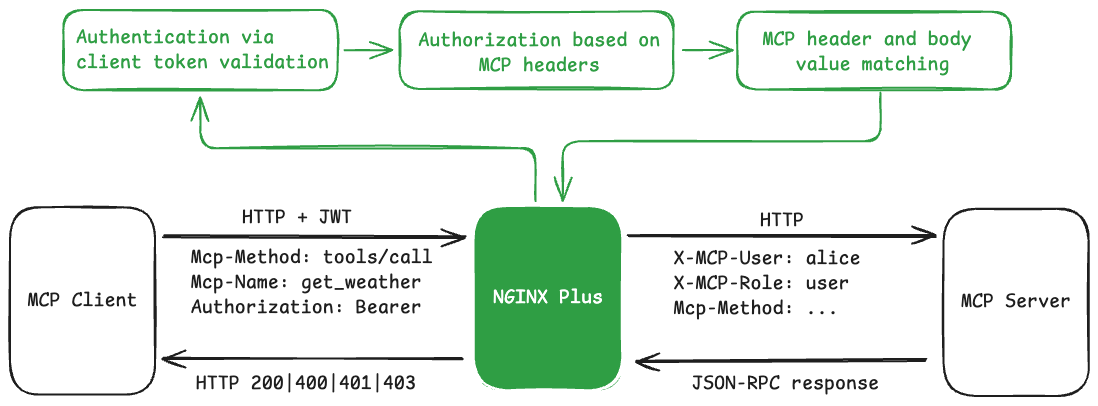
The 2026-07-28 MCP specification introduces new HTTP headers, Mcp-Method and Mcp-Name, enhancing client intent visibility in requests. Discover practical ways to implement robust security policies directly at the gateway.
https://t.co/NMKckngVqr
Learn how to configure the Office 365 URL Updater, create the Tenant Restrictions service, and test your setup to maintain secure and controlled access to critical resources.
https://t.co/OtCNsQdmGR
Effective post-quantum cryptography migration starts with one crucial step: inventory your cryptography. The Cryptography Bill of Materials (CBOM) provides a structured way to capture this complex landscape.
https://t.co/Md8AvMuxrX
Discover how proactive automation, health monitoring, and programmable infrastructure empower businesses to maintain uninterrupted operations and position for future growth.
https://t.co/IBoeUqANV8
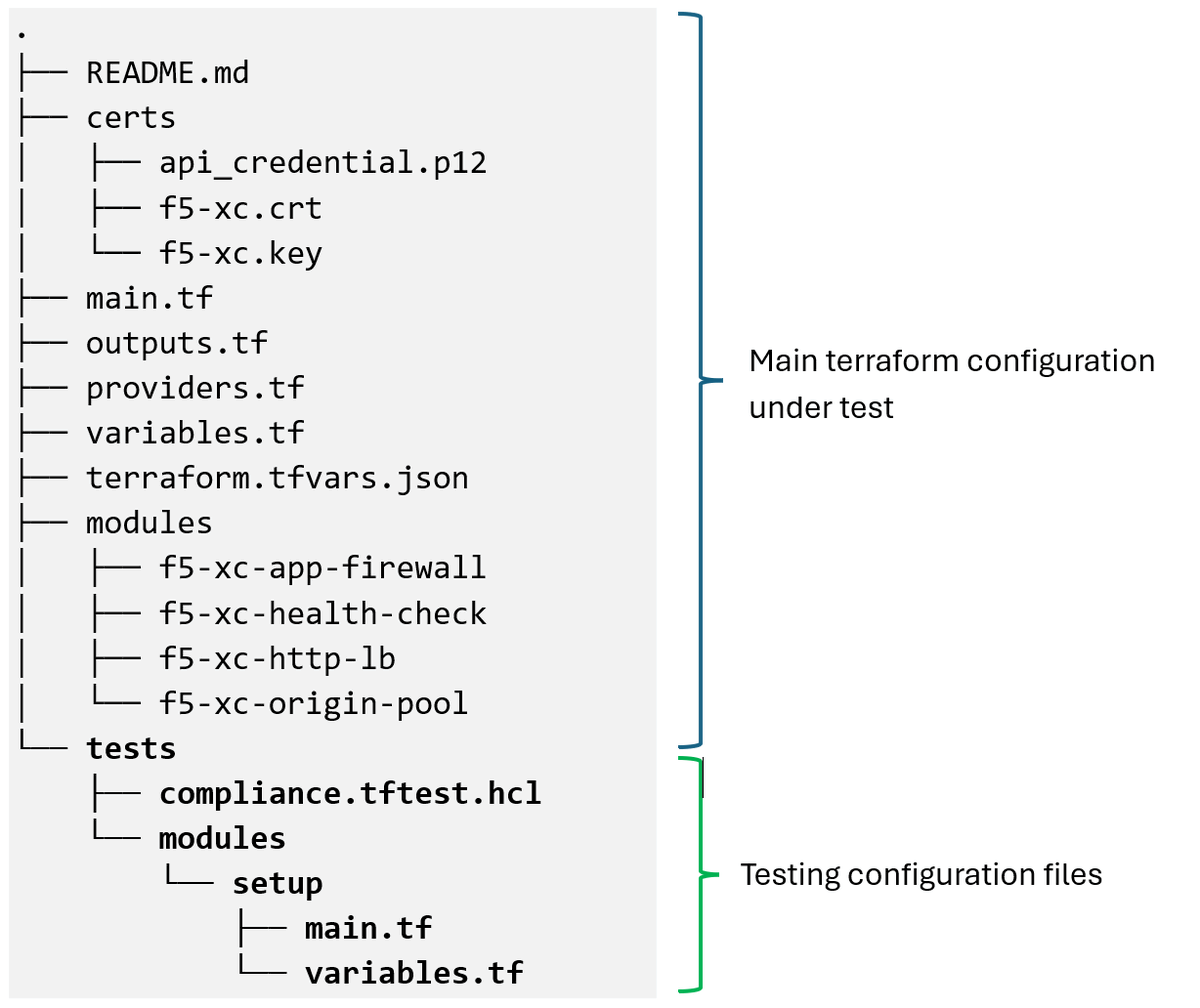
Explore how F5’s example for WAAP-protected HTTP applications leverages this framework to enforce compliance, security policies, and resource governance efficiently.
https://t.co/J52i5y03s7