A Long Day for Us at Falcon Feeds 🙏
On 23rd January 2024, 6 PM PST, our Twitter account was compromised by crypto scammers, even with MFA enabled. Unfortunately, we lost access and witnessed one of the largest scamming incidents we’ve ever experienced. The scammers managed to post nearly one tweet every minute, resulting in over 60+ fraudulent tweets every hour till 1:30 am PST on 24th January.
This incident comes after months of persistent, multi-vector attacks targeting us for exposing threat actors and their false claims. As challenging as this has been, we remain steadfast in our mission to shine a light on malicious activities.
After hours of collaboration with the X (formerly Twitter) team, we have successfully regained access to our account. We sincerely apologize for the alarming content posted during this period and the inconvenience caused to our followers. Rest assured, a detailed release on the incident, including a thorough analysis of the scammer group, will be coming soon.
We would also like to extend our heartfelt gratitude to the cybersecurity community for their swift support in spreading awareness and assisting us in recovering our account. Your help has been invaluable in mitigating the damage.
While this event has been embarrassing, it strengthens our resolve to continue exposing threat actors. Thank you for standing with us during this time. Stay tuned for our detailed blog and release in the coming days.
Thank You ❤️
@UK_Daniel_Card@vxunderground@vxdb@ich_rish99@rushibmehta@craiu@H4ckManac@deepwebkonek@DarkWebInformer@AlvieriD@Cyberknow20
@ToddAtLarge_
@Mudit__Gupta
@ZoomZoomZero
@SaifuddinAmri__
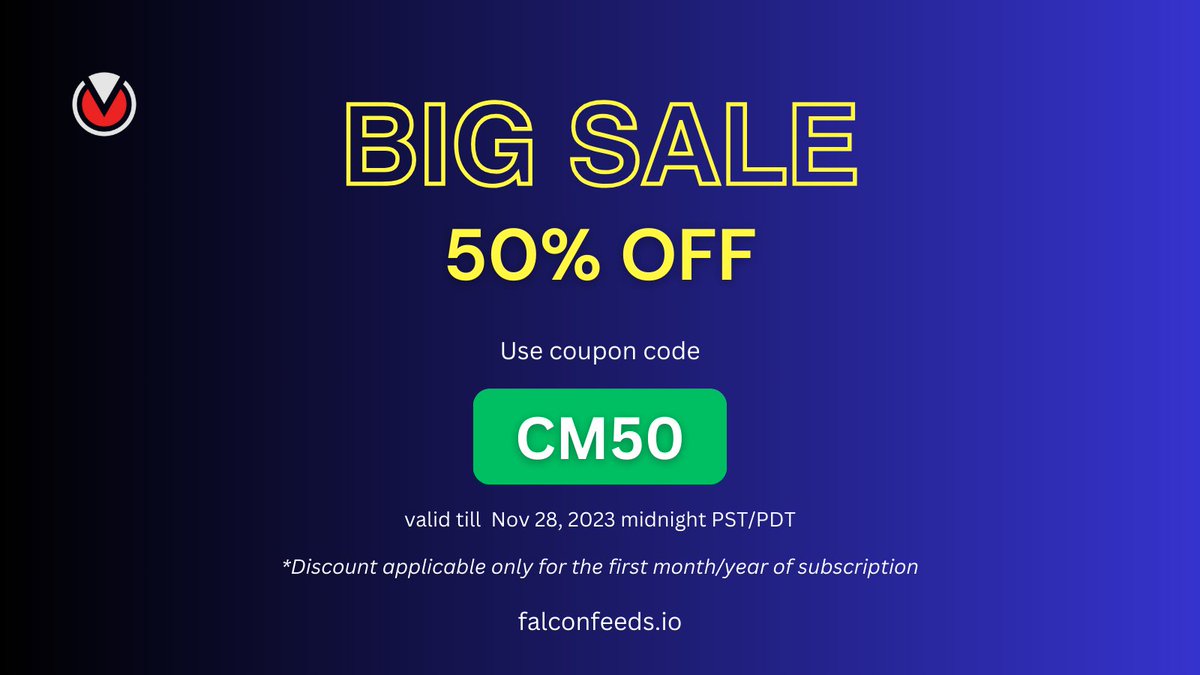
HURRY NOW!!! Get 50% discount on all plans for the 1st month/year of your subscription.
Use coupon code "CM50" to avail this offer while subscribing to https://t.co/aqk7mBsnvi
Valid only for the first 100 customers who redeem the coupon before Tuesday Nov 28th, midnight.
#cybermonday #falconfeedsio #threatintelligence #blackfriday #bigsale
Hurry!!! only for 1 day - 90% OFF on our Business Plan for the whole year!
Use coupon code “BF199” while purchasing the subscription to avail this Black Friday offer!
Offer available for new subscribers only for the first year of subscription, valid till Nov 21st end of day.
Buy now at https://t.co/h4tBtzcgX2
#Threatintelligence #Cybersecurity #Blackfriday #Darkweb
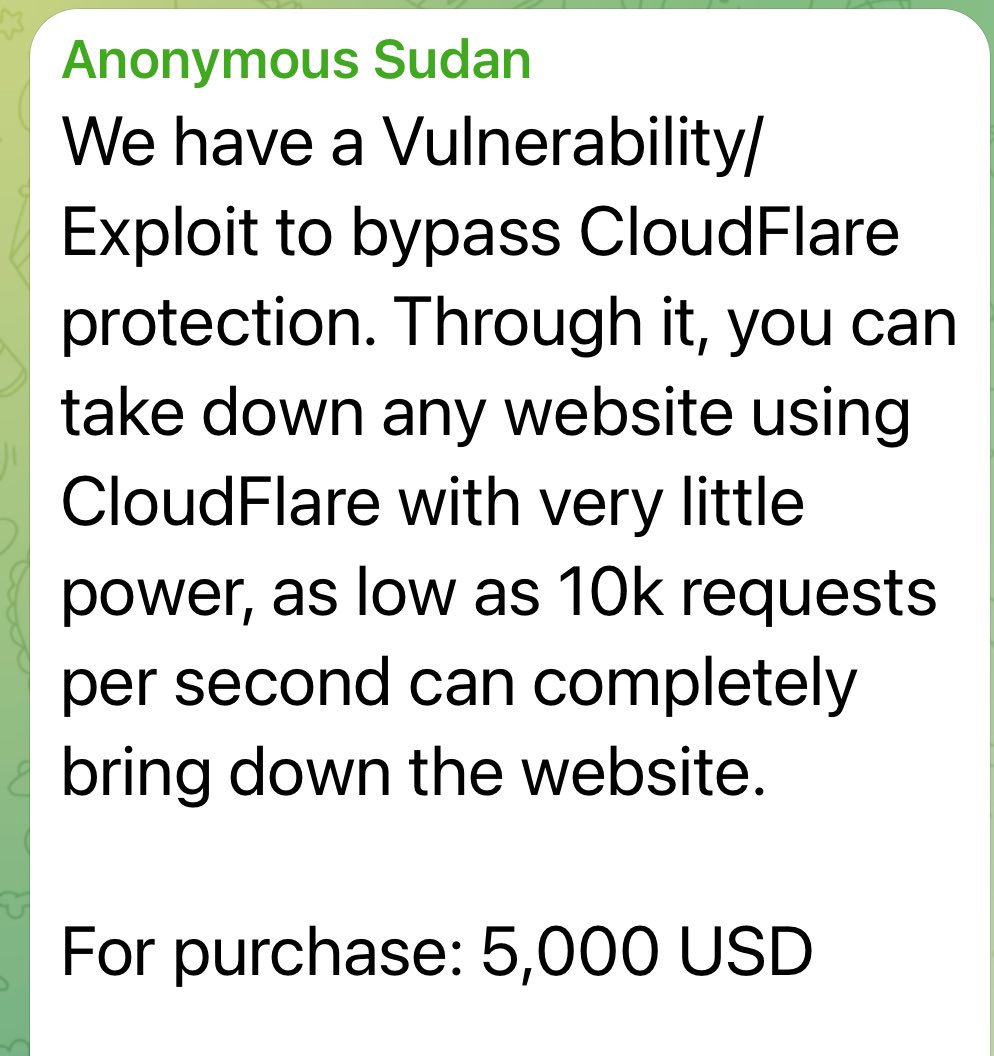
🚨 Threat Intelligence Update: Anonymous Sudan’s Claim on Cloudflare 🚨
Anonymous Sudan is taking its cyber campaign to a new level, claiming they’ve acquired a vulnerability that could bypass Cloudflare’s robust defenses. In an unexpected turn, they’re reportedly opting to sell this access, marking a strategic shift from their typical DDoS onslaughts.
This development could signify a change in tactics for the group, known for its relentless DDoS attacks, which often hit a wall against Cloudflare’s protective measures. The sale of such a vulnerability indicates a more calculated approach in their cyber warfare strategy.
Stay tuned as we continue to monitor the situation and assess the implications of this potential threat.
@Cloudflare
#CyberThreatIntelligence #Cloudflare #CyberSecurity #AnonymousSudan #DDoS
🚨 New Blog Alert! 🚨
“The Evolving Landscape of Cyber Warfare in the Israel-Palestine Conflict: A Comprehensive Analysis”
Delving deep into motives, methods, & consequences of cyber-attacks in the ongoing geopolitical crisis. Our research sheds light on industries & countries impacted by these conflicts. Stay informed!
Read the full Blog by @SahariyaMayank : https://t.co/p8JFS68OK9
#Cyberattack #Threatintel #threatintelligence #DDoS #IsraelPalestineConflict
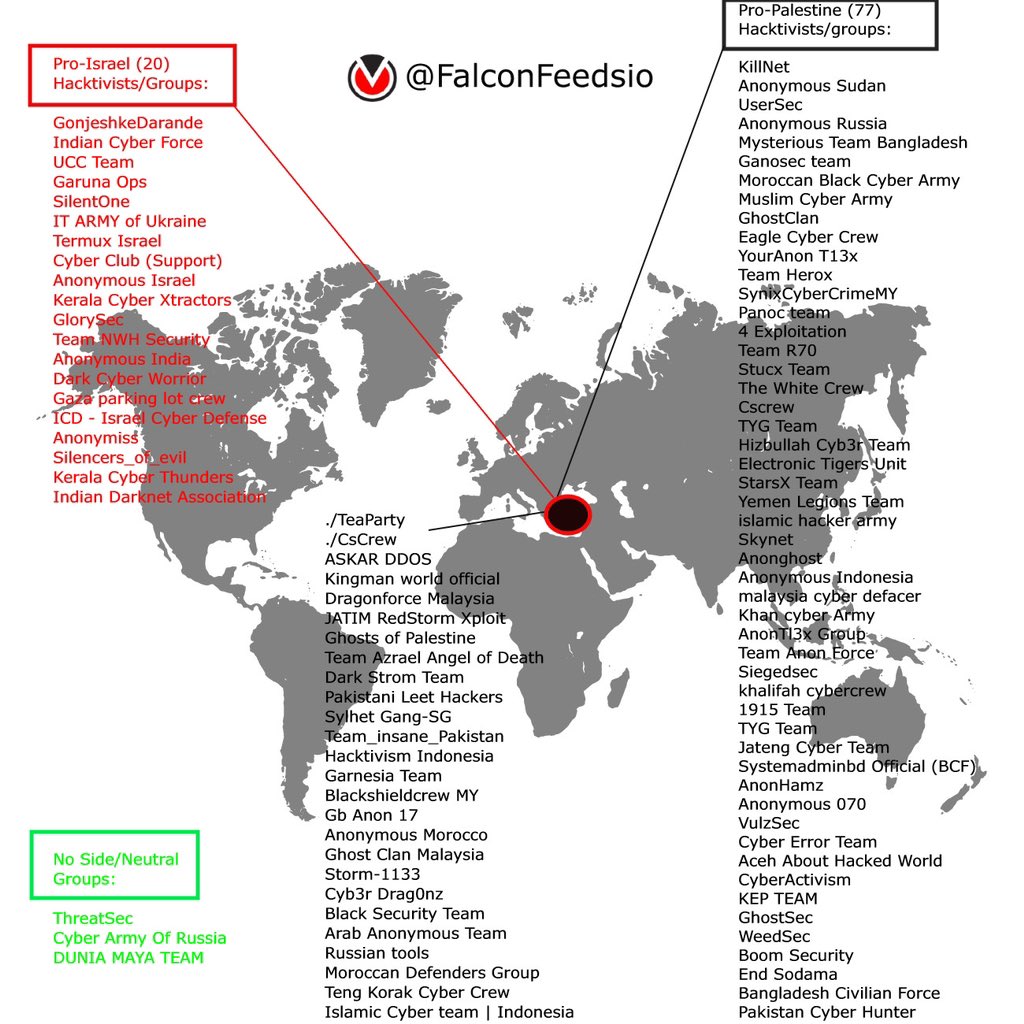
Tracking the Cyber Frontlines: Israel vs. Palestine 🌍🔍
We have identified 100 active groups participating in the ongoing cyber warfare between Israel and Palestine. Of these, 20 groups align with pro-Israel sentiments, 77 support the Palestinian side, and 3 remain neutral. We’re closely monitoring the activities of each of these entities. Stay tuned for an upcoming blog where we’ll delve deeper into our findings and continue to provide updates on these threat actors.🛡️💻🕊️
#Threatintel #Israel #Palestine #CTI #Threatintelligence #IsraelPalestineConflict
#Cyberwarefare
#Cyberattack
🚀 20,000 Followers Milestone! 🚀
Thank You all.
A year ago, we ignited Falcon Feeds with a dream: to democratize cybersecurity. Our mission was clear - make the elusive threat intelligence from the deep, dark, and open web accessible to not just a privileged few, but to every researcher and security professional out there. This journey began as a side project, but in just months, it transformed into our core pursuit, leading us to unveil our platform in June and subsequently, our premium version in September.
📈 By The Numbers:
•A thriving community of 20,000 on Twitter, including security experts, CISOs, practitioners, and even journalists.
•A diverse and global user base: from individual researchers, SMEs, to governments and large enterprises.
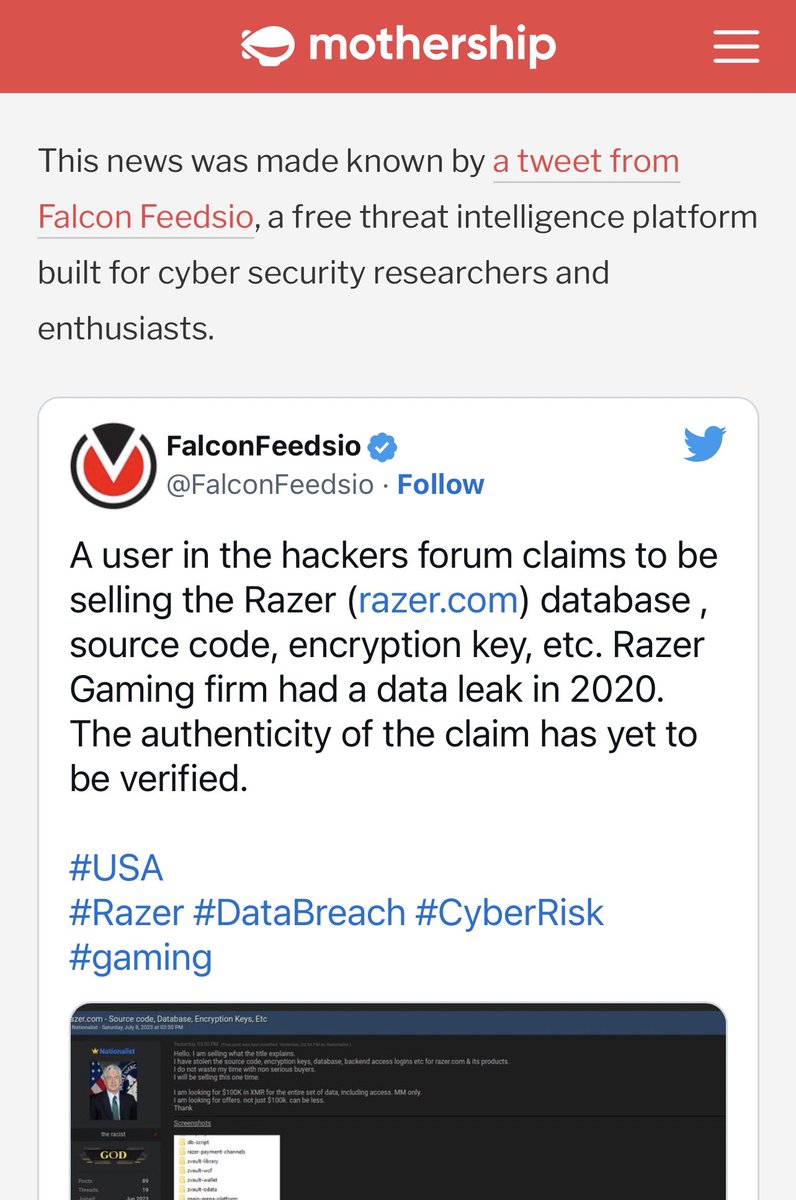
•Featured in over 100 media outlets, spanning 35 languages worldwide.
Our gratitude knows no bounds. To the media fraternity for amplifying our voice, and to every single follower and user for your trust - Thank you.
As we move forward, our commitment remains unwavering: to deliver tools and insights that fortify the global defense against cyber threats.
💡 Join Our Movement:
•Explore our platform: https://t.co/aqk7mBrPFK
•Stay updated on Twitter: https://t.co/UPa1yaW16B
#FalconFeeds #CyberSecurity
#Threatintelligence
🌍🛡️
Another DDoS attack on @FalconFeedsio - 233M requests!
@Cloudflare has successfully mitigated the attack.
We have been receiving threats from a malicious threat actor group Anonymous Sudan, and we think the latest attack has also been carried out by them.
#ddos#falconfeeds
🔍 Just published! Our in-depth research on #Cl0p Ransomware reveals tactics and attack vectors. Don’t miss our insights on how this notorious group operates.
Read the full blog : https://t.co/tixDBHs3zT
#CyberSecurity#ThreatIntelligence#InfoSec
🔍 Just published an in-depth research blog uncovering the truth about several malicious tools masquerading as GPT models. Our team delved into seven of these deceptive tools, exposing their true nature. Stay informed and check out the blog to learn more!
Read the full blog at
https://t.co/ZiptAJ4mPF
To track the threat actors visit : https://t.co/TbliHPsUn8
#AIsecurity
https://t.co/MG5DMBfAMn survived a massive DDoS attack today with 30 million requests! This is our 5th attack since launching less than 2 months ago. Monitoring threat actors is now more critical than ever as their tactics evolve constantly. #DDoS#Threatintel
Read the full story -
https://t.co/Q8zVxn7Ut0
📣 Calling all security professionals! 🔐👨💻
Check out https://t.co/sxvwwlqPX9, the threat intelligence platform to monitor security incidents, threat actors, and so much more. Sign up now!
#CyberSecurity#ThreatIntelligence#Cti#Threatintel#Ransomware
📣 Attention Twitter followers! 👋🏼🐦
🎯 We are actively monitoring NoName, a notorius pro-Russian threat group 🇷🇺🎯 They've targeted European countries and their banking & critical infrastructure 843 times! Track the threat actor and their platform Ddosia which lets users take part in their DDoS attacks.
🔒 Signup for Falcon Feeds: the exclusive threat intelligence platform. Sign up now at https://t.co/TbliHPsUn8 for FREE! 🚀
🌍 Stay informed, know their targets, industries, and countries affected. Join Falcon Feeds today! #Cybersecurity #ThreatIntelligence #Ddosia