A ClickFix case brought our team down a BabaDeda chain that led to an undocumented end: CNCMachineRMS, a 1.14 MB RAT with zero imports, every string built on the stack, and its own scripting language.
The full research + PDF report below. ⤵️
https://t.co/fUoh0ZoT3a
🧑🍳 Here’s a CyberChef recipe for decoding Tycoon2FA’s JavaScript obfuscated with invisible Unicode characters:
🔗 https://t.co/HYGBSoiFOZ
(Feel free to customise it as needed.)
🪝Tycoon2FA now uses invisible Unicode characters to encode #JavaScript in its #phishing landing page.
It uses the Halfwidth Hangul Filler to represent binary 0 and the Hangul Filler to represent binary 1. These bits are joined into a binary string, split into 8-bit chunks (bytes), and then converted into characters.
Samples of #Tycoon2FA Phishing Page:
cloloudaxis[.]ru - https://t.co/q87uc4pULz
kolivax[.]ru - https://t.co/9YmQ3WIBQs
#PhishingAlert #MailMarshal
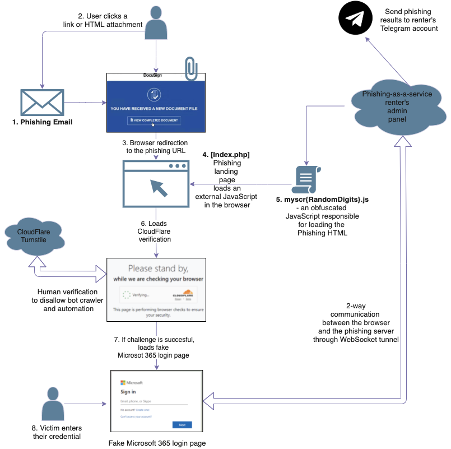
Why do cybercriminals love phishing-as-a-service platforms? 🎣🧑💻
Low barriers to entry, easy scaling, subscription-based models, easy evasion, and cheap prices are among the few main reasons.
Stop sophisticated - and unsophisticated - cybercriminals from gaining entry into your organization with simple but effective PaaS techniques: https://t.co/nb2rWJ6CCf
🚨 Watering-hole attack on Advanced IP Scanner! Users searching for this tool may end up downloading a backdoored version from hxxps://advancced-ip-scanner[.]com. The setup file is compromised with CobaltStrike. [1/2]
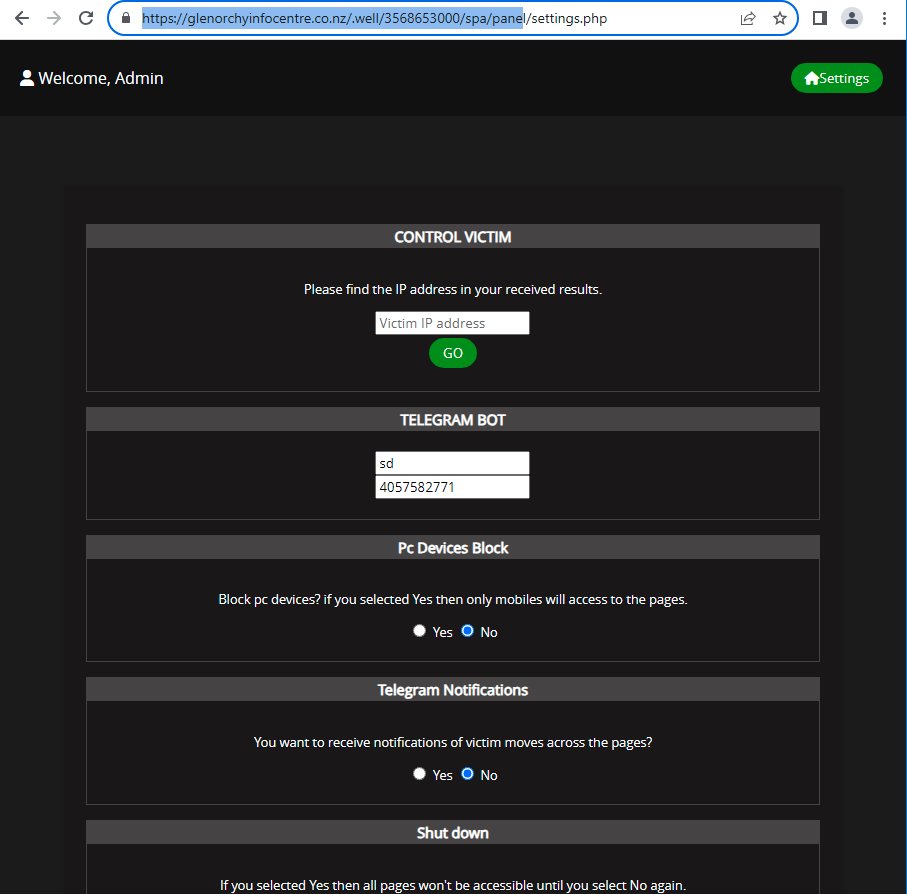
Trustwave SpiderLabs’ Email Security team write about the Tycoon Group phishing-as-a-service (PaaS) framework. Its key selling features include the ability to bypass Microsoft two-factor authentication & leveraging Cloudflare to evade antibot measures. https://t.co/kA0ybRxAwR
🕷️🔎 SpiderLabs has identified a new #phishing-as-a-service, called Tycoon Group.
#TycoonGroup offers features like bypassing #MFA for Microsoft and Gmail, high-speed link functionality, and more.
Get the details - and IoCs - below:
https://t.co/9jS2HGqnYq
🚨 Trustwave has observed surges in attacks exploiting vulnerabilities in Apache ActiveMQ.
Get the details on the ActiveMQ vulnerability, dropped payload, Godzilla webshell, affected versions, and the IOCs below 👇
https://t.co/Wpp9J2c3jq
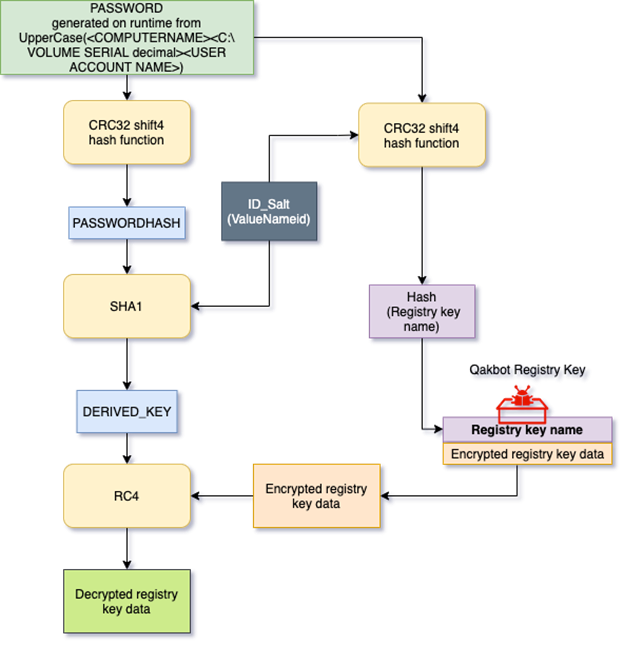
Trustwave SpiderLabs researchers Lloyd Macrohon & Rodel Mendrez show how to decrypt Qakbot (Qbot/Quakbot) encrypted registry keys. https://t.co/8HCQOMzML7
🔒 During a recent #malware incident response case, Trustwave SpiderLabs encountered an interesting piece of #ransomware that goes by the name of #BlackByte. Read our two-part blog series to learn more.
Part 1 (in-depth analysis) is here: https://t.co/g8hL3hApLZ
Trustwave SpiderLabs has discovered a new #malware dubbed 'Pingback' that uses a variety of tricks to stay under the radar and evade detection, while stealthily capable of executing arbitrary commands on infected systems. 🕷️ Read the SpiderLabs blog: https://t.co/fNxspgiNkv
Unfortunately with any tragedy you'll find criminals devoid of morals trying to take advantage of the vulnerable. True to form we continue to see an uptick of COVID-19 #phishing scams. Please stay safe out there! #infosec#malware https://t.co/UtFq9ZoIMe