We are pleased to release tmp.0ut 5 Volume!
Get your viruses, rootkits, strange ELFs, weird machines, tiny files, cool art, and phresh beats here!!
https://t.co/tZLM50HOc0
📁 .ppkg files are Microsoft deployment containers used to configure Windows devices. @dtmsecurity wrote about these and how to abuse them for code execution.
🧐 So I went back and reproduced the technique to identify detection indicators.
🖊️ https://t.co/FM3cLaxsov
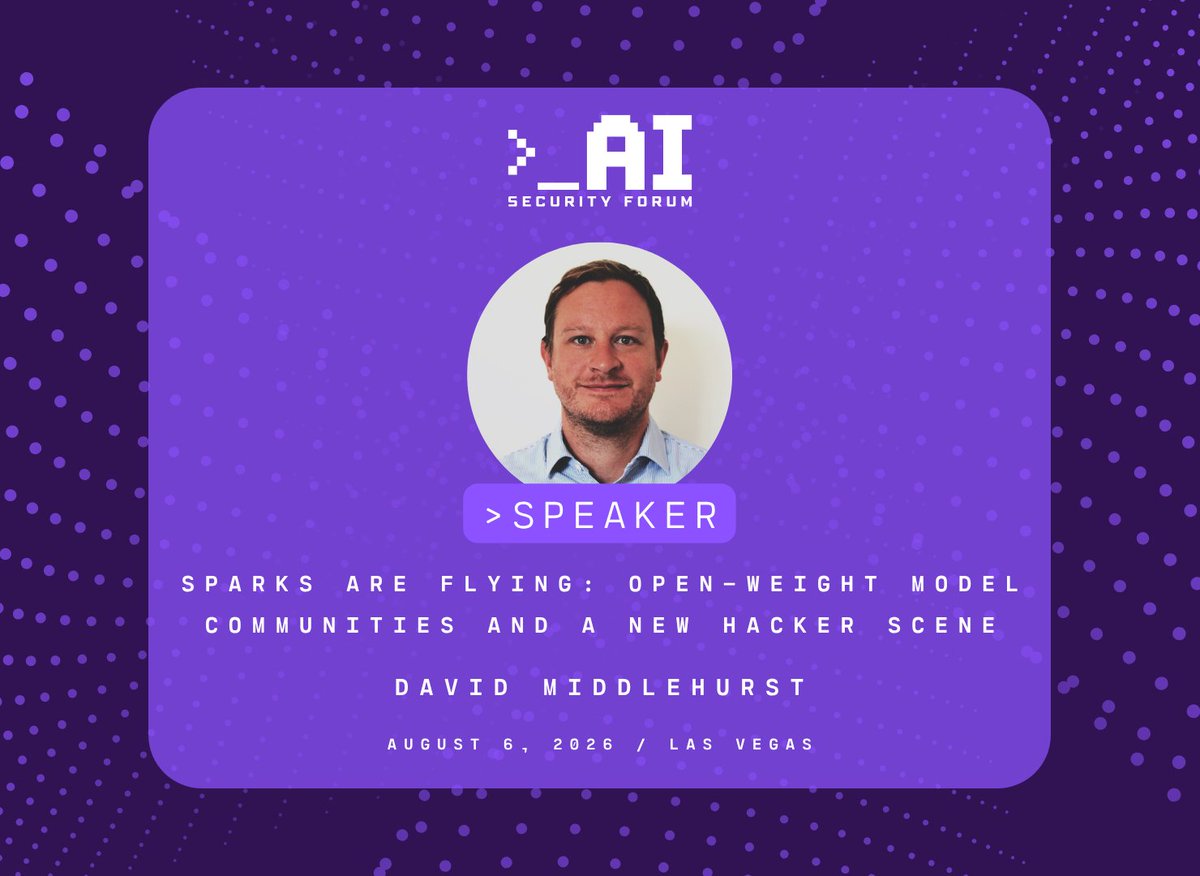
Next week I’m Vegas-bound. On Thursday I’ll be speaking at the AI Security Forum. Looking forward to sharing some AI research, presenting on something other than traditional red teaming for a change, and of course catching up with lots of humans.
Once weights are in the wild, the control surface moves from API governance to local modification. @dtmsecurity maps the "abliteration" scene and what breaks once safeguards can be stripped offline.
For session times & detail, check our conference app.
#AISecurity
Once weights are in the wild, the control surface moves from API governance to local modification. @dtmsecurity maps the "abliteration" scene and what breaks once safeguards can be stripped offline.
For session times & detail, check our conference app.
#AISecurity
Note on WordPress pre-auth RCE (CVE-2026-63030). There are SQLi poc's out there, but RCE PoC has not yet been exploited in the wild. Will only release our technical post if we have proof of exploitation. Our RCE payload does NOT require poorly configured MySQL.
I came across a simple technique that abuses Fondue.exe, a native Windows binary, to execute a custom malicious APPWIZ.cpl file placed in the same directory.
PoC and More details on how it was discovered later!
#redteam#offsec
Wow this post really blew up! If you want to know more about the smallest possible files that do things, check out the 6th annual Binary Golf Grand Prix, happening now til January 18th!
https://t.co/Lb4J5rNJGN
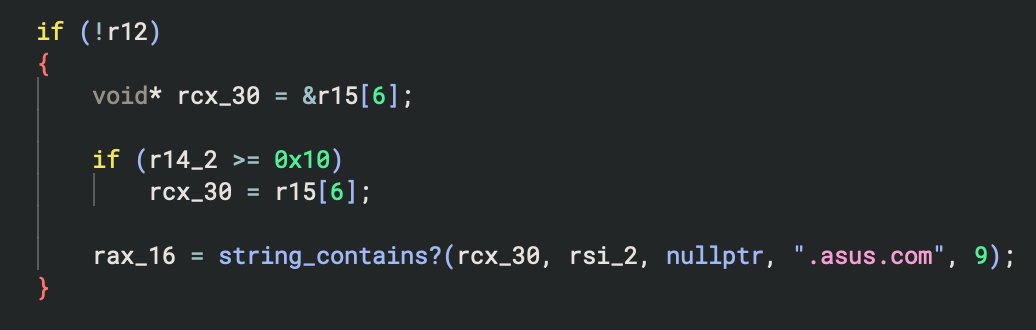
Two blog posts just dropped - one with the details on the bloatware pwning shenanigans I was up to earlier in the year, and another on pipetap, a new Windows named pipe proxy/tool.
https://t.co/bmqZ9x3obQ
https://t.co/QD59sHpTEP
Would you like to be my colleague, and get to wear an awesome red hoodie? We are looking for a full-stack / offensive developer. Drop me a message or apply directly: https://t.co/GKI48eVUPC
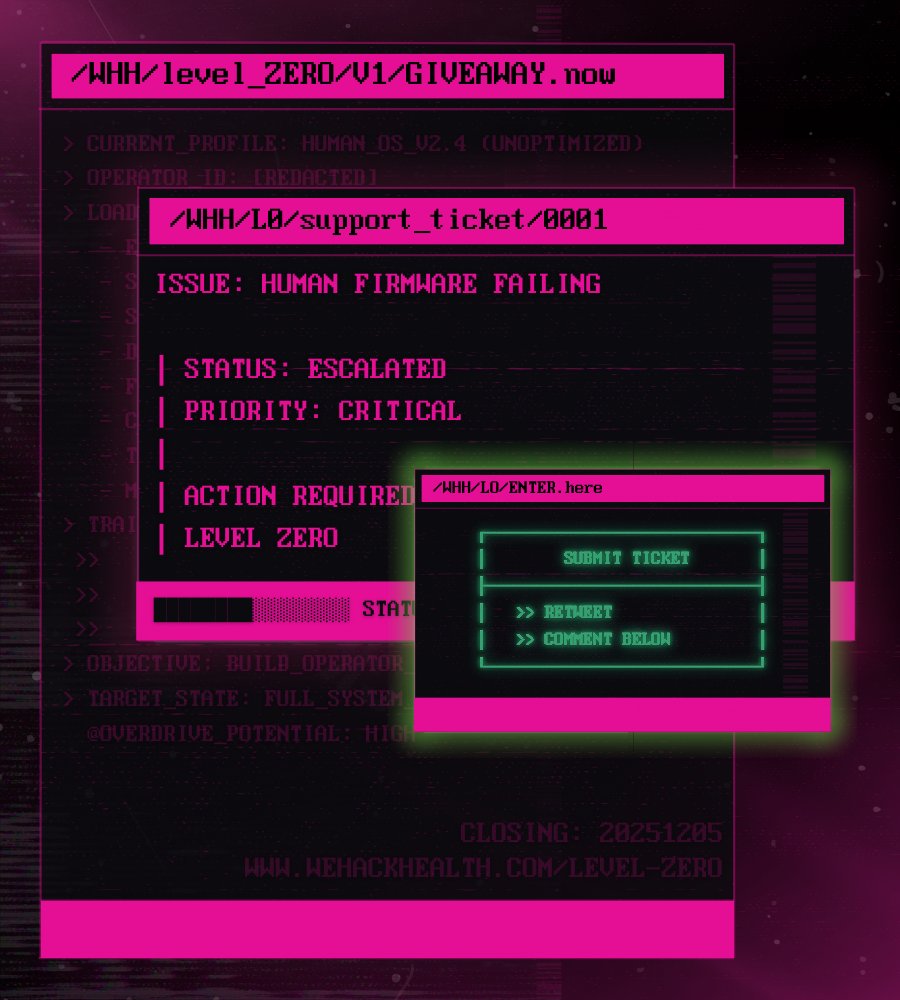
We are giving away 1 free spot for level ZERO.
If you are a cyber pro or tech bro and want a full system reset - now is your chance.
To enter: 🔄 retweet
Bonus entry: 💬 comment below - 1 thing you want to fix in the new year.
Winner announced Friday.
#wehackhealth
Slides and Such for my @BSidesVienna talk about Linux H4x as just a bunch of syscalls, Living Under the Land on Linux
Slides: https://t.co/06QPZ6gR5G
and Such: https://t.co/6oA1XbpoAO
New writeup for #BGGP6 !!
What's the smallest Wireshark dissector? What's the most annoying Wireshark dissector?
Find out here: https://t.co/VMlMXuGXsz
Last month, @d_tranman and I gave a talk @MCTTP_Con called "COM to the Darkside" focusing on COM/DCOM cross-session and fileless lateral movement tradecraft.
Check out the slides here: https://t.co/1KNln1ldzF
Recording should be released soon.
Credential Guard was supposed to end credential dumping. It didn't.
@bytewreck just dropped a new blog post detailing techniques for extracting credentials on fully patched Windows 11 & Server 2025 with modern protections enabled.
Read for more ⤵️ https://t.co/mYPHg1mTKj