@Uniswap So you can tap on the sign saying "Onchain looks good here" but offchain you dodged a bullet because you don't interact with smart contracts in a vacuum.
Someone got popped , someone else bothered to tell you and you got saved.
In Greece, we have a saying:
«Στο σπίτι του κρεμασμένου δεν μιλάνε για σχοινί.»
Roughly translated: "Don't talk about rope in the house of a hanged man." 🧵
Funny story, @Uniswap.
On March 21, 2026, I reported that a developer working on your codebase had been compromised by the exact same North Korean operators who later hacked Binance.
I documented active credentials, access to your private monorepo, production release infrastructure, and a potential path to pushing malicious updates to mobile wallet users.
You acknowledged the report and classified it as "informational" and out of scope.
You were warned before this became your own disaster.
So perhaps a little less sarcasm about security and a little more appreciation for the people who help keep your users safe.
@Gi7w0rm Wanna guess the next step ? Our lawyer (who also got paid and cost us money) says you should not publish for XYZ reason. You should be responsible and not do it.
“You should never sit on vulnerabilities. Always disclose responsibly. Give vendors time to investigate and patch.”
Meanwhile, I APPARENTLY RUN A CHARITY.
Their external security consultants get paid by the hour to investigate my findings, while I'm expected to provide detailed technical analysis, reproduction steps, and evidence for free.
Everyone gets paid. Except the person who found the vulnerability. 🙃
Also (because I am resentful as my CFO (and wife) says), lets not forget how @Uniswap responded to me saving them on the EXACT SAME SITUATION 8 months ago. Informational that saved them a couple of Billions.
Cause apparently we are all working on a charity.
Security is never a finished job 🔒
We recently brought in security firm @kumioai to review our web and API stack, helping us identify areas to strengthen.
Their CTO spent nearly 2 years investigating North Korean hackers, uncovering evidence of 1,600+ affected organisations.
#BsidesDublin2027 - Provisional Date 22nd May 2027
We are back up and running and happy to announce a provisional date of the 22nd May 2027.
Here's to another great year 🎆
@malwrhunterteam The title of my autobiography is
"I should have documented more and I should have read before". BUT the other chain you posted is definitely not test (will post later :D)
People !
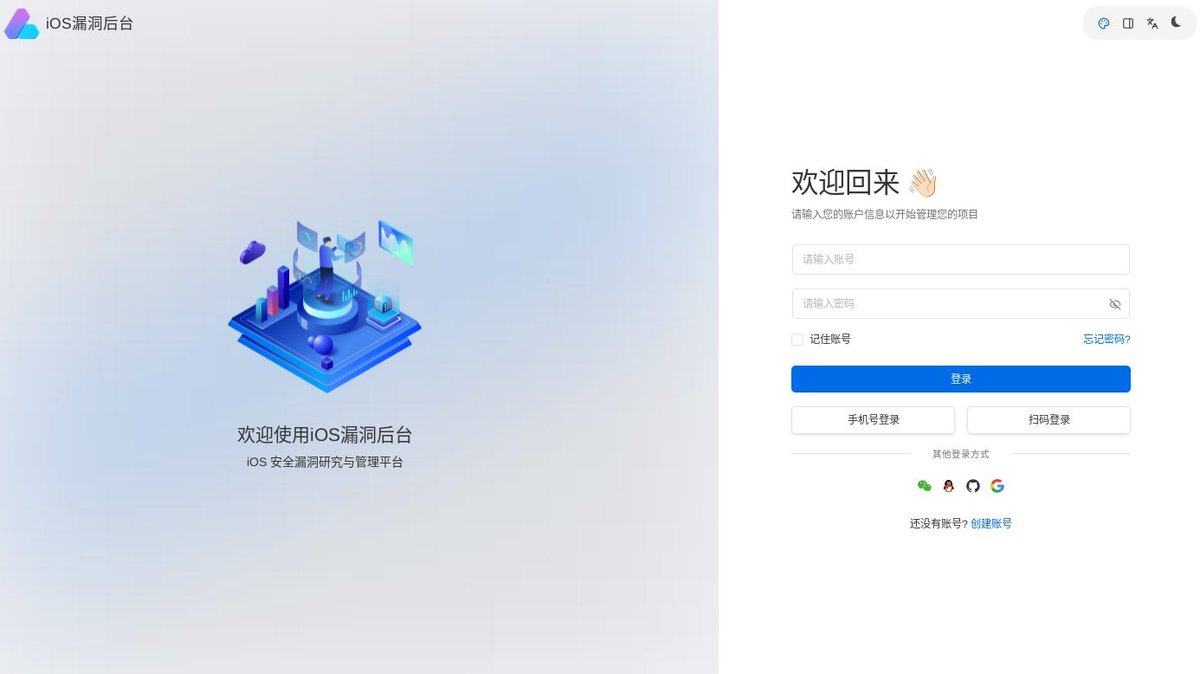
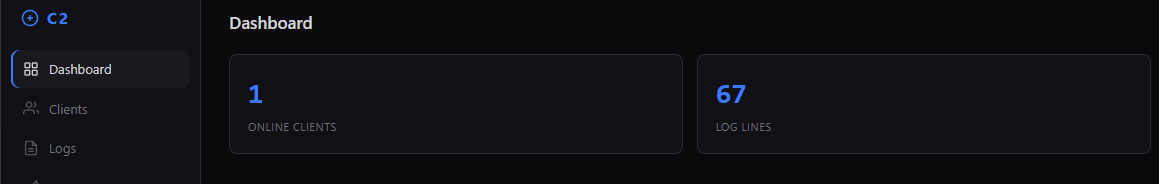
Stop probing criminal panels!
That's illegal (I might also want to do it and not have to fitler all the noise...).
Joking aside https://admin.msxf[.]info/api/devices. 122 devices most of them are just lfi prompts. This seems like a test env to me.