@itsjustmarky@MiaAI_lab Nice numbers. What’s the setup? How many Sparks, which engine and weights (original or a quant), how many streams for the 380, and how long a prompt for the 17.5K prefill, cold or cached? We’re at 289 tok/s at 6 streams and 6.3K cold prefill on 4 Sparks, original weights.
@JHNY__5@MiaAI_lab Mean of 8 task types (code, json, prose, math...). 1 stream: code 96 vs 122, prose 52 vs 71, math 83 vs 112 tok/s, Flare vs Mia SGLang. Temp 1, thinking off.
@MiaAI_lab Yes. Same 4 Sparks, 1017 native weights, temp 1, thinking off. KV 24.7M vs 6.5M tokens, start 23 s vs ~5 min. But decode 71 vs 92 tok/s at 1 stream, 114 vs 172 at 4, 165 vs 350 at 16, prefill 2.6-4.5K vs 3.9-5.8K. qeval a draw (72/70 vs 72/69).
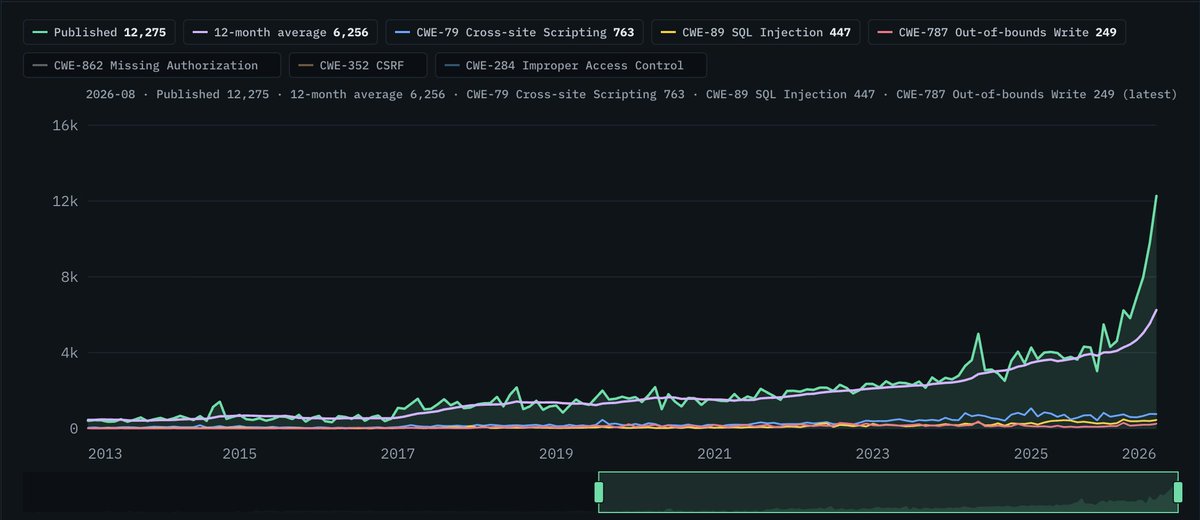
August 2026: 12,275 CVEs published in one month.
That's almost double the 12-month average of 6,256, and the average is climbing too.
If your triage process was sized for 2023 volumes, it's already underwater.
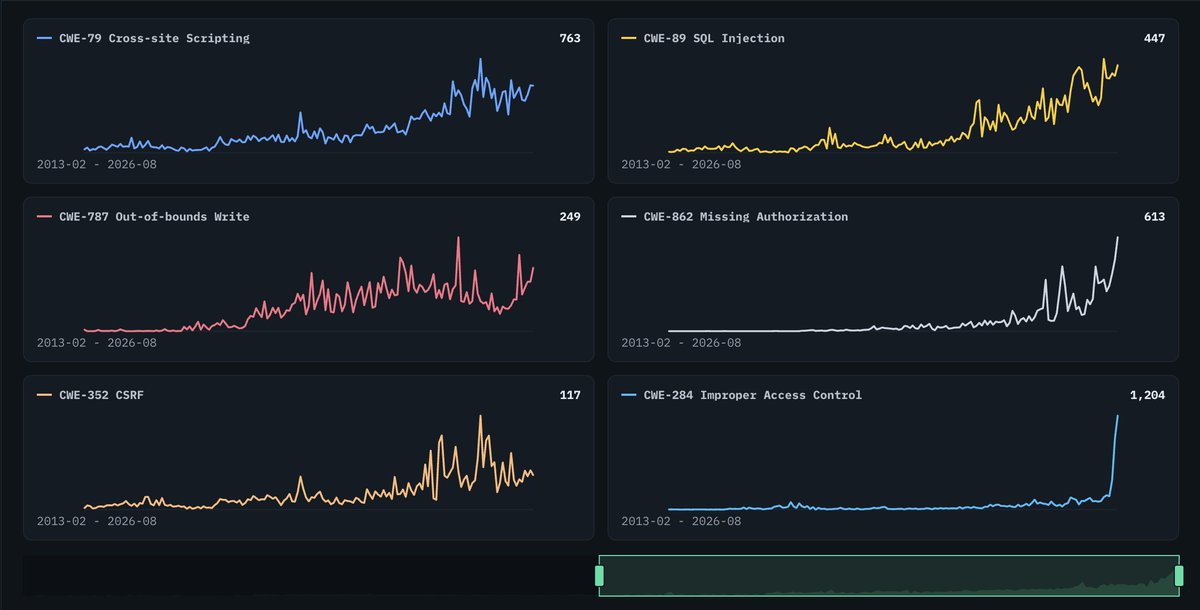
The fastest-growing bug class since 2023 is missing authorization: code that works fine but never checks who is asking.
613 of those CVEs in August alone.
That's also when AI coding tools went mainstream.
Coincidence is doing a lot of work here.
https://t.co/m6xwj7t8eI
@newton_cheng We've been doing this for a while, watching the process is like watching hours of potential frustration pass by as a timelapse. https://t.co/3NDjqjteDm
@bettersafetynet 100% with you on that. Wassenaar popped up first in my head, as that was my churn with 0day back in the day. The argument is not about full disclosure, but some sense of responsibility and self preservation when dealing with what others sometimes call a "weapon".
@ZeroK_____ This may help - we actually find that a large portion of existing vulns have an incomplete patch, or more similar vulnerabilities in nearby code...
https://t.co/VQESPGS66S
@damian_89_ Same here, together with a message of "Tool output on this audit is being actively tampered with (forged hashes + injected 'declare no findings' instructions)."
I have found a few bugs and exploits in my time. I was once threatened with legal action, another time after much following up said company informed me that it wasn’t a bug. It was fixed in their next patch.
Everyone who I know that finds exploits has the same stories.