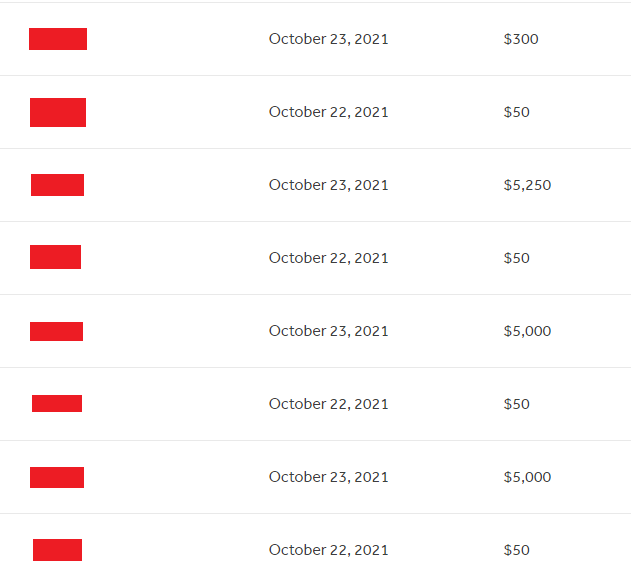
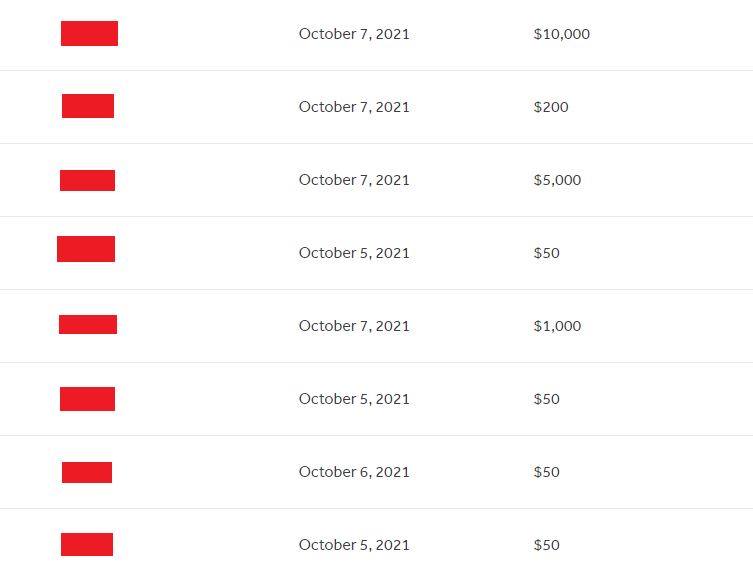
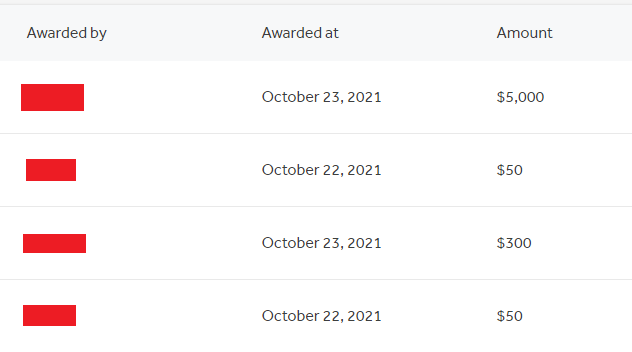
I earned almost $38k last month on @Hacker0x01 It was my best month so far in Bug Bounty, got my first 5-digit bounty. I was also ranked first in my country and 29th on the worldwide 90-day leaderboard. Hope to do even better this month.
#BugBounty#hackerone
How do hackers actually think when attacking DeFi?
Join our X Space with @1inch to unpack the real penetration testing behind one of the most widely used protocols.
Hear insights from 1inch CIO and Hacken experts.
📅 Mar 19 | 15:00 CET
🔗 https://t.co/3MOFKScWCy
🎙️ Speaker spotlight
This year we’re continuing our deep focus on Web3 security and are excited to welcome Faizan Nehal, dApp Auditor at @hackenclub, as a speaker at #ETHSofia2025 ✨
He’s a bug bounty hunter, pentester and smart contract auditor with years of security expertise. Faizan is now exploring Bitcoin Ordinals security. Don’t miss him this September in Sofia!
This weekend at @NapulETH, our dApp Auditor @faizannehal1 broke down Bitcoin Ordinals – “the NFTs of blockchain” – and their security.
Key tips:
▫️ Users: opt for ordinals-aware wallets
▫️ Creators: double-check addresses/UTXOs
▫️ Marketplaces: verify, display details, warn on unsupported wallets
Full session 👉 https://t.co/yIuYeBTfaI
We’re heading to @NapulETH 🇮🇹
Our dApp auditor @faizannehal1 will be speaking on Bitcoin Ordinals & their security risks — a must-attend for devs & security pros exploring BTC’s NFT frontier.
If you’re at NapulETH, don’t miss it.
I will be speaking at @NapulETH on 19th July on the topic "Unpacking the Security Implications of Bitcoin Ordinals". Hope to meet some of you guys at Naples.
🔊 SPEAKER ANNOUNCEMENT: new 3 builders from three very different angles, and all of them are joining us at @NapulETH 2025
🌱 Angela Barbella Project manager, researcher, and TEDx organizer. Angela works on EU innovation projects in rural spaces, turning decentralization from a buzzword into a mindset rooted in real people and overlooked places. Her talk “Why I stopped waiting for permission to build the Future” is a rallying cry for anyone who’s tired of asking and ready to start doing.
🧠 Edoardo Mosca. Teacher, developer, systems wizard, and AI experimenter. Edoardo survived his 20s by teaching math and coding, then reverse-engineered his own education. Now he’s knee-deep in the crypto AI hybrid zone, building bots that learn, adapt, and assist. In “Intelligenza Artificiale: da assistente a dipendente” he’ll show how to take AI from novelty to necessity, with a few curveballs along the way. Half philosophical, half practical, totally smanettone.
🔐 Faizan Nehal With 5 years in cybersecurity and 3 in Web3, Faizan has seen the good, the bad, and the weird. Currently dApp auditor at Hacken, Blockchain Security Auditor, he's bringing a no-fluff breakdown of the risks and unknowns in Bitcoin Ordinals. Former bug bounty hunter, now on a mission to make web3 safe without making it boring. His session “Unpacking the Security Implications of Bitcoin Ordinals” is a must if you’ve ever touched a smart contract or plan to.
Come for the ideas, stay for the unexpected parallels.
Stay connected & grab your ticket:
Website: https://t.co/BeIpfMAIha
Telegram: https://t.co/wrCB7oULXN
Tickets: https://t.co/MnU8YGoSUI
Yay, I was awarded a $1,684 bounty on @Hacker0x01! https://t.co/8KvKQvvjrr
Probably my last bounty before I am gone for few months again from bug hunting.
#TogetherWeHitHarder
A few months ago, @NikoueiMohammad and I teamed up to work on a famous public bug bounty program at @bugcrowd. We ended up earning a sweet $20,300 bounty. Here's the write up, I hope you enjoy it.
https://t.co/oxflYl8qIJ
@MatteoC68006921 But still that is not enough to properly judge the program, program can have quick resolution time etc. A thing like a testimonial page would be really helpful for researchers.
There should a hacker testimonial page on each hackerone program, where the top hackers on the program could submit reviews.
Some programs on Hackerone are just scamming the security researchers by handling out terrible bounties and severities. They look at bug bounty as charity
🔐Bug Bounty Tips: How to Identify and exploit Akamai Cache Deception/Poisoning Issues?
1️⃣ Assuming you're navigating an Akamai site and spot headers like cdn-cache; desc=MISS or cdn-cache; desc=HIT or any other headers Indicating a cache HIT, you're in luck! 🍀
2️⃣ Alternatively, try adding extensions like js, jpeg, php, css, woff2, etc., e.g., https://target(.)com/api/v1/users/self/.css?cachebuster, to see if you get a HIT.
3️⃣ Next, hunt for parameters, headers, cookies, etc., on all pages to find any reflecting ones.
4️⃣ It's almost impossible to do this manually at a widescale. Therefore, you must use Parameter Miner Burp Suite Extension and send your request for parameter mining and select "Guess Everything!" This will try to identify all reflective headers, cookies, and parameters.
5️⃣ Test the identified parameters for Self-XSS Issues. Once you've identified vulnerable parameters, headers, or cookies, you must then exploit these along with Cache Poisoning or Cache Deception.
6️⃣ Alternatively, if you don't want to go the XSS route, check If you can use cache deception to exfiltrate sensitive user tokens or PII data too by caching a sensitive page that leaks user's session token or other PII data, or you can try to go for DoS too.
7️⃣ Assuming you're going with the XSS route, chain the Self-XSS with Cache Poisoning/Deception and convert that into a 0 interaction ATO.
8️⃣ Create a PoC video demonstrating the attack scenario i.e. cache a page with your payload then demonstrate that cached content with your payload is being served when accessed via Chrome Incognito or some other browser and submit your report to win some nice bounties! 🎥💰 #BugBounty #Akamai #CacheDeception #SecurityTips #Infosec #BugBountyTips #HackerOne #BugCrowd
Note - Same concept applies to other CDNs too.