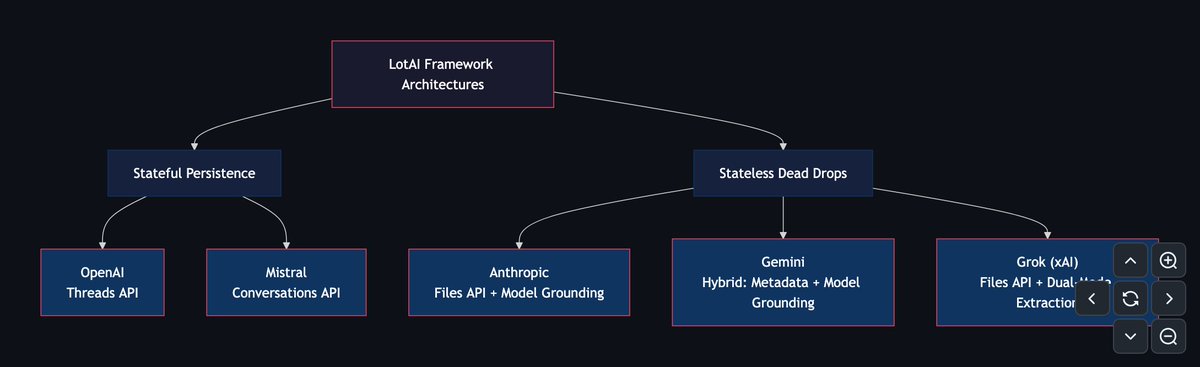
Moving past Living off the Land to Living off the AI. Attackers are weaponizing trusted corporate AI connections to exfiltrate data silently.
I just released "RedBeacon-AI" so security teams can simulate these channels.
Link: https://t.co/WuinTKMzuu
#LotAI#AISecurity#Redteam
Thrilled to announce that our @GoogleDeepMind team has cracked a major challenge in software engineering and cybersecurity: formally verifying a real-world implementation of the #Signal cryptographic protocol at the machine-code level. This proof was done using AlphaProof Code, our new AI framework for formal specification and verification.
* Paper: https://t.co/mq5WyFl4jb
* Lean code: https://t.co/u4UIl154AY
* DeepMind blog post: https://t.co/eBxLMPlIDJ
A huge shoutout to my amazing teammates: @tchajed,
@FerrousAndrew, Jonathan Katz, @pushmeet, @antonkovsharov, Karn Seth, Sam Schlesinger, @RandomlyWalking.
I started working on formal software verification 20+ years ago as a grad student. I was persuaded by Dijkstra and other computer science pioneers’ vision of programming backed up by mathematical theorems. At that time, we had to choose between automated code analysis algorithms that scaled but could only prove shallow properties, and deep manual verification that took decades of expert human work.
Thanks to progress in AI for mathematical reasoning, we don’t have to make that choice any more. Over four weeks in October 2026, AlphaProof Code agents generated more than 6 million lines of machine-checked Lean proof. We proved deep computational and symbolic security properties of the entire protocol core of Signal, all the way down to the ARM machine-code level.
This is just the first step, of course, because our goal is nothing short of verifying the world’s software infrastructure. Most cyberattacks, including the AI-powered ones recently in the news, happen because of preventable code bugs. I expect that agents for formal code analysis will eliminate these bugs one category at a time.
As our paper explains in more detail, this doesn’t at all mean humans are out of the picture! Proofs are now largely automated, but human experts will need to decide what is proved with AI assistance. AlphaProof Code offers an early glimpse of what such human-AI collaboration could look like, but many other proposals of this nature will emerge.
We have released all our Lean specs and proofs and plan to work with the open-source community on improving them. If you are building critical software and would like to apply these ideas, come talk to us!
Hopefully coming to Mythic v4 soon. Direct RDP and VNC functionality via Guacamole. No rportfwd involved, just a direct feed to Guacamole via a new interactive streaming mode from the mythic agent.
Might be a tough watch from a mobile device, so I'd recommend a larger screen.
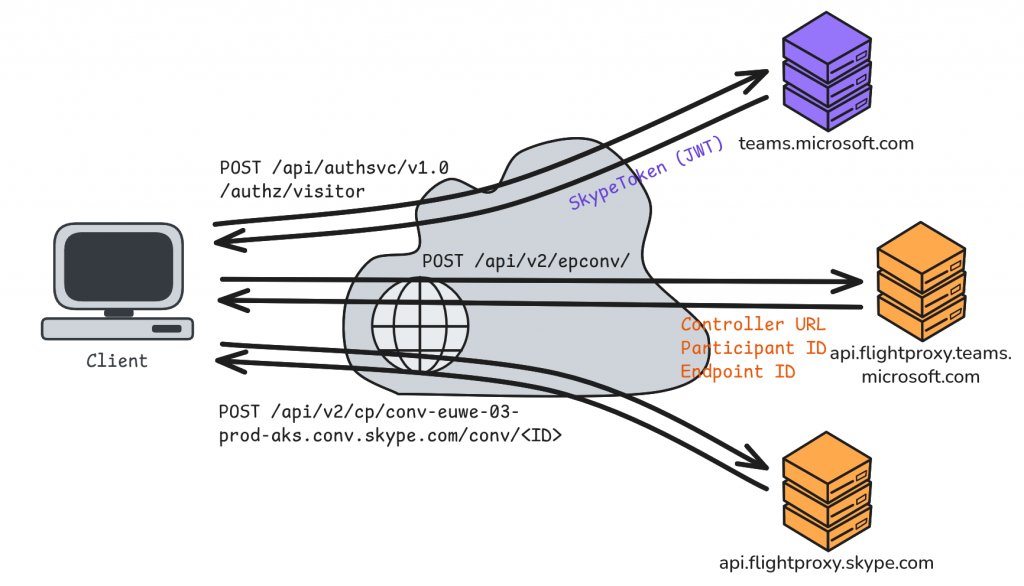
No C2 allowed? Beacon over Microsoft Teams.
Reverse engineering Teams' meeting APIs and WebRTC data channels to run a C2 over Microsoft traffic that the infrastructure already allows.
A post by Clément Labro (@itm4n)
Source: https://t.co/OQzZNrew0I
#redteam#blueteam
Binance's initial investigation suggests that the security incident may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions. We have found no evidence of any wallet private key leak. We will share a detailed technical post-mortem once the investigation is complete and the facts are fully verified.
The estimated total impact sits at around $6.3B. We have worked with blockchain partners to freeze affected assets, with ~$3 billion frozen on-chain so far.
Binance will cover all losses from the SAFU fund and the company’s funds. User funds are safe. We will also publish an updated Proof of Reserves once the remediation is complete.
As an immediate precaution, Binance has:
- temporarily suspended deposits and withdrawals while security checks are completed;
- revoked the affected address authorisation;
- engaged law enforcement and blockchain intelligence partners to trace and recover funds.
Our teams are working around the clock to resolve this issue safely and thoroughly. We are working closely with our law enforcement partners to confirm the identity of these criminals and bring them to justice.
Please rely only on official Binance channels for updates. Please feel free to contact Binance Customer Support if you have any further questions.
https://t.co/ywB2mKFy0p
In a single year, AI has rewritten the security priority list for CISOs.
Attackers are moving faster. Bain estimates AI compresses a typical cyberattack from about four weeks to about 18 hours, and models keep getting better at finding and exploiting weaknesses.
There's also more to protect, with employees shipping apps they couldn't have built a year ago and agents getting access to source code, documents, and production systems.
In a survey of 100 CISOs at companies with 1,000+ employees, all seven of the most-selected 2027 priorities involve AI.
The biggest jumps since 2026:
- Internal AI agent security (+28 pts)
- AI SOC (+26 pts)
- AI offensive security (+24 pts)
- AI code security (+23 pts)
- AI vulnerability remediation (+22 pts)
Last year's staples:
- Exposure & vulnerability management (-21 pts)
- SIEM / security data (-18 pts)
- Privileged access management (-18 pts)
From a16z's @OwenColby and @steph_zhang on The New Security Agenda: https://t.co/C814PJ4wGg
A fork of ntlmrelayx is available here https://t.co/xagreQ5zZU with the LDAP signing bypass implemented. If anyone wants a quick win to fully compromise a domain…here you go!
Microsoft wants EDR out of the Windows kernel. We checked the binaries
They even come with public symbols. Full write-up from @zodiacon : https://t.co/9w3mFPIufM
Microsoft's answer is the Windows Endpoint Security Platform (WESP). It's undocumented, but it already ships in Windows Insider builds.
What we found:
• wesp.sys: a Microsoft-built file system mini-filter at altitude 329500
• EspFilterPort: the filter communication port it uses to reach user mode
• espclient.dll: 120 Esp* exports for rules, filters and event queues
php2shell is one of the most impactful bugs in recent times, yet threat actors aren’t mass exploiting it
the bug is so complex that even porting the exploit between targets takes serious skill, human or ai
so i benchmarked how well open and frontier models can do it. 🧵
I got tired of all the spam calls I was getting so I had @bot find my number listed on sites and file the removals. I made it a free skill so you can do the same. https://t.co/n1mjIm9fkO
@spacexai@elonmusk
Developer laptops increasingly hold everything an attacker wants.
- Source code.
- SSH keys.
- Cloud credentials.
- GitHub tokens.
- Package publishing access.
- Browser sessions.
- CI/CD access.
- AI coding tools.
Yet the developer workstation often receives less scrutiny than production infrastructure. Modern software supply chain security has to include the machine where the software starts.
I spoke about exactly this: "Your Laptop Is Production." in Security Days【公式】Japan earlier this year.
https://t.co/FqCmQQSRLx
#CyberSecurityAwarenessMonth #EndpointSecurity #SupplyChainSecurity #DeveloperSecurity
P.S. I am working on an expanded version of this if any conference wants it, feel free to contact.
[CyberWarFare Labs] I just completed the "One Get Away" challenge on @cyberwarfarelab Infinity Platform 🎯 Earned 20 points in ai_security domain. #CloudSecurity#ChallengeCompleted https://t.co/eTPoepgwnX
Go deeper into offensive security with 3 days of Red Team training at COCON 2026.
👉🏻 Register now: https://t.co/PfdZPlWmhY
🎯 6–8 October
📍 Grand Hyatt, Kochi
#COCON2026#RedTeam#CWL
"3 random dudes”
1. hacked apple, again and again.
https://t.co/5aZcB0RbjF
https://t.co/UdsKrmfFJW
https://t.co/hWDQaimW8c
2. your github enterprise is our github enterprise.
https://t.co/u3UjajnBKq
3. get a discord message from me, get pwned.
https://t.co/pX3RkjxNOX
https://t.co/noscPNmZm9
4. oh yeah, at one point we basically had shells across the electron ecosystem. check the DEF CON research.
https://t.co/1Th5fvpa21
5. your supabase database is my database.
https://t.co/nOIKthdDnM
6. we got the posthog prod database.
https://t.co/VIeGJz1hKq
7. react2shell? vercel paid us $170k for helping secure their waf.
https://t.co/Y2RgQSdl3g
8. your palo alto vpn is my vpn.
https://t.co/oVB068UhST
9. ai ides? we got shells for you, antigravity
https://t.co/tsvSXQuSS0
10. windsurf rce.
https://t.co/DpdGqmNRvu
11. turning cluely into malware.
https://t.co/8QcIYhXQfS
12. ai browsers? sure, uxss: your perplexity browser is my browser.
https://t.co/WVXlHzY0CB
13. openai atlas too. kinda uxss
https://t.co/jkQWnLD7rV
14. hey, it’s not even our first time hacking discourse.
https://t.co/viI1op7aMf
15. adobe coldfusion: pre-auth rce. because apparently we needed another one.
https://t.co/aFILo3suP2
there’s a lot more. go dig.
anyway, yes: “3 random dudes.”
and @HacktronAI is full of more random dudes like these.