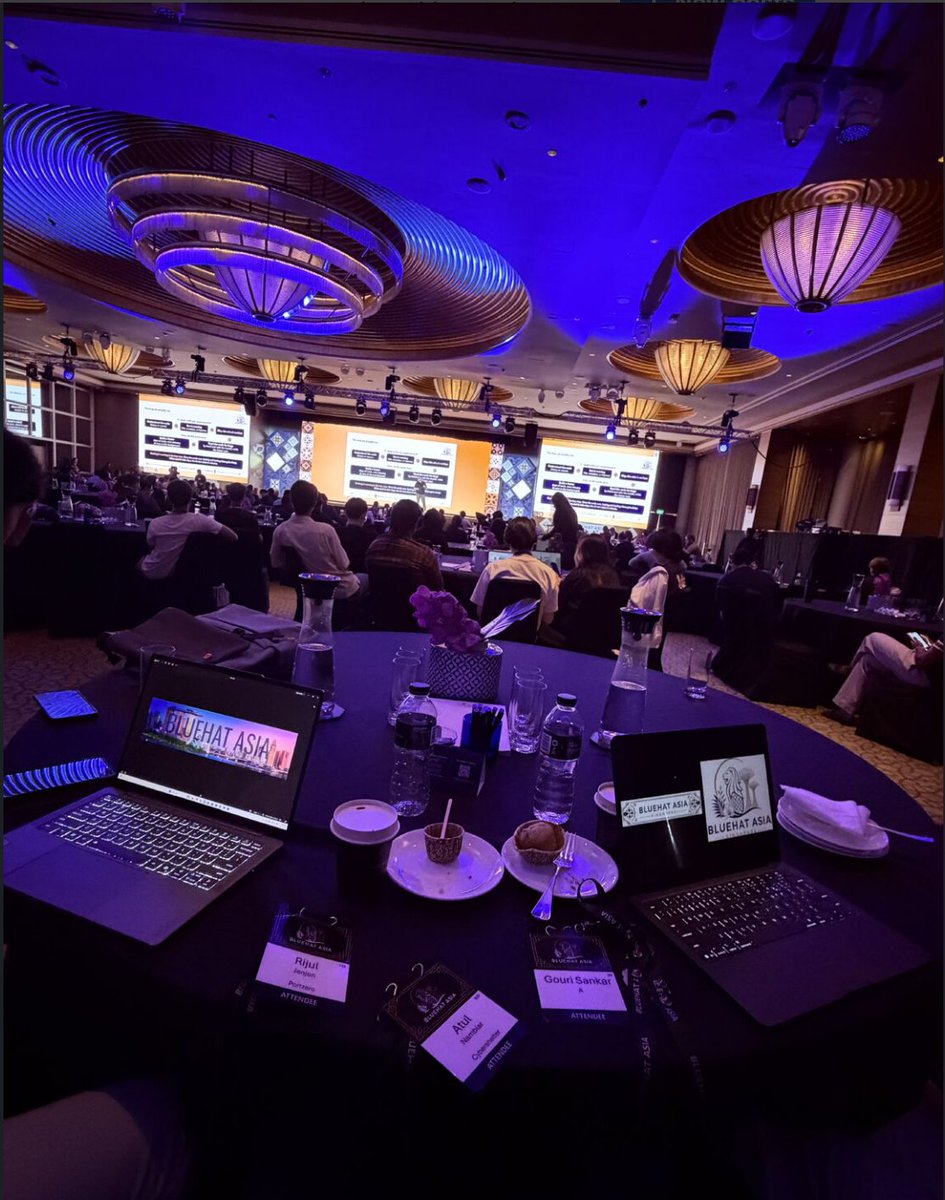
Day 1 at #BlueHatAsia 2026 (MSRC) done. 🇸🇬
Highlights:
Halvar Flake's "An Age of Experimentation" keynote
"PUT-ting on the Risk" one GET→PUT swap, 5 Criticals
"Four Simple Paths to Own an Entra ID Account"
DirectX kernel LPE → Hyper-V guest-to-host RCE
Thanks MSRC.
Over the past several days, we have been listening to the conversation around coordinated disclosure and the relationship between security researchers and vendors. We recognize that this relationship is both critical and, at times, fragile. We deeply value the security community, and will continue to take your feedback seriously.
To be clear about our approach to legal matters, we have no intention to pursue action against individuals conducting or publishing their security research. When an individual breaks the law and engages in malicious activity causing real harm to our customers, we will work with law enforcement as appropriate.
We recognize the work that goes into researching and submitting a vulnerability. We are committed to approaching every interaction with transparency, clear communication, and professionalism. We continue to believe strongly in Coordinated Vulnerability Disclosure as the foundation for protecting customers and improving our products. Each year we process a high volume of vulnerability reports. That volume continues to grow and will continue with the rise of AI-enabled research. We acknowledge that some interactions have fallen short and are working to learn from them.
Many of us have experience on both sides of this work, as researchers reporting vulnerabilities and as responders triaging and assessing them. That perspective informs how we approach this feedback and the importance we place on getting it right, particularly as the volume and complexity of research continues to grow.
The security community plays a vital role in helping us protect customers. We are committed to maintaining a constructive and respectful relationship and growing together. We know that, given the nature of this work, there will at times be misunderstandings. We remain committed to engaging in good faith and to providing a respectful and professional experience for all researchers, regardless of past interactions.
‼️ After the MSRC blog post about Nightmare-Eclipse, researchers are coming forward with their own MSRC horror stories.
The response from the security community isn't going Microsoft's way. As they’re not backing Microsoft.
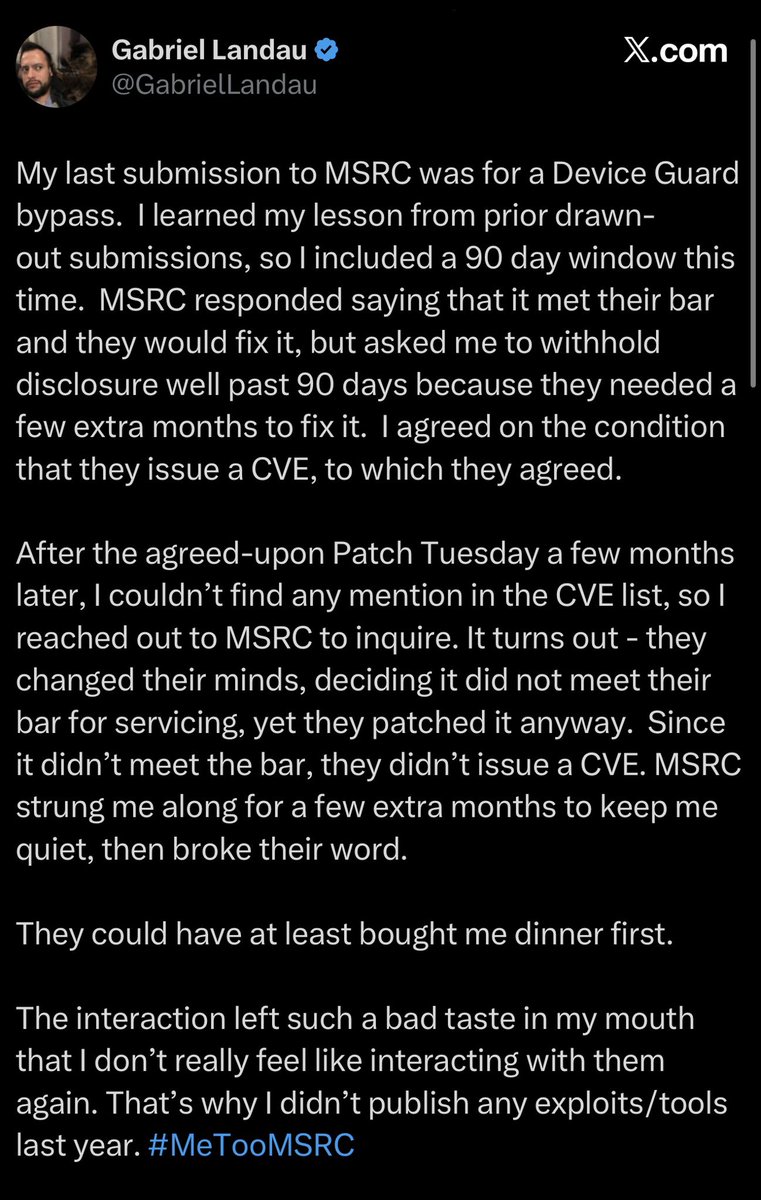
Gabriel Landau, a well-known Windows security researcher, says he reported a Device Guard bypass with a 90-day window. MSRC told him it met their bar and they'd fix it, then asked him to hold disclosure for extra months. He agreed on the condition they issue a CVE. They patched it silently, decided after the fact it "didn't meet the bar," and never issued the CVE. In his words: "MSRC strung me along for a few extra months to keep me quiet, then broke their word."
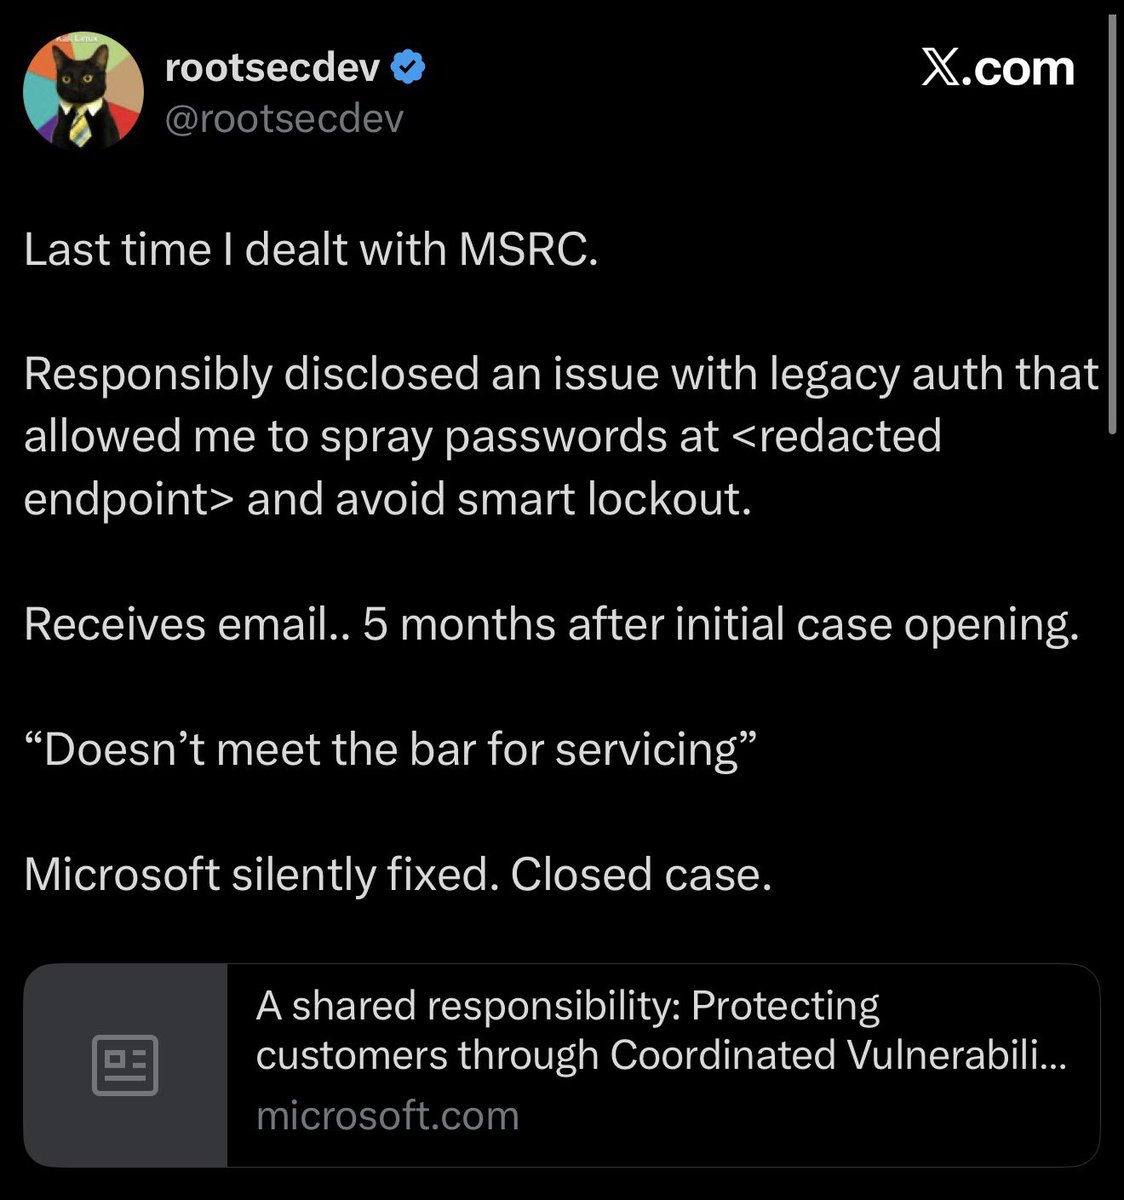
Another researcher, rootsecdev, says he responsibly disclosed a legacy-auth flaw that allowed password spraying while avoiding smart lockout. Five months later, MSRC replied that it "doesn't meet the bar for servicing," silently fixed it, and closed the case.
Microsoft's post was meant to defend their coordinated disclosure policy. Instead it became a thread of researchers explaining why they've stopped trusting their process.
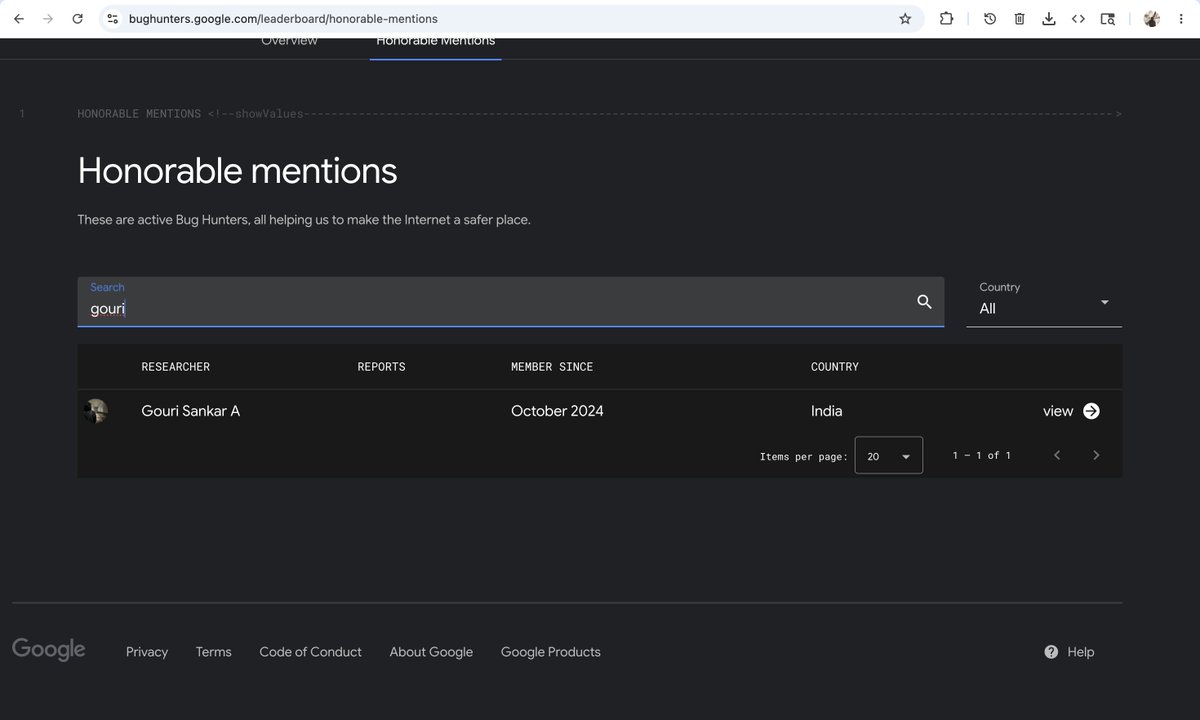
Excited to be featured in Google Bug Hunters Honorable Mentions ! Thank you @Google Security Team for the recognition
Grateful to be contributing to a safer internet alongside other talented researchers.
The journey continues..
#BugBounty#CyberSecurity#GoogleVRP#Sec#InfoSec
I just gave Claude Code a rooted Android phone…
It autonomously reverse-engineered Subway Surfers, hooked the coin logic, bypassed the anti-cheat, and gave itself UNLIMITED coins in ONE session.
Turns out I'm the youngest documented Indian bug bounty hunter to earn $10K+ from @Microsoft via MSRC multiple reports, multiple Hall of Fames, all at 18. Just a curious kid who loved breaking things to secure them.
#BugBounty#MSRC#EthicalHacking#CyberSecurity#Kerala
Just got my first CVE! 🔐
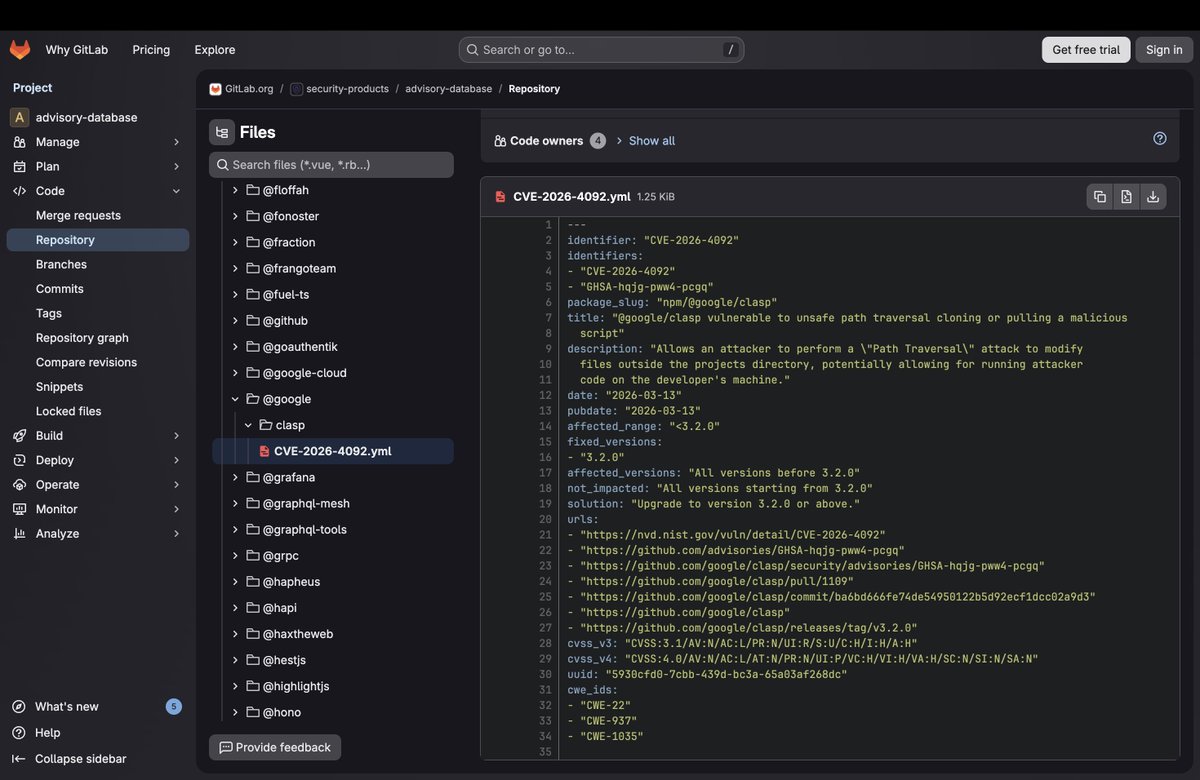
CVE-2026-4092 — Path Traversal in @google/clasp
High severity — CVSS v4: 8.7
Arbitrary file write via malicious GAS project.
Discovered, reported & fixed. Patched in v3.2.0.
- Affected: < 3.2.0
- Patched: v3.2.0
https://t.co/kL7sPPXvYd
#CVE