

Top Tweets for #BugBounty_Tips


🐞 How to Get Better at Bug Bounty in 2026
If you want to become a better bug bounty hunter, stop hunting the same way everyone else does.
1️⃣ Stop submitting low impact bugs
P4/P5 and low hanging fruit are becoming harder to monetize. Automated tools are getting very good at finding them.
Focus more on:
→ Bug chaining
→ Business logic
→ Broken access control
→ Account takeover
→ Impact escalation
2️⃣ Stop submitting bugs that programs don't accept
Read the Rules of Engagement before hunting.
If a program clearly says something isn't eligible, don't waste your time submitting it.
Only push further if you can demonstrate a real security impact that goes beyond the exclusion.
3️⃣ Think about impact, not just the vulnerability
Finding an IDOR is one thing.
Finding an IDOR that leads to sensitive data exposure, privilege escalation, or account takeover is completely different.
Always ask:
"What can I chain this into?"
4️⃣ Stop chasing quantity without quality
100 weak reports won't make you a better hunter.
Study your reports. Understand why they were accepted, rejected, duplicated, or marked informative.
5️⃣ Study disclosed reports
Read real reports from experienced hunters.
Look at:
→ Root cause
→ Exploitation
→ Impact
→ Attack chain
→ How the researcher proved it
6️⃣ Understand the application first
Don't immediately start throwing payloads everywhere.
Understand the application's:
→ Roles
→ Permissions
→ Workflows
→ APIs
→ Payments
→ Invitations
→ Trust boundaries
7️⃣ Build your own methodology
Don't blindly run 50 tools and submit whatever they find.
Use automation to move faster, but use your own brain to find the interesting stuff.
8️⃣ Learn to chain vulnerabilities
A low impact issue by itself might be useless.
But when combined with another weakness, it can become critical.
Stop asking:
❌ "What vulnerability can I find?"
Start asking:
✅ "How can I break the application's security model?"
🚀 Learn ethical hacking and bug bounty with me at https://t.co/W8zRpkSUVE
🌐 https://t.co/1Ezryc4AJX
#BugBounty #CyberSecurity #EthicalHacking #WebSecurity #Pentesting #BugBountyTips #Hacking #InfoSec #AppSec


The last payload I used to put a site to bed and slip a stored XSS into it.
(custom Waf)
<img/src='x'/onwheel=self[`al`+`ert`](1)>
#bug #bugbounty #bugbounty_tip #bugbounty_tips #xss
The result of the collab with @khode4liam was a dangerous bug. writeup? soon🔥🗿
#bugbounty #bugbouty_tip #bugbounty_tips #bugbountytips


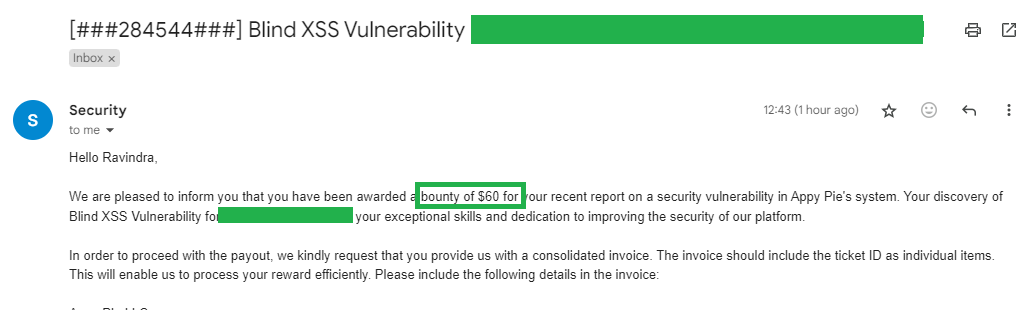
I don't think it's right bounty for blind xss. But this will help me to add extra zeros in my account . Thanks for bounty @AppyPieInc
#BugBountyHunter #bugbounty_tips

New subdomain enumeration script :
My new public script, which is called "cloud data" is a data gathering script.
it's parses some public data sources and gathers ip and domains of your target.
More info and usage : https://t.co/XEkuHxgBXU
#bugbounty #bugbounty_tips #recon

Google Map Api Key Checker by
@dirtycoder0124
This tool checks found api_key is vulnerable to exploit or not.
https://t.co/VUokoSidJp
#bugbounty #bugbounty_tips #infosec
#bugbountytips

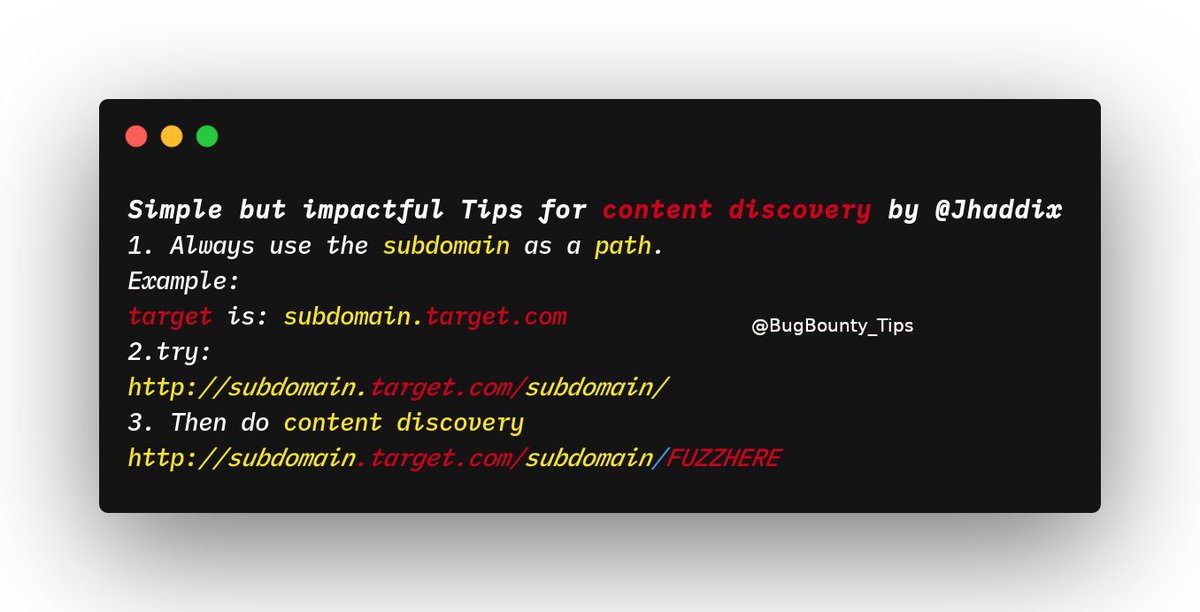
Crawl Subdomains with curl to get more subdomains
one liner : cat subdomains|xargs -P40 -n1 curl -sL | grep -Po '((http|https):\/\/)?(([\w.-]*)\.([\w]*)\.([A-z]))\w+' | grep '.intel.com'
#BugBounty_tips
Dont forget to sort


@bugbounty_tips Salam, the unroll you asked for: @bugbounty_tips: #BugBounty_Tips Q&A #1 We are very pleased to announce that one of @Bugcrowd active hacker @Hxzeroone… https://t.co/JMd7IQy78I Enjoy :) 🤖

Thank you @Hxzeroone for giving your valuable time in our #BugBounty_Tips Question-answer session!
All the best for your bug bounty journey!
Also thanks to all the participants.
If you want more guest in the upcoming session you can comment on their name.
#infosec #bugbounty
#BugBounty_Tips Q&A #1
We are very pleased to announce that one of @bugcrowd active hacker @Hxzeroone is joining us to answer your questions related to hacking, bug hunting & pen-testing!
You can ask your questions in the comment!
#bugbounty #infosec


Connected 137 friends just in few days.
Looking forward to reaching 1337 friends soon.
If you want to give any feedback/support/suggestions. Please do comment. Your feedback will be appreciated to share/post more #bugbounty_tips!
Thank you!
#infosec #bugbounty #bugbountytips
Google Map Api Key Checker by @dirtycoder0124
This tool checks found api_key is vulnerable to exploit or not.
https://t.co/KTR2viGRGP
#bugbounty #bugbounty_tips #infosec
#bugbountytips



Last Seen Hashtags on Sotwe
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.7M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.6M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90.1M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers