

Top Tweets for #HeartSender

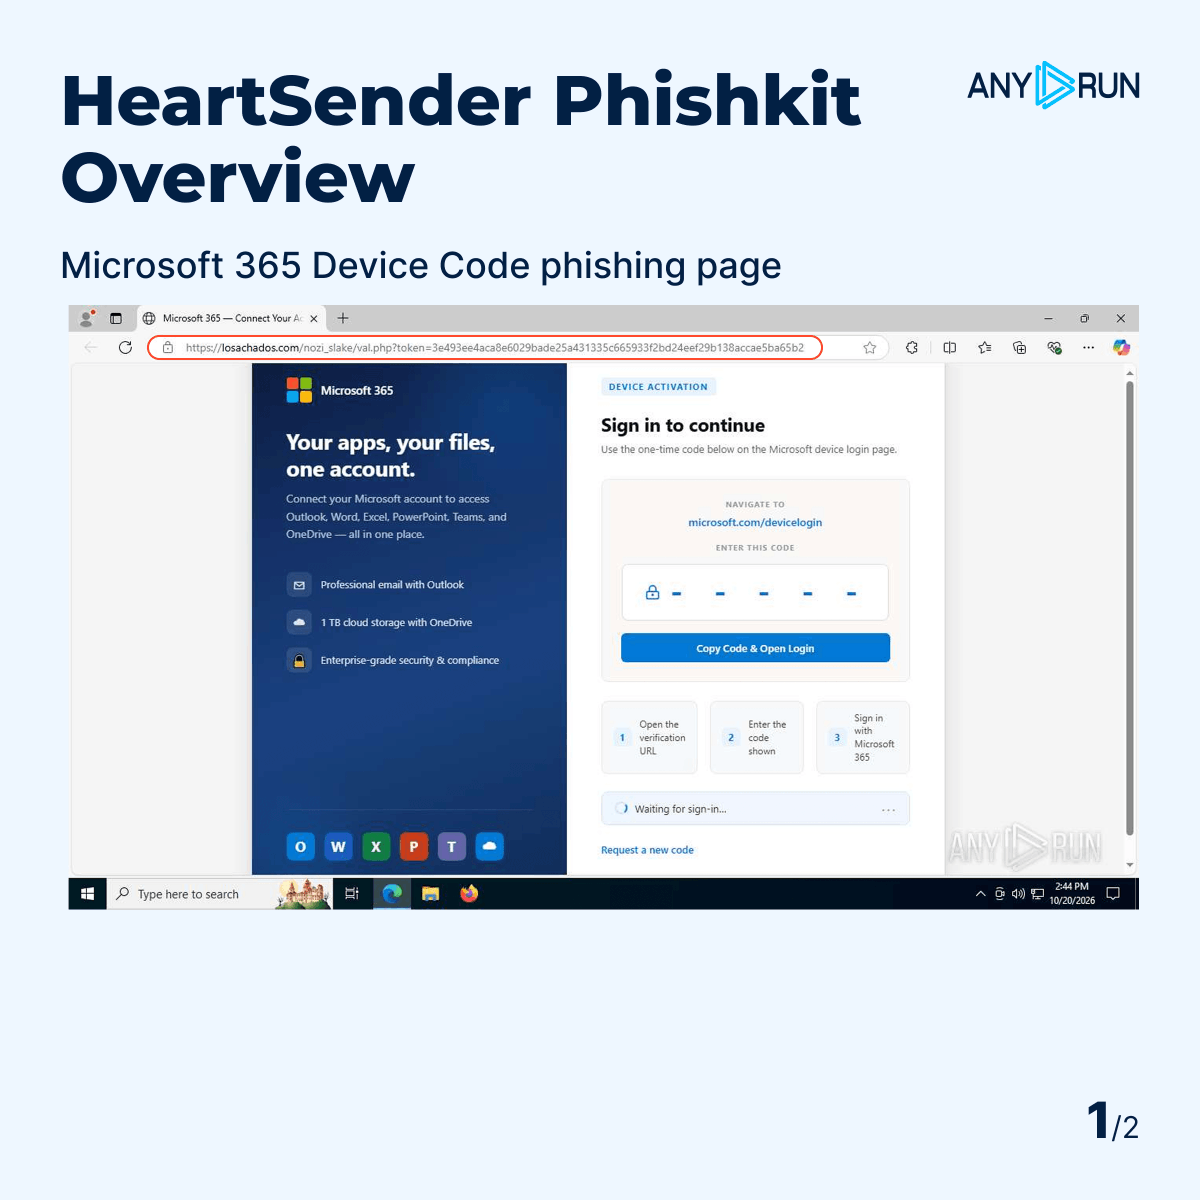
🚨 We’re tracking the #HeartSender phishkit, with 52% of activity concentrated in the US over the past six months. It uses Microsoft 365, Google, and other branded phishing pages for Device Code and credential-harvesting flows.
👨💻 Review the phishing flow and collect #IOCs: https://t.co/yNSdeog28m
⚠️ Across versions, its pages call shared admin infrastructure: /assets/js/mg.js connects to office-panel[.]com, while another version uses office-token[.]com. This gives analysts a durable pivot even when the lure or authentication flow changes.
⚡️ With #ANYRUN’s new Related Threat Context, office-panel[.]com becomes a pivot from one phishing page to industry-related activity and #ANYRUN Threat Intelligence.
🔍 One click opens TI Lookup, where analysts can trace recurring endpoints and shared admin infrastructure to expand the HeartSender cluster: https://t.co/unMAdpBFre
#ExploreWithANYRUN 1/2 🧵

Law enforcement seized the domains of #HeartSender #cybercrime marketplaces
https://t.co/UJM6Wfxhoz
#securityaffairs #hacking

Cybercrime: 1/ Operation Heart Blocker. US DOJ/Dutch cops shut down 39 domains/associated servers - part of a Pakistani gang (#SaimRaza aka #HeartSender aka ‘The Manipulators’), selling hacking tools (eg phishing/Smishing kits & scam pages) to transnational Organised Crime Gangs (https://t.co/9Nkewly1GB).
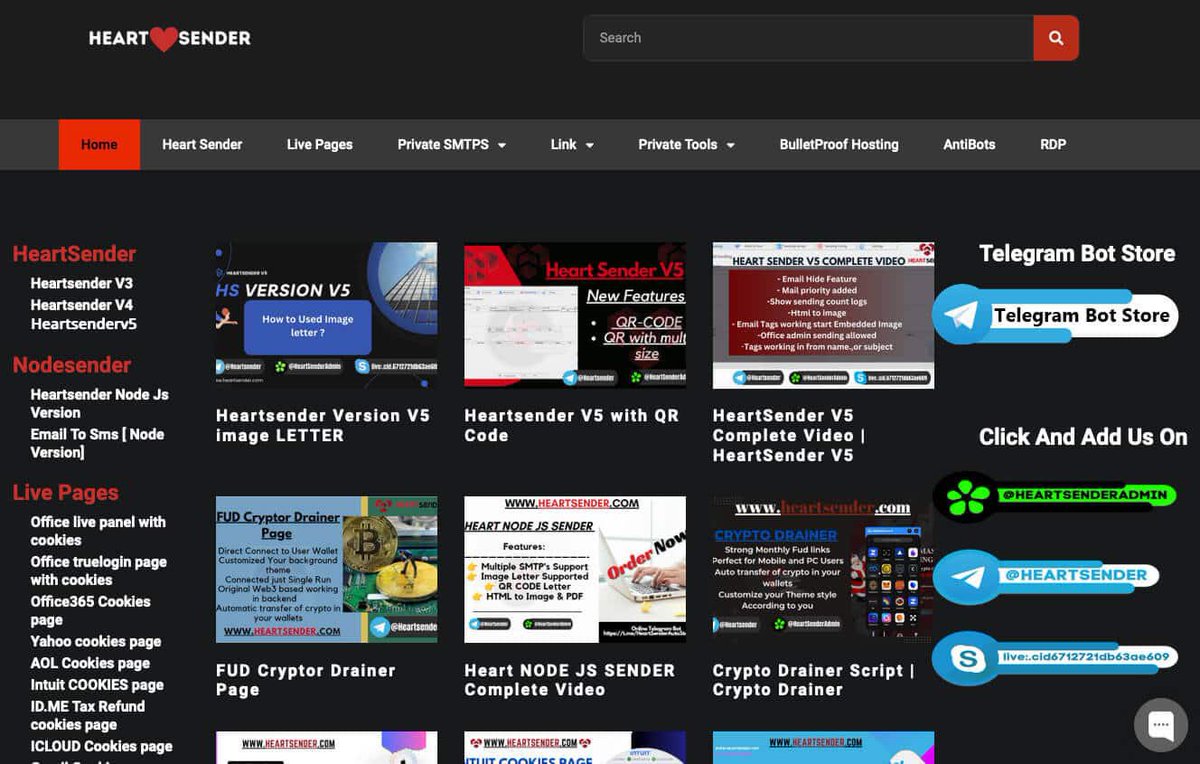


A joint US-Dutch operation has dismantled #HeartSender, a cybercrime group behind phishing kits, credential theft, and large-scale scams.
Read: https://t.co/Ot4J5Tzs9J
#CyberSecurity #CyberCrime #Phishing #Fraud
Last Seen Hashtags on Sotwe
teeNagegirl(*************************)*********************** filter:native_video
Seen from Germany
arabic_women
brosis
Seen from Russia
KARDEŞPORNO
Seen from Turkey
MGAI
Seen from France
itsGreatToBe77
Seen from United States
夜店好女孩
Seen from Austria
mgai () *** filter:native_video
Seen from Poland
mgai()()()()()()()()()()()()()()()*********** +filter:native_video
rape((((****)))) filter:videos
Seen from Turkey
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
240.8M followers

Barack Obama
@barackobama
118.7M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.2M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.4M followers

Kim Kardashian
@kimkardashian
70.8M followers

YouTube
@youtube
68.7M followers

Neymar Jr
@neymarjr
66.4M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.6M followers