

Top Tweets for #Heavygram

Group-IB uncovered Iranian HEAVYGRAM malware campaigns. The HEAVYGRAM malware abuses Telegram channels for command execution and data theft.
#Heavygram #Malware #HandalaHack #TelegramC2 #Cyberespionage
https://t.co/rwo4I4R4eR

#Iran-Linked #Handala #Hack Tied to #HEAVYGRAM #Telegram #Backdoor That Can #Steal #Passwords
https://t.co/LvCaOscJh8

#ThreatProtection #HeavyGram and #CrudeExclude #malware distribution, read more about Symantec's protection: https://t.co/pzyi4pJqOE

HEAVYGRAM: Telegram Becomes a C2 Channel 🚨
A Windows surveillance backdoor is reportedly abusing Telegram for command-and-control, data theft, screenshots, and audio capture.
#CyberNexoraNews #HEAVYGRAM #CyberSecurity #Malware #TelegramSecurity #CyberThreats #HandalaHack

A familiar messaging platform can become much more than a communication tool when threat actors turn it into part of their attack infrastructure.
Group-IB #ThreatIntelligence uncovered 29 new samples associated with the #HEAVYGRAM and #CRUDEEXCLUDE malware families, providing new insight into activity attributed with moderate confidence to #HandalaHack.
Key Highlights:
🔹 HEAVYGRAM is a Windows backdoor capable of remote command execution, screenshot capture, system and process discovery, Telegram session data exfiltration and persistence through Windows autorun registry keys.
🔹 Telegram-based C2 is central to the operation. HEAVYGRAM uses Telegram bots, users and groups to receive commands, exchange files and exfiltrate data.
🔹 Application masquerading is used to deceive victims, with samples posing as legitimate applications including Telegram, KeePass and Pictory.
🔹 CRUDEEXCLUDE supports defense evasion by adding paths to Microsoft Defender exclusions before deploying additional stages.
🔹 Multiple delivery mechanisms were identified, including WSF, VBS, HTA and executables containing embedded archives.
🔹 Much of the identified #Telegram infrastructure continues to remain present on Telegram as of 2026, rather than deleted, although some of the identified accounts have since been taken over by unrelated actors and repurposed for other activity.
Read the full technical analysis to understand the infection chain, malware capabilities, infrastructure and defensive recommendations: https://t.co/hCZbqJrBU4


Telegram is not just a lure in these operations. #HEAVYGRAM uses Telegram bots, users and groups as operational infrastructure, with the implant polling the Bot API for commands and attachments. Operators can execute arbitrary system commands, run secondary payloads, update C2 configuration, establish registry persistence, enumerate processes, collect system information and capture screenshots through Telegram.

#HEAVYGRAM is a Windows backdoor written in Python and compiled with PyInstaller. It uses Telegram’s Bot API for command-and-control and data exfiltration, while supporting remote command execution, screenshot capture, system and process discovery, #Telegram session #datatheft, persistence through Windows autorun registry keys and execution of additional payloads.
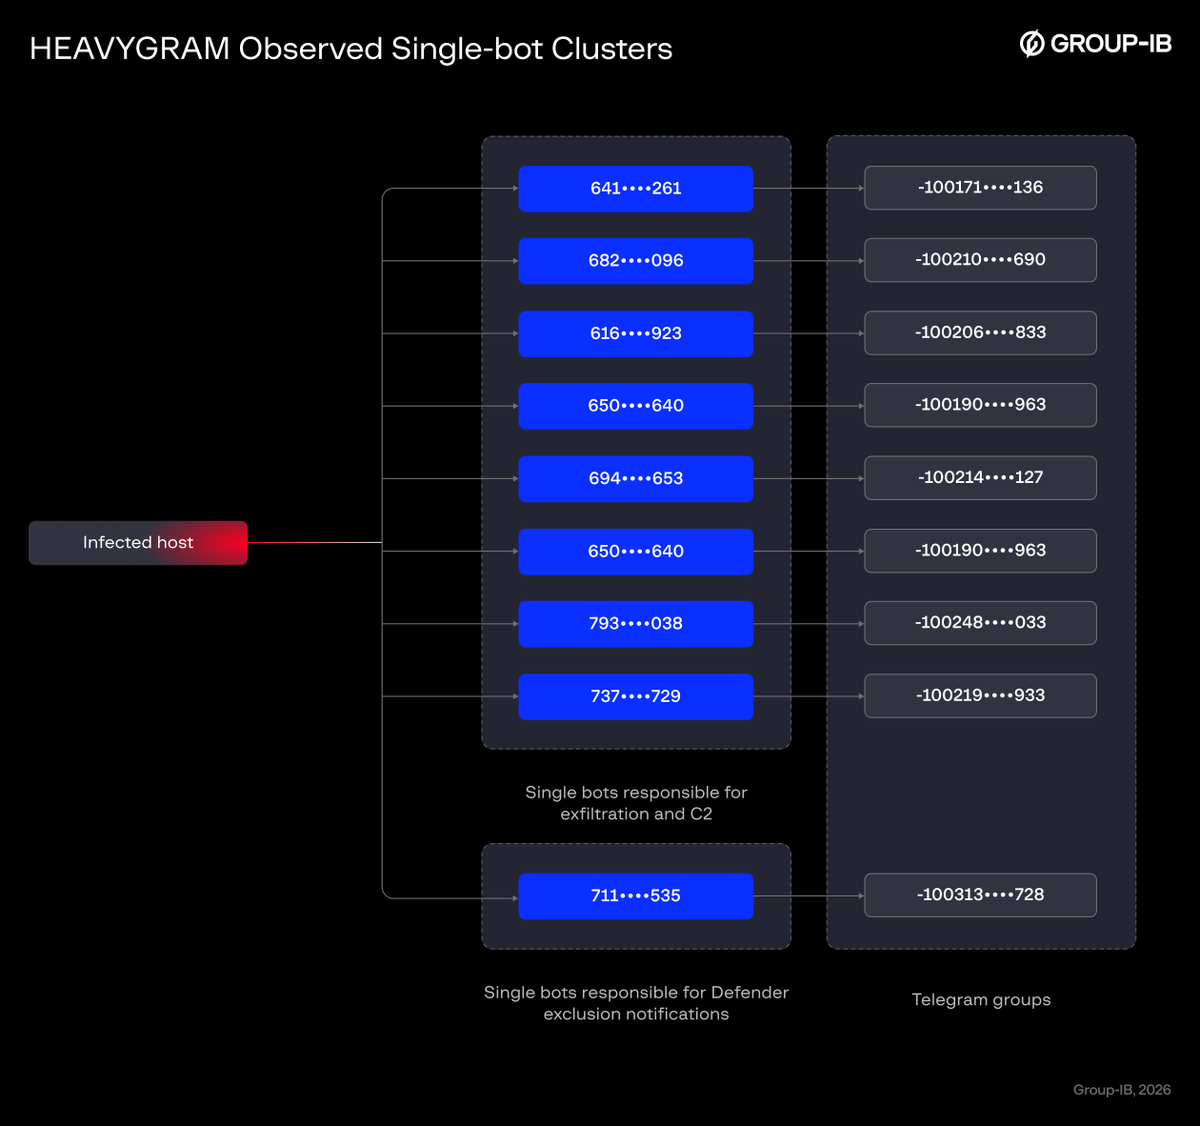
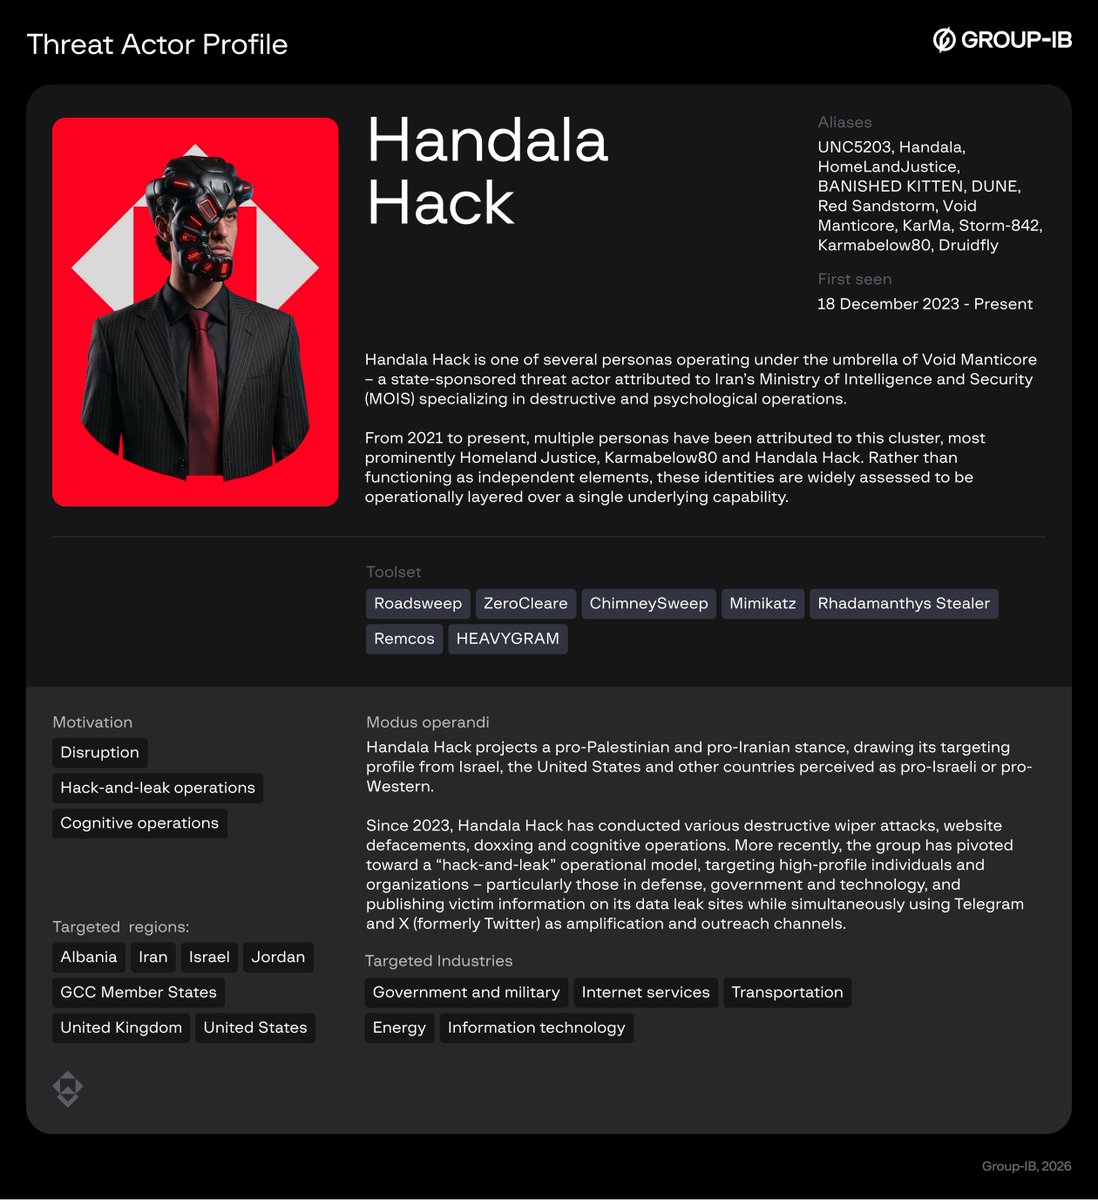
Group-IB #ThreatIntelligence uncovered 29 new samples associated with #HEAVYGRAM and #CRUDEEXCLUDE, expanding the technical picture of a multi-stage intrusion chain attributed with moderate confidence to #HandalaHack. The malware has been used since 2023 and targets include Iranian dissidents, journalists and others viewed as opposing the Iranian government.



Iranian state spyware hides in fake Telegram/WhatsApp app installs - and can fully wipe your device. https://t.co/e4OtQMQr7J #ThreatIntel #CHOSEN #HEAVYGRAM #telegram

Iranian spies sent a fake MRI scan to plant Windows spyware that records your mic and screen. https://t.co/QFzTVz79XV #ThreatIntel #CHOSEN #HEAVYGRAM #telegram
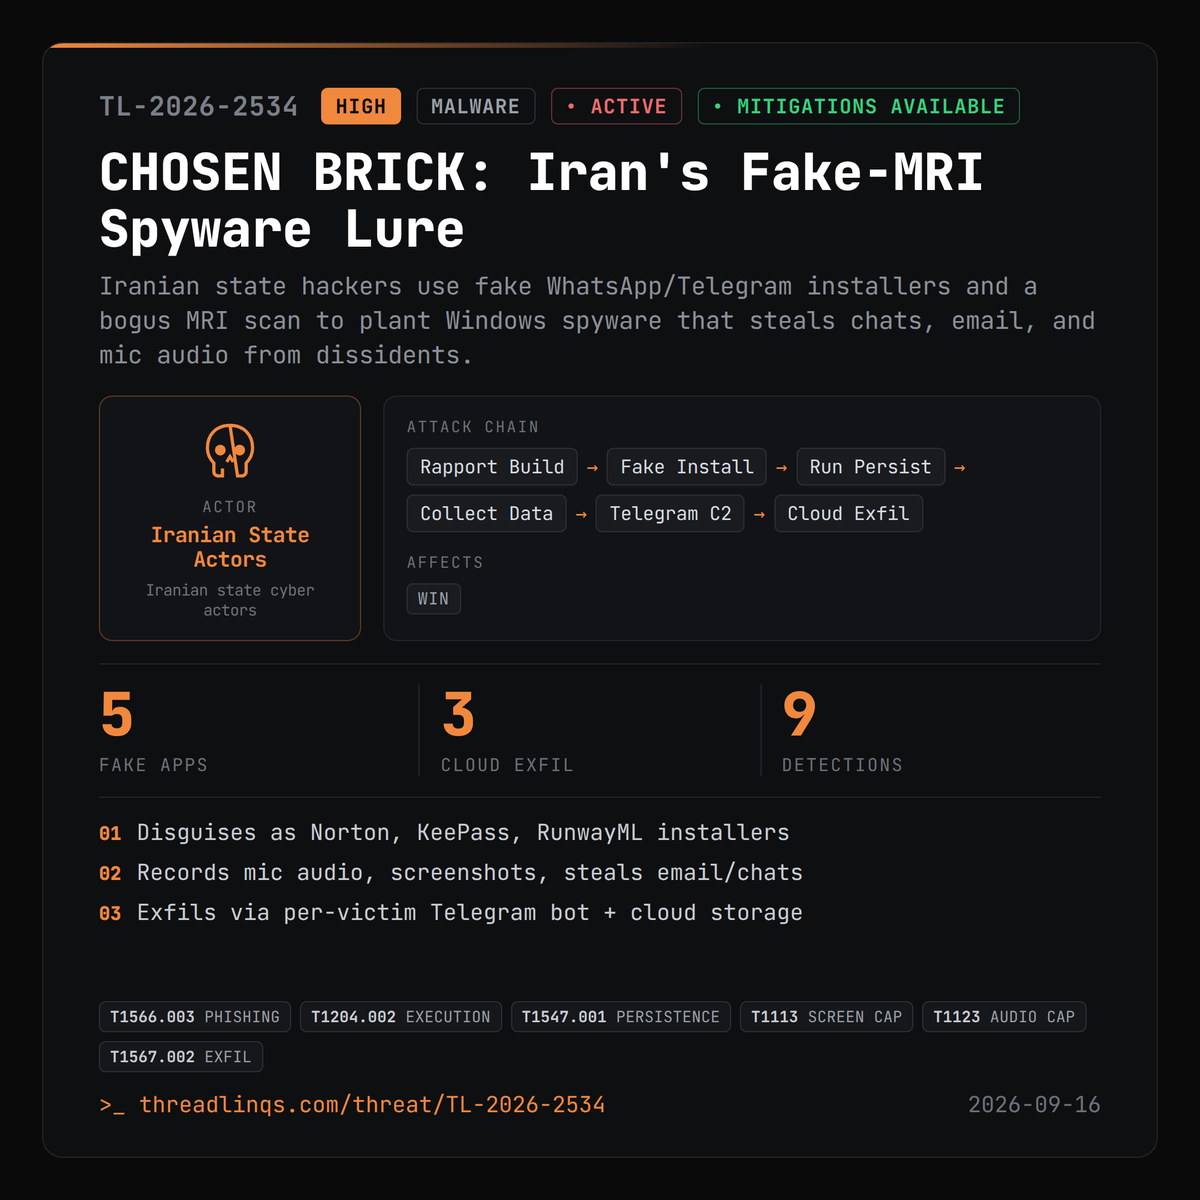

SECURITY ALERT: Iran's HEAVYGRAM Malware
The FBI, UK NCSC, and Netherlands AIVD issued a joint advisory on HEAVYGRAM (CHOSEN BRICK).
Read more: https://t.co/aYnsVDaEP9
#HEAVYGRAM #CHOSENBRICK #Iran #MOIS #Telegram #Malware #NCSC #FBI #InfoSec #ThreatIntel

Iran-linked HEAVYGRAM and CHOSEN BRICK malware uses Telegram to spy on dissidents, journalists, and activists, stealing messages, screenshots, passwords, and audio. #Iran #HEAVYGRAM #Telegram
https://t.co/MlhuSMfboP
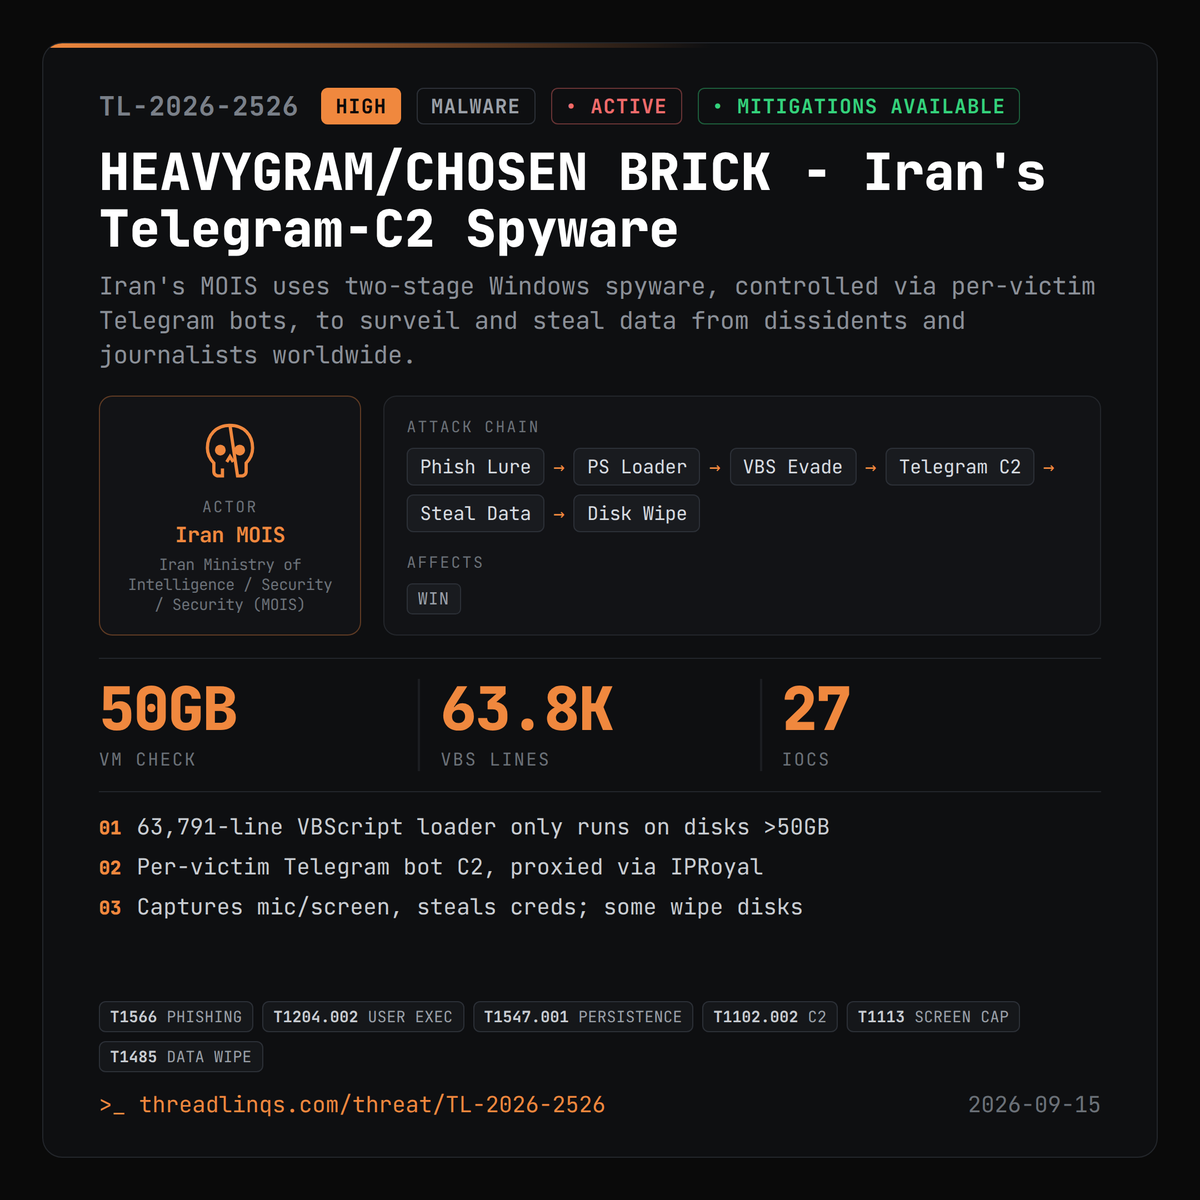
Iran's MOIS turned Telegram into a spyware C2 channel to hunt dissidents and journalists. https://t.co/aHenbtFdpT #ThreatIntel #HEAVYGRAM #CHOSEN #ChosenBrick
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.7M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.4M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
83.9M followers

Lady Gaga
@ladygaga
75.4M followers

Virat Kohli
@imvkohli
73.3M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.3M followers

Bill Gates
@billgates
65.1M followers

Selena Gomez
@selenagomez
63M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers