

Top Tweets for #Socks5systemz

ThreatProtection New malware campaigns are leveraging an updated #Socks5Systemz #botnet with enhanced obfuscation and C2 infrastructure, powering criminal proxy services. Read more about Symantec's protection: https://t.co/Wkj6MCnupF #Cybersecurity

New blog with an update on the Socks5Systemz botnet with some interesting details! https://t.co/Drr5O0f293 #socks5systemz #proxyam

#Socks5Systemz detection rule is found!
also 5 different filetypes have been observed to be used
online.exe
soon.exe
off.exe
job.exe
crt.exe
Detection rule used:
https://t.co/6fEo3zYvBB
cc: @500mk500 @thehappydinoa @abuse_ch @Wafer4014 @NDA0E
https://t.co/qegfdbZcFI


Payload statistics from August 2024 📊 We observed 593 tasks distributed by threat actors across the tracked botnets. This resulted in 3825 unique payloads.
Top families:
1. #StealC
2. #Amadey
3. #Socks5Systemz
4. #SmokeLoader
5. #VidarStealer
Unpack and detection: @unpacme


🚨 Join us for a webinar on the latest updates in #ThreatDetection! https://t.co/zxi5tHsKzG
🔍 Unveiling #Stealc #infostealer, and #Latrodectus #downloader
🛡️ #YARA Rules targeting #Kematian stealer, #Socks5Systemz, #FakeBat, #STRRAT, and latest #Lumma variants.
and more.
#malware #phishing #malwareanalysis
https://t.co/zxi5tHsKzG

Payload statistics from July 2024 📊
We observed 459 tasks distributed by threat actors across the tracked botnets. This resulted in 4262 unique payloads.
Top families:
1. #Socks5Systemz
2. #StealC
3. #SmokeLoader
4. #Amadey
5. #Tofsee
Unpacking and detection: @unpacme 🤝


#Socks5Systemz bad guy stuff. Was hunting down a different "fake" installer that was holding mal code and found this instead. Just a simple google search to find it.
https://t.co/29UOgVNeLR
I would block:
totrakto[.]com
soneservice[.]shop
95[.]163[.]241[.]63
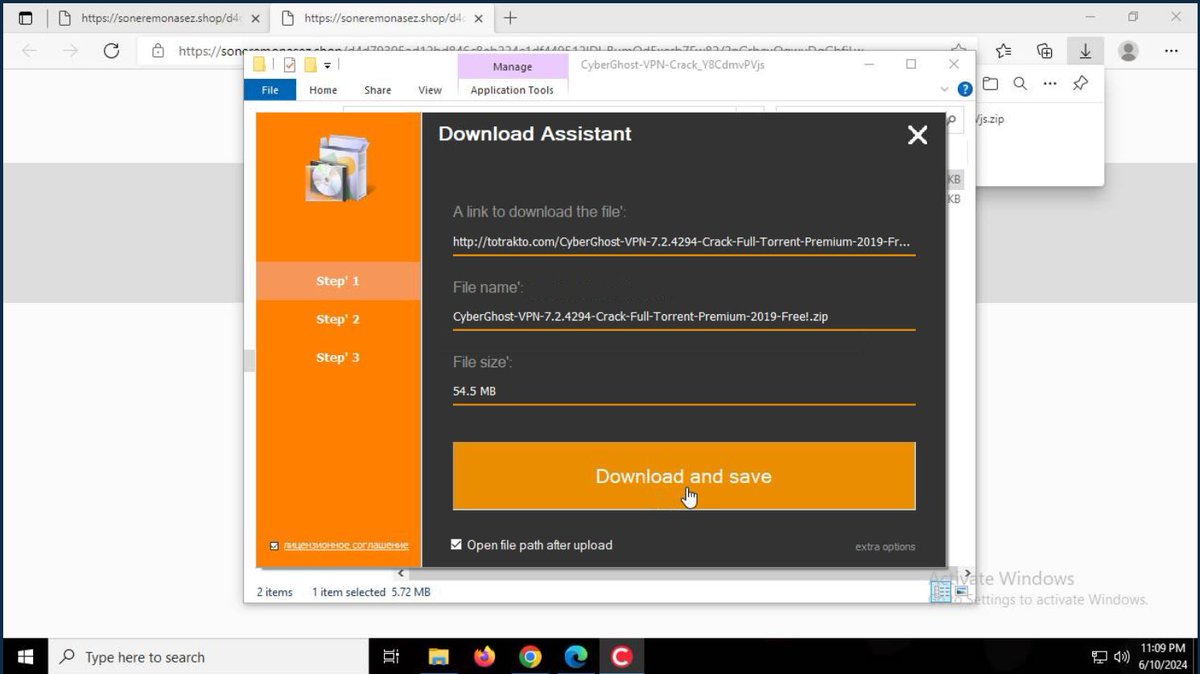
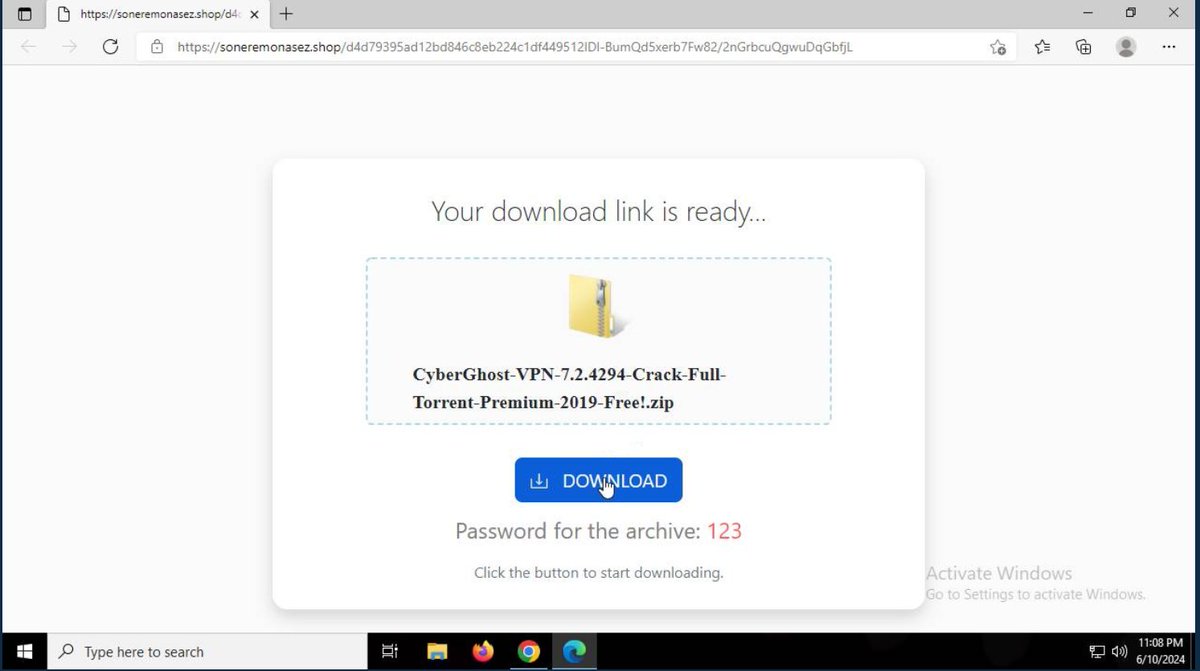
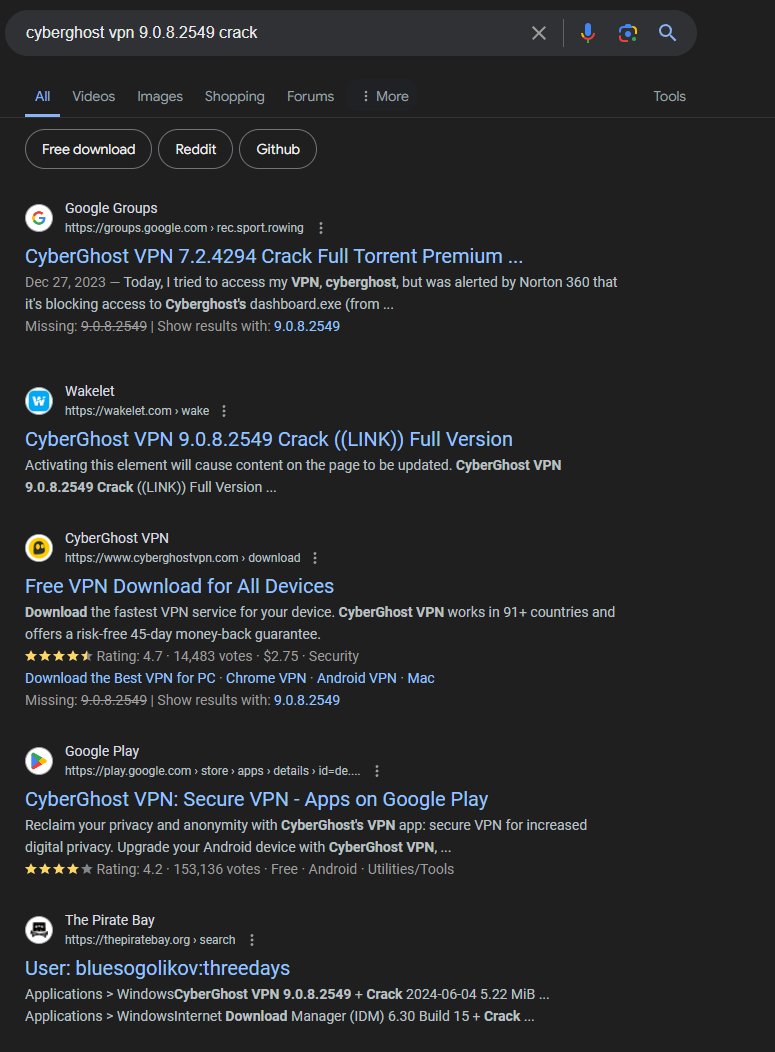
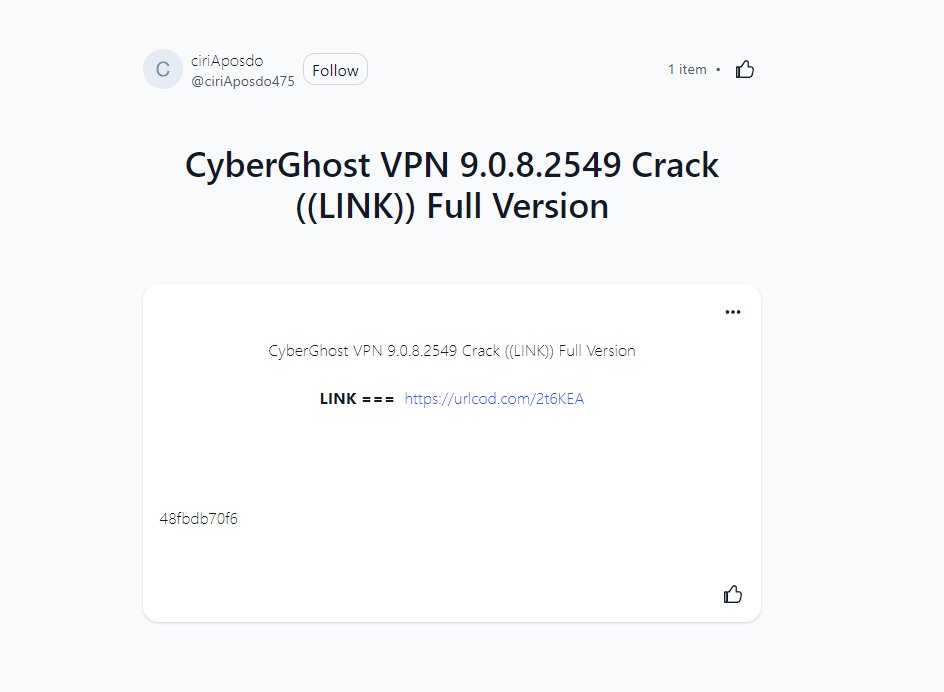

Unlike #botnets that launch #DDoS attacks, #Socks5Systemz specializes in traffic forwarding 🤖
With thousands of devices currently infected, it's important to know how it operates.
Learn more and collect its latest #IOCs and samples ⬇️
https://t.co/WUebWn2xtv

Massive #Socks5Systemz proxy botnet campaign against #Hungarian targets (using weaponized TeamViewer) @500mk500 @whitehoodie4
Samples: https://t.co/kBU8v0FkgP
https://t.co/5JijLxxUGq
https://t.co/yJBj0Yvamx
https://t.co/vxfG8iQimi

Quite a bit of malicious activity at 185.196.8[.22 hosting #Socks5Systemz e.g.: bwodlpc[.com/click/?counter=[ID]
id0032[.online
08schedule[.online
bogodej[.com
ddbzxgg[.info
[..]
![peterkruse's tweet photo. Quite a bit of malicious activity at 185.196.8[.22 hosting #Socks5Systemz e.g.: bwodlpc[.com/click/?counter=[ID]
id0032[.online
08schedule[.online
bogodej[.com
ddbzxgg[.info
[..] https://t.co/lIZ4woSZBm](https://pbs.twimg.com/media/GBaR1h2WYAAg9-v.png)

#socks5systemz C2 IP: 69.30.233[.]162
Sandbox: https://t.co/rd7nn5BEOz
Also a lot of DGA domains:
https://t.co/Gt20BW6xeD
For reference used:
https://t.co/0N360kpaLR
cc: @500mk500 @malwrhunterteam


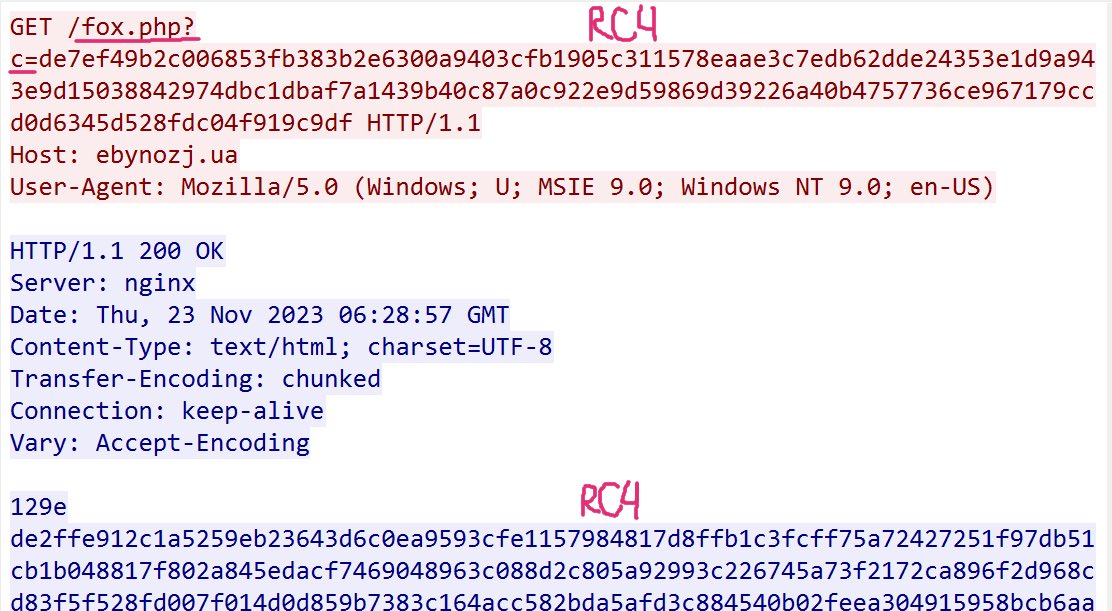
New #rc4 key & HTTP URI found in ProxyBot #Socks5Systemz described earlier in https://t.co/mC1mm5IlEa 👾
C2: 88.80.147[.]36:1074
https://t.co/Ee0G4yT2Of
https://t.co/6cf05gHPiG
Thanks @4ekin !
5 interesting #malware threats @Jane_0sint discovered in November 👩💼
🔹 #Steganography
🔹 #Tycoon platform using WebSocket to communicate
🔹 #Ransomware research that fell into the wrong hands
🔹 #socks5systemz malware used to proxy traffic
More 🔽 https://t.co/LMmvLgdM7f
#ANYRUN_insights

The #Socks5System Proxy Bot Traffic Analysis
Utilizes two types of C2 connections for communication, the proxy bot distributes roles between two servers:
- HTTP/80 C2 connection
- TCP/1074 Сlient connection streams and proxy server commands
Link to the sample ↘️
https://t.co/k0BxwFQlMy
The C2 connection diagram can be found in our last post ↘️
https://t.co/pw2Jk3mPFx
The Socks5System proxy bot binds TCP/1074 sockets to communicate with the proxy server. The first packet one byte long determines the type of command being sent: 0x00, 0x01 or 0x02.
An alive command connection on TCP/1074 conveys messages from the server describing client streams, structured as follows:
🟥 Address type (IP/domain)
🟩 Destination address (IP/domain)
🟧 Destination Port
🟪 Connection ID
Upon receiving server commands, the proxy bot performs the following actions:
1⃣ Sends a 0x01 command packet type to the TCP/1074
2⃣ Sends a 10-byte packet with the client connection ID inside
3⃣ Relays data from the proxy-server clients to the internet
This scheme of interaction with two servers allows the proxy bot to remain online with C2 to update proxy addresses and with the proxy to receive new client streams.
Also stay tuned and check out the new samples at the tag link ↘️
https://t.co/cBxL1RKkIE

New #rc4 key & HTTP URI found in ProxyBot #Socks5Systemz described earlier in https://t.co/mC1mm5IlEa 👾
C2: 88.80.147[.]36:1074
https://t.co/Ee0G4yT2Of
https://t.co/6cf05gHPiG
Thanks @4ekin !
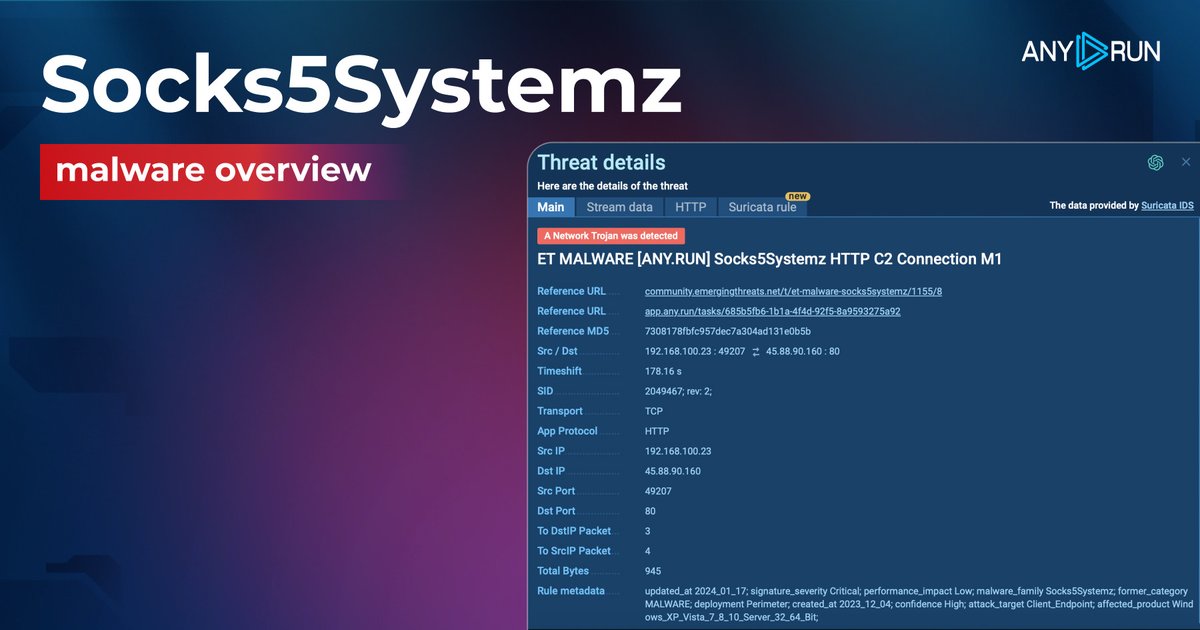
#socks5systemz is a #malware that turns victims’ devices into proxies for forwarding traffic
It was first spotted by our sandbox 3 years ago 👉https://t.co/tzTinSxxbP
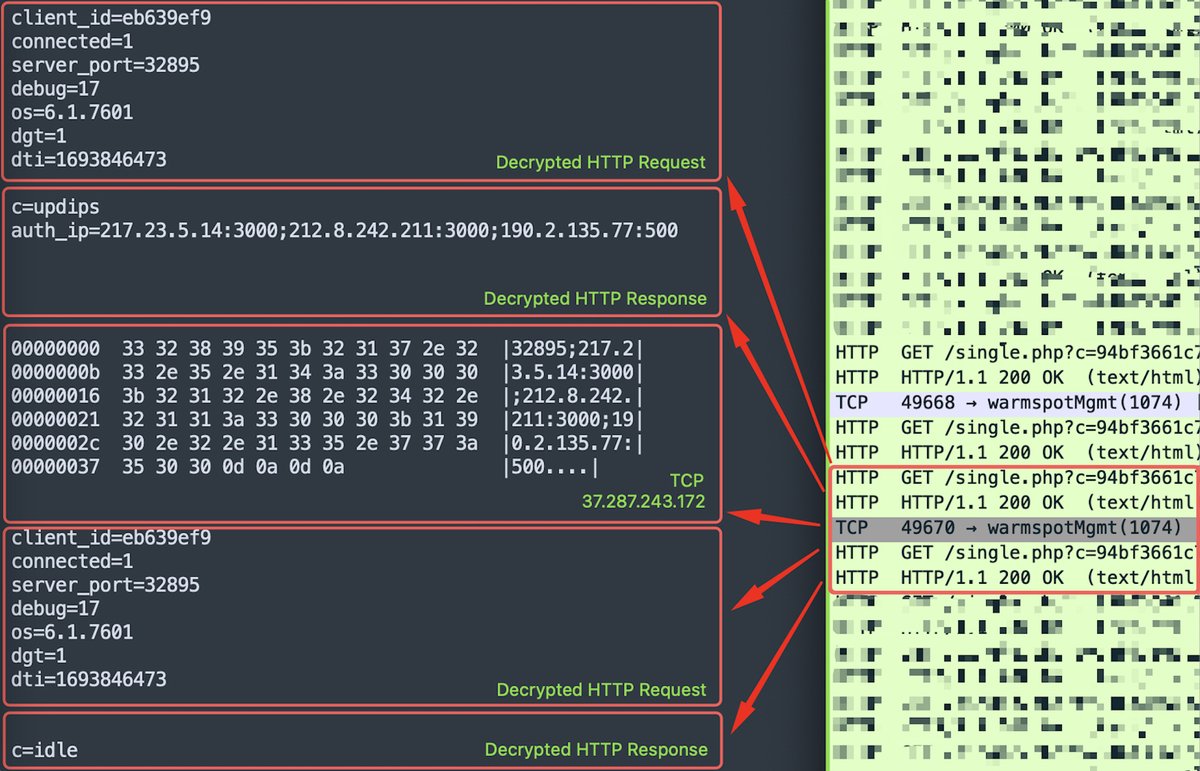
🔹It attempts to connect via HTTP request to port 80 and a backconnect server over port 1074/TCP.
▪️By combining these two connections for the connect and updips commands, we illustrate how socks5systemz can be used to proxy traffic.
Follow the tag link 👉 https://t.co/n0pq4BZ6fI
🔸You can also find socks5systemz in the public database using the signature 2829008.
▫️Here is a #CyberChef recipe for decrypting command connections 👉https://t.co/OqdZYPQ7R7

#ThreatProtection #Socks5Systemz, a new #proxy #botnet has been discovered in the wild, read more about Symantec's protection: https://t.co/9clAGsvQ9U

The C2 protocol in BitSight’s "Unveiling Socks5Systemz" report is identical to what’s described by DrWEB in a blog post from 2016 about BackDoor.TeamViewer.49. They even use the same RC4 encryption key "heyfg645fdhwi"!
#Socks5Systemz #TeamSpy
https://t.co/E0fqBRyvTX

A proxy botnet called 'Socks5Systemz' has been infecting computers worldwide via the 'PrivateLoader' and 'Amadey' malware loaders, currently counting 10,000 infected devices.
https://t.co/IVdZcrZdEt
#botnet #Socks5Systemz #cybersecurity #threatresq

Embrace the future with #SOCKS5Systemz! 🚀 Bitsight’s Threat Research team recently discovered a new malware sample distributed by the PrivateLoader and Amadey loaders. Discover more: https://t.co/pN4iixMKl0
#Privateloader #Amadey #ProxyService #ProxySecurity


Hunting #Socks5Systemz panels rel. to #TeamSpy with FOFA
title=="Phichichi" && fid="hC3Y75PtrHXEGYlvOGjMNw=="
/185.141.63.172/auth.php
/109.236.85.145/auth.php
/193.242.211.141/auth.php
/109.230.199.181/auth.php
/212.8.242.211/auth.php
dead panel
/178.32.216.234/
@ViriBack


Last Seen Hashtags on Sotwe
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.4M followers

Kim Kardashian
@kimkardashian
70.8M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.4M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers