

Top Tweets for #StopRansomWare

New study: What CISA’s own ransomware advisories name: a census of the #StopRansomware series
Read the study: https://t.co/ZdVhXZdQvp
#Ransomware #CISA

Desmantelan a KillSec/killsecurity/KillSec3 ransomware, el lider tendría 16 años.. #Stopransomware #KillSec #ransomware
https://t.co/AzYpIHt4vW
Operador del ransomware Ryuk recibe una condena de 2 años #StopRansomware #ransomware #cybersecurity #Ryuk
https://t.co/OVPDZS7S7p
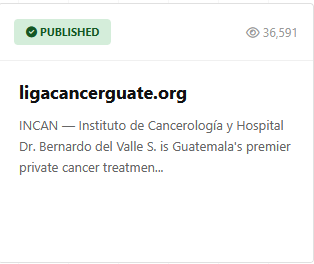
🔴🇬🇹Recordemos que el grupo KryBit fue el que listó al hospital en su sitio DLS y describió que habían robado 78.11 GB de información. Además, en la lista de archivos se pueden observar datos personales y sensibles de salud de pacientes.
#ransomware #StopRansomware #KryBit #Guatemala #ciberseguridad
Un ciudadano ucraniano ha sido condenado a cuatro años de prisión por su participación en los ataques de ransomware Conti entre 2021 y 2022.
#Conti #Ransomware #cybersecurity #StopRansomware
https://t.co/6i1U9q3aYg

#threatreport #HighCompleteness
#StopRansomware: Medusa Ransomware | 18-08-2026
Source: https://t.co/laIsJgK3sG
Key details below ↓
🧑💻Actors/Campaigns:
Spearwing
💀Threats:
Medusa_ransomware, Screenconnect_tool, Beyondtrust_tool, Interactsh_tool, Lolbin_technique, Minidump_tool, Rclone_tool, Ligolo-ng_tool, Cloudflared_tool, Nezha_tool, Meshagent_tool, Meshcentral_tool, Gsocket_tool, Gs-netcat, Anydesk_tool, Atera_tool, Ehorus_tool, N-able_tool, Simplehelp_tool, Splashtop_tool, Mimikatz_tool, Vssadmin_tool, Shadow_copies_delete_technique, Crackmapexec_tool, Netexec_tool, Robocopy_tool, Ligolo_tool, Bomgar_tool,
🎯Victims: Medical, Education, Legal, Insurance, Technology, Manufacturing, Healthcare and public health sector
🏭Industry: Healthcare, Critical_infrastructure, Education, E-commerce, Government
🌐Geo: United states
🔓CVEs: CVE-2025-10035 \[[Vulners](https://t.co/5mjrasyr0I)]
- CVSS V3.1: *10.0*,
- Vulners: Exploitation: True
Soft:
- fortra goanywhere_managed_file_transfer (<7.6.3, <7.8.4)
CVE-2024-1709 \[[Vulners](https://t.co/DDyKoz3SZq)]
- CVSS V3.1: *10.0*,
- Vulners: Exploitation: True
Soft:
- connectwise screenconnect (<23.9.8)
CVE-2023-48788 \[[Vulners](https://t.co/eN4a0nwD0c)]
- CVSS V3.1: *9.8*,
- Vulners: Exploitation: True
Soft:
- fortinet forticlient_enterprise_management_server (<7.0.11, <7.2.3)
CVE-2026-1731 \[[Vulners](https://t.co/oPbjFItc64)]
- CVSS V3.1: *9.8*,
- Vulners: Exploitation: True
Soft:
- beyondtrust privileged_remote_access (<25.1)
- beyondtrust remote_support (<25.3.2)
📚TTPs:
⚔️Tactics: 8
🛠️Technics: 29
🧨IOCs:
- Domain: 3
- File: 20
- Command: 4
- IP: 1
- Path: 1
💽Software: GoAnywhere, SoftPerfect Network Scanner, MySQL, Local Security Authority, Windows Defender, Linux, PsExec, Active Directory, Bandizip, Sysinternals PsExec, ...
🪙Crypto: bitcoin
🔢Algorithms: base64, aes-256, gzip
📜Programming Languages: python, php, powershell
#threatreport:
Medusa is a ransomware-as-a-service (RaaS) operation active since 2021 and using affiliates since at least early 2023. By April 2026, Medusa actors had affected more than 500 victims, including organizations in healthcare, education, legal, insurance, technology, and manufacturing. The operation uses double extortion: files are encrypted and stolen data is threatened with publication on a Tor-based leak site. Healthcare and Public Health organizations have been frequently targeted, although the actors generally operate opportunistically against organizations with exposed or unpatched systems.
Initial access is commonly obtained through phishing, stolen credentials, and exploitation of internet-facing vulnerabilities. Reported targets include ScreenConnect CVE-2024-1709, Fortinet EMS CVE-2023-48788, Fortra GoAnywhere CVE-2025-10035, and BeyondTrust CVE-2026-1731. Medusa actors reportedly exploit newly disclosed vulnerabilities rapidly, sometimes within 24 hours, and use Interactsh domains such as oast[.]site, oast[.]pro, and oast[.]fun to verify successful exploitation and identify compromised hosts.
After gaining access, the actors perform network and filesystem discovery using PowerShell, Windows Command Prompt, WMI, Advanced IP Scanner, SoftPerfect Network Scanner, and CrackMapExec/NetExec. They use RDP, PsExec, and legitimate remote-monitoring tools including AnyDesk, Atera, ConnectWise, eHorus, N-able, BeyondTrust, SimpleHelp, and Splashtop for lateral movement. Credential theft techniques include Mimikatz, LSASS dumping through Task Manager or comsvcs.dll, plaintext credential capture with mimilib.dll, and extraction of ntds.dit and registry hives from Volume Shadow Copies.
For stealth and persistence, Medusa actors use encoded PowerShell, certutil, deleted PowerShell history, vulnerable or signed drivers to disable EDR, and tools placed in Windows Defender exclusion folders. Observed C2 and remote-access tooling includes Ligolo-ng, Cloudflared, Nezha, MeshAgent, GSocket, web shells, and Linux reverse shells.
Data is archived with Bandizip and exfiltrated using Rclone, sometimes renamed to evade detection, while small files may be transferred through RDP clipboard functionality. The encryptor, gaze.exe on Windows and https://t.co/KFKlYAWM5a on Linux, is deployed through PsExec, PDQ Deploy, BigFix, or SFTP. It stops security, backup, database, and other services, deletes shadow copies, encrypts files with AES-256 using the `.medusa` extension, and can power off virtual machines. Ransom demands are typically requested in Bitcoin and require contact within 48 hours, with additional threats to sell or publish stolen data.


#StopRansomware
The #FBI, Cybersecurity and Infrastructure Security Agency (CISA), and U.S. Department of Health and Human Services (HHS) are releasing a new updated joint advisory to disseminate known Medusa ransomware tactics, techniques, and procedures and indicators of
compromise identified through FBI investigations as recently as April 2026.
Medusa is a ransomware-as-a-service (RaaS) variant first identified in June 2021.
Both Medusa developers and affiliates use a double-extortion model where they
encrypt victim data and threaten to publicly release exfiltrated data if a ransom is
not paid.
Learn more here: https://t.co/0KJemaPk8y


CISA and five agencies warn that Gunra ransomware is hitting critical infrastructure with double extortion. A Linux flaw may let victims recover free.
#GunraRansomware #Ransomware #CISA #StopRansomware #Conti #CriticalInfrastructure #Cybersecurity
https://t.co/bAn5z7n46A

CISA: Six-nation #StopRansomware advisory on Gunra, a fast-professionalizing Conti-derived RaaS (alias "Golden Community") hitting government and critical infrastructure globally with double extortion and demands in the tens of millions. https://t.co/9BhUQjUPXm

🚨🇺🇸 U.S. Agencies Issue Joint #StopRansomware Advisory on Gunra Ransomware
The FBI, CISA, NSA, U.S. Secret Service, DoD Cyber Crime Center (DC3), and South Korea’s National Police Agency have released a new joint cybersecurity advisory detailing the emerging Gunra ransomware threat.
Gunra first appeared in April 2025 and evolved into a structured Ransomware-as-a-Service (RaaS) operation in early 2026. The group reportedly operates under additional branding, including “Golden Community,” and recruits affiliates and initial-access specialists through dark web forums.
🔍 Key findings:
* Gunra is based on or heavily influenced by the leaked Conti ransomware source code.
* Initial access has included exploitation of internet-facing firewall/VPN infrastructure, including CVE-2024-55591 and CVE-2025-24472 affecting FortiOS/FortiProxy.
* Operators have abused default credentials, stolen VPN/VDI sessions and modified authentication systems to bypass MFA.
* Gunra uses Impacket tools including https://t.co/mMs571Rgr8, https://t.co/YPzBGej3ML and https://t.co/SjGy8LxEmH for lateral movement and credential dumping.
* Observed exfiltration includes OneDrive and SharePoint data, with some incidents involving tens of terabytes.
* Tools observed include RClone, FileZilla, 7-Zip, WinRAR, Sliver, Mimikatz, AnyDesk and others.
* Windows and Linux ransomware variants have been observed.
* Windows encryption uses ChaCha20 + RSA-4096 and typically appends the .ENCRT extension.
* Attackers have deleted volume shadow copies and, in at least one incident, destroyed backup/archive data at both primary and disaster-recovery sites.
* Gunra uses double extortion: steal the data, encrypt systems, then threaten publication or sale through its leak infrastructure.
⚠️ Particularly notable: researchers identified a weakness in certain Gunra Linux variants that may allow encryption keys to be reconstructed using file timestamps, potentially enabling recovery without paying a ransom.
🛡️ The agencies recommend prioritizing patches for exploited internet-facing systems, enforcing MFA, auditing privileged accounts, segmenting networks, maintaining tested offline/immutable backups, and validating defenses against Gunra’s mapped MITRE ATT&CK techniques.
Analyst Note: Gunra’s evolution from a ransomware variant into an affiliate-driven RaaS operation is important. The advisory shows an intrusion chain extending well beyond encryption—edge-device exploitation → credential/session theft → MFA bypass → lateral movement → cloud data theft → backup destruction → ransomware deployment.
Source: Joint Cybersecurity Advisory AA26-222A — August 10, 2026
#DDW #Ransomware #CyberSecurity #Gunra
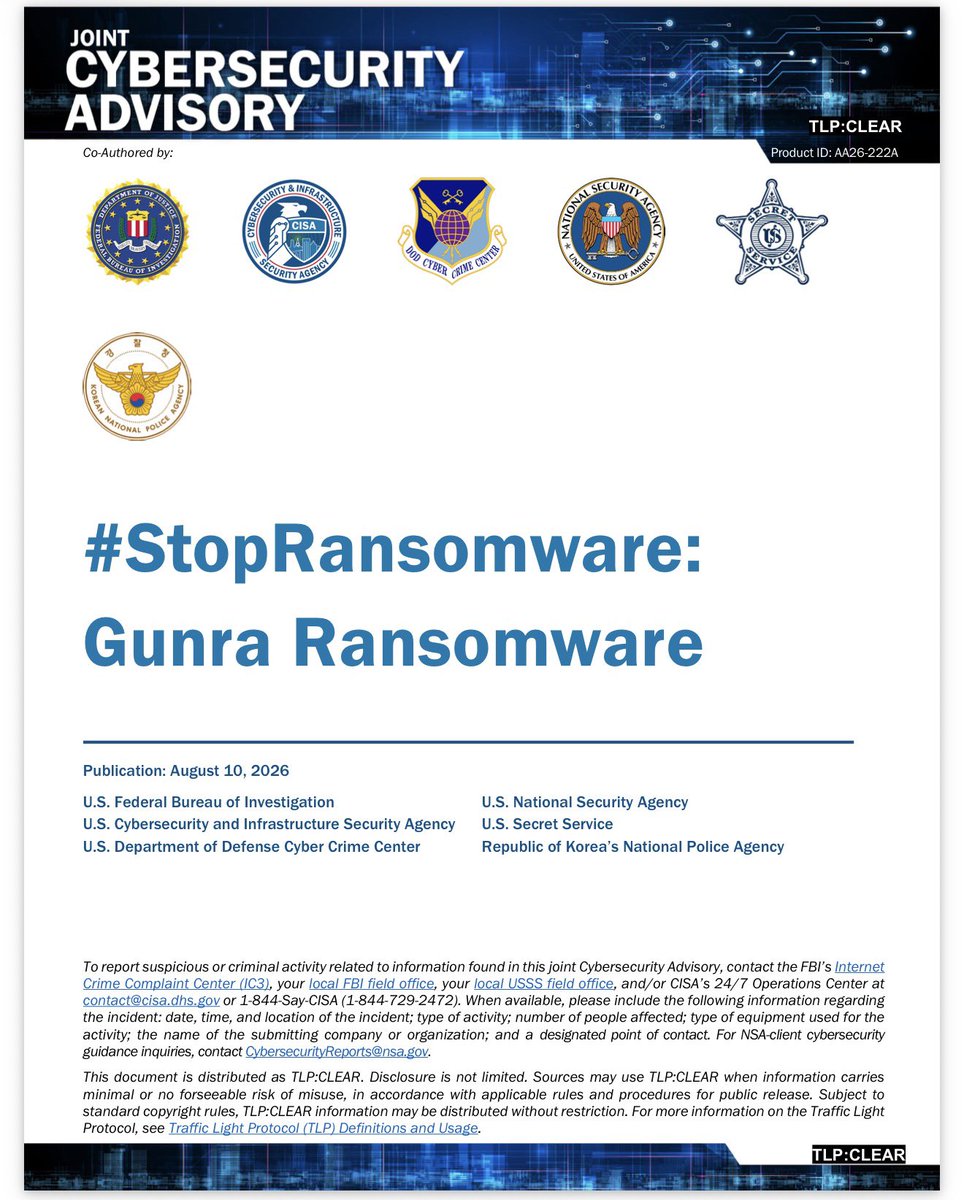

#StopRansomware: Gunra Ransomware https://t.co/8kWdfJtlEN
2025年に日本の複数企業もターゲットにしてたアクターでしたよね

Our new #Stopransomware joint advisory with @FBICyberDiv and partners details Gunra ransomware threat activity + detection & mitigation guidance to help protect your org from this double-extortion variant. Learn more 👉 https://t.co/qTQjwSdVdY


NSA joins the @FBI and others in releasing a joint Cybersecurity Advisory, “#StopRansomware: Gunra Ransomware,” as an ongoing effort to publish information about various ransomware variants and threat actors. Learn more: https://t.co/1gi9DRjwdY


According to our investigation, the artifacts and infrastructure overlap with Interlock activity. We observed the use of #NodeSnake RAT and Interlock RAT, both of which are referenced in CISA’s #StopRansomware advisory. https://t.co/J5UdNBN5s9 2/7

Spot on quiz, @elormkdaniel
! The absolute first step is C: Disconnect infected systems from the network.Why? Immediate isolation contains the spread, ransomware often moves laterally fast, encrypting more files or exfiltrating data. CISA's #StopRansomware Guide.

Your organization has been hit by a ransomware attack. Critical systems are locked, and a message demands payment in Bitcoin.
Question:
What should be your first step?
A. Pay the ransom to quickly recover data
B. Attempt to decrypt files using random tools
C. Disconnect infected systems from the network
D. Contact the attackers for negotiation
@elormkdaniel Spot on quiz, @elormkdaniel
! The absolute first step is C: Disconnect infected systems from the network.Why? Immediate isolation contains the spread, ransomware often moves laterally fast, encrypting more files or exfiltrating data, CISA's #StopRansomware Guide.

DC3 has partnered with @FBI, @CISAgov, @HHSgov and global allies to #StopRansomware. Explore our joint #cybersecurity advisory on #AkiraRansomware for key #TTPs & #IOCs to help protect orgs and critical infrastructure from this ongoing threat. https://t.co/RKrRdRqvML

🚀@CISAgov & our partners have released updated guidance to protect organizations against an uptick in Akira ransomware attacks. Read this important #StopRansomware advisory. https://t.co/U70Pv2I4Ee


REMINDER: Malicious cyber actors don’t take vacations. Ahead of Labor Day weekend, school personnel can brush up on info & recs to protect against ransomware attacks with the #StopRansomware Guide: https://t.co/X3B5HmZfNH
Last Seen Hashtags on Sotwe
sleepingsister
Seen from France
Galataawards
Seen from United States
snapchat
Seen from United States
กางเกงในใช้แล้ว
Seen from Thailand
Jailer2
Seen from India
ibubugil
Seen from Malaysia
น้องมินตรา
Seen from Thailand
AnáliseEstrutural
Seen from United States
leak
Seen from France
somosGigante
Seen from United States
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.8M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.6M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90.1M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.3M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers