Azure Outlook Command & Control that uses Microsoft Graph API for C2 communications & data exfiltration. Couldn't get it to work with Cobalt Strike due to having to refresh the JWT, so I built my own simple beacon for this PoC. Will be posting on GitHub ;)
THREAD with a couple of interesting bits from @AmnestyTech's new report on what they learned from looking for NSO Group's spyware on phones https://t.co/CG60vx7cRg
New blog post from TAG with details of a North Korean campaign targeting security researchers working on vulnerability research and development.
https://t.co/Ec2TaMMXeQ
Stay safe out there everyone!
#BadBullzVenom
1) #VenomLNK -> 2) XML/JS pulled from ddy7itsuemb9i[.]cloudfront[.]net -> 3) #TerraLoader
Use of anti-sandbox techniques to prevent further analysis. I was unable to get the last stage i.e. #more_eggs
d04a0a43777452d0fc85c9c084b165a3 @VK_Intel
#FIN7#RubberDucky
File Rubber Ducky file uploaded from India. C2 reported by @SpiderLabs in March
Hash: aaabd97e378541c5eff9ebb7c50dd17981d9434b
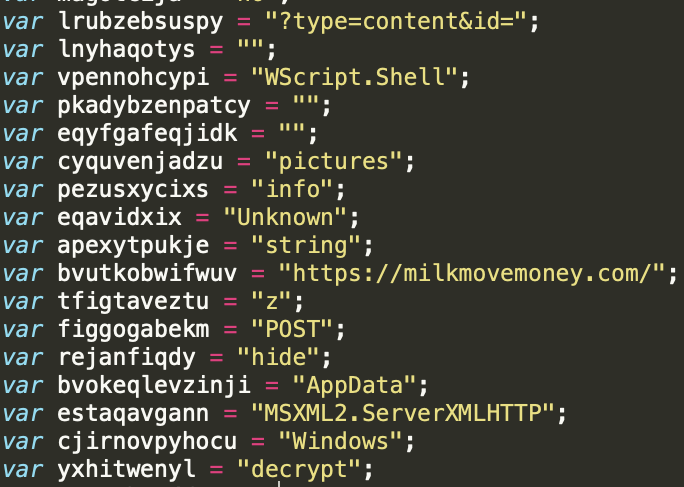
C2: milkmovemoney[.]com
More details here: https://t.co/ySprbWxDaP
#APT33#PoshC2
Potential APT33 PoshC2 Powershell payload uploaded from UK. Probably someone is already trying to analyse it.
C2:investersalliance[.]net
MD5: 230ca8d0a05178ac69d34e802f1d949d
Checkout previous APT33 PoshC2 analysis by @Arkbird_SOLG here - https://t.co/ZEi4MQ8UZw
@vivekramac@Ch33r10 It could be a BIN attack if the cards are from same BIN number. They are probably using your gateway to just validate card numbers for a bigger transaction fraud.
#FIN7#JSSLoader#Malware
C2: spacemetic[.]com
MD5: 51db6352da13bdafe2a302386ae80a93
Probably used in March/April campaign
Loved this part - PathC:\Work2\2020\Z\JSS4\JSS\obj\Release\FApplication.pdb
@James_inthe_box
#FIN7#Carbanak#BIOLOAD
New sample uploaded to VT looks a lot like Carbanak backdoor.
MD5: cab6967687d78971109d322ba70e07b5
C2: 94[.]158.245.141
It's possibly a payload from BIOLOAD loader documented by Fortinet.
#APT33#PoshC2#Iran
Possible APT33 campaign.
C2: microsoft-support[.]servehttp[.]com
Kill switch Date: "01/06/2020"
MD5: 1de42fcd254779f6c9a41bfed895d739
Similar to some good analysis done by @Arkbird_SOLG
here -https://t.co/ZEi4MQ8UZw
@hadianjazi Another file that you may have missed with same C2: 107[.]175.64.251
1c41fcc012a4fe3f8f5d159d5225ad0bdcd160578a4dc3a0699b7e6b5eb08d9a
Filename: third_islamic_unity_conference.doc
Interestingly Islamic Unity Conferences happen in #Iran#TransparentTribe
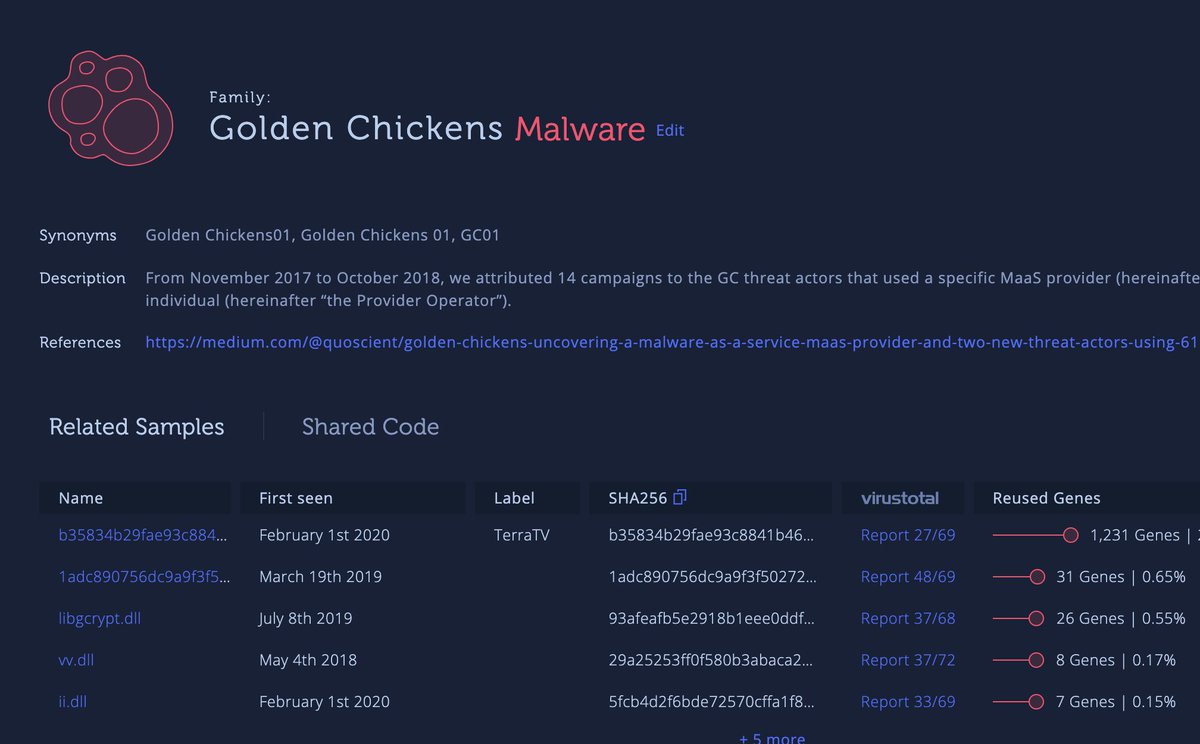
New TerraTV sample (part of the #GoldenChickens MaaS suite) with low VT detection rate, a rather consistent trend for Golden Chickens malware:
https://t.co/NkHByuBBvI
I am looking for some help in grabbing DNS banners on TCP/UDP 53. I can't see any support for DNS protocol using zgrab2. Masscan does not seem to return the DNS banners. @zakirbpd Anything that you can assist please?#zmap#zgrab2#masscan