

Top Tweets for #X64dbg

x64dbg is an open-source Windows debugger used for reverse engineering and malware analysis. It helps inspect assembly, registers, memory, and program execution.
#Cybersecurity #x64dbg #ReverseEngineering #MalwareAnalysis
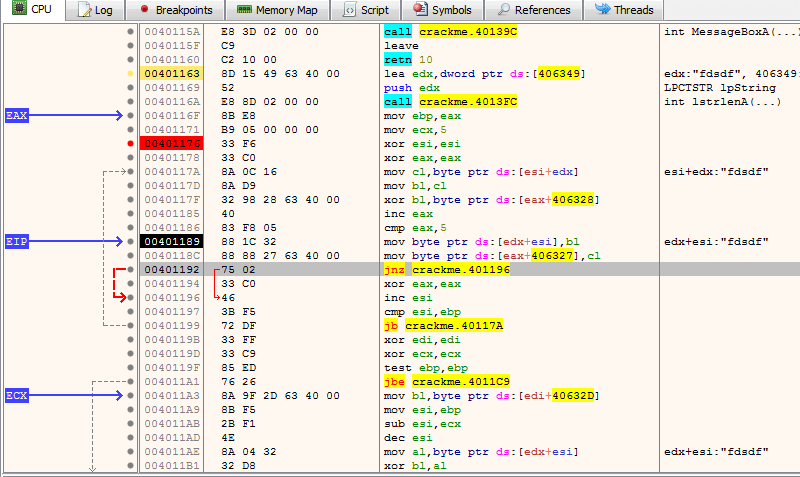
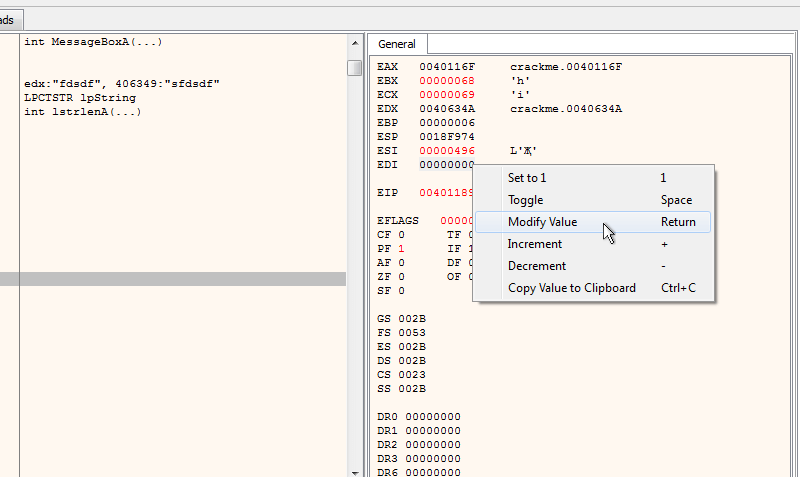
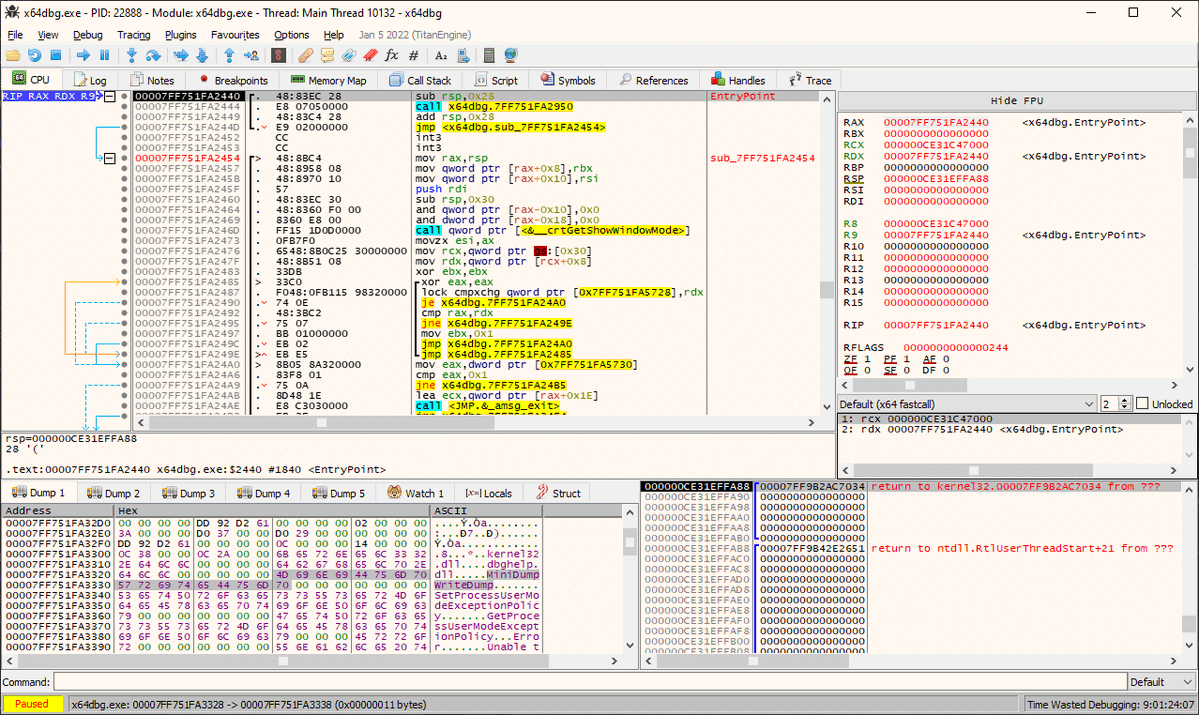

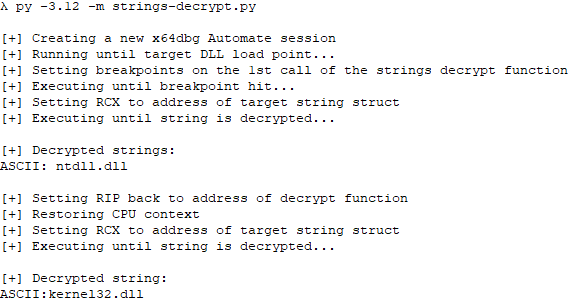
Anyone use #x64dbg-automate for automating malware debugging workflows? I've been playing around with it for unpacking and decrypting strings and it's very useful. Especially when code emulation isn't viable for whatever reason.
https://t.co/jou0qmlwgr

Very nice combo of the best tools used to fully dissect this one nice piece! 💯
➡️ From #IDA, #x64dbg to #tiny_tracer and #pebear), and more...
I like the way this shows where the #AI limitations are when it comes to this multilayered kind of advanced malware. One would spend much more time with a bunch of MCP servers, lacking expertise and experience, stuck on some layer.
This is where seniority matters more than a subscription plan☝️
Great work @elasticseclabs and @DanielStepanic 💙👑
#advanced #malware #reversing #FTW

OXLOADER is staging shellcode in the PE .reloc section. Detection rates are low.
New research from Elastic Security Labs.
Legitimate toolchains don't emit code into .reloc. It's a static-analysis red flag, but most engines aren't catching it in practice.
Before dropping the payload, OXLOADER runs 5 checks:
- Emulation: malformed WNetAddConnection2W call, expects ERROR_BAD_NAME (0x43)
- CPU count: 3+ CPUs required
- RAM: 3 GB minimum via GlobalMemoryStatusEx
- Display refresh rate: 20 Hz floor via WMI Win32_VideoController
- Geography: CIS GEOIDs and Russian LANGID excluded
Pass all five, and a copied system DLL gets a new .xtext section injected with the shellcode. DonutLoader wraps the final payload: CASTLESTEALER.
Distributed via Google Ads impersonating Node.js. The ad campaign targeted US-based victims. The advertiser account has since been removed.
Elastic Defend catches the full chain behaviourally. Static engines largely miss it.
Full technical breakdown, YARA rules, and IOCs visit https://t.co/NoA6sCz3Q0 from @DanielStepanic and @k33b0i:


Quick #x64dbg command that sets the BeingDebugged flag in the PEB to 0 - useful for malware that checks if it is being debugged. There are also plugins that do this automatically 😊
memset peb()+2, 00, 1
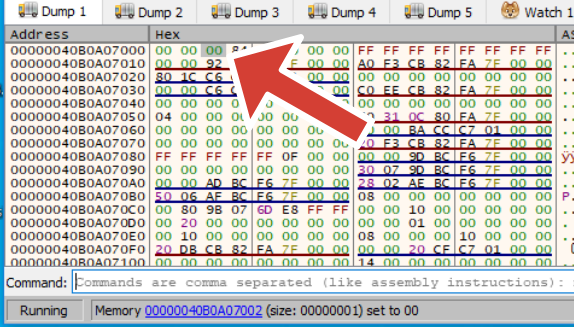
Quick #x64dbg command that sets the BeingDebugged flag in the PEB to 0 - useful for malware that checks if it is being debugged. There are also plugins that do this automatically 😊
memset peb()+2, 00, 1

Today I pushed a majorly overdue feature to #x64dbg Automate and its MCP, remote debugging! Analysis targets can be isolated while driving x64dbg over the network. Full functionality is available over the wire.
Also, Linux client support 🐧🎉


Djuma Mubarak! With @mrexodia at @hack_lu 2025! Thank you for @x64dbg ❤️
#hacking #cybersecurity #malware #malwareanalysis #maldev #research #threatintel #redteam #blueetam #purpleteam #programming #reveng #reverse #x64dbg


Unpacking Malware by Davide Bragetti https://t.co/GgfKOMbDOX
In manual and automated ways
#pe_sieve #tiny_tracer #pe_bear #ida #x64dbg #Pestudio #BareTail #ProcessHacker #UPX

Hello! I just dropped a new article about an old but very up-to-date subject. Please let me know if you find anything incorrect or not well-explained.
https://t.co/Abno7ODe1u
#malwareanalysis #reverseengineering #malcat #x64dbg #pebwalk #shellcode


#Windows #x64 #Assembler with Visual Studio and #x64dbg @mrexodia - this will help you get started on digging into Windows Internals


🧠Learn to Crack Software🧠
Ever wondered how software gets pirated or want to learn how license validation is bypassed with real reverse engineering skills this blog is for you.
👇Read More
https://t.co/E9YayiKWGO
#crackme #reversing #x64dbg #redteam #reverseengineering

Just earned the Certified Exploit Development Professional (CEDP) certification from @cyberwarfarelab
Huge thanks to CyberWarFare Labs for this challenging and rich course!
#ExploitDevelopment #RedTeam #Infosec #BufferOverflow #WinDbg #x64dbg
https://t.co/KQeTrugSdk


11 years after XP's end-of-life we have decided to completely stop supporting operating systems older than Windows 10.
The project will slowly transition to Visual Studio 2022 and Qt 5.15 with CMake, to make it easier for new people to contribute. Exciting updates are coming!


New Video: Writing x64dbg unpacking scripts 🦔 📹
#MalwareAnalysisForHedgehogs #x64dbg
https://t.co/6tLoPSQdWS

در بخش اول قسمت دهم از دوره رایگان مهندسی معکوس نرم افزار، در خصوص ماهیت دستورات منطقی صحبت کردیم. همچنین دستورات NOT و OR و XOR رو در #اسمبلی 32 بیتی و 64 بیتی در دو محیط، ویژوال استدیو و #X64DBG بررسی کردیم.
https://t.co/9VqKvc345y
#ReverseEngineering
#دوره_رایگان_مهندسی_معکوس_نرم_افزار با تمرکز بر درک زبان #اسمبلی و کار با ابزارهایی مانند #X64dbg و #IDAFREE و #WINDBG منتشر شد.
https://t.co/aR8DSTFYZp
Last Seen Hashtags on Sotwe
limpopoboyviralvideo
Seen from South Africa
begÜmpolat
Seen from Turkey
behan incest
Seen from United Kingdom
rechtehatsie
Seen from United States
bursatravesti
Seen from Turkey
Dandadan
Seen from Turkey
snapchat
Seen from Switzerland
มมสนัดเย็ด
Seen from France
仮面ライダーカブト
ชักว่าวแตกใส่
Seen from United States
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.2M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.4M followers

Kim Kardashian
@kimkardashian
70.8M followers

YouTube
@youtube
68.7M followers

Neymar Jr
@neymarjr
66.4M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.6M followers