

Top Tweets for #apt36

One phishing email. One malicious file. A serious security risk.
APT36 highlights how attackers can exploit malicious files and hide activity within encrypted traffic.
Strengthen visibility, threat detection & Zero Trust security with Trident Techlabs.
#Cybersecurity #APT36

Explore how the Operation RapidRust APT36 malware campaign by Zscaler ThreatLabz exposes new tools like RUSTYSHADE and RUSTYMOVE targeting governments.
#OperationRapidRust #APT36 #Cybersecurity #ZscalerThreatLabz #Malware
https://t.co/2LJDzNPB1W

Operation RapidRust: Transparent Tribe (APT36) targets India & Afghanistan govt with new Rust backdoor RUSTYSHADE using private GitHub repos as C2. #APT36 #CyberSecurity #ThreatIntel
https://t.co/HUZAm0Y9ji

Transparent Tribe (APT36) launches a Rust-based backdoor using private GitHub repos as C2 servers, targeting government and defense in South Asia. SOC teams must monitor Rust binaries and GitHub traffic closely. #APT36 #RustLang #ThreatHunting #SOCMinute

Transparent Tribe launched Operation RapidRust against government and defense targets in India and Afghanistan, using Rust backdoors, private GitHub C2, and new tools for stealthy theft and USB propagation. #India #APT36 #RustBackdoor
https://t.co/9LLvAEUKiT

APT36: Operacija RapidRust isporučuje 4 zlonamjerna softvera https://t.co/uiKhj0UsuK
#apt36 #bočnokretanje #cybersecurity #dataexfiltration #githubtoken #malwarecampaign #mrežnaodbrana #operacijarapidrust #psnatch #rustyshade #sajberbezbjednost #usbširenje #zlonamjernisoftver
APT36's Operation RapidRust targeted India and Afghanistan government and defense orgs with RUSTYSHADE, RUSTYMOVE, PSNATCH, and BASHNATCH for encryption, exfiltration, persistence, and USB spread. #APT36 #India #RUSTYSHADE
https://t.co/zeyNr9xSUu

#APT #APT36 #TransparentTribe #CrimsonRAT #threat #malware
📍🇵🇰
💥🇮🇳🌏
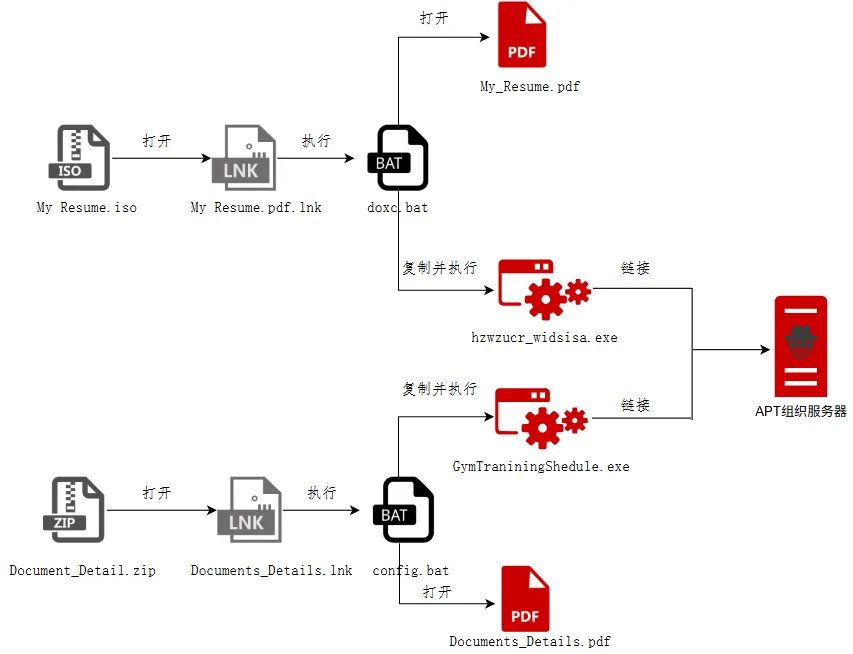
⛓️ #Phishing > #ISO | #ZIP > #LNK (Fake pdf.lnk) > #BAT + cmd.exe > Decoy PDF > Drop in %APPDATA% | Mv LOCALAPPDATA + Self-Delete > Exec payload | RegKey + Startup Persistence > #CrimsonRAT | #Golang #RAT > #C2
🔗360 Advanced Threat Research: https://t.co/YZBsqxOUtW

New instance of malicious Linux desktop entry file used by #APT36 with only 1 detection on VT.
MD5 hash: dc6bf7339f6680086a09d5ad905d8786
Filename: Document Details.desktop
1⃣ Abuses private GitHub for C2. The authentication token is inactive now.
2⃣ Uses timezone check to target India specifically
3⃣ Fetches decoy PDF and next stage payload from private GitHub repo.
Malicious GitHub repository: github[.]com/cqasdgqa-code/
#threatintel
@smica83 @malwrhunterteam


Acronis ties a new PATCHCORD malware APT36 campaign to Afghan telecom and Indian targets. SHEETCORD malware abuses Google Sheets for C2.
#PATCHCORD #APT36 #TransparentTribe #SHEETCORD #Malware #CyberEspionage #InfoSec #ThreatIntel
https://t.co/BcC6XIdCKb

@Acronis #APT36 Suspected in #PATCHCORD Espionage Campaign Using Google Sheets C2
https://t.co/5Sxd9Yktyg
#securityaffairs #hacking #malware

📲 TransparentTribe’s Android Espionage: How APT36 is Siphoning Data Across South Asia
https://t.co/1uUnCc8oYT
#CyberAsia #TransparentTribe #APT36 #AndroidEspionage #SouthAsiaCyberThreat


Sample is now on VT!
🚩Hash: 3e9b3306644b1a4d8c3ac23c7e0d4c7b
🎯Actor name: APT36
🔹Comment: Pakistan-based threat actor APT36, also known as Transparent Tribe, has pivoted from off-the-shelf malware to "vibeware", an AI-driven development model that produces a high-volume, mediocre mass of implants. Using niche languages like Nim, Zig, and...
🌐URL: https://t.co/nJzdHBOjR6
🔎OnVT: https://t.co/4zn1IFXVqw

#APT36 #WhisperLynx
Users/WhisperLynx/Desktop/My creation/My creation/My creation/Creation/Target_update/client/New folder/window_Gym _trainer.go
/api/gym-membership?client_id=%s
/api/exercise-download?exercise=%s
/api/coach-instructions?client_id=%s
#APT36
ZIP> LNK > BAT
1b5d96e5b41d9720a4b35919a807bc34
#Go #AI #Gym
Confirmation Of Availability Form For NDC 61/`/NicUpdatedProtection.txt
41724f263cac4520874765b11027eaa1
#C2
monitorondomainwintgt2[.]store
:15500/api
@PrakkiSathwik @500mk500 @ElementalX2 @polygonben
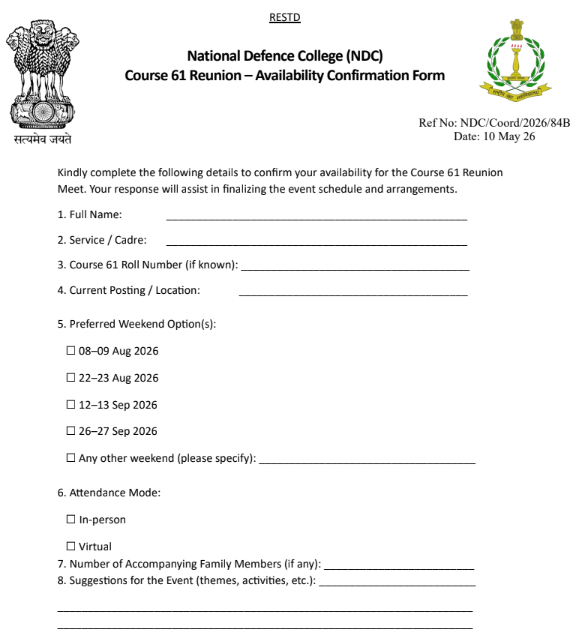


Operation ShadowRecruit targets Indian job seekers with SheetAgent RAT, abusing ControlR and Google Sheets for C2. Seqrite links it to APT36.
#OperationShadowRecruit #APT36 #SheetAgent #Malware #InfoSec
https://t.co/omQtpwDJsU

#CrimsonRAT Payloads of #APT36 / #TransparentTribe
03 File(s): harmalrtbrim.jpg / harmalrtbrim.exe
MD5: 4e433dc08fd86851f3124afd375deb9b
MD5: 14fe42342fd59a116cb86b5d3d980bab
MD5: 11f36387fc925689d3957202726d849a
02 File(s): rthmis voitbum.exe
MD5: 720a742b3f57db44ebeaf6f8d2f7035d
MD5: cf3a70ddcc52aca32ef3fe1c9bb0c980
C2 Infra:
64.188.12[.]144:12246
64.188.12[.]144:15891
wamous.duckdns[.]org
Persistence via Scheduled Task [Name]: "Uploader"
@500mk500 #Malware #ioc #APT #RAT


🎯 The #APT36 🇵🇰 cluster can't stop, won't stop. They just added #CVE-2026-21509 and #CVE-2026-21513 (borrowed from APT28) onto their delivery chain, pushing updated FIREPOWER via weaponized RTF and LNKs against 🇮🇳 targets. Separately, fresh SheetCreep + a shiny new CrystalShell-Slack variant co-dropped on a Kashmir target, because one implant is never enough. The vibeware factory is running three shifts: Crystal, .NET and PowerShell. Stay safe!
IoCs
6df13b336f3daccc29a5f24bd5824f4ae9b4d7c45ee9c9adcd7a36679ee009c5 - CVE-2026-21509
558dd73f708d4ea7b33fec295ac201ee5c76ba293856d8835225538c11ff208e - CVE-2026-21513
9a93231038c7807c7c1376de1546cae94b6778106bb2ef115631da0991adbb91 - FIREPOWER
12335f9a1b7d3b84d2844b42f6f2ae03b70c2cc3d68e6c2dd468ee1ec6b2f3c1 - CrystalShell
3d74a0fb447590ba7c054e6e7c6d182d145651f588aa4de8bf0972461d9652f2 - SheetCreep
SHEETCREEP malware is a C# Google Sheets RAT tied to APT36. It hides command-and-control inside Google Sheets to evade network detection.
#SHEETCREEP #GoogleSheetsRAT #APT36 #TransparentTribe #Malware #Phishing #RAT
https://t.co/1gSlcKsiEo

#APT36 #TransparentTribe
PPT for Breifing at HQ Norther Command(ZIP)
bd260bf220b310ebdd9ab0b50114f627
#Crimson #RAT
c6409e078bad9094ab4b26dad5219f6c
/excel/excel.bat
/excel/office.bat
PPT for Breifing at HQ Norther Command.pptx.lnk
C2: 155.117.45.44
@500mk500 @PrakkiSathwik
Last Seen Hashtags on Sotwe
minichat)(****************filter:videos
Seen from Spain
momsonn
Seen from United Kingdom
FemboyTrap
Seen from Spain
cantho
Seen from Vietnam
BharatChorro
Seen from United States
transblowjob
Seen from United States
bbw
Seen from United Kingdom
ayodhyamarathon
Seen from United States
ชักว่าวโชว์สาว
Seen from Thailand
scat dildo
Seen from Turkey
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.7M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.3M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
83.9M followers

Lady Gaga
@ladygaga
75.4M followers

Virat Kohli
@imvkohli
73.3M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.3M followers

Bill Gates
@billgates
65.1M followers

Selena Gomez
@selenagomez
63M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers