

Top Tweets for #crypto24

No se necesitan 15 años de secreto para ejercer nuestros derechos, la evidencia forense conoce la verdad. #BHU #URUGUAY #CRYPTO24
👉https://t.co/eAJSG8nP91
Podcast episode:
https://t.co/aKTM5ef4o6
https://t.co/o841SZuoHY
https://t.co/ZHrZEKUJfY
https://t.co/YNkA3mX3li
From being wrongfully jailed in 2017 to reaching global headlines on @DarknetDiaries and Digital Forensics Magazine, the truth cannot be censored.
Now escalating internationally: as an Italian citizen, I have formally filed an Art. 144 action before the @GPDP_IT in Rome.
By documenting state mail server rejections (SMTP 111 & 550) following massive government data breaches, Uruguay's EU GDPR Adequacy Status is now under direct European scrutiny. Institutional silence fails when verifiable evidence goes global 🌍
⚖️CC: @Corriere @repubblica @SkyTG24 @EDPB_EU @EFF @privacyint #GDPR #Privacy #DataProtection #Cybersecurity #HumanRights #AlbertoHill #Italy #Uruguay
https://t.co/Xyu8azFXPC
#BHU #AGESIC #URCDP #CERTUY #URUGAY


Actor : crypto24
Victim : Estudio O'Farrell
Date : 2026-03-24 08:48:37 UTC +3
According to #DarkWeb #Ransomware activity detected by the ThreatMon Threat Intelligence Team. The “#crypto24” Ransomware group has added Estudio O'Farrell to its victims.
Analisis completo crisis BHU Banco Hipotecario del Uruguay
@HackersOIHEC #BHUCrisis #Crypto24 #DobleExtorsión #700GBDataLeak #ProtocoloDelSilencio #SecuestroDigital #VulnerabilidadSistémica #DeudaCibernéticaNacional @88choppertime @YourAnonSurge_ @SPYDIRBYTE @xVENDETTAMAFIAx @jasonsnitker @unixdoss
El Secuestro Digital del Banco Hipotecario: Crónica de un Ciberataque Anunciado - Actualización final octubre 2025.
https://t.co/oR9i34bBdn via @adanielhill @ONVentura @grazianopascale
The Digital Dissident: Alberto Daniel Hill and the Battle for Transparency in Uruguayan Cybersecurity
#BHUCyberattack #Crypto24 #NationalCyberDebt #AlbertoDanielHill #SecuestroDigital #ProtocoloDelSilencio #Uruguay #Cybersecurity #DigitalKidnapping #PII
https://t.co/tM1cIlmjIh
700 Gigabytes and a Guy Fawkes Mask: How Uruguay's Cyber Silence Led to the BHU Catastrophe
#BHUCyberattack #Crypto24 #NationalCyberDebt #AlbertoDanielHill #SecuestroDigital #ProtocoloDelSilencio #Uruguay #Cybersecurity #DigitalKidnapping #PII
https://t.co/fMSUfypHM1

🇺🇾 El grupo #Crypto24 #ransomware ha publicado parte de la información del #ciberataque perpetuado a Banco Hipetecario del #Uruguay 🇺🇾 (https://t.co/kpg7Lvtxmp)
@mef_Uruguay
Monitorea este incidente en #VenariX ➡️ https://t.co/OW9Te2XdwS #Ciberseguridad #BancoHipotecario #Montevideo #infosec #CyberAttack #CyberSec #banco #finanzas #ransomwareattack #BHU


El grupo #Crypto24 #ransomware se adjudica el #ciberataque perpetuado a Banco Hopetecario de #Uruguay 🇺🇾 (https://t.co/kpg7Lvtxmp), un banco estatal dependiente del Ministerio de Economía y Finanzas (@mef_Uruguay)...
Monitorea este incidente en #VenariX ➡️ https://t.co/OW9Te2XdwS
#ciberataque #ciberseguridad #BancoHipotecario #Montevideo #infosec #CyberAttack #CyberSec #banco #finanzas #ransomwareattack #BHU

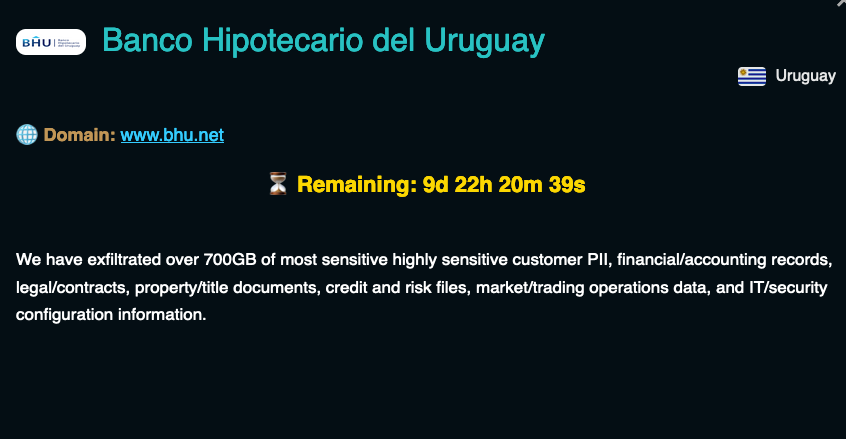
Informe para la Nación: La Filtración Consumada del BHU y la Quiebra de la Confianza Pública.
Toda la información esta disponible, #crypto24 cumplió la amenaza.
@GTLiber
@sagilet
@grazianopascale
@HackersOIHEC
@marcospresa609
@certuy
@three_cube
@DerechaLegal
@PhDenLogica
@takethismessage
@Sonia19011953
@alcidesmlo
@iben
@liontarakos
#BHUCrisis #Crypto24 #DoubleExtortion #700GBDataLeak #PIIDataBreach #SecuestroDigital #BHU #UruguayCyberCrisis #InstitutionalOpacity #ProtocoloDelSilencio #NationalCyberDebt #SystemicFailure #CriticalNationalInfrastructure #AlbertoDanielHill #CybermidnightClub #HackerActivist #WrongfulImprisonment #CounterNarrative #ProphecyValidated #PKICrisis #DigitalMasterKey #Arugu1337 #PlataformaGURI #ANEP #RelationalBetrayal #WeaponizingTrust
Informe para la Nación: La Filtración Consumada del BHU y la Quiebra de la Confianza Pública https://t.co/8Z1cgb0AFg via @adanielhill
Gracias por amplificar Informacion que la gente, en particular los clientes del BANCO HIPOTECARIO DEL URUGUAY tienen el derecho de conocer y al menos éticamente el BANCO debe informarle a, como mínimo a aquellos cuya Informacion ya fue publicada por #crypto24
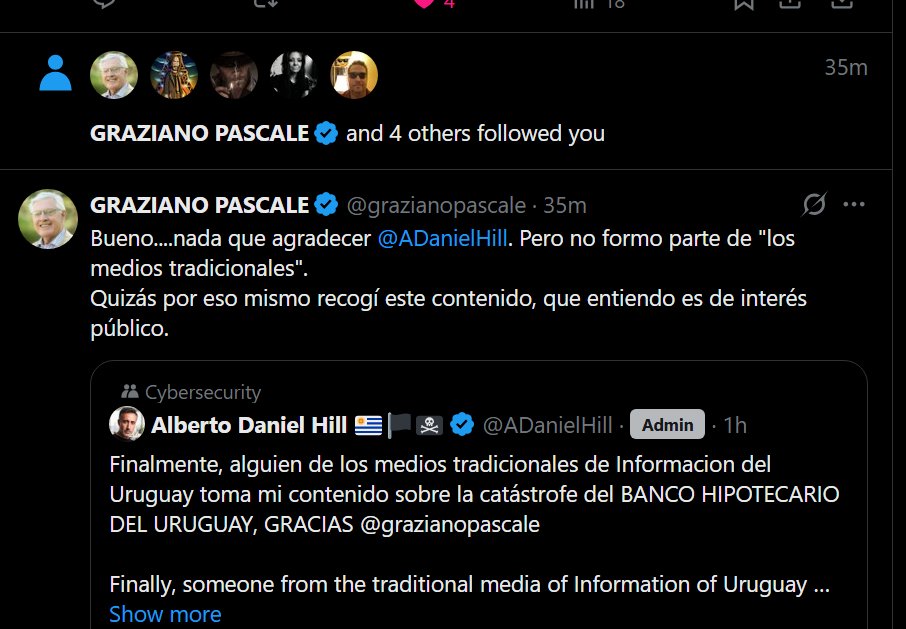

Bueno....nada que agradecer @ADanielHill. Pero no formo parte de "los medios tradicionales".
Quizás por eso mismo recogí este contenido, que entiendo es de interés público.
Expert Review and Strategic Analysis of the ANEP Cybersecurity Incident Affecting Plataforma GURI (October 2025)
https://t.co/pb3LpHo1Bh
@marcospresa609
Conoces a alguien a quien le inte rese esta Informacion?
@GonzaloRonchi
@puestaapunto12
#crypto24
@Iben
@jasonsnitker
@urbanosoax
@PequeSarpa
@mef_Uruguay
@agesic
@_venarixES_
@_venarix_
@HackersOIHEC
#BancoHipotecario #infosec #banco #finanzas #ransomwareattack #BHU
@mef_Uruguay
#ANEP #PlataformaGURI #GURIIncident #Uruguay #Cybersecurity #DataBreach #PII #DataExfiltration #Tacuara #PampaLeaks #BHU
@three_cube
@DerechaLegal
The GURI Platform Breach
The ANEP GURI incident involves a significant cybersecurity event that impacted the Plataforma GURI (Gestión Unificada de Registros e Información), the core educational management system used by the Administración Nacional de Educación Pública (ANEP) in Uruguay. The platform serves as a central nervous system for primary education, storing essential student and teacher data and facilitating administrative and pedagogical functions.
The incident and the official response began in October 2025.
Confirmed and Validated Events (Official ANEP Narrative)
The following details have been confirmed through official ANEP communications:
1. Incident Classification and Initial Response (October 3, 2025)
• Detection: ANEP officially detected a "cybersecurity incident" ("Incidente de ciberseguridad") affecting the GURI platform on October 3, 2025.
• System Disruption: As an immediate action, GURI was taken completely offline and remained "out of service". This action was described as a precautionary measure.
• Operational Workaround: ANEP issued an instruction mandating that staff revert to tracking daily attendance in a written, manual format until further notice. The suspension of electronic functions interrupted the real-time data flow GURI was designed to provide.
2. Restoration and Operational Impacts (Up to October 8, 2025)
• Partial Restoration: By October 8, 2025, ANEP confirmed a partial restoration of service. Specifically, the public-facing component, GURI Familia (available via app and web versions), was functioning again.
• Teacher Access Delays: Even after the partial restoration on October 8, official communications consistently noted that technical teams were "continuingly to work on access to GURI by teachers". This prolonged delay suggested the administrative and pedagogical backend, which involved high-privilege read/write functions for the estimated 24,000 affected educators, was either the primary point of compromise or the most difficult section to re-secure.
3. Critical Information Gap (The Official Silence)
• The primary failure in governance confirmed by the sources is ANEP's official refusal to confirm or deny the alleged massive data exfiltration.
• Official ANEP updates focused entirely on the successful restoration of services and did not address media reports or claims of compromised data.
• ANEP's initial use of vague terminology like "cybersecurity incident" avoided specifying whether data theft or a breach had occurred, minimizing public panic and deferring mandatory disclosure requirements concerning PII compromise.
@marcospresa609 Conoces a alguien a quien le inte rese esta Informacion?
@GonzaloRonchi @puestaapunto12 #crypto24 @Iben @jasonsnitker @urbanosoax @PequeSarpa @mef_Uruguay @agesic @_venarixES_ @_venarix_
@HackersOIHEC #BancoHipotecario #infosec #banco #finanzas #ransomwareattack #BHU @mef_Uruguay
#ANEP #PlataformaGURI #GURIIncident #Uruguay #Cybersecurity #DataBreach #PII #DataExfiltration #Tacuara #PampaLeaks #BHU @three_cube @DerechaLegal
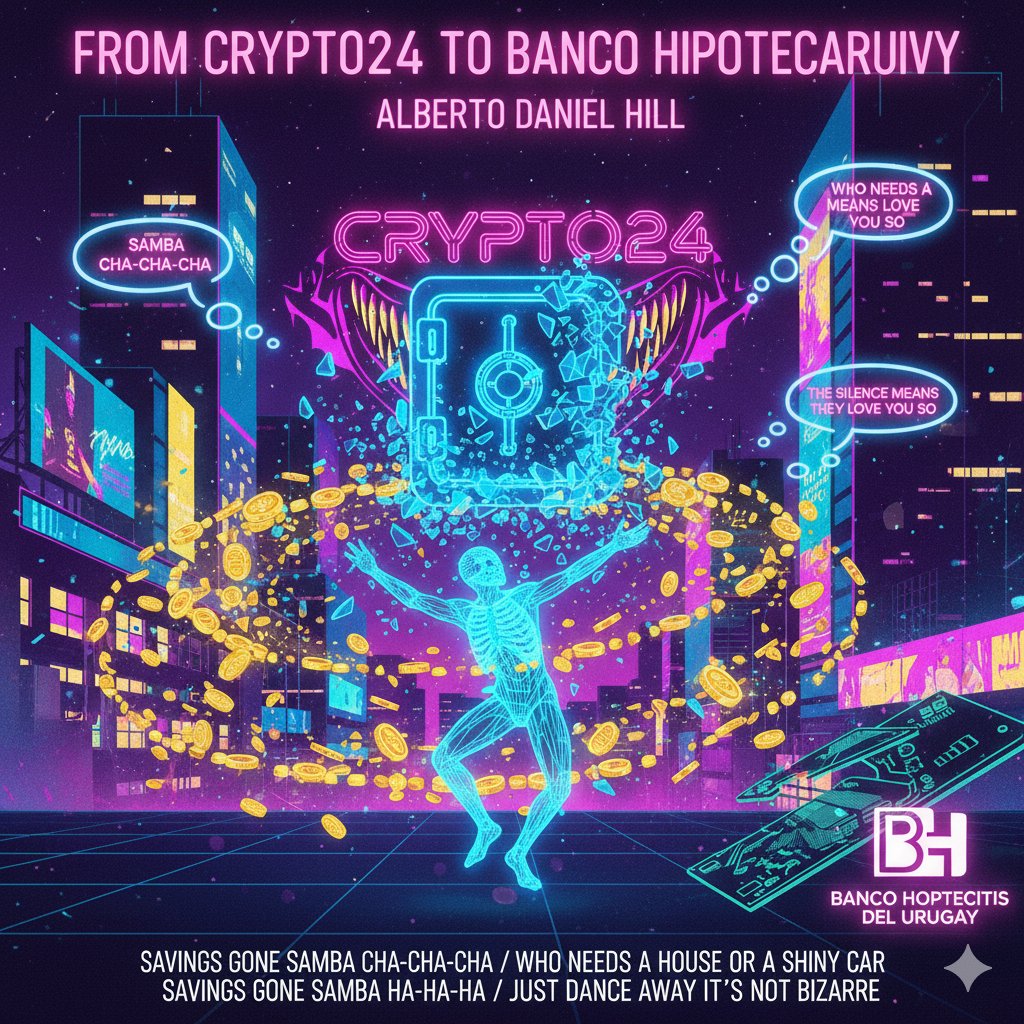
I told the truth, others hide it. Thanks TO @_venarixES_AND @HackersOIHEC --- Tonight new podcast episode of @TodayDarkweb covering everything about the official narrative vs facts.
El grupo #Crypto24 #ransomware se adjudica el #ciberataque perpetuado a Banco Hopetecario de #Uruguay 🇺🇾 (https://t.co/RyMGw4ZIRf), un banco estatal dependiente del Ministerio de Economía y Finanzas (
@mef_Uruguay)... Monitorea este incidente en #VenariX 📷 https://t.co/FP1DePcp3t #ciberataque #ciberseguridad #BancoHipotecario #Montevideo #infosec #CyberAttack #CyberSec #banco #finanzas #ransomwareattack #BHU
El grupo #Crypto24 #ransomware se adjudica el #ciberataque perpetuado a Banco Hopetecario de #Uruguay 🇺🇾 (https://t.co/kpg7Lvtxmp), un banco estatal dependiente del Ministerio de Economía y Finanzas (@mef_Uruguay)...
Monitorea este incidente en #VenariX ➡️ https://t.co/OW9Te2XdwS
#ciberataque #ciberseguridad #BancoHipotecario #Montevideo #infosec #CyberAttack #CyberSec #banco #finanzas #ransomwareattack #BHU
El grupo #Crypto24 #ransomware afirma haber #hackeado a Assicurazioni Generali S.p.A. 🇮🇹(@GENERALI), es una de las compañías de seguros y gestión de activos más grandes del mundo.
#OTCMKTS $ARZGY
#BIT $G
Más ℹ️ en #VenariX ➡️ https://t.co/OW9Te2XdwS
#CyberAttack #insurance #Italia #Generali #seguros #AttaccoInformatico #infosec #CyberSec #ciberataque


🚨 nuova rivendicazione #ransomware Italia 🚨
🏴☠️ gruppo #Crypto24
🧬 Generali Assicurazioni Group | Mogliano Veneto (TV)
🎯 settore: assicurazioni
🔗 https://t.co/UBnSycTulB
🗓️ 18 settembre 2025
📄 sample: -
▪️ dati esfiltrati dichiarati: -
▪️ dati esfiltrati pubblicati: -
⏲️ scadenza: 27 settembre 2025
#ransomNews #security #infosec


Crypto24 ransomware uses custom “EDR-blinding” tool to hit high-value targets https://t.co/8bhz4fxqSE #Crypto24 #EDR #GoogleDrive

#ThreatProtection Deployment of the #RealBlindingEDR tool among the recent activities of the #Crypto24 threat group , read more about Symantec's protection: https://t.co/qoRK4MmbZo #malware
Actor : crypto24
Victim : Palmgold Management Sdn Bhd
Date : 2025-08-18 15:47:10 UTC +3
According to #DarkWeb #Ransomware activity detected by the ThreatMon Threat Intelligence Team. The “#crypto24” Ransomware group has added Palmgold Management Sdn Bhd to its victims.
Last Seen Hashtags on Sotwe
aifurryart
Seen from Malaysia
minichat #snapchat
Seen from Turkey
kobukaishow10
Seen from United States
jakipz
Seen from Vietnam
SuperCodingGoûter
Seen from United States
Maharashtra Bandh
Seen from Singapore
anxiouspanda
Seen from United States
yerli
Seen from Turkey
homoflex
Seen from Spain
amalapaulhot
Seen from India
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.7M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.4M followers

Virat Kohli
@imvkohli
73.4M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.4M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers