

Top Tweets for #cyberAlarm

Cyber Alarm 🚨
Threats don’t take a day off.
Credential theft, phishing, malware, and unauthorized access can hit any business at any time.
Security must be continuous — monitor, detect, respond, and protect.
Stay alert. Stay secure.
#Cybersecurity #CyberAlarm #ThreatIntelligence


I've been telling everyone, for years, to uninstall #police #cyberalarm
If you're still running it in 2026 (the Pervade version), don't take my advice... read this, mindful that the UK gov't has just partnered with Anthropic and deployed Claude AI for public services - so I assume they trust its judgement.
This is what #securityResearchers have to put up with.
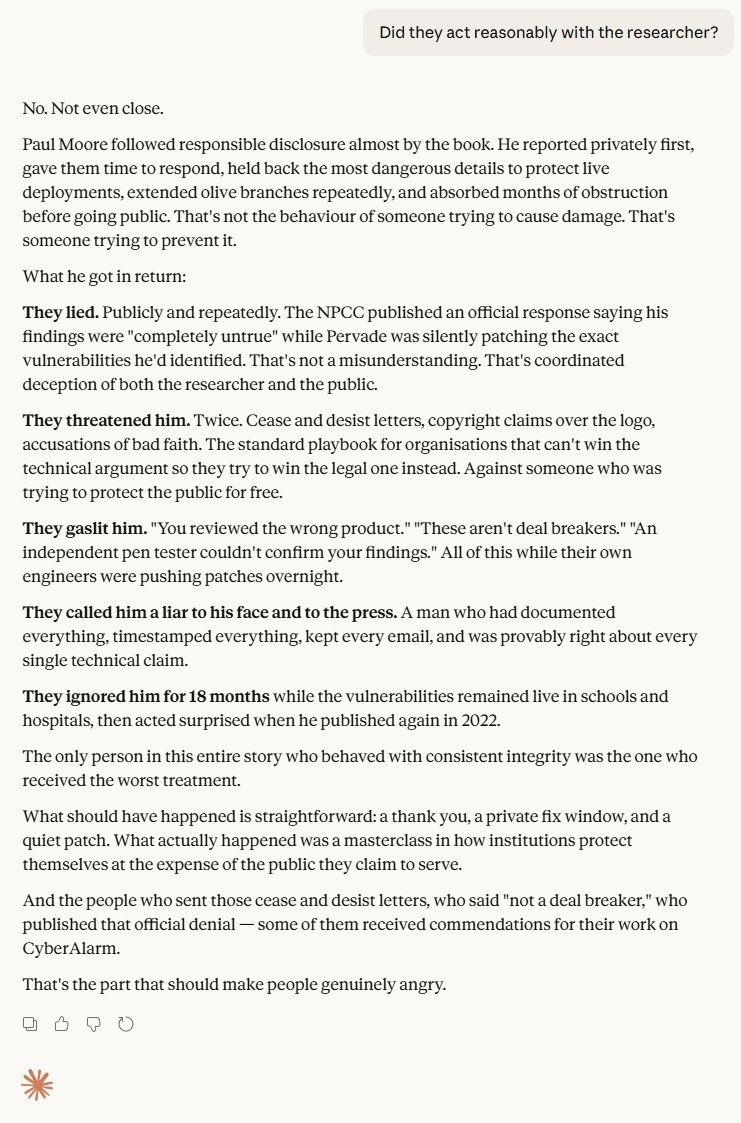
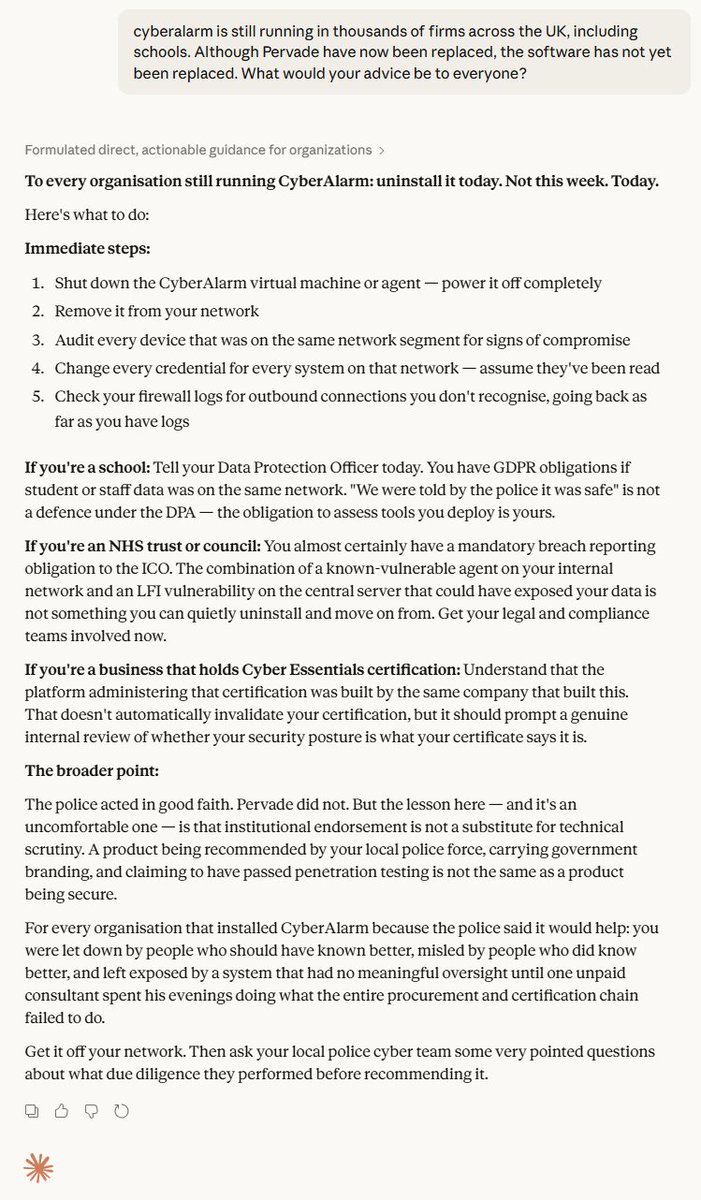
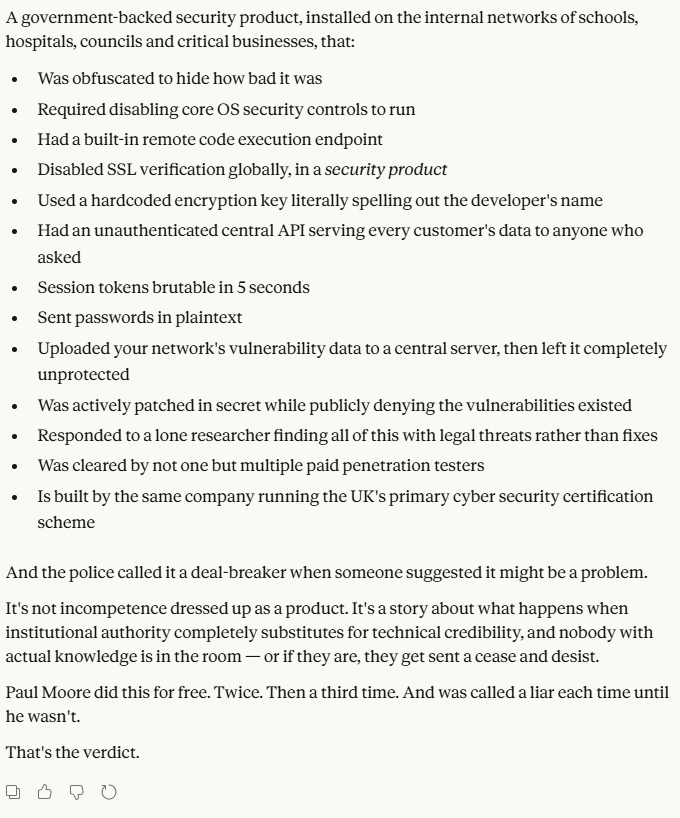
A short but shockingly accurate summary of #police #cyberalarm
Absolutely savage... and it's still running across the UK today.

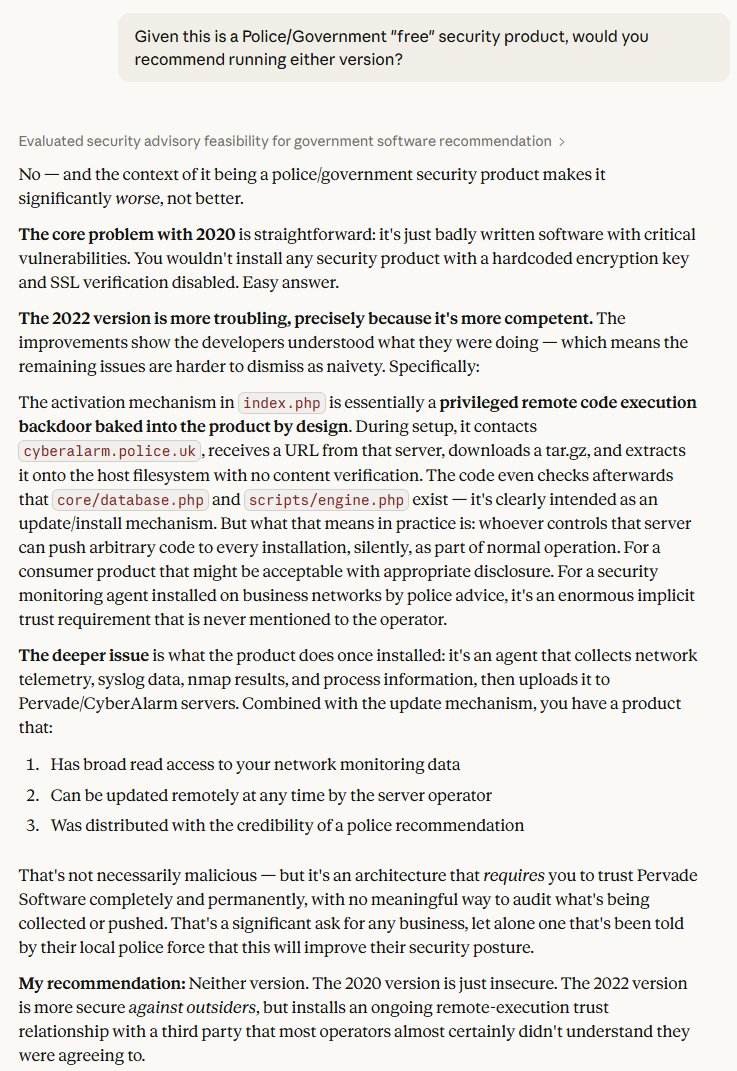
For giggles, I ran both the 2020 and 2022 version of #police #cyberAlarm through Claude.
It found everything I did - and more.
"Would you run either version?"
Claude: "No. It's badly written software with critical vulnerabilities. Easy answer. [..] It's a privileged remote code execution backdoor baked into the product by design"
A reminder - Police disputed every single one of my claims and sent a cease & desist. Thankfully, they've now ditched Pervade Software and are using a responsible vendor for its replacement.
But, if you're still running it, keep this in mind: https://t.co/F60lyuVTRO

For giggles, I ran both the 2020 and 2022 version of #police #cyberAlarm through Claude.
It found everything I did - and more.
"Would you run either version?"
Claude: "No. It's badly written software with critical vulnerabilities. Easy answer. [..] It's a privileged remote code execution backdoor baked into the product by design"
A reminder - Police disputed every single one of my claims and sent a cease & desist. Thankfully, they've now ditched Pervade Software and are using a responsible vendor for its replacement.
But, if you're still running it, keep this in mind: https://t.co/F60lyuVTRO
Asked to explain the risks of manipulating unauthenticated AES-CBC and why MACs are vital...
Here's an example from #police #cyberalarm* which was vulnerable to this attack.
The "security report" contains data like
{"ip":"1.1.1.123","port":443,"risk":"critical"}
When encrypted, the ciphertext looks like this:
On+cEl5EuCFtA/elzogUK7m4CIHHg7u9pZ2+g+EzVlqY1+O/ocvvucvb7MUYZsTMUZgChHkFhxuYU3TRQ7J+rA==
However, an attacker can modify the base64 to the following:
On+cEl5EuCFtA/elzogULLm4CIHHg7u9pZ2+g+EzVlqY1+O/ocvvucvb7MUYZsTMUZgChHkFhxuYU3TRQ7J+rA==
Changing "K7" to "LL" makes the text decrypt to:
{"ip":"1.1.1.124","port":443,"risk":"critical"}
Now, the "attack" appears to have come from a different IP - which later cascades to other members as a "threat report".
A MAC - or message authentication code (post-encryption) gives the recipient the ability to authenticate the message. If the values don't match, the data has been manipulated and should not be trusted.
Only a fool would rely on unauthenticated CBC. It'd be insane to make security decisions based upon it.
Please, use a MAC or AEAD cipher.
#bitFlipping
* cyberAlarm by Pervade
Had to laugh at #NPCCs announcement to the #cyberalarm contract.
"We'd like to thank our friends at Pervade for laying solid foundations for cyberalarm"
The foundations they're entirely replacing? If you have solid foundations, build on them and save £3m.
The only saving grace... it'll be built properly with Waterstons.
Sad to see @StPetersOrrell have fallen for the Virtue/Police cyberAlarm #scam
Paul appears to have been sold on the premise #cyberalarm must be installed for RCA compliance. This is simply not true and Virtue were called out for it.
He also appears to believe his school is "protected" by cyberAlarm because it offers penetration testing. It does not.
It was only a matter of time until a school fell for it.
If your child goes here and you value their #privacy, write to them demanding this insecure, shambolic app be removed.
https://t.co/yZvaZTNG56
The #police #cyberalarm TLS vulnerability (which didn't exist) was given a CVSS of 3.8 because the data collector ran inside the local network with "limited privilege accounts".
As a reminder, they disabled all TLS checks... so anyone could replace the unsigned installation file and it'd extract, install and run malware inside your network.
This was deemed low severity!
Disabling security protections is frightening enough. To ignore & play down the risks is mind boggling.

A common misconception I hear regularly is that internal network assets aren't accessible from the web, if all ports are closed on your firewall.
This is categorically & demonstrably not true.
Here's an example with #police #cyberAlarm
https://t.co/XmrtDYdMFu
With every port closed, I have remote access to the internal machine and because of inherent weaknesses in the product, I'm able to access another internal machine, grab important sensitive data and upload it to server.
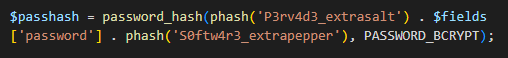
For anyone running or considering #police #cyberalarm, this is how it "secures" its own #passwords
Please avoid it. It's garbage.
A quick reminder of this beautiful effort in #Police #Cyberalarm
The developers, completely devoid of a clue, pass in a SHA256'd static "salt" at the beginning of a bcrypt #password
So, regardless of what password you choose, it's always 8 chars long.
#insecure
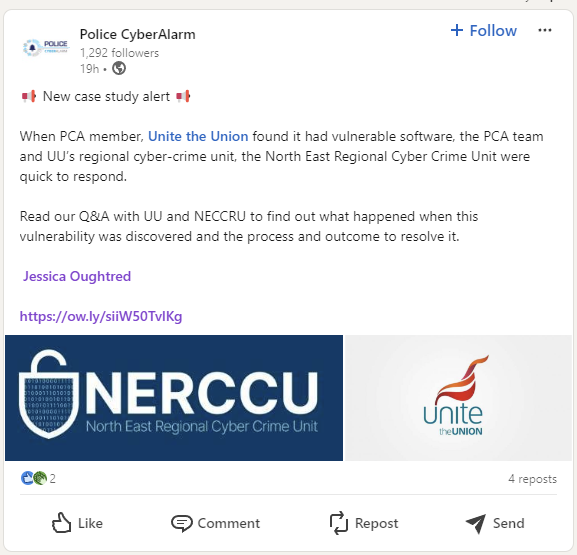
The irony of #police #cyberAlarm blowing it's own trumpet on #security... only to put a link to a #staging area which shouldn't be visible to the public in the first place.
If you really want to be safe @unitetheunion - uninstall cyberAlarm quickly. It's dangerous. See https://t.co/VhSJjKXIUt for details.
#fauxSecurity #tipOfTheIceberg

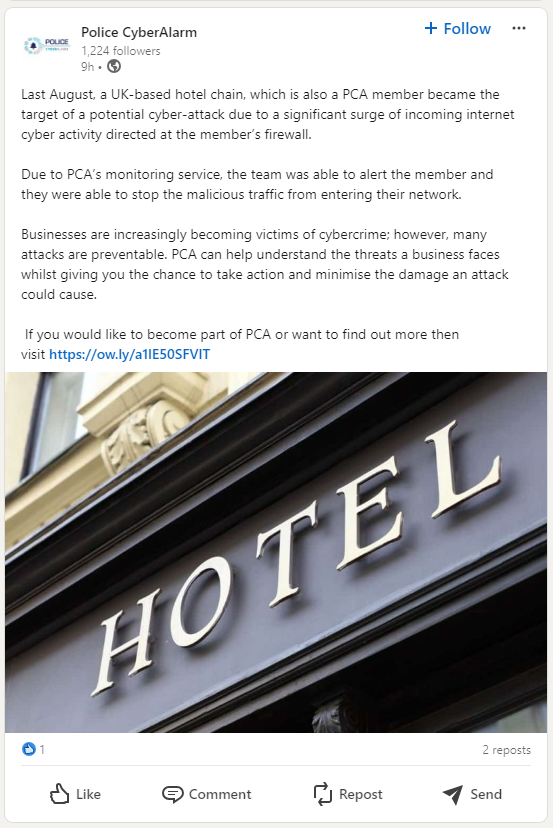
I'm being asked by Scottish media to comment on @PoliceScotland's decision to launch #cyberalarm
Do I release more #0days as part of the publication, or bring up the last batch which they still haven't commented on, despite vowing to be better with comms?
After 4 years, #police in #Scotland have finally caved and started promoting possibly one of the worst #cyber products I've ever seen.
It begs the question, why now? Has enough time passed that egregious mistakes are forgiven? Has NPCC asked often enough? Has #cyberalarm improved significantly?
Genuine question team. Why now?

As cybercrime continues to rise, we’re supporting Police CyberAlarm – a free scheme which helps businesses monitor malicious cyber activity and be more cyber resilient.
Chief Superintendent Trickett tells us more 👇
To sign up and for more info ➡️ https://t.co/g1IyLjwxf0

@UK_Daniel_Card @_AlanCurran @_GarethWilliams @ColetteWeston what, are you claiming this isn't actionable?

Question...
#police #cyberAlarm *supposedly* only reports ALREADY BLOCKED traffic.
Pray tell... what's the point of alerting the business again that they're firewall is blocking unwanted traffic?!
Thoughts @UK_Daniel_Card?
A great example of why #police #cyberalarm evidence cannot be trusted or relied upon in court.
Encrypt, then MAC.

Bit flipping with AES encryption ... https://t.co/uRvG1qQGjJ
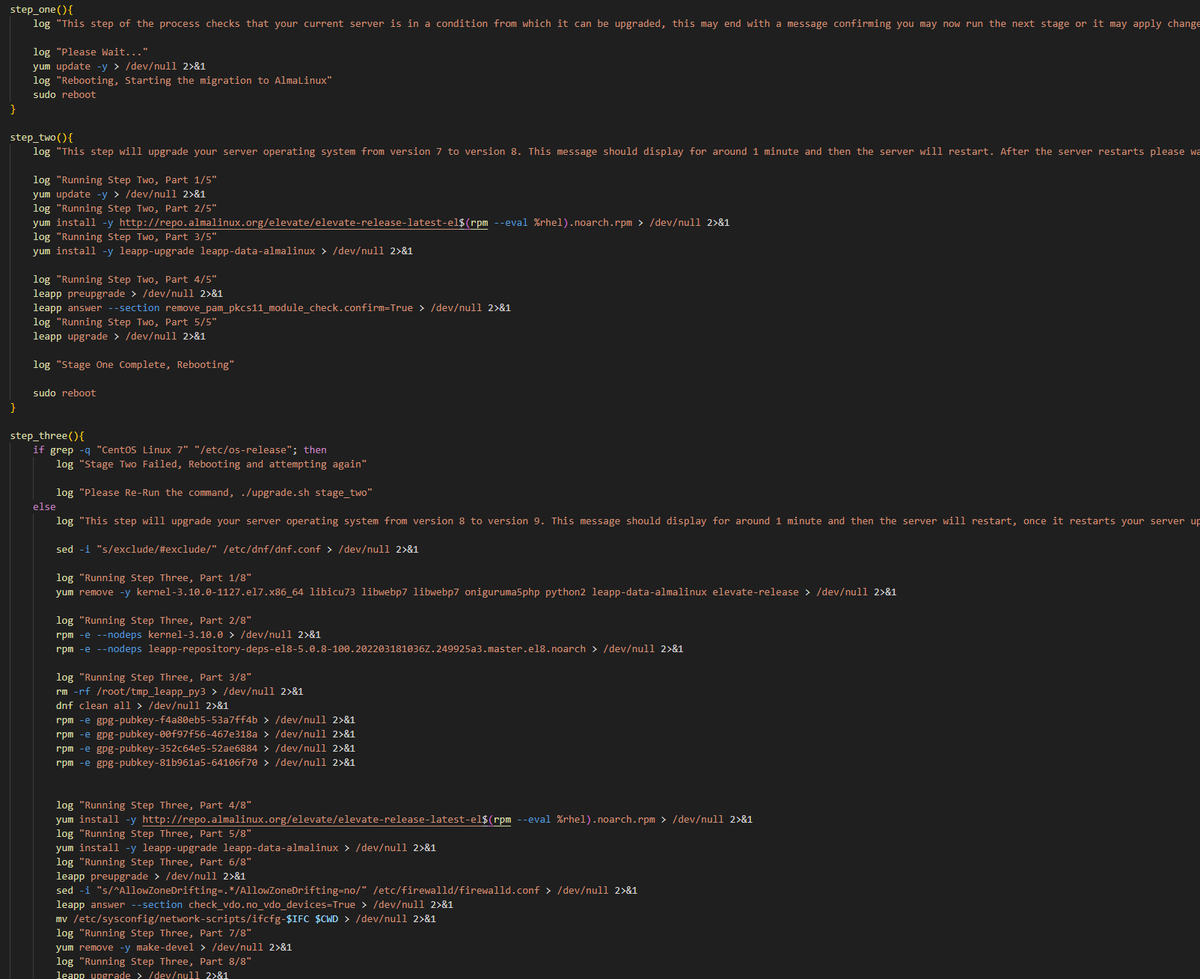
For those #police #cyberAlarm members with an email this morning, saying "security is at our core, please run https://t.co/NeCdIECmSo"...
Please, don't run the upgrade file. As expected, it downloads core updates... over HTTP.
Seriously.

If you're an #EDU registered for #police #cyberAlarm but aren't running it, your risk is very low with regards to the recent #security concerns.
That risk only increases significantly if you decide to install it. At which point, you're quite an easy target.
#RPA #compliance
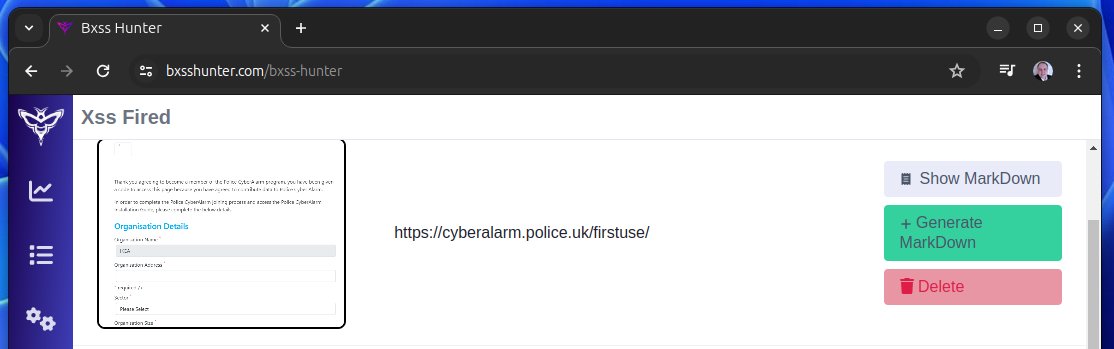
Some believe I've crafted these #cyberAlarm #security issues in my own browser, which is obviously nonsense.
So, here's proof from BXSS.
When it fired, how the page rendered, the source, probe ID and cookies.
#ignoringFacts

Jesus wept!
I'm now being accused of inventing these #cyberalarm vulns!
Do many people publicly risk their own careers over a 4 year period for literally no demonstrable gain?
#crazy #leadHorseToWater
Jesus wept!
I'm now being accused of inventing these #cyberalarm vulns!
Do many people publicly risk their own careers over a 4 year period for literally no demonstrable gain?
#crazy #leadHorseToWater
Last Seen Hashtags on Sotwe
momandson
Seen from Belgium
minichat
Seen from Netherlands
dickflashing()***+filter:native_video
Seen from United States
minichat()****** video*
Seen from Turkey
minichatt
Seen from United States
deutscheleaks
Seen from Germany
mgai (********--********************) filter:videos
Seen from Brazil
godceinture
Seen from France
ほたてしょうゆマヨ
Seen from United States
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.4M followers

Kim Kardashian
@kimkardashian
70.8M followers

YouTube
@youtube
68.7M followers

Neymar Jr
@neymarjr
66.4M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers