

Top Tweets for #phaas

BigBear 2.0 phishing bypasses Microsoft 365 MFA via Evilginx2, stealing 474 sessions across 461 orgs in 40+ countries as a PhaaS service.
#BigBear20 #Evilginx2 #Phishing #MFABypass #Microsoft365 #AiTM #PhaaS
https://t.co/JDM4ReSE3u

BigBear 2.0: la piattaforma di phishing-as-a-service che aggira anche l’MFA di Microsoft 365
il blog: https://t.co/rpIVHZ9NRW
#cybersecurity #aitm #cybercrime #evilginx2 #infosec #mfabypass #microsoft365 #phaas #phishing #spearphishing

The Outsider Phishing Kit persists despite the Operation Ghost Hook takedown. Discover how the ChenLun Outsider PhaaS kit bypasses MFA via AiTM attacks.
#OutsiderPhishingKit #OperationGhostHook #PhaaS #ChenLun #Cybercrime #Smishing
https://t.co/ul2YKIzIqF

From its Telegram-based affiliate ecosystem to its centralized phishing panel and #AiTM capabilities, Outsider demonstrates how #PhaaS is turning sophisticated phishing operations into a scalable service. Discover the technical analysis of ChenLun, the kit's infrastructure, attack flow, fingerprints and defensive measures: https://t.co/YhdfzLayeg


We analyzed #AnonyMousKIT, an AI-powered #PhaaS ecosystem designed to help criminals bypass Apple’s Activation Lock by targeting owners of stolen devices with sophisticated #phishing campaigns.
- 506 kit-family domains & 168 storefront brands
- Email, SMS, WhatsApp, Recorded voice & AI-powered vishing
- Apple ID, passcode & 2FA harvesting
- Exposed backend logs, operators & infrastructure
Read the analysis: https://t.co/WaClFOUsHa


Cisco Talos discovered the JWR phishing framework, a new PhaaS variant. Read our JWR phishing framework analysis to learn about this real-time cyber threat.
#JWR #Phishing #CiscoTalos #PhaaS #CyberSecurity #InfoSec
https://t.co/FjwDBGJdA7
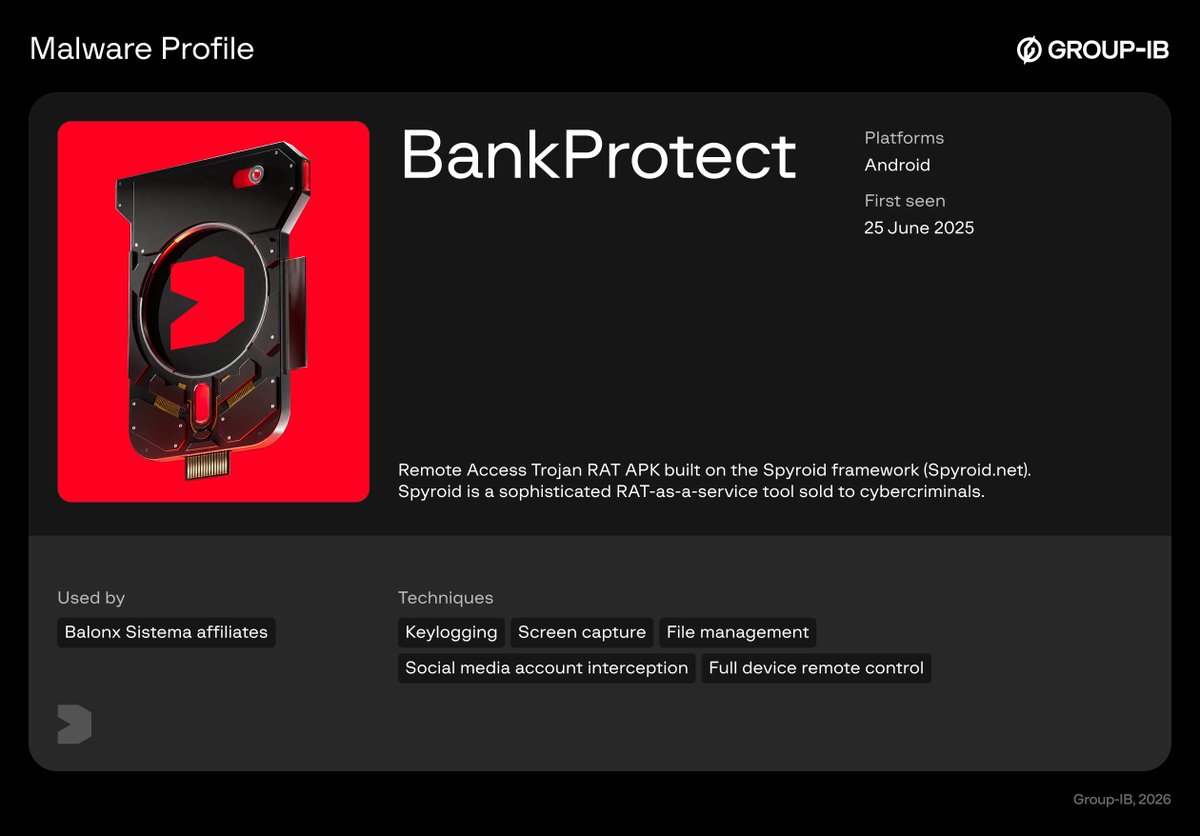
Balonx Sistema is a Mexican #PhaaS operation targeting 20+ banks with real-time WebSocket session control, Spyroid-based Android RAT (BankProtect), and AI-powered #vishing automation. Since October 2025, over 1,100 victims have had credentials and financial data harvested. This is criminal SaaS at industrial scale. #ThreatIntel




🌍 #WeeklyThreats: Le ultime dalla penisola, piattaforme #PhaaS, #malware e operazioni #APT in Asia, violazioni di dati e iniziative internazionali.
L'ultima settimana cyber nel nostro report #CyberThreatIntelligence
🔗 https://t.co/XRPH0gfwWV
#Cybersecurity
Researchers expose the Greatness PhaaS platform, an AiTM phishing kit sold on Telegram that steals Microsoft 365 tokens past MFA.
#Phishing #PhaaS #AiTM #Microsoft365 #CyberSecurity
https://t.co/uUNap5G5w1

Phishing kits used to point everyone to the same fake login page. Logokit now rebuilds each victim's real corporate login in real time. Learn more about the recent developments. https://t.co/QU69E62bD0
#BarracudaONEplatform #PhaaS #cybersecurity


🚨 New research: The IRONTOLL ("Iron Man") PhaaS campaign is leveraging advanced phishing techniques to target organizations and evade detection.
Read our full analysis:
https://t.co/YdV0tLi50Z
#CyberSecurity #ThreatIntel #Phishing #PhaaS #BlueTeam #PhishEye

🔥 ARToken PhaaS Infrastructure 🔥
A total of 8 ARToken Dashboard servers have been identified.🎯
#PhaaS #Eviltoken #ARToken


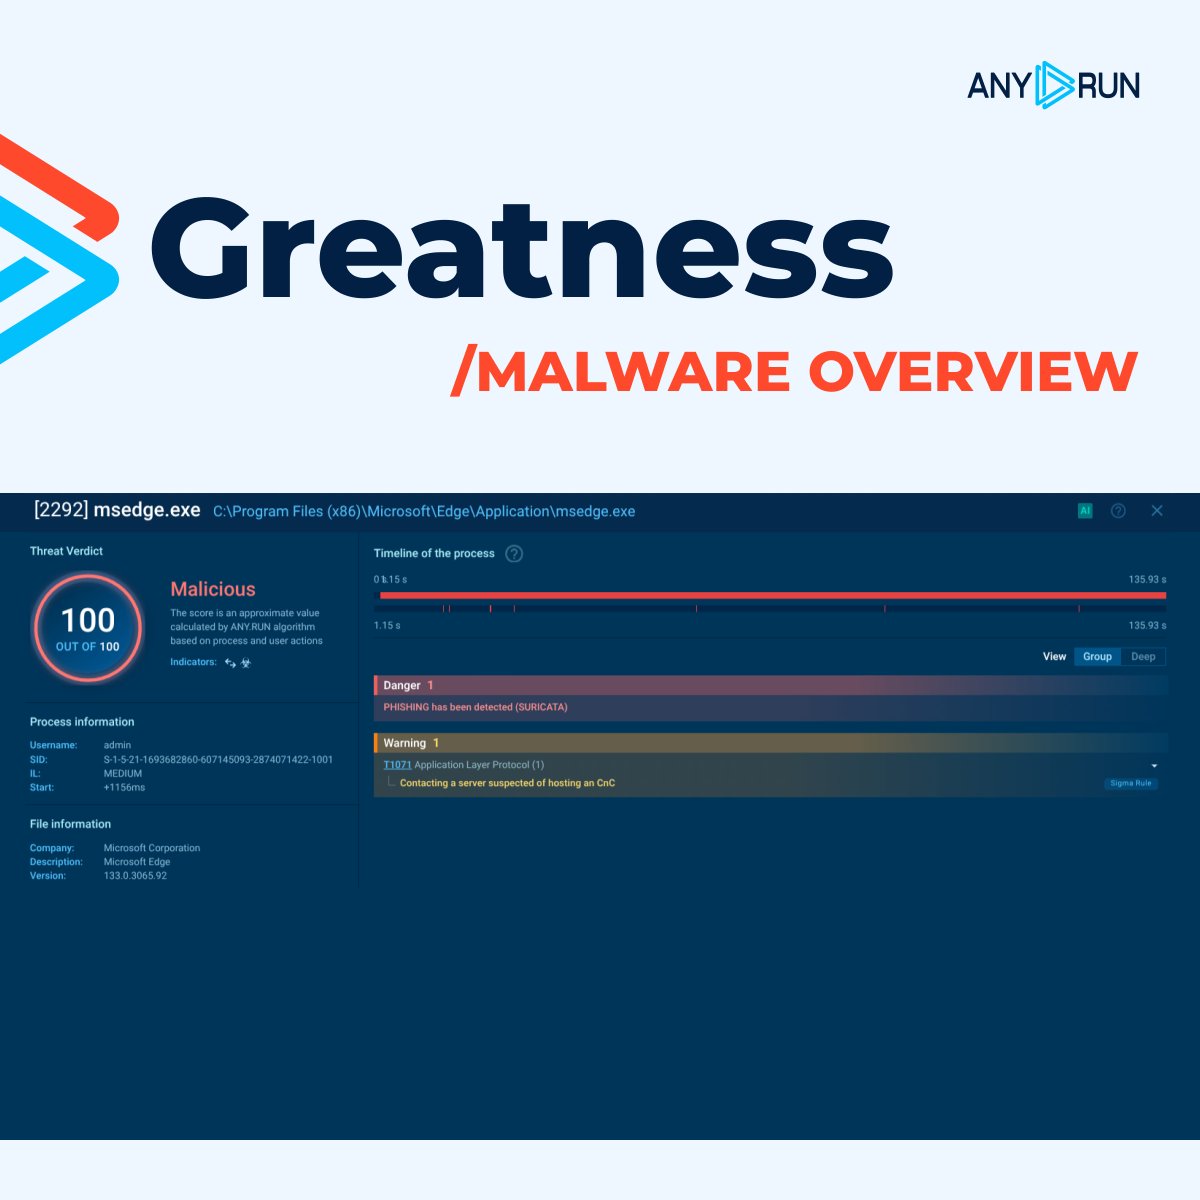
🚨 Greatness #PhaaS turns a fake Microsoft 365 login page into a potential BEC, data theft, and payment fraud incident.
👨💻 Learn how its branded lures, MFA bypass capabilities, and credential theft workflows put business identities at risk: https://t.co/r6venb6Drp

🚨 New Research - The Quarry ⛏️
Years of activity and hundreds of affiliates in one #MaaS/#PhaaS ecosystem, The #Threat Research Team traced all the way from campaigns and operators to Rockky, the developer behind it all.
#Phishing kits impersonating SSA/IRS and SaaS brands deploying RMM, RATs or custom #hacktools
👽 Blogpost: https://t.co/EeltGgSNCj
🔗 Report: https://t.co/gGpesGeZ1d
#ThreatHunting #Cybersecurity #Research #CTI #Malware #RE


📣🚨🪝Group-IB, INTERPOL and Algerian Police have dismantled a decade-old Phishing-as-a-Service (#PhaaS) Network called #SniperDZ - Its alleged developer has been arrested as well.
Read: https://t.co/X1LftPob1s
#CyberSecurity #CyberCrime #Phishing #Algeria #Interpol
🚨 𝗢𝗔𝘂𝘁𝗵 𝗧𝗼𝗸𝗲𝗻 𝗔𝗯𝘂𝘀𝗲 𝗜𝘀 𝗚𝗿𝗼𝘄𝗶𝗻𝗴: 𝗚𝗿𝗲𝗮𝘁𝗻𝗲𝘀𝘀 𝗥𝗲𝘁𝘂𝗿𝗻𝘀 𝘄𝗶𝘁𝗵 𝗗𝗲𝘃𝗶𝗰𝗲 𝗖𝗼𝗱𝗲 𝗣𝗵𝗶𝘀𝗵𝗶𝗻𝗴
We've identified renewed activity associated with the Greatness #PhaaS, which combines #AiTM and Device Code #Phishing to target Microsoft 365 Accounts.
⚠️ Device Code Phishing abuses Microsoft's legitimate device authorization flow to obtain access tokens without directly collecting passwords or MFA codes. This shifts risk from credential theft to token abuse, reducing traditional phishing indicators for SOC teams to detect and investigate.
❗️ Greatness promotes token- and cookie-based access to Microsoft 365 accounts through its Telegram channel, advertising passwordless and code-less account compromise scenarios.
Observed capabilities include:
🔹 Device Code Phishing for M365 token theft
🔹 Phishing templates impersonating DocuSign, OneDrive, Outlook, and Voicemail
🔹 Country-targeted login lures
🔹 Cloudflare-hosted phishing links
🔹 Keyword-based targeting engine
🔹 Centralized administration panel
👨💻 Review the analysis session, investigate the phishing flow, and validate detection coverage: https://t.co/PtQqvDlyRz
🔍 Track Device Code Phishing activity associated with Greatness and uncover related infrastructure in #ANYRUN TI Lookup: https://t.co/YDn4yRxQ6Q
🚀 Strengthen phishing detection and accelerate response across your SOC with #ANYRUN: https://t.co/LEPvxOXvaD
#ExploreWithANYRUN


Discover how the Chinese PhaaS ecosystem uses real-time interception and AI automation to bypass MFA and exploit digital wallets.
#Cybersecurity #PhaaS #ThreatIntel #Phishing #MFABypass #Infosec #CloudSecurity
https://t.co/sNQHhkYV3e

AI "vibe coding" and the EvilTokens PhaaS platform are supercharging device code phishing to bypass Microsoft 365 MFA. Secure your network today!
#DeviceCodePhishing #Microsoft365 #CyberSecurity #InfoSec #Phishing #MFA #EvilTokens #PhaaS #AI #VibeCoding
https://t.co/WsQD7RVjQv

Last Seen Hashtags on Sotwe
rabopeludo
Seen from United States
Hayalguienahi
Seen from United States
britisholivia
dufh
Seen from United States
NexusLeague
Seen from United States
pasif
Seen from Turkey
MythologicalNFT
Seen from United States
ModiGoBack
Seen from France
IndiaandTaiwanTrueFriends
Seen from United States
Hotwife
Seen from Thailand
Most Popular Users

Elon Musk 
@elonmusk
241.6M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.2M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
89.9M followers

Taylor Swift
@taylorswift13
83.8M followers

Lady Gaga
@ladygaga
75.3M followers

Virat Kohli
@imvkohli
73.2M followers

Kim Kardashian
@kimkardashian
70.8M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.2M followers

Bill Gates
@billgates
65.1M followers

Selena Gomez
@selenagomez
63M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers