@robinhanson Impressive but not surprising 👍
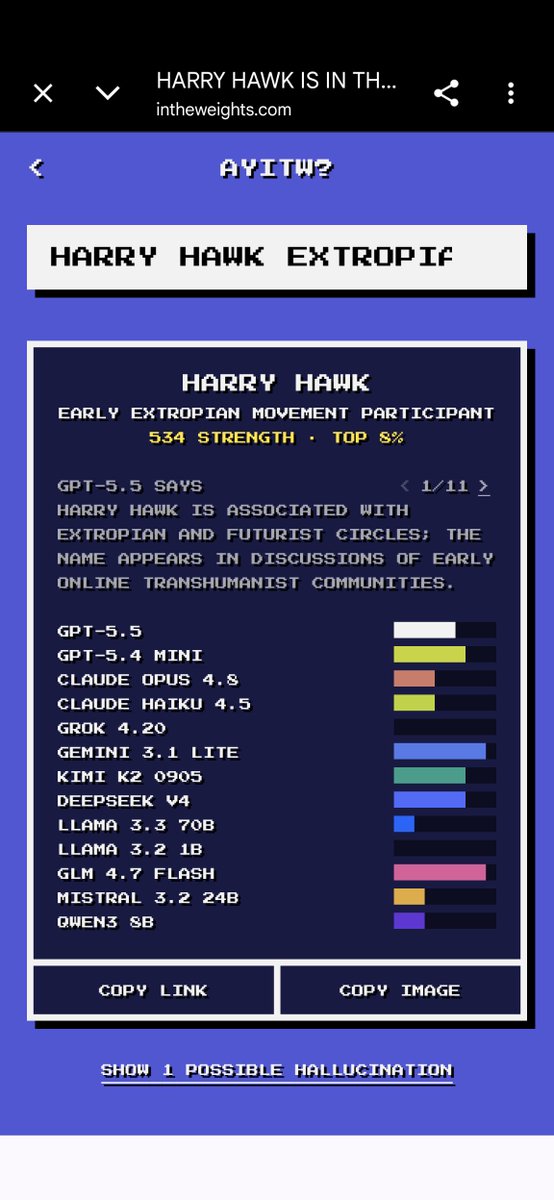
I didn't exist at all until I "showed my metal." A few models think I'm fictional. https://t.co/F167Zatjic
Crazy 72 hours in security. Three major incidents dropped back-to-back: eMudhra, PingCAP (TiDB Cloud), and PHP.
Here is the short version of what happened and who got hit.
1. eMudhra (Trusted CA compromise)
eMudhra generated 8 intermediate CA certificates in April 2025 (cross-signed by Sectigo). A bug in their HSM key-wrapping test script created a second set of P-384 keys where the private keys were single-byte numbers under 256. Operators picked the wrong key labels and signed them into real CA certs.
One of the intermediate CA private keys was literally the number 4.
The other seven: 56, 66, 115, 155, 156, 230, 237.
Three weeks later (May 2025), their CRL signatures started failing because the CRL signer was using the real keys instead of the weak ones. Instead of asking why the keys didn't match, someone switched the CRL signer to the weak keys and closed the ticket.
• Browsers are safe: Chrome, Firefox, Apple, and Microsoft already blocked them, and zero rogue certs hit CT logs.
• Servers are not: curl, Python (certifi), Go binaries, and Docker base images don't check CRLs. Update ca-certificates, certifi, and Go (1.27.3 / 1.26.10).
• 10-second check on any server:
curl https://t.co/vhiGLxNhIS
(TLS error = safe. 200 OK = still vulnerable.)
2. PingCAP / TiDB Cloud (10.6 TB breach)
Attackers found GCP and Azure credentials committed inside PingCAP's own repos. They set up a replication feed of TiDB Cloud's production control plane and exported the entire database every 6 hours for 22 straight days. 88 full exports, zero alerts. 200 GB is already out on torrents.
Beyond the 413 private repos and 20.6M customer SQL queries logged from their web SQL Editor, PingCAP engineers were pasting customer secrets into Jira tickets.
Who is affected in the leaked records:
• Live credentials exposed in support tickets:
- Pinterest: AWS keys for their pingcap-logs S3 bucket
- CardX / Silverlake (NPCI-linked env): AWS admin key in a backup log with full access to 258 external S3 buckets
- DeBank: 38 presigned S3 URLs
- An unnamed AI/dev platform: a 314 MB slow-query log attached to a ticket containing 8,027 live customer secrets (an AWS root key, a GitHub admin PAT over 1,701 repos, 7,485 AWS STS tokens, and 192 OpenAI/Anthropic/Gemini keys)
• Tenants with infra metadata, VPC CIDRs, app-server IPs, or contract pricing exposed:
- Tech: Atlassian, Databricks, Airbnb, Baidu, LINE, Nylas, Persona, PatSnap
- E-comm & Travel: https://t.co/C512KFOEq5, Shopee, Flipkart, Mercari, ZOZO, AEON, Delhivery, Klook
- Gaming: Capcom, Square Enix, Konami, Bandai Namco, Cygames, Colopl, DMM
- Finance: PayPay, SoftBank, SBI, SB Payment Service, Fujitsu, TOPPAN, Bank of China, China Life
- Crypto: Bitget (said only public trade logs were on it and they already left), Pionex, DigiPlus, NFTscan, Chainbase
• Developer profiles leaked (from a purchased https://t.co/28tjHqd5Wr table in PingCAP's BigQuery):
- 24,900 personal emails + GitHub/LinkedIn profiles of engineers at Tencent (3,327), Huawei (2,726), ByteDance (2,475), AIG (2,140), Mastercard, Flipkart, and bKash.
If you use TiDB Cloud: rotate your console API keys, DB passwords, and anything you ever pasted into a support ticket.
3. PHP "PHP2Shell" (CVE-2026-109618 & CVE-2026-109619)
Two CVSS 9.2 pre-auth RCEs leaked yesterday ahead of today's 14:00 UTC patch.
Public writeups trace it to a heap Use-After-Free in PHP's native C multipart/form-data session upload-progress handler (ext/session/session.c).
Because C-level multipart parsing runs before line 1 of index.php:
• App auth, Laravel/WordPress middleware, and file_uploads = Off do not stop it.
• Only PHP 8.2–8.5 get official patches today (59% of PHP servers on Shodan are on EOL <= 8.1).
• Until you patch php-fpm: lock php_admin_flag[session.upload_progress.enabled] = off and block unexpected multipart requests at Nginx/Apache/Cloudflare.
GOP sent fake pamphlets saying "groups like these are set up to become your found family"
people check the group, it's fake, and set up to be similar to the name of an existing group.
it's 14 days till midterm elections nov 3rd.
either they think people are too stupid to learn the truth, the media is too cowed on the issue, or they expect us to be too buried under this crap for 14 days for their subterfuge on this to get back to them!
i expect the latter
@McFaul I believe it sets up post-election conflict. Whether the Dems flip the Congress or not, regardless of the outcome, it increases the tension and polarization, which is generally Russia's game plan.
I'm testing the Hack your Android TV interface with Codex. I've always loved Android - I'm now much more appreciative.
This is a real average person AI use case. 95 million homes have TVs and many of them have Android (guess).
We spend hours a day in front of our TVs. This is a huge unlock
@awoooouwuooooo@grok@hhawk well you're the one not responding to what i said in the quote tweet. you're saying it's not because it's about trans kids only, and i'm saying it's not even, they use it as a wedge issue and it is prohibiting as written
@VsimPohuy It's to create post-election conflict. Whether the Republicans win or the Democrats win, either way it creates conflict. It's how Russia operates.