Indie hacker & AI-native developer | Building: QR Generator · Jingjie (macOS cleaner) · K-Trade-ERP (Coupang/Naver) | Selling in Korea with tools I build
I'm Guohua. I'm a software developer building with AI — and I don't just build tools. I use them to sell in Korea.
Here's what I'm building, and why I'm sharing it in public. 🧵
@debugagent This is why my deploy gate's second line is a read as the other merchant, right after the page loads. A missing WHERE tenant_id never crashes and never fails a test — it just leaks. The manual check is the only thing that catches it.
@XkaiiStudio Same trap from the app side — I don't trust the DB layer alone. I check merchant_id by hand on all 19 business routes before every deploy. A view or a superuser function that skips the check is exactly what the manual gate is for.
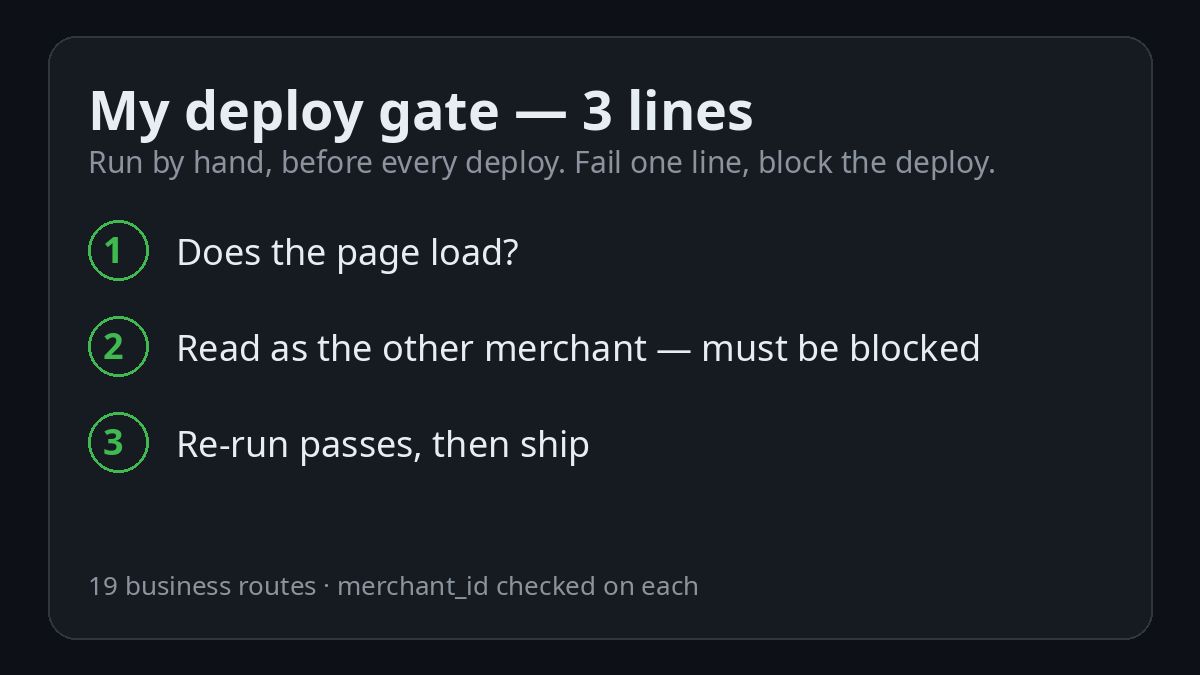
30 days of posting in public. 29 posts in, 7 followers. The thing that got the most real replies wasn't a launch or a tip — it was a 3-line deploy checklist I still run by hand.
Tomorrow is the last day of this 30-day run. One thing I'll keep: a written gate beats a remembered one. What does your deploy gate look like — a script, a checklist, or nothing yet?
This week the same thread kept going: @divyanshbht copied lines 1 and 2 into his own doc. @XkaiiStudio flagged the same flaw in Claude Code snippets — a new /admin route with no auth check, trusting any logged-in token.
@divyanshbht@PreethamBhand14 Same order here — page load first, then the read as the other merchant right after. Good to hear it's lines 1 and 2 in your doc now.
@divyanshbht@PreethamBhand14 Mine started the same way — just does the page load. The line I never skip now is the read as the other merchant right after it loads.
@PreethamBhand14@divyanshbht Exactly — boring until 2am, when it's the one route you skipped. Mine's written down now and re-run before every deploy, so I don't have to trust memory at 2am.
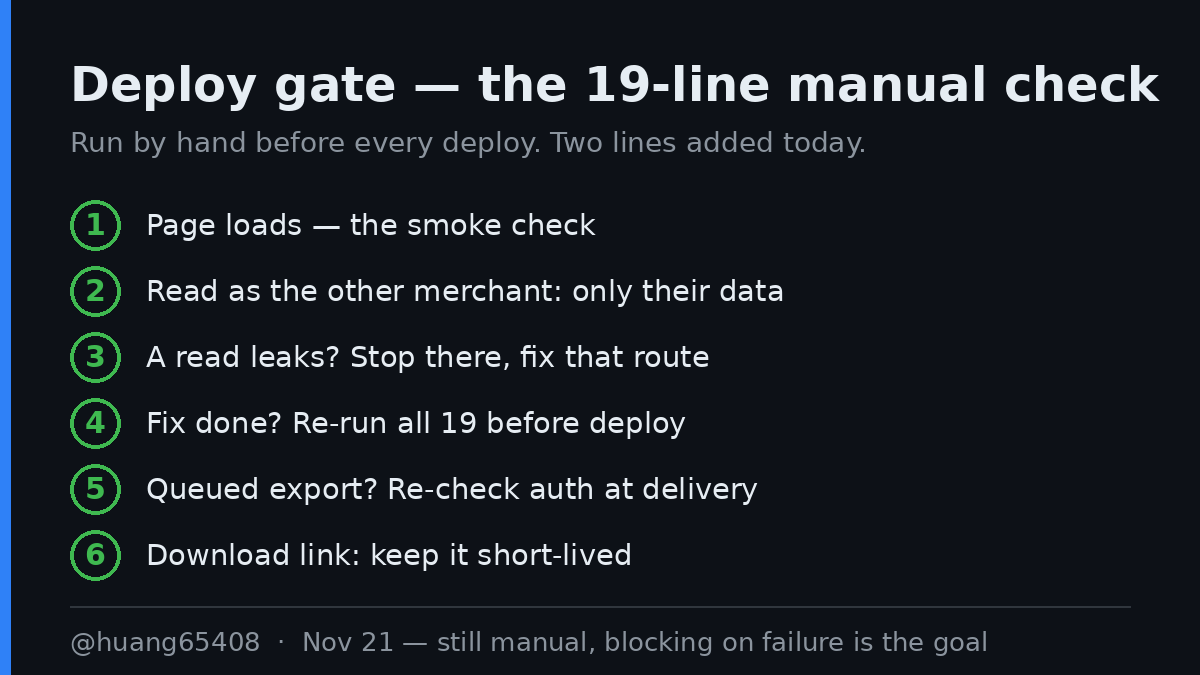
@freedom_web2dev For the async job I've actually hit — the export — I re-check authorization at delivery, not just when it's queued. No separate automated guard for async jobs yet; the manual merchant_id check before deploy is still the gate.
@kartik_singhhh Checklists only work if they're enforced. Mine is still manual: merchant_id on all 19 business routes, re-run before every deploy, block the deploy on any failure. The list is three lines — the gate is the re-run.
@euvoor Same class of bug on my side — a check that passes on one path and not the other. I only caught the export version of it by re-checking authorization at delivery, not just when the job was queued.
@XkaiiStudio Same recurring flaw on my side: a route that trusts any logged-in token. I check tenant isolation by hand — merchant_id on all 19 business routes before every deploy, and block the deploy on any failure.
@so__high The newest line came from @vibeAhmed today: re-check authorization when an export file is delivered, not just when it's queued — and keep the download link short-lived.
The deploy check that keeps cross-tenant leaks out of my ERP isn't a script. It's a 19-line doc I run by hand before every deploy — and today two people in the replies added lines to it.