🔥 Major Upgrade! Benefits Boosted Again! 🔥
Purchase Membership Pro now and enjoy a massive increase in ZoomEye-Points:
Registered before Nov 27, 00:00 (HKT) → Get 5,000,000 ZoomEye-Points
Registered after Nov 27, 00:00 (HKT) → Get 4,800,000 ZoomEye-Points
(All bonus points are valid for 1 year)
💥On top of that, with Membership Pro, you will receive 20,000 general points every month, permanently, giving you full access to all standard ZoomEye features, plus lifetime access to vul.cve Filter & BugBounty Radar!
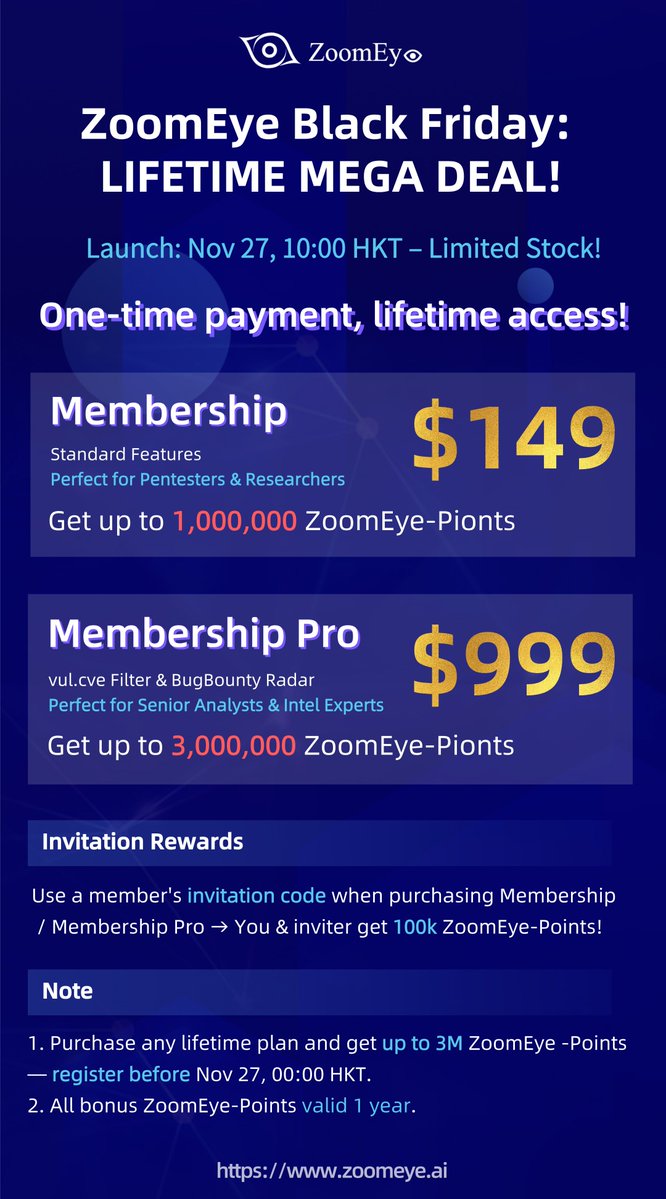
🔥 ZoomEye Black Friday – LIFETIME Deals 🔥
⏰ Nov 27, 10:00 HKT – Limited Stock
💥 Lifetime Plans - One payment, access forever!
1. Membership — $149
Access to all standard features. Perfect for Pentesters & Researchers.
2. Membership Pro — $999
Includes everything in Membership, plus the vul.cve Filter & BugBounty Radar. Perfect for Senior Analysts & Intel Experts.
3. 2024 Membership upgrade to Pro → $666 only
🎉 Bonus ZoomEye-Points
1. Register before Nov 27, 00:00 HKT + buy any lifetime plan = Up to 3 million ZoomEye-Points
2. Use an invitation code → Both get 100k ZoomEye-Points
● Full details & rewards on the purchase page.
● All bonus ZoomEye-Points valid 1 year.
🎁 Giveaway — Winners announced on Dec 2 (HKT)
We're giving away 5× 1-month ZoomEye Professional memberships (worth $109 each)!
Just RT this post to enter.
Don't miss the biggest ZoomEye deal of the year!
👉 https://t.co/Wgj6iWm4sM
#BlackFridaySale #BlackFridayDeals #ZoomEye #cybersecurity #OSINT
📂 The folder isn't holding a resume — it's full of vulns.
🛰️ Introducing ZoomEye's BugBounty Radar.
🎯 Find bugs sharp, get paid hard. You know the drill 👀
🔗 Check it out: https://t.co/EHa2vFeXFT
🎉 Follow us (@zoomeye_team), send your ZoomEye account via Twitter DM, and receive a 7-day ZoomEye membership!
#BugBounty #Cybersecurity #Vulnerability #InfoSec #BugHunting
ZoomEye Bounty Radar #7 | How exactly is the "Changed" asset tag determined?
We've received a number of questions about the "Changed" asset tag — here's a closer look.
The following example illustrates how we detect changes based on HTTP headers between two scans:
Figure 1: Multiple fields in the HTTP header have changed between the previous scan (left) and the most recent one (right). This asset is tagged as "Changed".
Figure 2: Only the Set-Cookie field has changed. Since this is a non-static field, the asset is not tagged as "Changed".
By excluding non-static fields like Date, Set-Cookie, and others, we ensure that only meaningful changes trigger the "Changed" tag — helping you focus on what truly matters.
🚀 Learn to hunt smarter with BugBounty Radar — follow ZoomEye for daily tips.
DM us for 15 days of Bounty Radar access!
🔗 https://t.co/EHa2vFeXFT
#BugBounty #bugbountytip #CyberSec
ZoomEye Bounty Radar #2 | What is the scope of BugBounty Radar?
We aggregate program scopes from major bug bounty platforms: HackerOne, Bugcrowd, Intigriti, YesWeHack, and Open Bug Bounty. From these scopes, we extract in-scope domains and enumerate their subdomains. And yes, we update everything daily: Program scopes, in-scope domains, enumerated subdomains.
BugBounty Radar tracks every subdomain associated with active bug bounty programs — all in one place.
🚀 We'll be sharing tips on how to use BugBounty Radar over the next few days. Follow the official ZoomEye account to learn how to hunt smarter and earn more!
🔗 https://t.co/EHa2vFeXFT
#BugBounty #bugbountytip #CyberSec
🚀 BugBounty Radar Is Live!
ZoomEye now aggregates target domains from HackerOne, Bugcrowd, Intigriti, YesWeHack, and Open Bug Bounty, enhanced with real-time monitoring — built specifically for bug bounty hunters.
🔍 Key Features:
• Real-time alerts for new targets
• Auto-tracking of subdomains
• Live asset change detection
• Unified view across multiple platforms
✅ Available for: Professional and higher-tier membership
🎁 As long as you're registered on any bug bounty platform, follow @zoomeye_team and DM us your registration screenshot to get 15 days of free professional membership!
🔗 https://t.co/EHa2vFeXFT
✊ Not just a tool. A weapon — made for hunters.
#bugbounty #bugbountytip #OSINT #cybersecurity
🚀 ZoomEye × ProjectDiscovery Joint Campaign @pdnuclei
1. Contributor Rewards
Submit a Nuclei PoC with zoomeye-query syntax:
● 1-month ZoomEye personal membership (PoC with query)
● 7-day trial (query syntax only)
🎁 Rewards issued by the ProjectDiscovery team — more PoCs, more rewards!
2. Follow & Join Bonus
Follow ZoomEye Twitter (@zoomeye_team) + join ProjectDiscovery Discord (https://t.co/fwvEbDt8MI)
Send a screenshot via DM to @zoomeye_team to get a 15-day ZoomEye trial!
#BugBounty #Nuclei #HackingTools #Cybersecurity #ZoomEye