In just 24 hours 🤯
✓ 𝟲,𝟴𝟭𝟳 vulnerabilities identified
✓ 𝟱𝟴𝟬 critical or high
✓ 𝟭,𝟰𝟭𝟭 already patched by Agent
Vercel Security Reviews are 100% free until Nov 10
So, here’s what we’ve witnessed over the last few days:
@marclou vibecoded https://t.co/J4X4mhIBDi, an alternative to https://t.co/JsYjDvS3bR 83% cheaper.
@ahmedgagan11 built https://t.co/208VoU0yoq, a more affordable alternative to https://t.co/L3v6cD8beo with a one-time payment.
And now, @BinaryScriptar has dropped https://t.co/HHQGHNz5Zf, which is completely free.
Are we finally witnessing the death of SaaS in real time, or is something else happening that I’m not fully able to figure out yet?
@levelsio ???
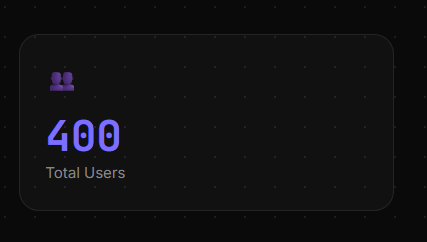
WonderLaunch just hit 400 users! 🚀
400 founders and makers in a community built to help indie products get discovered.
We’re building an alternative to Product Hunt where solo founders get a fair shot at visibility.
Still early. Still building. Next stop: 1,000. 👀
If you're building something, your next launch could be on WonderLaunch.
@wickedguro Huge respect to Nevo for this. Being this transparent and taking responsibility for your customers, even when things go wrong, says a lot about the kind of founder you are. This is how genuine trust is built. 🙌
It's 9:57 am. Been up all night. Postiz is back up!
Been a very hard night, and I feel like I let everybody down.
All the comments I got were very encouraging; nobody scolded me. Thank you so much for that!
During the day, a major PHP vulnerability was discovered, affecting about half the web.
Deployments on @railway stopped, and I assumed it was because of that, even though you do want deployments to upload the latest WordPress fix.
Everybody pinged Railway on Discord, and there was no answer- crickets... and people started getting extremely worried, especially because of >> PHP.
Then I got an email from Anthropic and Stripe saying my API keys were compromised. Still no answer from Railway, but I didn't take the risk; I rotated them and put Postiz down.
We all, even in Discord, already understood there was a leak, but Railway reported it only one hour later.
So the goal was to rotate all 140 keys (that's wild), because each key is duplicated across different containers (scattered). Some have the same variable with a different value (like different DB pool connections)
I was overwhelmed; it was too much, and I froze. I didn't know what to do.
I am lying on my Airbnb bed, but I know I need to get into sitting mode to be more serious, so I go to the kitchen and sit on a chair.
I asked claude to vibe code a system that:
- Will take all the keys and values from Railway (using their MCP)
- Will have an easy way to update all of them or one by one. Based on containers.
- Give me categories so I can be more organized. and prioritize.
I also started rotating keys from 12 am to 7 am.
All while Railway is still down and deployments are paused.
Once I finished I used Railway MCP to update all the env variables. if AI didn't exists I don't know how I could have done it.
Then, around 8:40am to 9:00am, we started deploying everything back to Railway to minimize downtime as much as possible.
And now everything is up.
I feel bad because DevRels at Railway sweet-talked me into staying after each incident and promised things wouldn't happen again; after two incidents, I should have migrated.
I couldn't find a platform I enjoyed as much as Railway, so I didn't want to switch.
Railway problems will happen again, and I will do everything I can to make sure they don't affect me like that anymore. The main problem was the lack of communication and 17 hours of downtime, which isn't realistic.
In the next few days, we will come up with a solid plan to migrate from Railway to a different service, trust is gone.
Also, Postiz grew from $300k to $303k MRR overnight. If you tried to cancel your subscription and couldn't, please contact [email protected], and they'll issue a full refund (super sorry about that).
This week, will be security week for everybody!
For a company trusted with critical infrastructure, transparency matters as much as security.
How long did it take from detecting the incident to informing users? When API keys and database credentials may be at risk, founders deserve a clear timeline, not just an urgent notice.
Trust takes years to build and minutes to lose.
@wickedguro Take your time, sir. You don't have to figure everything out today. You've built something incredible, and one difficult moment doesn't erase all the work you've put in. We're rooting for you. ❤️
The PHP security vulnerabilities and Railway’s API key leak are a reminder of how fragile our software infrastructure can be.
One vulnerability. One exposed secret. Potentially, an entire system at risk.
We’re entering an era where AI makes building software easier than ever, but securing it remains a serious challenge.
The future isn’t just about who can build software fastest.
It’s about who can build it securely. 🔐