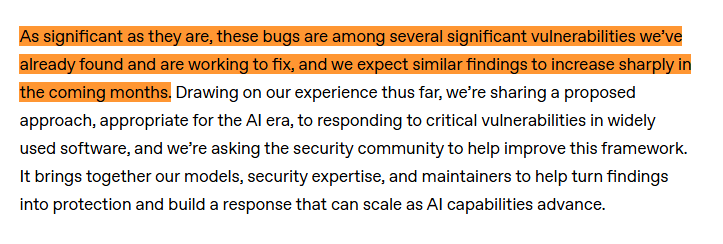
Holy Moly. OpenAI says it has found several other significant vulnerabilities beyond the two critical PHP flaws disclosed today and is still working to fix them. It expects similar discoveries to 'increase sharply in the coming months.'
Calif used GPT-5.6 Sol to uncover one PHP flaw; Wiz independently discovered both. PHP powers roughly 70% of websites. The two-month response involved Cloudflare, CISA and the White House's Super Intelligence Force.
@steipete Yeah… And even with planned release and partners informed weeks ago, the impact of it is this big.
So this was the ‘minimal impact’ plan there was for such a vuln.
Interesting times ahead🤷♀️.
@frankmariap3@bslagter Back je site up als je een eigen site hebt en zet ‘m op zwart. En dan maar even afwachten.
Maar uit deze post blijkt dat de release via OpenAI gelopen is, wat gelukkig betekent dat de grote jongens (AWS, cloudflare etc) wisten dat dit ging komen en zich hebben voorbereid.
OpenAI models helped researchers—operating as part of our Patch the Planet initiative—discover critical security flaws in PHP, an open-source programming language used to run an estimated 70% of websites.
Over the past two months, we led a coalition of maintainers, researchers, and security providers to prepare fixes and protections ahead of disclosure. This duration was necessary because the fix was quite intricate and required a major change to the PHP engine. Every site using PHP can now safely upgrade their version to stay secure, in addition to applying mitigations from various security vendors.
Due to the severity of these flaws and PHP’s widespread use, we consider this bug to be one of the most impactful vulnerabilities in recent memory. It also marks a new phase, where AI can find security bugs with internet-scale impact.
This is an example of the Defender’s Window in action: to our knowledge, frontier AI was able to find this vulnerability ahead of attackers, giving defenders time to prepare.
https://t.co/TW3jrSbB3f
Really? De echte vertaling:
‘PHP kwestie’ is een hele grote open deur in 50-70% van alle websites in de wereld, en om 16:00 wordt een design voor een nieuwe deur vrijgeven, en in dat design kan je ook zien waar de oude open deur staat.
Dus het wordt een race tussen aanvallers en verdedigers. En de aanvallers zijn met (veel) meer. (autonomous agents swarms)
If your website runs PHP or you are not sure if it does:
run a full backup.
As in now. You have about 45 mins left before we enter unexplored territory with an unknown outcome.
(Probably your site will be good, but better safe than sorry 👍)
#PHP2SHELL
@wol En dan werkt de halve site niet meer (input shizzle, contact forms etc). Wij snappen waarom dat komt, de gemiddelde bezoeker wordt boos.
Beter ff op zwart dan.
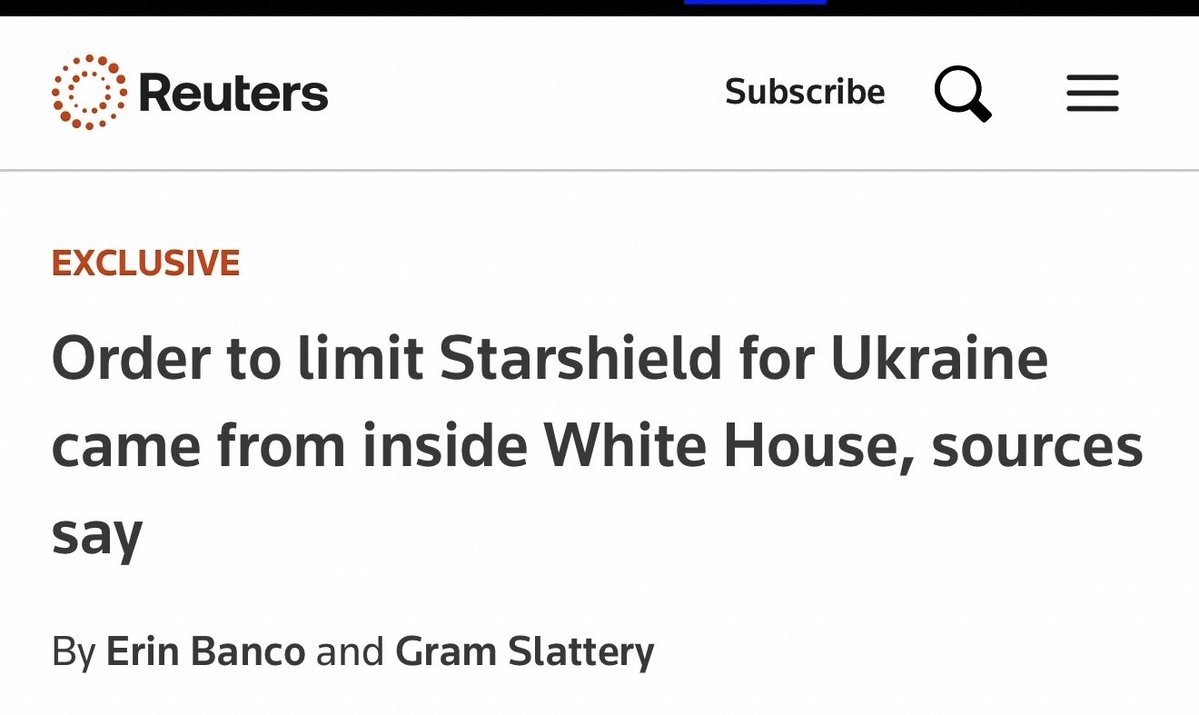
Reuters 🤷♀️.
Moeten we die dan geloven?
Nee, want ook geen bewijs.
En dan Rubio die Musk weer aanwijst maar bewust alleen heeft praat over StarLINK, niet StarSHIELD.
(En Starlink mocht al nooit voor aanvals-drones gebruikt worden, dat was Starshield).
Kortom: geloof geen krantenkoppen, informeer jezelf. 👍
Partly: about 45% of websites are directly vulnerable. Current exploit seems only partial succesful at most.
But 14:00 UTC, the patch comes out, revealing the whole vulnerability. Then, in 15 mins, exploits will come out.
Then, for the first time in history, we may see autonomous Open Model Agent Swarms (OMAS) attack at scale.
We’re entering unexplored territory today. Outcome: unknown.
@HennaVirkkunen Today, half the internet (70% runs php) becomes vulnerable to attack because of a huge bug in PHP. Millions of websites. Critical point 14:00 UTC, mass exploits expected 15 mins after that.
@HennaVirkkunen : Today we go chase Booking for DSA fines.
I…I can’t even.
@grok vat ook samen hoe vaak WSJ hard en objectief bewijs heeft geleverd voor hun beschuldigingen aan musk, en hoe vaak het ging om anonieme bronnen, verhalen en ‘hearsay’.
Pak dan ook meteen mee hoe vaak WSJ in haar artikelen argumenten die hun beschuldigingen tegenspreken in hun verhalen werden vermeld versus hoe vaak deze werden weggelaten