The first point is about refusing to reward a community member who built a project based on tech they're distancing from. Call it "unaligned circumstances".. Ofc they would never say it out loud, but it's something worth considering.
I replied to the 2nd point in another comment.
Yes, they shouldn't have. First off, community voting is retarded because the public doesn't possess the skill set to evaluate projects properly. They see something that appears nice on the surface and vote for it.
Secondly, most judges are in community-adjacent roles ("growth lead", "research at [xyz]", "tech writers" with no readers) who are either incapable of judging a project properly or lack the time to do so. When there are hundreds of submissions to wade through, it's no surprise if they cut corners. I suspect OP has @primordialaa to thank for boosting the project's credibility because he praised it in the replies while OFT sentinel was still being built (=potential epistemic deference by the judges). But I don't think Bryan had the time to actually inspect it.
Something like the OFT sentinel is useless for real monitoring. It's more of a gimmicky demo and on those grounds the prize seems excessive.
🚨 NEW info just dropped about why the Wyoming government deprecated @LayerZero_Core and migrated $FRNT to @Chainlink CCIP 👀
And it doesn’t look good 🤦♂️
According to @LawhornKA, CISO of the Wyoming Stable Token Commisison (@wyostable), the Commission conducted an extensive review of LayerZero Labs’ security posture and access-control processes
From this review, they discovered a repeated pattern of major operational security failures at @LayerZero_Labs, including:
- the failure to maintain proper control of a critical private key used to manage a live production FRNT deployment (!!)
- a recent access-control issue in which the company failed to transfer a production authorization to the Commission
- inadequate disclosures provided about incidents, both public and private
Yes, you read that right, LayerZero Labs lost control of a private key used to manage a live production deployment of the Wyoming state government’s stablecoin
This massive issue is in ADDITION to the $292 million LayerZero exploit, in which hackers affiliated with North Korea (DPRK) breached LayerZero Labs’ infra
And in addition to LayerZero Labs’ mismanagement of 3 production multisig keys that were engaged in non-multisig related activity (incl “McPepes” memecoin trading) on their production 2-of-5 Gnosis Safe multisig used to manage billions in user value
TL;DR: Based on all available public information, @LayerZero_Labs has one of the worst operational security track records in the entire blockchain industry and should be never allowed to touch a multisig private key ever again
Another DEVESTATING investigation that concludes AGAINST @LayerZero_Core
It is now painfully obvious why the migration to the @chainlink cross-chain standard is happening.
It doesn't matter how much money VC's pump into LZ, at its core, it is untrustworthy.
So, this new blog from the Chief Information Security Officer of the Wyoming Stablecoin has revealed a whole new cesspit of issues with LayerZero:
>LayerZero repeated pattern of operational security failures
So, there were even *MORE* opsec failures beyond North Korea hacking LayerZero Lab's DVN, specifically relevant to the work between the state of Wyoming and LayerZero.
>Lost control of the private key for the state of Wyoming
How do you simply just "lose control of a private key" which controls government assets?
Was Wyoming's token contract being entrusted to a single employee rather than a set of signers?
If so, what kind of employee are you not able to get a private key back from? Did they literally just lose the key because it was scribbled on a napkin?
Or did the employee simply refuse to give the private key back? if that's the case, what kind of employee and under what set of circumstances would be willing to do that?
Given that LayerZero's previous DVN hack involved inflitration by North Korea, one possible hypothesis could be that this "lost control of a private key" with Wyoming reads as North Korean involvement again.
>Inadequate disclosures about incidents
This is a polite way of saying that the LayerZero team then proceeded to lie to the state of Wyoming about what is actually happening with the safety of their assets.
If LayerZero is willing to cut corners on security and then lie to a government-level partner, how could anyone even trust them for anything?
If they will lie to the government, why would you believe their claims about their volume numbers being organic?
If they will lie to the government (which could cause serious legal issues), why wouldn't they lie to their other integration partners?
If they will lie to the government, why would you believe them about literally anything at all?
$ZRO
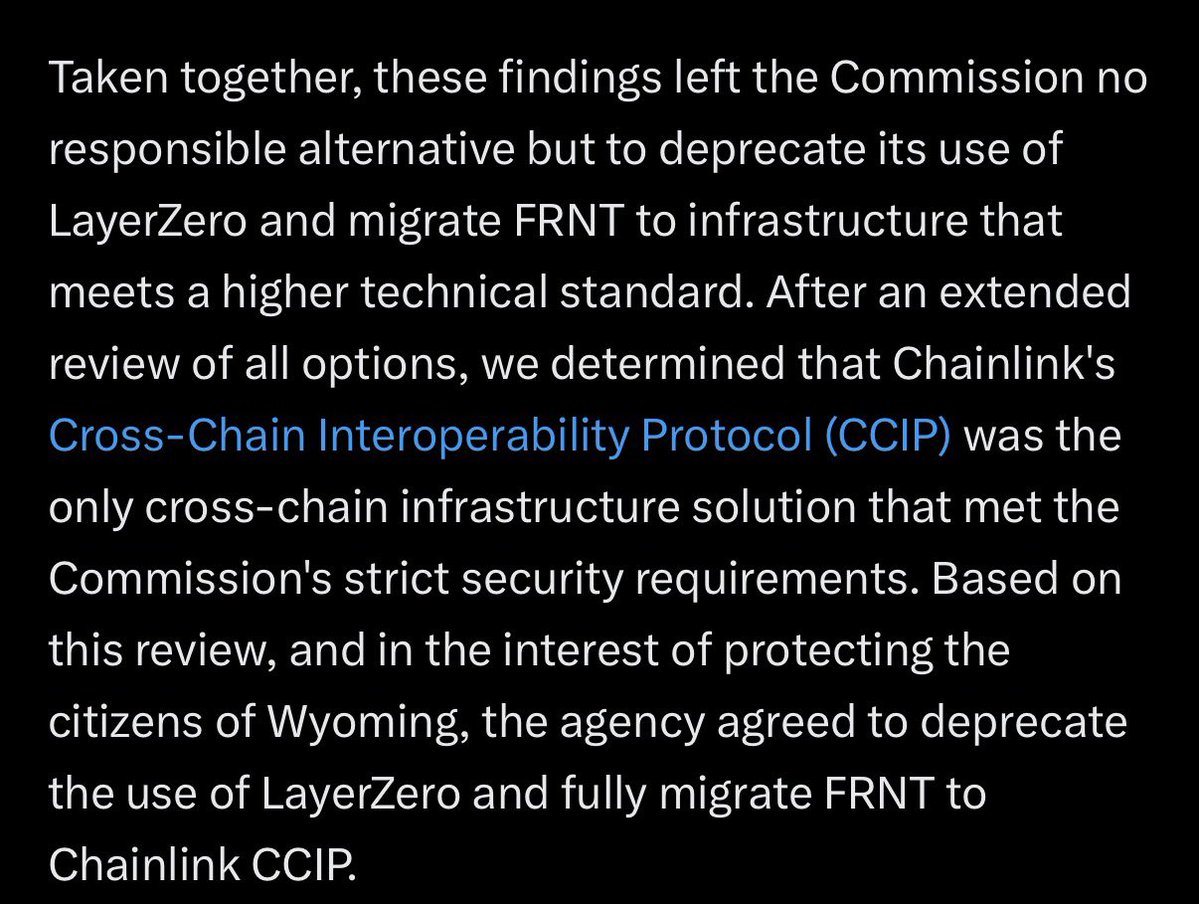
Wyoming Explains why $FRNT stablecoin was migrated to Chainlink from LayerZero
The Wyoming Stable Token Commission has offered transparency regarding its decision to migrate the $FRNT stable token from @LayerZero_Core to @Chainlink CCIP in August.
It is reported that the main reason for the decision was a "consistent pattern of major operational security failures," including access control and private key management risks.
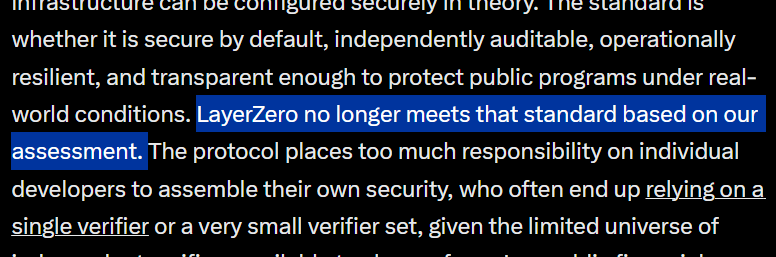
The organization noted that LayerZero could not satisfy the requirements needed for state-owned digital assets.
"the teams that understood what they were building on weren't at risk."
Of course they were. LZ Labs can forge messages unless you set the configuration. And until very recently over $3b in OFTs were still exposed to compromise because they relied on a default library contract that lz labs could instantly upgrade. Ethena and Etherfi were also unaware of it.
Your infrastructure was compromised, so own up to it.
"Yeah but we didn't think anyone would RELY on that infrastructure" isn't an excuse
Trust in LZ will tank, and it deserves to, after this.
@PaikCapital@DefiIgnas There are rules for what is allowed on the road. Meanwhile lz is like yeah sure, send the horse cart onto the autobahn bro, what's the worst that could happen.
@tayvano_@d3h3d_@torabyou What are we even doing here then? What's the point of crypto if censorship resistance is not a goal? Recreating tradfi rails with better tech?