‼️MALWARE ALERT — Absolute Eye RAT
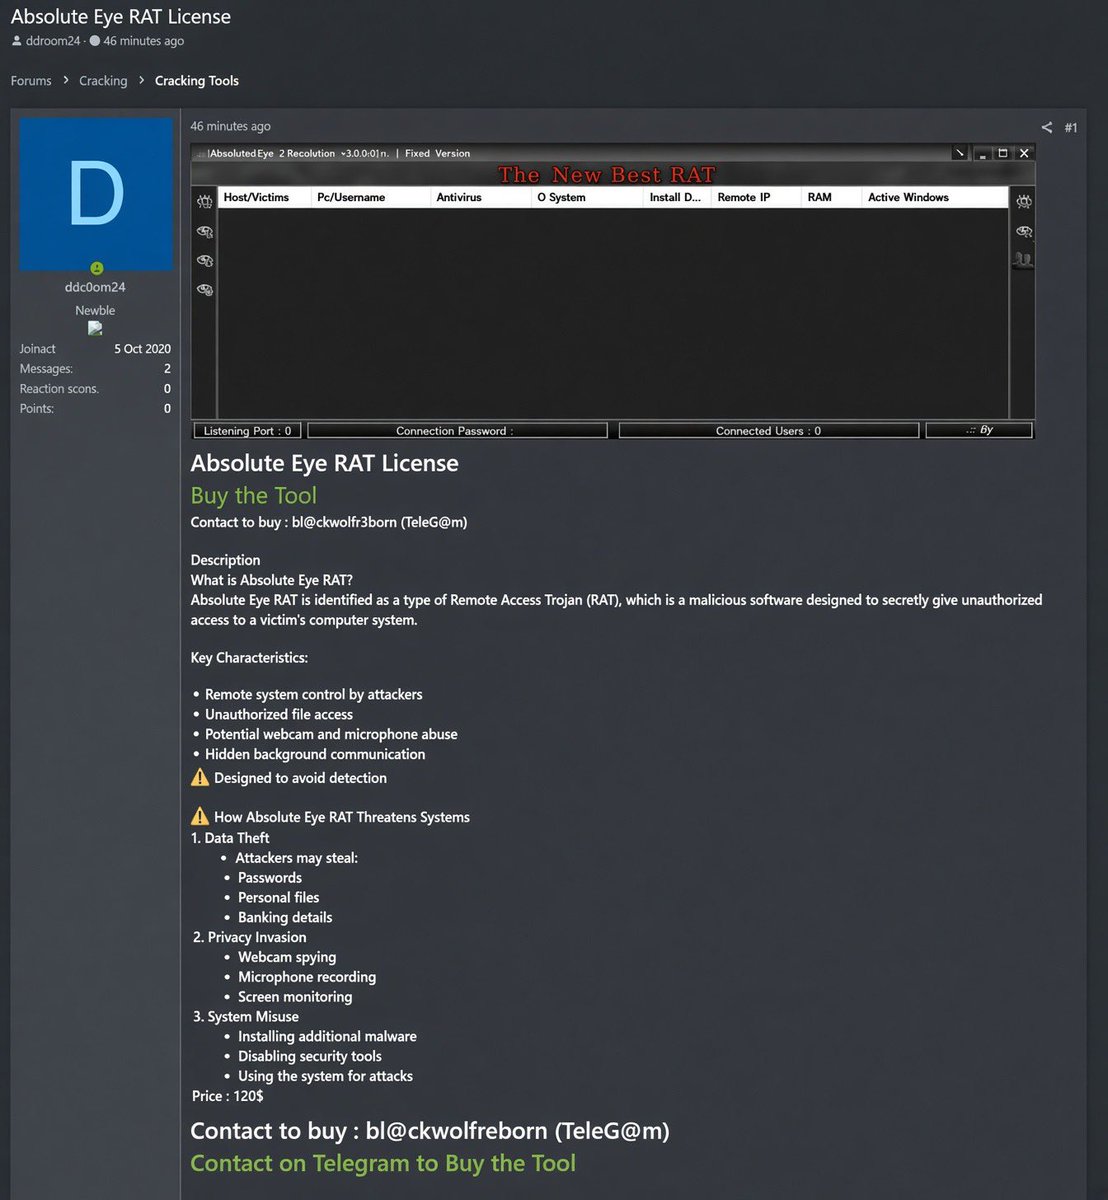
A forum post is advertising Absolute Eye RAT, a Windows Remote Access Trojan (RAT) reportedly offered for $120.
⚠️ Reported capabilities include:
• Unauthorized remote system control
• File access and data theft
• Webcam & microphone surveillance
• Screen monitoring
• Hidden background communication
• Potential credential and banking-data theft
• Possible installation of additional malware
• Attempts to evade detection or disable security tools
RAT infections can enable persistent surveillance and unauthorized access. Avoid suspicious/cracked RAT builds and use reputable security software.
#CyberSecurity #Malware #AbsoluteEyeRAT #RAT #ThreatIntelligence #Infosec #MalwareAlert
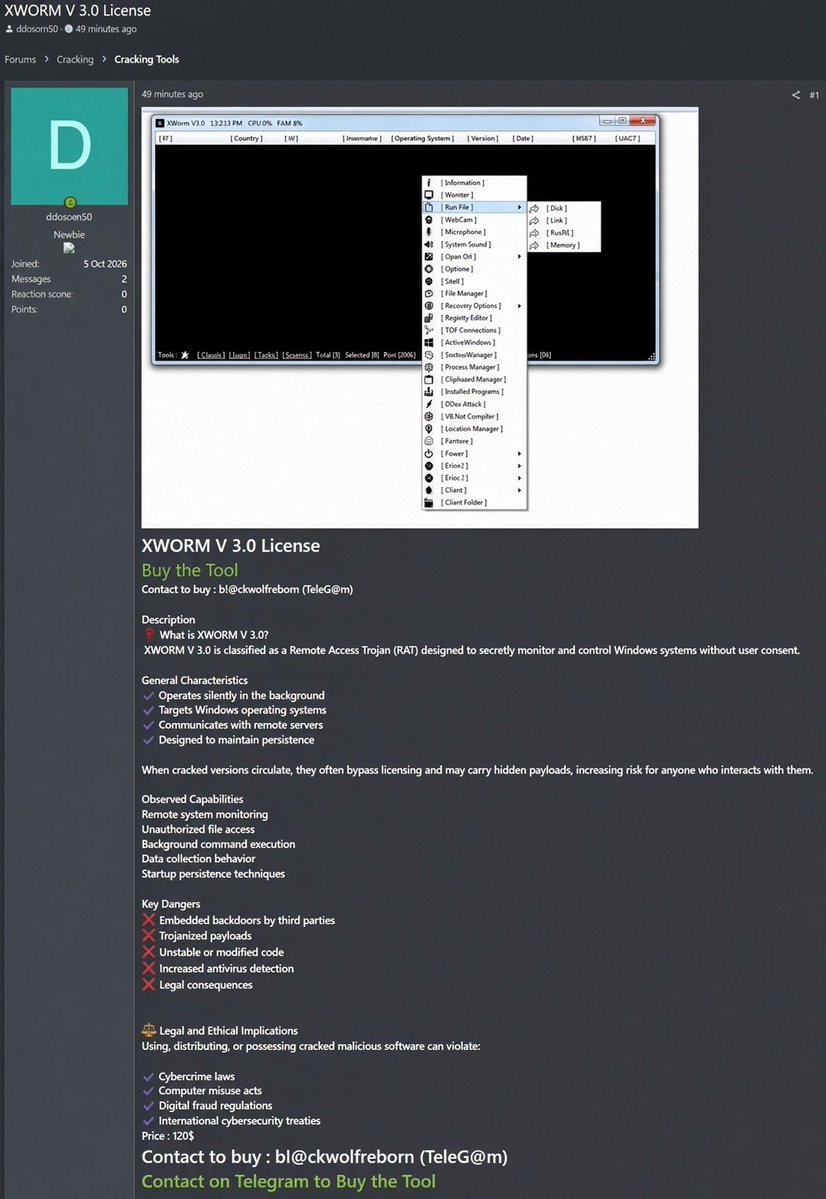
‼️MALWARE ALERT — XWORM v3.0 RAT
A forum post is advertising XWORM v3.0, a Windows Remote Access Trojan (RAT), reportedly offered for $1,205.
⚠️ Reported capabilities include:
• Remote system monitoring/control
• File access
• Command execution
• Data collection
• Startup persistence
• Communication with remote servers
Cracked or modified versions may introduce additional malicious payloads, backdoors, or other unwanted code.
🛡️ Users should avoid downloading, purchasing, or executing unauthorized/cracked RAT builds and rely on trusted security software and legitimate sources.
#CyberSecurity #Malware #XWORM #RAT #ThreatIntelligence #Infosec #MalwareAlert
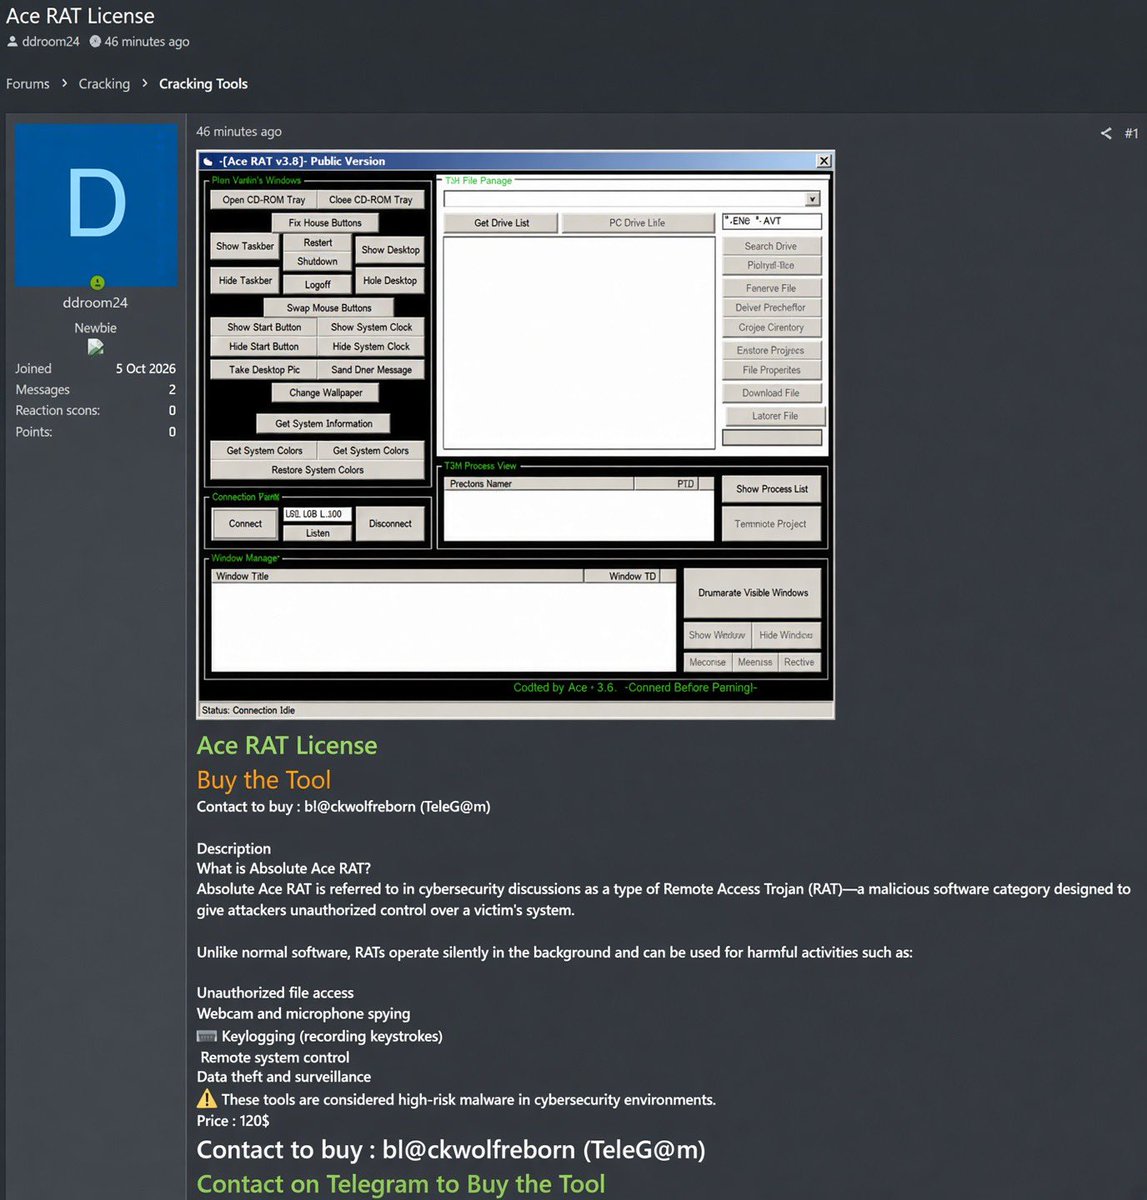
‼️MALWARE ALERT — Ace RAT v3.8
A forum post is advertising Ace RAT v3.8, a Windows Remote Access Trojan (RAT) reportedly offered for $120.
⚠️ Reported capabilities include:
• Remote system control
• File browsing, upload/download & deletion
• Process and window management
• System information collection
• Desktop screenshots
• Keylogging
• Webcam/microphone surveillance
• Remote shutdown, restart & logoff
• Wallpaper and system-setting manipulation
RATs can enable unauthorized access, surveillance and data theft. Avoid downloading or executing suspicious/cracked RAT builds and use reputable security software.
#CyberSecurity #Malware #AceRAT #RAT #ThreatIntelligence #Infosec #MalwareAlert
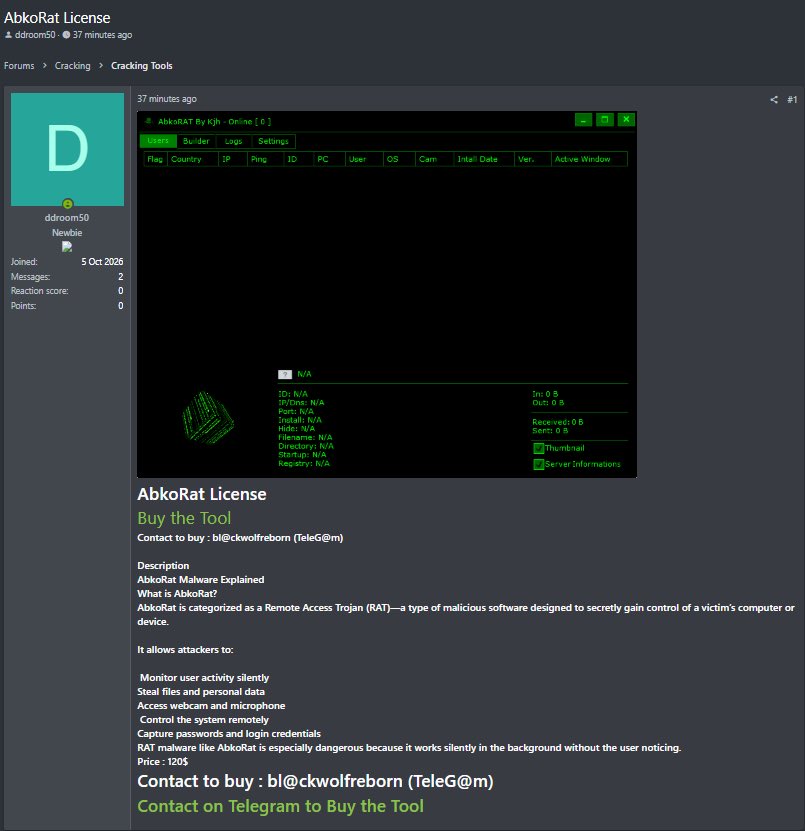
‼️MALWARE ALERT — AboRat RAT
A forum post is advertising AboRat, a Remote Access Trojan (RAT) reportedly offered for $120.
⚠️ Reported capabilities include:
• Remote system control
• User activity monitoring
• File & personal-data theft
• Webcam & microphone access
• Password/credential theft
• Silent background operation
🛡️ Avoid downloading or executing unauthorized RAT tools or cracked builds. Use reputable security software and trusted sources.
#CyberSecurity #Malware #AboRat #RAT #ThreatIntelligence #Infosec #MalwareAlert
⚠️ PREVENTIVE ALERT 🌐 💻: REPORTED EMERGENCE OF A NEW UNDERGROUND FORUM (PWSFORUMS)
The centralized cyber-intelligence system has logged a new alert based on activity detected across social media and monitoring platforms. The captured data reveals the existence of a new underground forum named PwsForums (pwsforums .pw), where activity from profiles known within the cybercrime ecosystem has been observed.
#Cybersecurity #ThreatIntel #PwsForums #ShinyHunters #DarkWeb #DataLeak #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
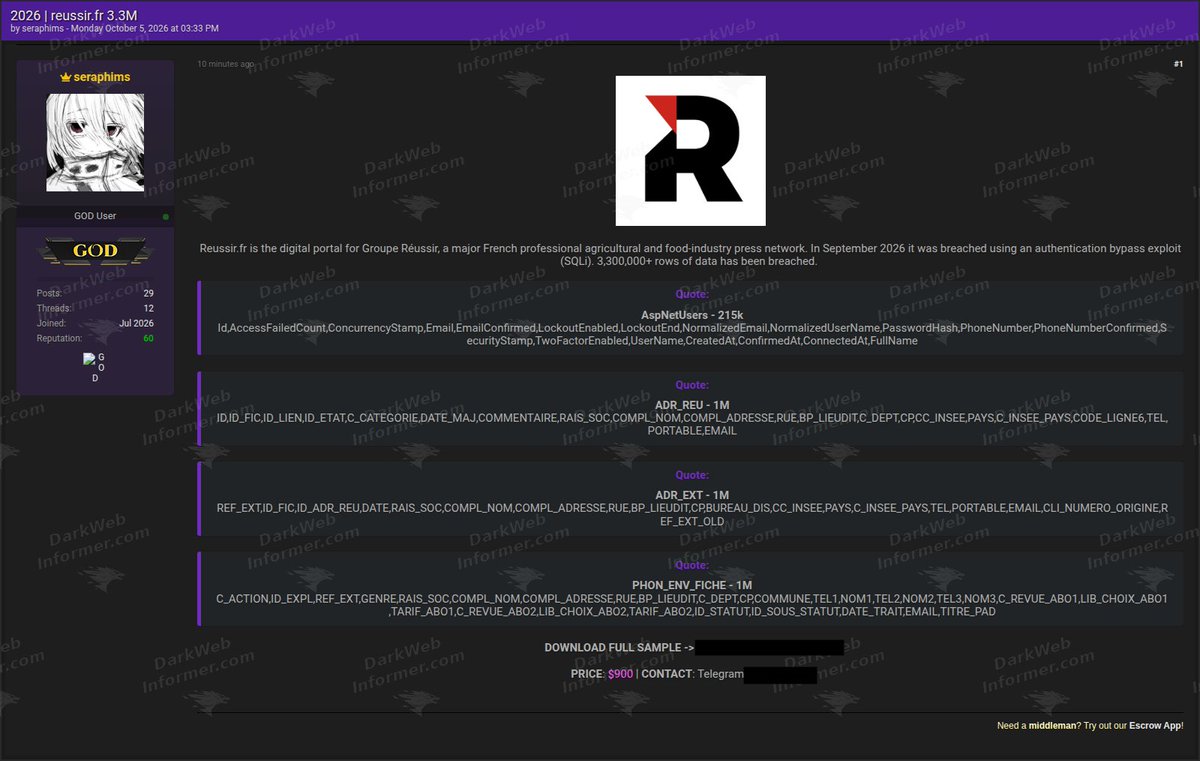
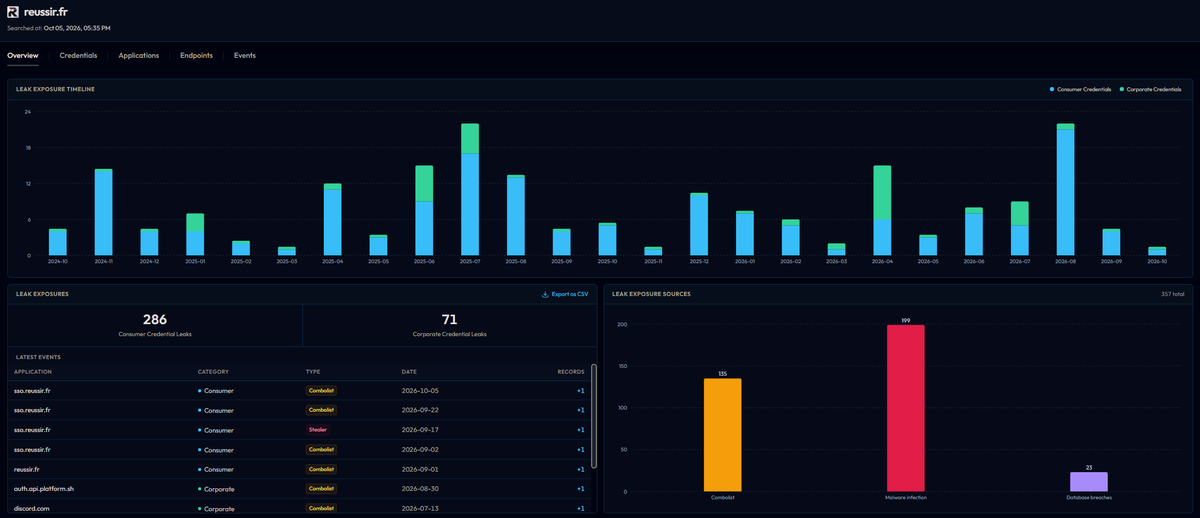
🚨🇫🇷 Groupe Réussir Dataset With 3.3 Million Records Allegedly Breached
A dataset allegedly belonging to French agricultural and food-industry media group Groupe Réussir has been offered for sale.
The actor claims an authentication bypass was used to obtain approximately 3.3 million records containing names, email addresses, phone numbers, addresses, account information, password hashes, and other customer data.
The dataset is being offered for $900.
Claim is currently unverified.
Infostealer data via @whiteintel_io
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. https://t.co/281Qjc6p2J
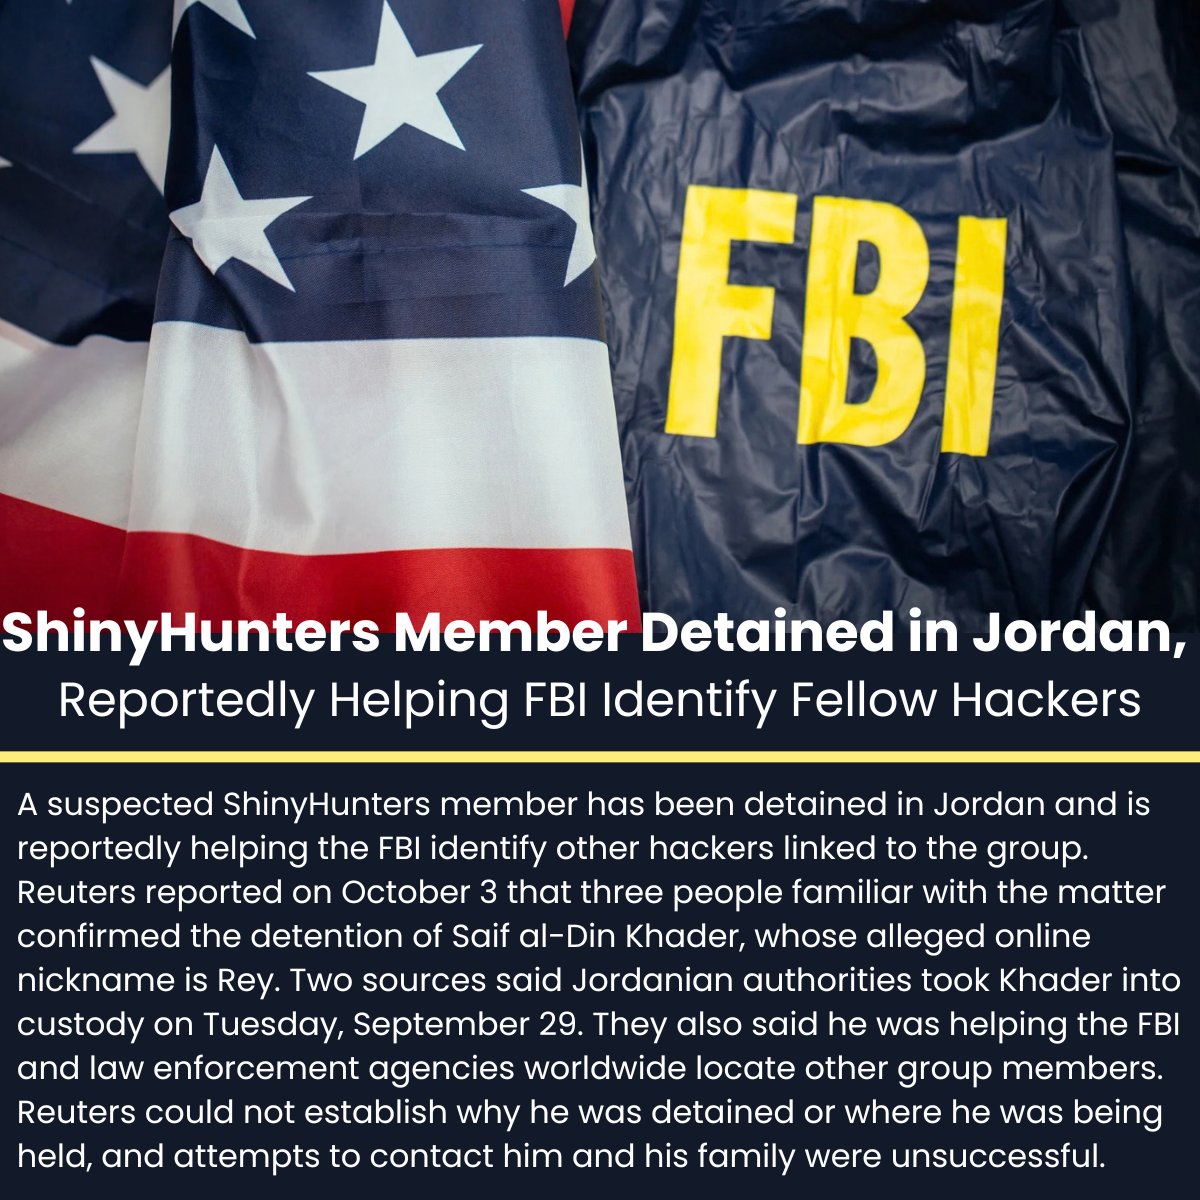
‼️ BREAKING - ShinyHunters Member Detained in Jordan, Reportedly Helping FBI Identify Fellow Hackers
Details: https://t.co/OV2TpHHWv0
A suspected ShinyHunters member has been detained in Jordan and is reportedly helping the FBI identify other hackers linked to the group. Reuters reported on October 3 that three people familiar with the matter confirmed the detention of Saif al-Din Khader, whose alleged online nickname is Rey.
Two sources said Jordanian authorities took Khader into custody on Tuesday, September 29. They also said he was helping the FBI and law enforcement agencies worldwide locate other group members. Reuters could not establish why he was detained or where he was being held, and attempts to contact him and his family were unsuccessful.
#cybersecuritynews
#ALERT ‼️ One of the head ShinyHunters Members Detained in Jordan
Saif al-Din Khader, an alleged key member of ShinyHunters who reportedly uses the handle "Rey” @dulls was detained by Jordanian authorities earlier this week for FBIjob hack, according to Reuters.
#cybersecurity
‼️ BREAKING: A key member of ShinyHunters has been detained in Jordan and is now helping the FBI identify the rest of the group that claims to have stolen data on every bureau employee, sources tell Reuters.
The sources name him as Saif al-Din Khader, alleged alias "Rey", and say he was taken into custody on Tuesday.
He told KrebsOnSecurity in 2025 that he was "already cooperating with law enforcement", a claim Krebs could not verify.
Default Passwords for Nearly Every SCADA System
Maybe not surprisingly, many SCADA systems still are authenticated with their default passwords from the manufacturer. The list can be useful during a pentest. Make sure you're safe!
https://t.co/yVnSOV9ghu