If you've ever wondered why smart TVs are so cheap, this is why.
@log4j rooted his Samsung and found an always-on hot mic, automatic content recognition, geolocation, network mapping, ad targeting and user profiling, shared with Samsung's "400 partners".
A lot of it can be blocked in <15 min, wrote a basic guide below.
What your TV is doing
The main culprit is ACR (automatic content recognition). Your TV screenshots what's on screen, fingerprints it, and sends it home to build your ad profile. Samsung does it every 500ms, LG every 10ms [1].
What is insane: it happens on connected devices too.
Plug in your laptop, your console, your work machine, and your TV can fingerprint that via HDMI [1].
He also found that if your Samsung doesn't have a mic, it'll look for one from a connected soundbar or bluetooth device.
https://t.co/vNdTnIQ6KF
It's on by default, and you likely agreed to it on the setup screen you clicked through in 10 seconds.
Step 1: Turn off ACR
Samsung: Terms & Privacy → Viewing Information Services
LG: Live Plus
Vizio: Viewing Data
Roku: "Use info from TV inputs"
Sony/Google TV: Samba Interactive TV
Menus vary by model, but those are the names to look for. While you're in there, opt out of interest-based ads, reset your advertising ID, decline every optional privacy agreement, turn off voice recognition, and delete apps you never open.
Step 2: Give smart devices their own network
Put the TV, cameras, speakers and vacuum on your router's guest/IoT network. The logic is simple: these devices rarely get patched. If one gets compromised (getting drastically more frequent with AI), it shouldn't be able to see your other devices or home network.
Step 3: Block trackers for the whole house with DNS-level filtering
NextDNS (cloud-based) is easy and has a solid free plan. Pi-hole is a little bit more work if you prefer self hosting. For simplicity we'll focus on the former.
1. Sign up at https://t.co/IwhafVWVM8 (free tier is plenty)
2. Privacy tab: add a blocklist (OISD is a good bet) and turn on Native Tracking Protection for Samsung, LG, Roku, Amazon (see attached image)
3. Setup tab: copy your endpoint
4. Paste it into your router's DNS settings as DNS-over-HTTPS/TLS (or use the IPs + "Link IP" if your router only does plain DNS)
5. Bonus: block outbound port 53 except to your router. Some devices hardcode their own DNS to get around you
Then open the NextDNS logs and watch how often your TV phones home. It's eye-opening. If an app or update breaks, find the domain in the logs and allowlist it.
Why they do this
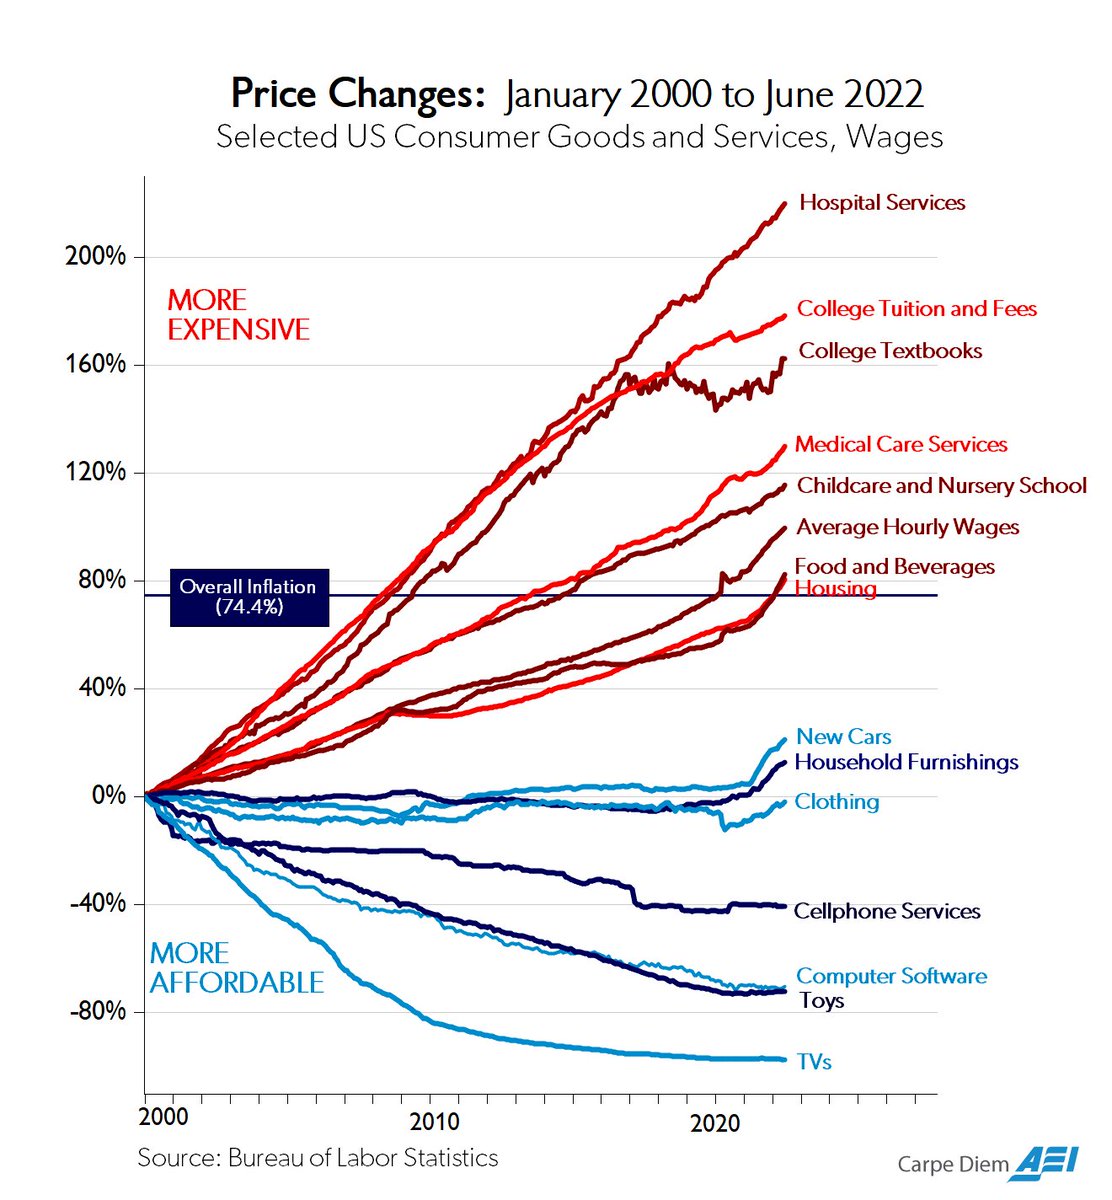
TV prices are down 97% since 2000 [2]. Most of that is better manufacturing and brutal competition. But once margins on the hardware hit zero, the cost moved to you.
In Q3 2024, Vizio lost $6.7M selling TVs and made $115.8M in gross profit from ads and viewing data [3]. They've said on earnings calls that they keep TV prices low to grow the audience they sell to advertisers. Walmart bought them in 2024.
This isn't a conspiracy theory either. Vizio paid $2.2M to the FTC in 2017 for tracking 11 million TVs without consent. Last December, Texas sued Samsung, LG, Sony, Hisense and TCL over ACR. Samsung and LG have since agreed to stop collecting that data without explicit consent [4].
TL;DR
1. ACR off
2. Ads + voice off
3. Smart devices on their own network
4. NextDNS filtering on the router
Sources:
[1] ACR study: https://t.co/S1IS8lXNbA
[2] Cost of US consumer goods: https://t.co/nclXELXcbd
[3] Vizio Q3 2024: https://t.co/CrVbwc9ZXk
[4] Texas v. Samsung: https://t.co/wFOUdeh1if
@levie Happy to show you how we’re approaching it at https://t.co/IhfjdRbgpN - analyzing intel with swarms of agents and then organizing teams of agentic fixers. Giving away most of the correlated intel.
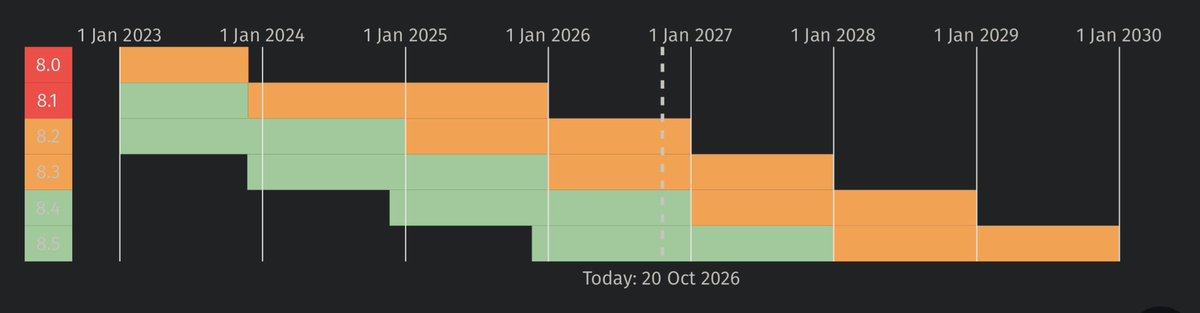
Okay, since the news is already out: an RCE vulnerability in PHP core, CVSS 10.0. Further details are scheduled for release on October 20. Only PHP 8 will receive patches.
@johnmcclure00 Tracking ~49 exploitation reports and 2 public exploits for CVE-2026-88779. It hit KEV the day it was published (Oct 4), so there was no patch-first window. If you're hunting, check SAML/AAA crashes and restarts. If you want more details: https://t.co/6IGCQhC2mz
The potential impact of the ConnectWise supply chain attack is massive.
One compromised OAuth application with elevated permissions could give attackers access to emails, files, and directory data across hundreds of Microsoft 365 tenants.
Even worse, attackers could establish persistent access by adding credentials to other applications, surviving the revocation of the original compromised credentials.
And with MSPs involved, the potential blast radius could extend even further to downstream customers.
We don't know the full extent of the compromise yet, but this could affect far more organizations than those directly using ConnectWise Cloud Backup.
https://t.co/0RMJugvcrM
If AI didn’t exist and I came to the infosec community and said “here’s a magic box that finds 0days” and “here’s another box that can autonomously scan networks for misconfigurations”, they’d be jumping up and down to see if we could glue together a self-replicating worm. 1/
it's funny how hard it is to get a text editor out of any of the ai tools now - even @cursor_ai. we’re in this weird teenager phase.
moving from coding to systems engineering.