Zero-day remote code execution vulnerability in iPhone Safari. Click a link, and your crypto, passwords and everything else on your iPhone are gone.
Exploited in the wild by "DarkSword" malware.
"The DarkSword attack program has leaked, with its core capability being: extracting forensic-level data from iOS devices via HTTP interfaces. In actual attacks, attackers can combine social engineering or watering hole attacks to lure users into falling victim, thereby stealing data from iPhone / iPad devices and uploading it to servers controlled by the attackers."
Update iPhones immediately. Apple originally patched this, but rumours suggest even the latest versions are vulnerable, “pending confirmation,” across a wider range than the original 18.4–18.7 window.
From a Chinese security researcher, SlowMist CISO, @im23pds
https://t.co/hIRaGvEha9
Gary Neville: "I've watched #mufc since the age of five and that's the worst 15 minutes I've ever seen. Absolutely pathetic. I've never seen such a lack of effort. What must Carrick be thinking?" [@ChrisWheelerDM, sky]
A decaída da Nike será estudada e entrará pra história.
Inclusive, não sei se vocês sabem mas o fundador da ON é o Olivier Bernhard, que era um atleta patrocinado pela Nike.
Ele mostrou o protótipo do tênis e da tecnologia que veio a ser o grande diferencial da ON para Nike que rejeitou a ideia por enxergar o potencial comercial do que chamou de design estranho.
The executives said the boardroom Wi-Fi “feels slow.”
Speed test: 487 Mbps.
Apparently 487 Mbps has bad energy.
So I created a new network:
EXECUTIVE_PRIORITY_5G
Same access points.
Same internet connection.
Same VLAN.
I just gave it a more expensive name.
Connected the CEO.
He opened a website and immediately said:
“Oh wow, this is way faster.”
By lunch, five VPs had asked for access.
I told them executive bandwidth is limited and I can only approve users with a genuine business requirement.
They are now competing for access to Wi-Fi they already had.
Performance is unchanged.
Satisfaction is through the roof.
CANADA HAS BEEN INVITED TO BE AN ASSOCIATE MEMBER OF THE EU!
"We want to bring the relationship with Canada to the highest level possible. We are opening the door for Canada to being the first associate member of the European Union"
If you need this much explaining to defend a goal, clearly something is wrong, that being said, city played much smarter than United today. Patrick Dorgu man, 🤦🏽♂️
Just had the creepiest scam ever happen 20 minutes ago.
I got a call from my wife telling me she forgot her wallet and needed the credit card to pay for her gas.
Except my wife was at home with me, and drives a Tesla. Same voice, bit... off, weird cadence but 100% sounded just like her. If she wasn't there, and it wasn't about gas I would have fallen for it.
I entertained it for awhile to get more out of it, I was so confused. Must be some sort of voice deepfake. The responses were too fast for ai, I think it was a voice filter. I wish I had thought to record it.
The future is about to get fucked. Warn your loved ones, do verbal passwords with your kids.
Bit taken aback
See.. Kobbie in 21/22. In youth football. Look at he range of passing that some says he needs.
Was always there. But people were busy looking at things like "but can he run"
Talent smacking everyone in the face. England or countries don't make talent like this often. Really.
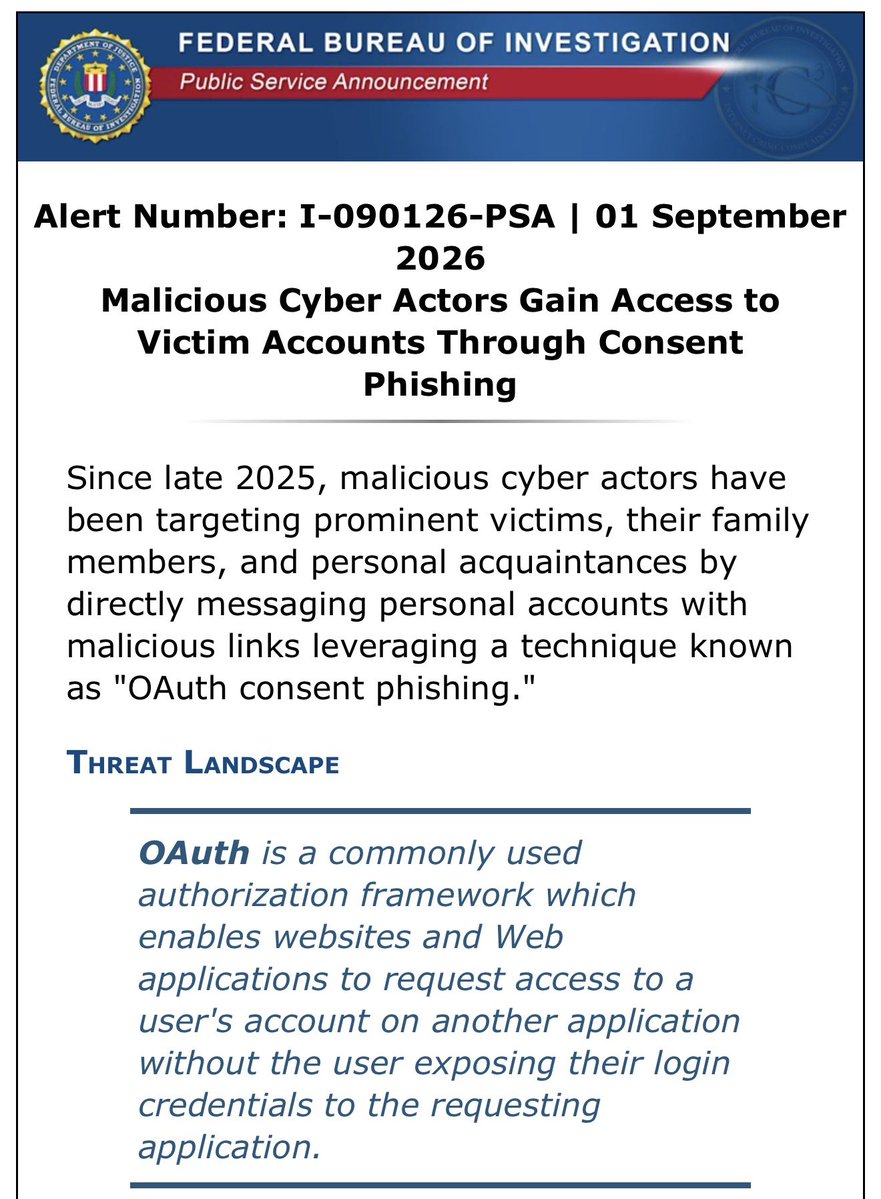
🚨 FBI WARNS OF OAUTH CONSENT PHISHING TARGETING PROMINENT INDIVIDUALS
The FBI is warning about an ongoing phishing campaign that can give attackers persistent access to email, files and other sensitive account data — without stealing the victim's password.
According to an official FBI/IC3 alert, malicious cyber actors have been targeting prominent individuals, their family members and personal acquaintances since late 2025 using OAuth consent phishing.
The attack abuses legitimate authorization mechanisms.
Here's how it works:
* Attackers create and register a malicious application with a legitimate OAuth provider
* The application requests powerful permissions, potentially including access to emails and files
* Targets receive phishing links through email, text or commercial messaging applications
* Attackers may impersonate journalists, academics, government officials, media personalities, event organizers or other trusted identities
* The victim is redirected to a legitimate cloud-provider authentication page
* The victim authenticates normally
* A legitimate-looking consent screen asks the victim to authorize the malicious application
* If the victim clicks "Allow," the application receives the requested permissions
The attacker never needs to receive the victim's password.
And MFA may still work exactly as designed.
The victim has authenticated successfully — but has been socially engineered into authorizing the attacker's application.
🚨 PASSWORD RESET ≠ REMEDIATION
This is where OAuth consent phishing becomes particularly dangerous.
The FBI warns that changing the account password does NOT necessarily remove the attacker's access.
The OAuth token can continue providing persistent API access until the malicious application's authorization/token is explicitly revoked.
Depending on the permissions granted, an attacker may be able to:
* Read emails
* Send emails as the victim
* Access cloud files
* Obtain sensitive information
* Maintain persistent access without repeatedly authenticating
⚠️ Analyst Note:
This is an important distinction for defenders:
Authentication succeeded.
MFA succeeded.
The user was still compromised.
OAuth consent phishing attacks the authorization layer rather than simply attempting to defeat authentication.
For organizations heavily dependent on Microsoft 365, Google Workspace and other SaaS platforms, security teams should treat OAuth applications, delegated permissions, consent grants and access tokens as part of the identity attack surface.
Password resets alone are not sufficient incident response when malicious OAuth authorization is involved.
Review and revoke unauthorized applications and tokens, restrict user consent where appropriate, monitor unusual application registrations and permission grants, and investigate abnormal API activity.
Official source — FBI / IC3:
https://t.co/lX25uaqlbK
#DDW #OAuth #Phishing #MFA #CyberSecurity
We are officially entering “Global Water Bankruptcy”.
The UN has announced that we will start running out of clean water (drinking, cooking, showering, dishes, laundry, etc.) in the next few years.
Water won't always be free. When clean water becomes scarce, it will be privatized, priced, and controlled. You will pay for it. And those who can't pay won't survive.
Data centers don’t actually need water. Data centers need cooling system and they are using water because it’s the most cheapest way to do it. Water should be for people before profits.
The world must remember that we live in a society, not an economy.