It’s amazing how much more accessible our motivation to exercise, do focused work, and generally feeling good, is, when we get our sleep-wake rhythms even mostly right. Viewing morning sunlight is a powerful lever to organize all that. It sets the foundation.
For specific protocols at zero cost, go to https://t.co/GYeOKlrJTD and put any combination of items into the search function and it will take you to the exact time stamps —meaning you don’t have to listen to entire episodes. It will also take you to our zero cost newsletter on this topic. Thank you for your interest in science!
Take care of yourself and take care of others. Daily investment in the 6 pillars is the way: morning sunlight, daily movement, quality nutrition, stress control, healthy relationships, deep sleep. Re-up every 24hrs so you can contribute and support others consistently too.
. #infosecurity and #IT professionals, join us tomorrow for a sneak peek into the future of cybersecurity with Nikesh Arora, Nir Zuk, and other exciting speakers on why ZTNA 2.0 is the best way to secure your organization moving forward. Register here! https://t.co/AzZq7u8Jd6
Wherever work happens, cyber threats are always nearby. Legacy cybersecurity can’t stop them. We need Zero Trust with Zero Exceptions. Industry-leading protection for all users, applications and data. https://t.co/O1uqF50u4m
#SecuredByPANW#WeveGotNext
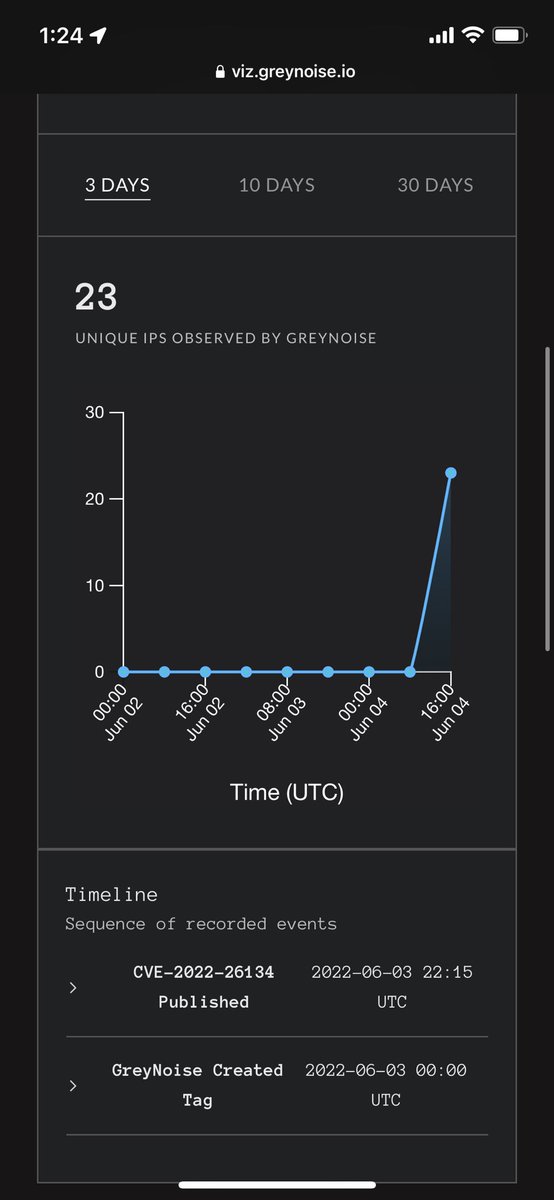
Widespread Atlassian Confluence CVE-2022-26134 exploitation, specifically that is *confirmed functional*, has just started. 23 unique IPs so far.
-Tags available to all @GreyNoiseIO users now
- Create an account to deploy a dynamic block list to block it
https://t.co/dbXTw2LWY6
.@Volexity discovers zero-day exploit impacting all current versions of Atlassian Confluence Server and Data Center. Attackers deploy in-memory Java implant to evade detection. Read more in our latest blog post: https://t.co/aCSwnSUfj8 #DFIR#ThreatIntel#InfoSec
Unable to extract credentials via DPAPI or Mimikatz? Don't worry. Microsoft got your back. Just use 'rundll32 keymgr.dll, KRShowKeyMgr' to extract all the stored passwords on the host, be it a target server, FTP or chrome's HTTP creds, microsoft has you covered. #redteam
In light of the Russian ground invasion of Ukraine, we (@GreyNoise) are doing a few things to be as helpful as possible for network defenders in Ukraine. I understand that the impact will be small all things considered, but this is just where we are:
I've had 3 calls so far today (it's not even 10) about defending against Russian cyber ops
I'm tired of having the same call... so... here's what I've told everyone. This is the playbook you need... but it's not going to be what you think it will be.
Ready? Lets go!
1
I want to talk a little bit about Emerging Threats IDS open and pro. First the pro set is a set of curated custom made detection rules you put in your suricata or snort instance.
🔜 🧵
Just got off phone with a client. Log4j is in their network. Vendor claims patch will be available next release... which is multiple months from now.
Here's what you do if you're in this situation.
1. Keep calm. There's no need to panic.
2. Carefully read this thread.
1/?