So tired of this "wisdom" that gets repeated with little thought (or lots of marketing).
Defense in Depth post breach is literally the opposite. Look at the whole and most meaningful part of the attack chain. 🦄
this post is a lie, and the user deleted the original thread.
They claim to have solved 11 challenges; the current FLARE-ON 13 only has 9 challenges.
I don't know where he's getting "dozens of players have finished all 11 levels" from...when you can clearly see there are only 9.
Would not be surprised if they solved an old year, say FLARE-On 9, which is from 2022 and had 11 challenges...plus all the answers and write-ups already posted online...
not much effort to solve an already solved CTF.
We (@GreyNoiseIO) are seeing a range of things to include what I assess are researchers scanning for a specific web shell using a secret probably trying to identify victims. Please note there are multiple things that need to be chained together as part of the attack.
This. It has always been about the fundamentals, and the thing that has changed with AI is the risk. What would be good enough security pre-agentic is probably not today, and in reality, good enough was probably more luck than you want to admit.
Hopefully you listened when I said get your resumes ready. @GreyNoiseIO is hiring Threat Researchers who will develop and exploit first, second, and third-party access and sources to produce cyber threat intelligence that practitioners will use to detect, disrupt, and impose cost on adversaries. https://t.co/bh6V84K6SN
Long time fan of @GreyNoiseIO, who I previously looked to in order to try to solve visibility gaps no one else could. I'm excited to join the team. Read the blog linked below for a snapshot into where we will lean in first. Also, get your resumes ready.
who here works in an enterprise security team?
are you seeing direct impacts from AI enabled attackers?
Because.....
i am not...... (and by me I mean global customers + me)
Like I can see baddies using AI
but i'm not seeing in alerts/incidents or activity any real impact from AI enabled baddies...
is it just me?
I was with a buddy the other day who run an MSSP SOC and they too haven't either....
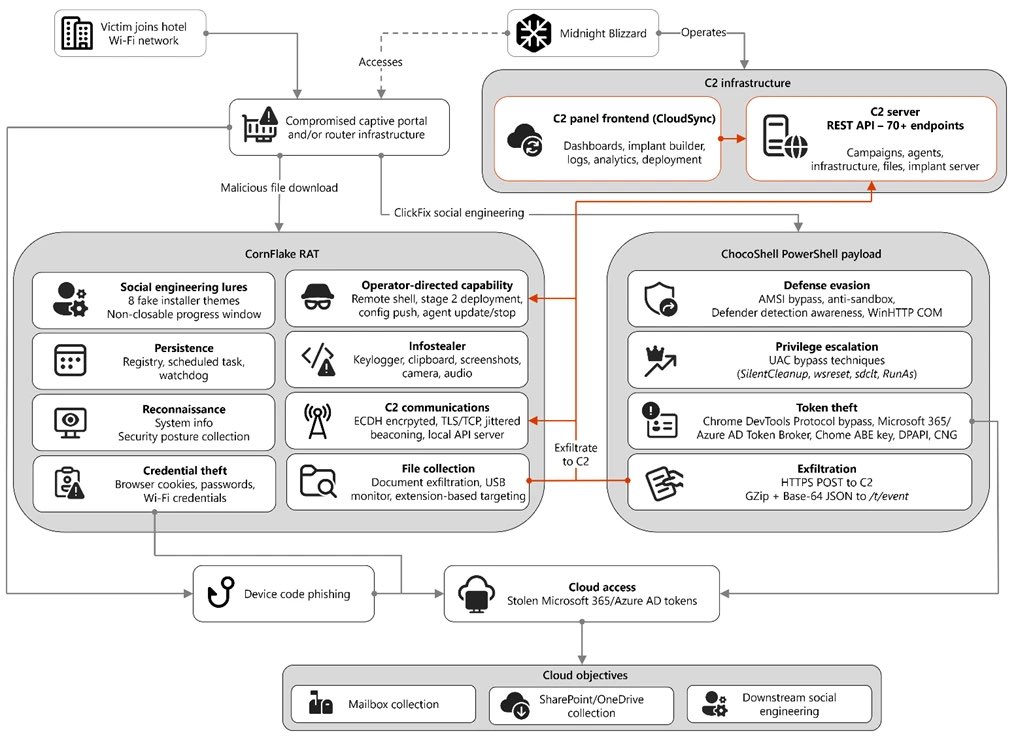
Microsoft Threat Intelligence has observed Storm-2945, a sub-cluster of Midnight Blizzard, compromising hospitality-related networks worldwide to steal credentials, access cloud environments, and deliver malware to travelers. https://t.co/bnizYidwOk
Since early May 2026, the threat actor has conducted widespread but targeted traffic manipulation attacks involving networks served by captive portals. In some cases, users were redirected through actor-controlled phishing infrastructure, while other activity led to the delivery of malware on impacted systems.
Microsoft assesses Storm-2945 to be an operational sub-cluster of Midnight Blizzard and details the malware, tradecraft, and cloud-focused techniques used throughout the campaign, including device code phishing and credential theft activity targeting travelers.
Get detections, mitigation, and hunting guidance from this Microsoft Threat Intelligence blog post.
Russian threat actor Midnight Blizzard is conducting widespread traffic manipulation attacks at hotels worldwide. Result: delivering malware or redirecting auth flows at their discretion, globally.
Since early May 2026, we saw this subcluster manipulate DNS and HTTP traffic from networks served by captive portals to redirect user traffic through actor-controlled infrastructure. We’re calling the campaign CaptiveCrunch.
“We have observed notable commonalities in the equipment and management systems used across multiple affected networks.”
We break down the malware & techniques, but the most important part is how dynamic all of it is: Midnight Blizzard is using AI to support a significant portion of these operations. They are moving and changing quickly.
Feedback welcome on the suggested mitigations: https://t.co/cVGbdQEpXQ
Help spread the word to VIPs in governments, diplomatic entities, non-governmental organizations (NGOs) in the US and Europe (probably also those traveling to Black Hat)
If your WFH desk setup doesn't cost more than a used Honda Civic, you aren't serious about your pipeline.
My ergonomic chair is built from the salvaged suspension of a 2019 Tesla Model S.
My primary monitor is a converted IMAX screen I bought from a bankrupt theater in Oakland.
When I drag a cell in Google Sheets, I physically have to rotate my entire torso. I burn 400 active calories a day just searching for the Slack icon.
Stop complaining about back pain and optimize your environment.
Something I've tweeted about in the past but that is coming to mind as I look at people being concerned with "burn out" is how often it is misattributed to fatigue from overworking. While chronic overworking can be a problem, I believe most issues with "burn out" stem from degrading morale within an organization. A key way to tell is if you take a bunch of time off, come back to work, and instantly get the feeling back. You're not fatigued; you're disillusioned with your current situation.
@SwiftOnSecurity Searched through your history to find why I thought you also needed to know that StumbleUpon is back. The world (wide web) is good again. https://t.co/ZPBTlas8e9
For the last decade, @patrickwardle has released a yearly blog post covering the most notable macOS malware. I'm a big fan and have learned so much from these so I decided to record a few videos using it as a learning resource. Here's part 1:
https://t.co/2UoAIJUeDW
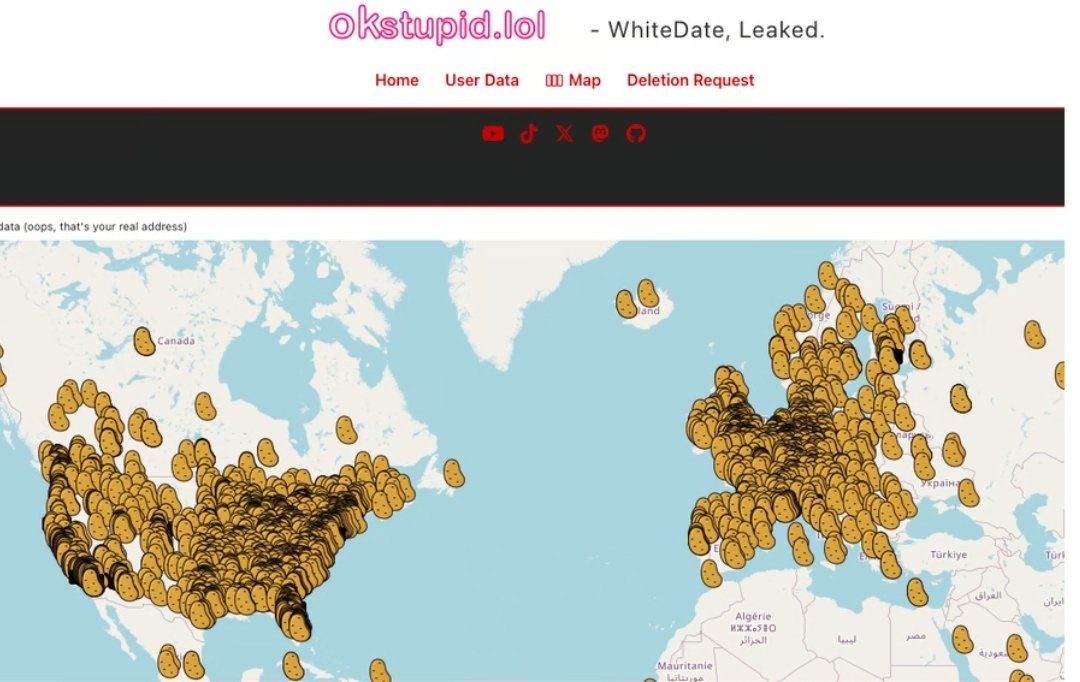
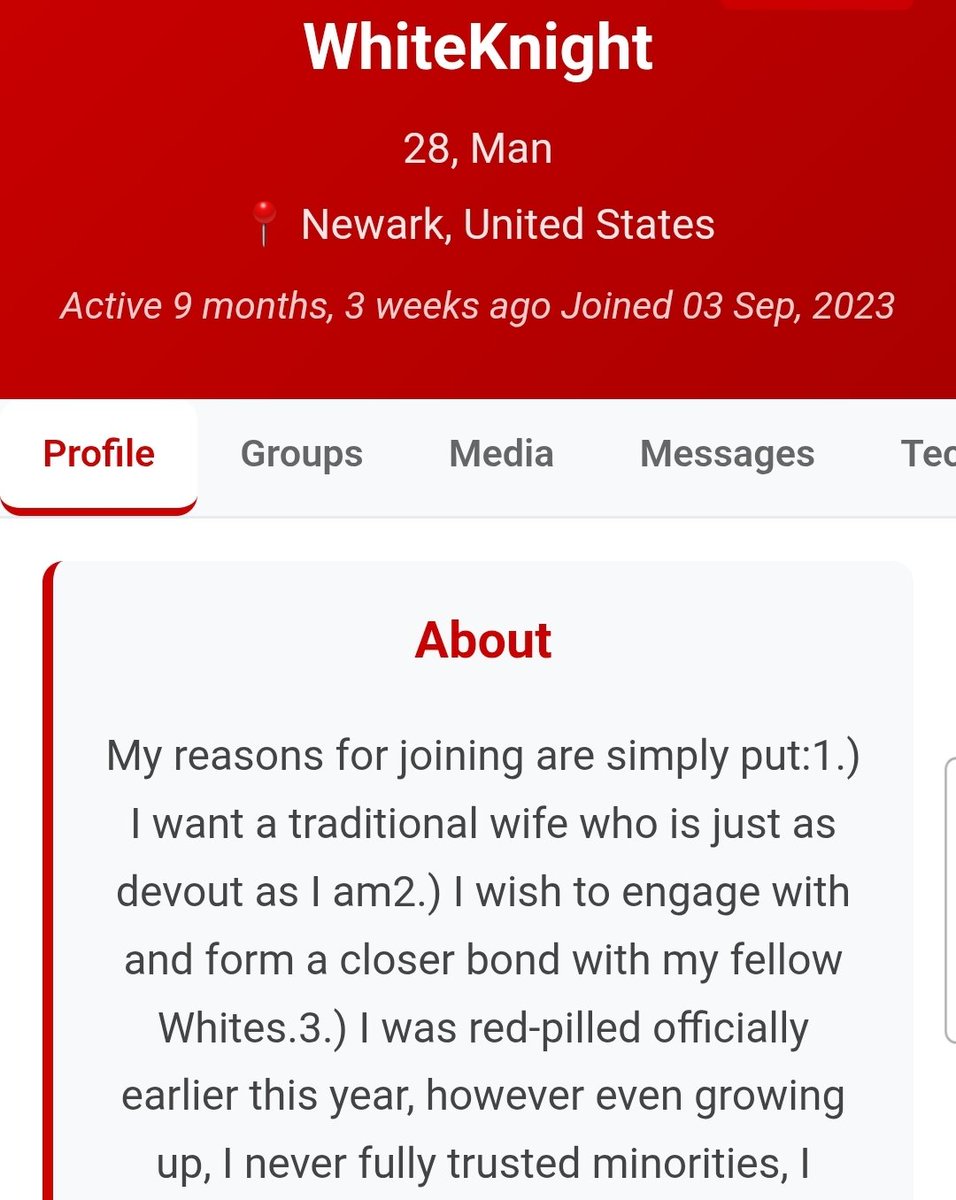
An investigative journalist infiltrated a white supremacist dating site & made them fall in love with an AI.
She created a website with over 8k profiles and placed them on a map, exposing users from very different regions of the world.
You can click your city to see them 🧵