#k4m1ll0#hacking#hacker#newhomepage
The purpose of my website has constantly changed in recent years. It was long overdue for a change.
https://t.co/c6MjKRVHYF
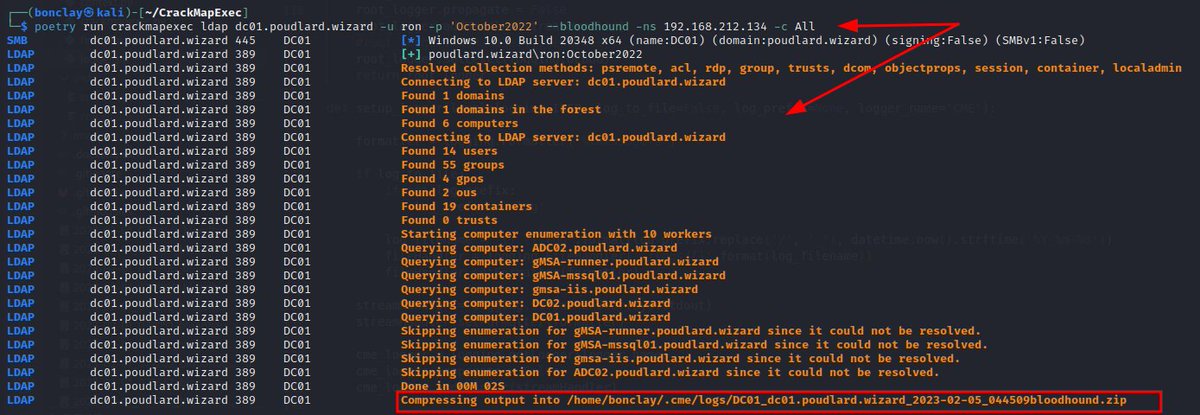
Bloodhound python from @_dirkjan is now integrated to CrackMapExec as a core feature 🔥
▶️ cme ldap <ip_dc> -u user -p pass --bloodhound
Enjoy this one, more juicy features to come soon 💪
Pushed on @porchetta_ind thanks to the sponsors as always 🪂
CVE-2021-46122 : Tp-Link TL-WR840N EU v6.20 Firmware 0.9.1 4.17 v0001.0 Build 201124 Rel.64328n is vulnerable to Buffer Overflow via the Password reset feature.... https://t.co/Q9yyMe8dDs
I didn’t think I would touch a Pandora FMS again ... but life has a sense of humor I couldn’t sleep and I played a little bit with HTB and it was Pandora again!
https://t.co/ISZo760oXP #hackthebox#htb#cybersecurity
@gghaggard @securityaffairs@Fortinet@FortiGuardLabs These vulnerabilities are monitored by the appropriate groups. As the vulnerability became official, it was only a matter of time before someone took advantage of it.
Most router firmware is not updated. If the default password is in use then, it is game over.
The FortiGuard Labs team recently encountered a MANGA (aka Dark) campaign that’s currently being distributed in the wild targeting TP-link wireless routers. It leverages a recently post-authenticated RCE vulnerability released barely two weeks prior. https://t.co/cYbTwCs2pf