@juliafmorgado I get your point but completely disagree security is everyone responsibility too, and that doesnt mean a company shouldnt have a dedicated security team. The same can apply to SRE shared responsibility doesn’t mean dedicated expertise has no place
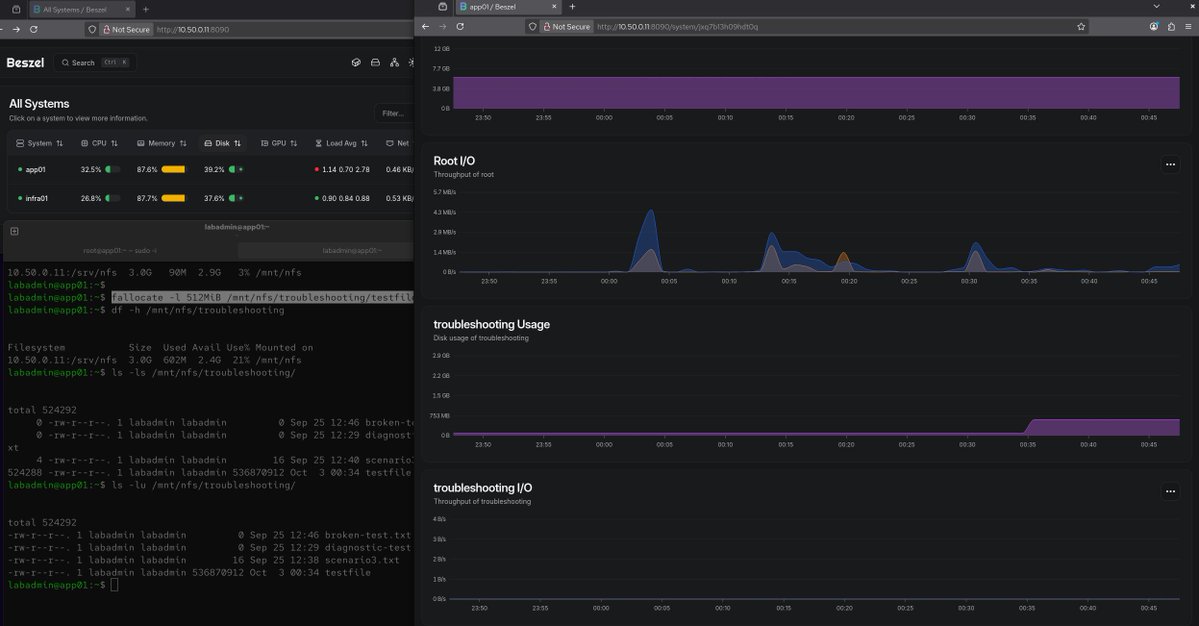
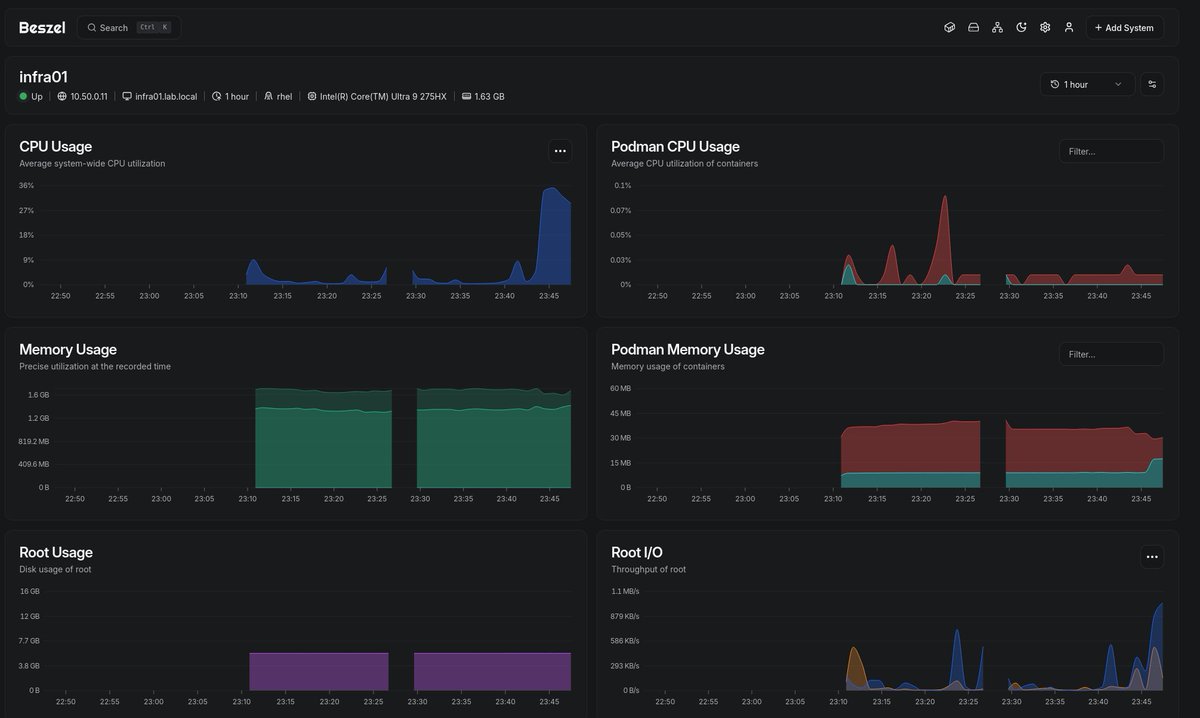
Building RHEL server & client monitoring and observability through a production style lab, introducing controlled CPU, Disk and NFS network latency failures and troubleshooting from symptoms to root cause with an SRE mindset
#SRE#Linux#RedHat#Cloud#sysadmin#podman#RHCSA
@madebygps Just do what’s interest you be it cloud,SRE, software , data engineering, AD etc. just focus on area that align with your goals and vision. Do this now or do that now just end up misleading people.
I scoped IAM narrowly and only added access when a real failure proved it was needed. No wildcard policies. The alternative is granting broad access “just in case.” That is faster on day one and a liability every day after.
Full writeup in the repo:
https://t.co/obDeYib5Qd
If you’ve ever wanted to learn more about Active Directory, now is your chance.
A list of Active Directory Domain Services modules on Microsoft Learn sorted from introductory to advanced.
Thank you Orin!
https://t.co/M0QVk3U3AE