@techspence I think if someone is to traverse into cyber, they should be curious as well they should be able to leave the thoughts that this won't work this way since cyber is all about possibilities, also in all domains including vapt, VM, dfir and all.
@techspence But I've seen IT people like I know this I'll not tell to other, cyber community and people are far better in collaboration and sharing than IT people. There might ofc be exceptions not generalising.
@FOHwithDrkabir@itsjustabhiii@kunalb11 Here comes the guy putting problem statement on users, what about when the number wasn't shared and still getting these? @FOHwithDrkabir I think you should care more about health and not give pep talk on privacy since it's not your domain as you'll always find users at fault
@kunalb11 It seems like you are there to f*ck whatsapp rather than fix or make it better. You are there for revenue and cost is paid by end user lol. Who cares, you don't ofc
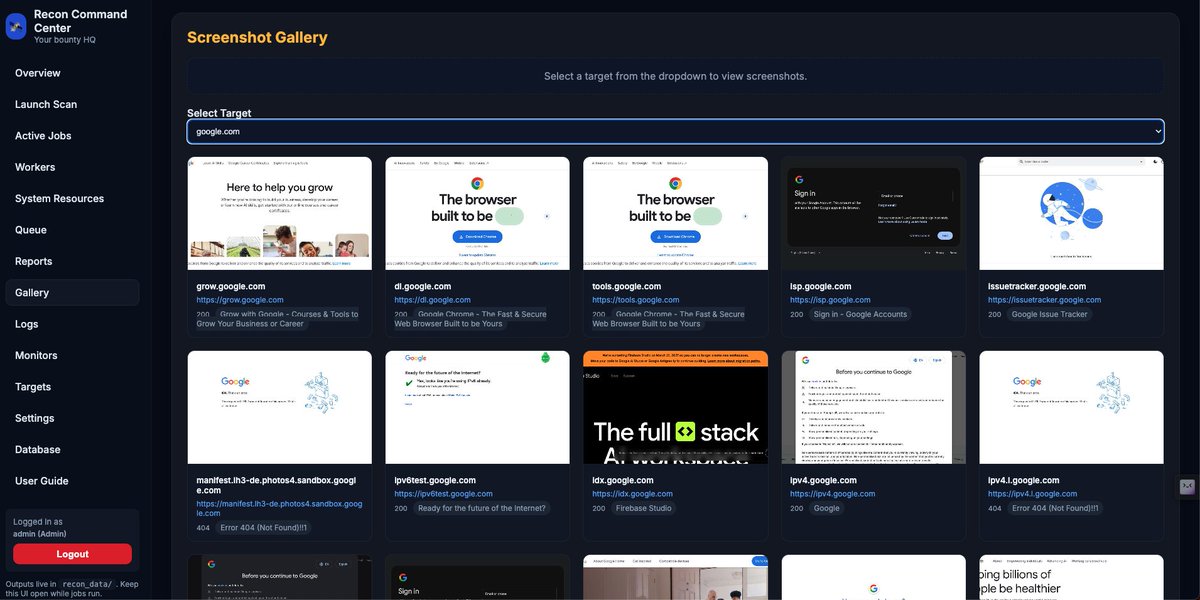
🐀 You don't need a paid recon platform.
I wired every recon tool I actually use into one free dashboard:
→ Amass, Subfinder, ffuf, httpx, nuclei, nikto — chained end to end
→ Live web UI, reports + a screenshot gallery
→ Stateful & resumable: re-run a target, it picks up where it left off
→ Docker, one command
It won't find bugs for you — it clears the recon grind so you get to hunting faster.
Free, open source. Authorized targets only 👇
https://t.co/gpt9ovEdzg
Much love <3 #bugbounty #recon #infosec
MICROSOFT OPEN-SOURCED A PII DETECTION SDK
presidio detects and anonymizes sensitive data before it ever touches your model
the problem is real: names, emails, SSNs, credit cards, medical records all flowing through LLM pipelines unfiltered
presidio stops that
▫️ detects PII in text, images, and structured data
▫️ redacts, masks, or anonymizes before it hits the model
▫️ supports NLP, regex, rule-based, and transformer detection
▫️ runs on Python, PySpark, Docker, and Kubernetes
▫️ even handles DICOM medical images
in an era of GDPR, HIPAA, and AI compliance audits, this is infrastructure not optional
https://t.co/pcEkm4mMt7
Master the art of reverse engineering and binary exploitation. Train through an immersive terminal. Progress through the belt system. 📍
Source: https://t.co/enxuULFPeF
Is future of bugbounty something like OSS-Fuzz reward.
You don’t report findings, you create a methodology. And agents use your methodology. If it finds bugs, you get paid.
https://t.co/rnygOwhd82
Next up in our series on Android and authentication 🤖 🔒:
Learn how the FIDO Alliance's Hybrid protocol has been expanded beyond CTAP messages to also support generic JSON, and which new use cases this extended approach enables.
https://t.co/4tU938BOcT
I’ve been a security engineer for a whole ass year now. Here are a few Infosec training resources shared w/ me that have been helpful over the last year in my role:
🧵1/10
We included WELA in one of our articles on Powershell for DFIR for those interested in hardening their systems with their recommendations
Learn how: https://t.co/cP54vFMbA7
#BlueTeam#DFIR@three_cube@_aircorridor
A researcher found an IDOR in Firefox allowing arbitrary account deletion via email. Initially, triage said this was unexploitable since an attacker can’t access the victim's password hash, which is required for account deletion.
But the researcher showed that for SSO users, the password hash check could be bypassed using the attacker's session. I guess the password-related DB values were None/NULL, causing the bug. Super interesting.
Always check SSO edge cases!
Full report👇
https://t.co/6WQaopkD9k