Vulnerability researchers, exploit devs and reverse engineers: before paying for another AI security course, read these two FREE posts by @ZephrFish.
This is what AI-assisted vulnerability research looks like when you build an actual pipeline around the LLM.
MCP:
8 MCP servers. 300+ tools. Patch diffing. Fuzzing. Crash triage. Ghidra. radare2. Frida. WinDbg/GDB. RAG. Proxmox. Exploit dev. CVE/disclosure workflows.
https://t.co/R98PxJUM0c
Harness:
Agent orchestration. Model routing. Persistent state. Scoped context. Validation gates. Knowledge reuse. Verification. Less token waste.
https://t.co/ivRzHAMqED
The interesting part isn't 'AI found a bug'.
It's turning years of human vulnerability-research knowledge and tooling into a repeatable system that can assist with 0-day hunting, 1-day analysis, RE and fuzzing without blindly trusting the model.
And yes, the workflow has produced validated findings and paid for itself through bounty payouts.
FREE content. Serious rabbit hole. Bookmark both.
#VulnerabilityResearch #ReverseEngineering #AISecurity
We're lucky to have so many great folks in the hacker community creating content about the Web Security Academy!
Daniel Lowrie (@daniellowrie_) has a YouTube playlist of lab walkthroughs which you can find here.
The best part is that he doesn't just *do* the labs, he explains his thought process, so the whole thing becomes an interactive learning experience. We'd recommend following along in the labs as you go!
https://t.co/niVlkacpFg
If you're looking for some more advanced reading, @garethheyes figured out how to use CSS in emails to steal passwords. This is what platinum tier security research looks like.
https://t.co/85qHdj5dR4
Infosec tradecraft just became reusable by AI agents.
SpecterOps just open-sourced:
79 skills.
22 reusable agents.
26 plugin families.
BloodHound. Cobalt Strike. Outflank C2. Ghidra. Binary Ninja. Ghostwriter. Recon. AppSec. Code review. C2 development. Reverse engineering. Adversary simulation. Windows + macOS tradecraft.
And this is NOT just for red teamers.
Vulnerability researchers:
These workflows could accelerate code review, patch analysis, 1-day research and potentially help with 0-day discovery when paired with real research expertise.
Reverse engineers + malware analysts:
Give agents structured workflows, references and tooling instead of starting every investigation from a blank prompt.
Blue teams + detection engineers:
Study the same offensive tradecraft, emulate attacker behavior, build better detections and start asking what telemetry survives increasingly agent-assisted operations.
DFIR + threat intel:
Understand what adversaries may automate next and turn repeatable investigative knowledge into reusable workflows.
Red teamers:
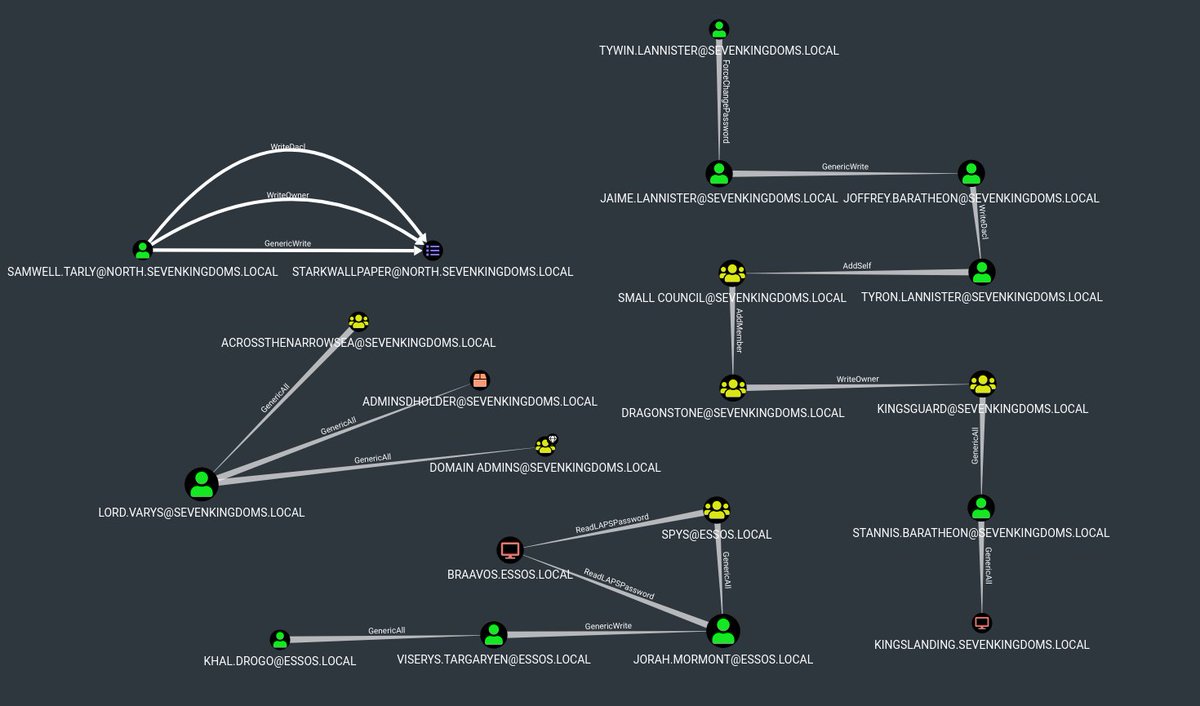
BloodHound attack paths, recon, C2 development, adversary simulation and operator tradecraft are becoming increasingly agent-assisted.
This isn't another collection of AI prompts.
It's practitioner knowledge being turned into reusable, reviewable security workflows.
Potentially useful for everyone from CTF learners and newcomers all the way to malware analysts, reverse engineers, exploit devs, red teams, blue teams and vulnerability researchers.
This is only the beginning.
@SpecterOps Skills:
https://t.co/Cj77Ir3Qlj
@OutflankNL and @kyleavery breakdown:
https://t.co/q5sEaZlp1E
#Infosec #RedTeam #ReverseEngineering
Exploiting default Active Directory permissions to create malicious, dormant DNS records for future hostnames.
This might help hijacking new machine records upon network join for subsequent Kerberos or NTLM relay attacks.
A post by Giulio Pierantoni.
Source: https://t.co/1BxP8ANonm
#redteam #blueteam
Kerberos persistence with Windows tokens and CS beacon.
A post by Romain de Reydellet (@pentest_soka)
Source: https://t.co/M4xnM22YGj
#redteam#blueteam
The team is working hard, and the second batch for the Malware Development Course 2.0 is already on the way for next week.
Another 20 modules will be released with updated content and code.
Syllabus: https://t.co/P6qCbpbTa0
0-Day Used by Lazarus in #DreamJob Campaign Against Defense Sector:
💥LPE vulnerability in Microsoft’s Afd.sys driver (CVE-2026-68820)
🧰New tools, including #Troy backdoor
🌍Compromised Roundcube servers (CVE-2025-49113) as infrastructure
Read More :
https://t.co/GDI2Ze7CRH