The TL;DR of what Anthropic just said:
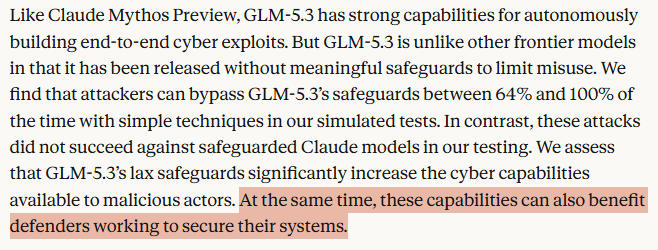
1.) GLM-5.3 is as good as Mythos for exploit development.
2.) Unlike Claude, GLM-5.3 gives you the results you pay for.
3.) Governments should ban AI models which are as good as theirs but are not made by them.
The funniest part is how Anthropic admitted self-reflectively that the lack of guardrails may actually be benefiting the defenders working to secure their systems. 🤪
Something they never wanted to allow, because of possible misuse.
I don't get it, but I feel Anthropic should at least put a note at the very bottom if they are doing paid advertising to promote GLM-5.3. 😜
Source:
https://t.co/IxhLSijYf8
Build the ultimate Windows kernel debugging setup! Automated VMs, ret-sync with IDA/Ghidra, and source-level kernel debugging. Your exploit lab for Cedric Halbronn (@saidelike)'s classes awaits! Debuggers 3011: Advanced WinDbg https://t.co/6SFhe8yPHg
I mean, I'm tired of being right..
yes CyberKimi is the best obliterated model in the space, fine tuned for cyber, already proven to perform better than Kimi K3 (matter of fact, better than any other open weight model)
more here: https://t.co/8uqVoHJBb3
After I removed the safety guardrails from a powerful open-source model, it found vulnerabilities in my household devices and hacked into a PC. But it also told me how to make everything a lot more secure. https://t.co/tQ4dpBIwji
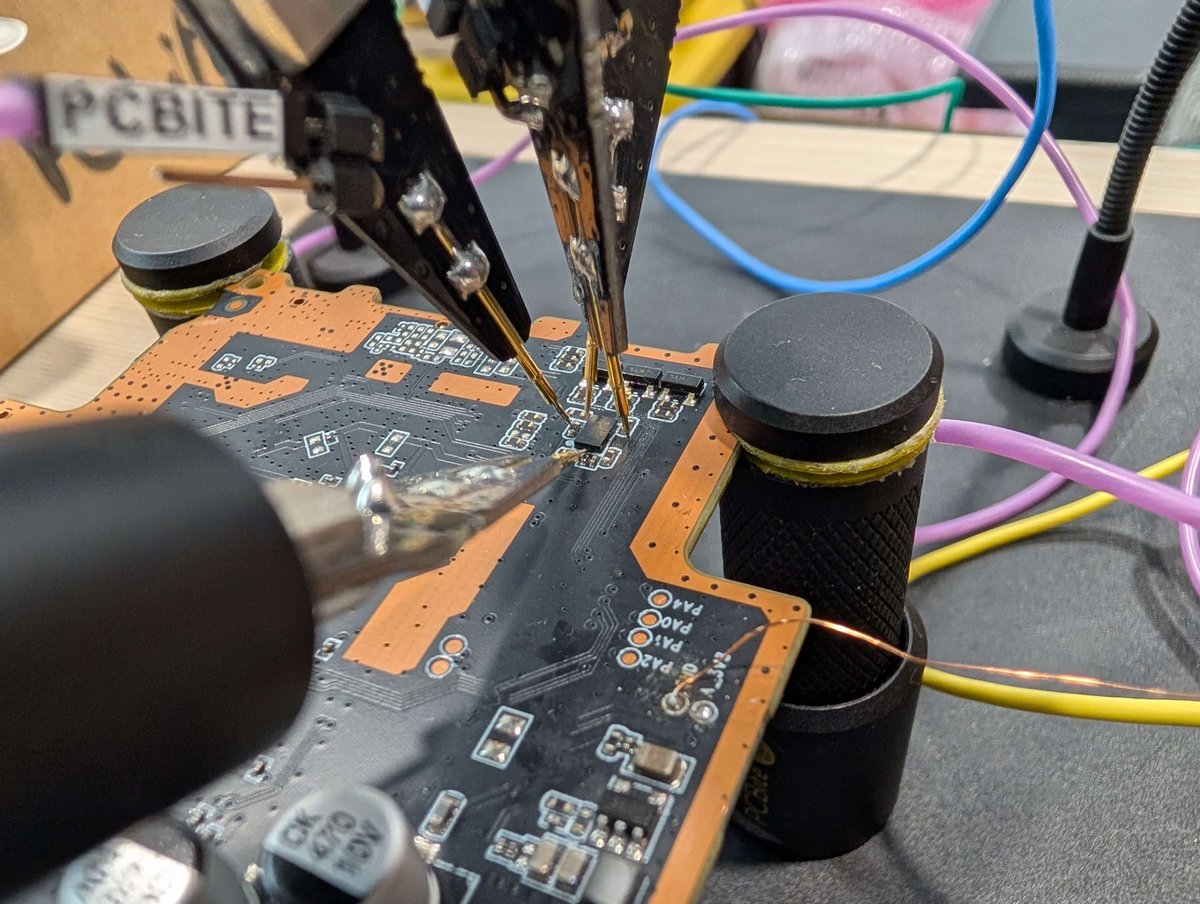
I built an operating system just for reverse engineering CPUs.
We used it to poke around the branch predictors on Apple Silicon and found some cool stuff (including Phantom fetches!).
See what we found here: https://t.co/eN0PXNusNG
You may not want to believe it but it doesn’t make it any less true. You absolutely can defend Active Directory. Start by doing this:
Part 1 - Disabling NTLMv1
Part 2 - Removing SMBv1
Part 3 - Enforcing LDAP Signing
Part 4 - Enforcing AES for Kerberos
Part 5 - Enforcing LDAP Channel Binding
Part 6 - Enforcing SMB Signing
Part 7 - Implementing Least Privilege
Link to all articles 👇
https://t.co/JNDMfVqoDP
🚨Multiple remote OpenWrt 0days disclosed by Hacker House - pre-auth to full device compromise, command execution as root on millions of routers worldwide. Fixes shipping now. Here's how our inference-fuzzing methodology found them, via @TheHackersNews https://t.co/A20DfHKRz2
Regular reminder… this hardening series by Jerry Devore is super awesome. There’s no way you won’t learn things by reading these.
Part 1 - Disabling NTLMv1
Part 2 - Removing SMBv1
Part 3 - Enforcing LDAP Signing
Part 4 - Enforcing AES for Kerberos
Part 5 - Enforcing LDAP Channel Binding
Part 6 - Enforcing SMB Signing
Part 7 - Implementing Least Privilege
Link to all articles 👇
https://t.co/JNDMfVqoDP
Over 90 binary exploitation challenges with detailed writeups. From your first buffer overflow to House of Orange. All free. All open source tools.
Assembly fundamentals. Ghidra. GDB. pwntools. Stack overflows through every mitigation bypass: ASLR, PIE, NX, canaries, RELRO. ROP chains: static, dynamic, ret2csu, SROP, stack pivoting, partial overwrites. Format strings. Shellcoding.
Then heap exploitation: double frees, use-after-frees, heap grooming, fastbin attacks, tcache poisoning, unsorted bin attacks, large bin attacks, unlink exploitation. House of Spirit. House of Lore. House of Force. House of Einherjar. House of Orange.
Integer exploitation. FILE exploitation. Obfuscation and MOVfuscation. Custom architectures. Z3 and angr for symbolic execution. Automatic exploit generation.
Every challenge has a writeup walking you from being handed the binary to writing the exploit. No IDA license needed.
If you are learning binary exploitation, this is one of the most complete free courses that exists.
https://t.co/Znn6a1nsT3
Author: guyinatuxedo
Demo Reference: https://t.co/klbPRWubFp
#ExploitDevelopment #ReverseEngineering #InfoSec
"Mathematics for Computer Science" is one of the best freely available textbooks on the subject. In more than 1,000 pages, it covers mathematical proofs, logic, sets, functions, graphs, number theory, counting, recurrences, probability, and randomised algorithms.
The book is freely available under a CC BY-SA 3.0 license. It was originally developed for MIT’s Mathematics for Computer Science course, and it is suitable both as a university textbook and as a reference for self-study.
https://t.co/Aga1yf0DIo
You really should require assignment for Azure CLI, Azure PowerShell, Graph Command Line Tools, etc.
Assign a group so that only members of that group can use them, and if licensed, gate access behind PIM/Access Packages
I even have setup scripts here:
https://t.co/4d2PNP04gQ
@Darkwebcomputer I recommend blocking admins on high or medium user risk, block on high / MFA on medium or low sign-in risk
I share them as policies here:
https://t.co/survXtdhiG
Oh whoa, this Anthropic news is insane. The Commerce Department is placing both Mythos 5 and Fable 5 under the guise of US export controls, blocking access outside the US and foreign persons in the US.
A little preview of my ContinuumCon talk, which is today at 1:30pm eastern.
Episode 184 | Active Directory Isn't Dead. It's Just Undefended
https://t.co/rq0BxE4JRZ
**NEW** BHIS | Blog
A fake badge. A held door. A few assumptions. That’s all it can take to bypass physical security.
The Art of the Badge: A Hard Truth About Physical Security
by: Robert Boettger | Guest Author
Published: 06/10/2026
Learn more: https://t.co/ZcQ7cICxCv
Wanna watch AI write an exploit with a power level over 9000? Check out the latest video where I guide you through a binary exploitation challenge and even have ChatGPT write out the exploit... so technically my hands are clean 🤓
Check out in the latest video below:
https://t.co/20voTGRmhg