Traditional security verifies who you're connecting to. mTLS verifies who's connecting too.
With Mutual TLS, both sides prove identity before any application data is exchanged. The client verifies the server. The server verifies the client. No certificate, no connection.
With MonoCloud, tokens issued through mTLS are cryptographically bound to the client certificate. Stealing the token alone is not enough. Without the matching private key, it becomes useless.
Pair that with OCSP-based certificate validation and support for AWS Private CA, Google Cloud CAS, HashiCorp Vault, or your own PKI, and identity gets enforced at the connection level, not just during login.
👉 Explore mTLS on MonoCloud at https://t.co/A0joEXMSUz
#Authentication #MTLS #Security #Identity
Passwords are not going away overnight. But the direction is clear.
Passkeys and FIDO2 are live standards with widespread platform support. Early adopters are already reporting better security and higher user satisfaction than traditional password systems. SSO with MFA is the bridge getting organizations there.
The teams building on modern authentication foundations now will not have to rebuild from scratch when passwordless becomes the norm. The infrastructure, the protocols, the user behavior transfers.
MonoCloud is built for where authentication is going. Passkeys, magic links, social login, API protection, and audit logging. Ready today, designed for what comes next.
👉 Sign up free at https://t.co/A0joEXMSUz
#Auth #Authentication #DeveloperTools #SSO #FIDO2 #SaaS
I've built authentication systems 4 times.
Not because I enjoy auth.
Because every time I needed magic links, OTPs, or passwordless login, the options were:
- Expensive
- Locked behind sales calls
- Painfully documented
So I kept building it myself.
The 4th time became MonoCloud.
Now flying to Singapore for Authenticate APAC 2026 to talk about the problem I've spent years trying to solve.
#Passkeys #Authentication #Passwordless #Authenticate2026
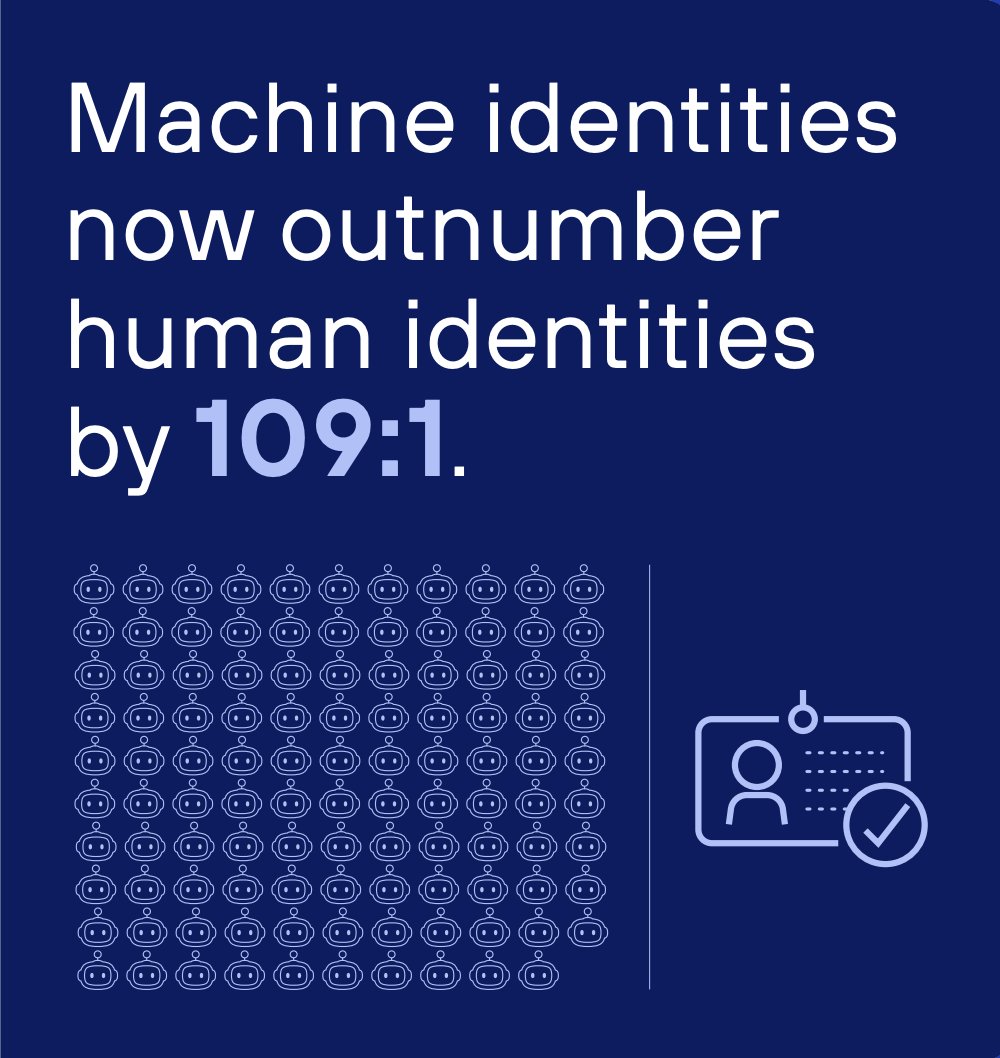
Machine identities now outnumber humans 109 to 1.
Your auth infrastructure was built for the 1.
Every agent calling an API, every service talking to another service, every automated workflow running at 3am needs credentials. It does not have a phone. It cannot approve a push notification. And the static API keys most teams hand to agents were never designed for this.
Most organizations can tell you what their agents do. Almost none can tell you what those agents can actually access, when that access gets revoked, or which systems can inherit it downstream.
That is where the breach lives and not in a stolen password. In a token nobody remembers issuing that never expired. https://t.co/P7vSiX5XT6 was built for exactly this problem and right now it's free to use.
#morethanauth #identity #authentication #authinfrastruture #monocloudauth
Palo Alto highlighted a Bloomberry finding today: 38% of MCP servers have zero authentication.
That’s bad.
But the other 62% have a different problem.
Even when they use OAuth 2.1, they mostly authenticate the human user’s delegated consent. The AI agent making the actual tool calls is still invisible to IAM.
So you have an authorized user, an agent acting under that authorization, and no clean identity record for what the agent actually did.
I ran into the same pattern while working on device auth.
Bearer credentials granted to “the device fleet” rather than to a specific device.
No strong binding between the credential and the entity holding it.
An audit trail that says:
“device category X accessed resource Y”
instead of:
“device serial 4829-A accessed resource Y at 14:32:07 with proof abc123.”
That difference matters when something goes wrong.
You can’t revoke “the fleet.”
You can revoke a specific device if you know which one.
Same problem for agents.
You can’t govern “the agent” as a vague extension of the user session.
You need the agent to be a first-class identity principal, with scoped credentials bound to a specific task or runtime, auditable at the tool-call level.
The MCP spec is moving in this direction. Resource indicators give clients a way to explicitly identify the target MCP server for a token. Token exchange is being discussed for delegation and on-behalf-of flows.
But implementations are behind.
38% having no auth at all is a long way from where this needs to be.
#MCP #OAuth #AIagents #IdentitySecurity #IAM
If your billing API and your admin API accept the same token, they share a trust boundary. Compromise one → compromise both.
Wrote up audience-scoped APIs and 4 other patterns, with a working repo:
https://t.co/fS4mnRg8D3
#WebDev#NodeJS#APIsecurity
MonoCloud simplifies authentication and identity for modern applications.
Whether you're building a SaaS, API, mobile app, or device ecosystem, MonoCloud provides the secure infrastructure you need.
Learn more: https://t.co/3w2NvHENvN
#OAuth#Authentication#DevTools
@PhilipsLightIND why aren’t any of your hue products available in India anymore? I’m looking for the E27 & GU10 bulbs for my hub and I can’t find them in stock anywhere
@UbiquitiIndia I have an RMA which has been approved but haven’t heard from anyone from Ubiquiti. No one picks up the phone on the number posted on your site. Please help
Simplify authentication with MonoCloud — branded login pages, easy integration, and flexible identity methods give you full control. With MonoCloud, you can stop worrying about auth and start building the apps your users love!
Explore our website to learn more: https://t.co/VHpFaWwR7m
#authentication #login #saas #developers #sso #mfa #programming
Today, we're excited to announce MonoCloud! It's the authentication and identity management tool that makes it easy to secure your apps, APIs, and devices and everything in-between.
Try MonoCloud @ https://t.co/VDecH3kFBX
#monocloud#oauth#oidc#iam#authentication
@GergelyOrosz We built our startup using C# and DotNet, we use Macs, JetBrains, hosted on AWS EKS (Linux containers). Our database is MongoDB. Nothing from Microsoft. Not a dollar of ours has gone to Microsoft (other than GitHub). DotNet is not how it used to be. You have so many options now.
@davidfowl@quorralyne We built 100s of API endpoints and our entire Login UI for our Authentication-as-a-service platform using minimal APIs. https://t.co/i1q8kN7zqE @MonoCld
🚀We're Thrilled to announce the launch of MonoCloud, our Identity-as-a-Service platform. Built for developers to seamlessly integrate authentication into their applications. Join us now, its free.
#MonoCloud#LaunchDay#OAuth#OIDC#IAM
https://t.co/UKqrx2xjlB
Viking Energy Group Inc. and Camber Energy, Inc. have entered into a non-binding Letter of Intent (LoI) regarding a proposed merger.
https://t.co/BKhEn1u9nr
#oilandgas#oil#energy