‼️ BREAKING: A 16-year-old is suspected of running the KillSec ransomware group, Europol says.
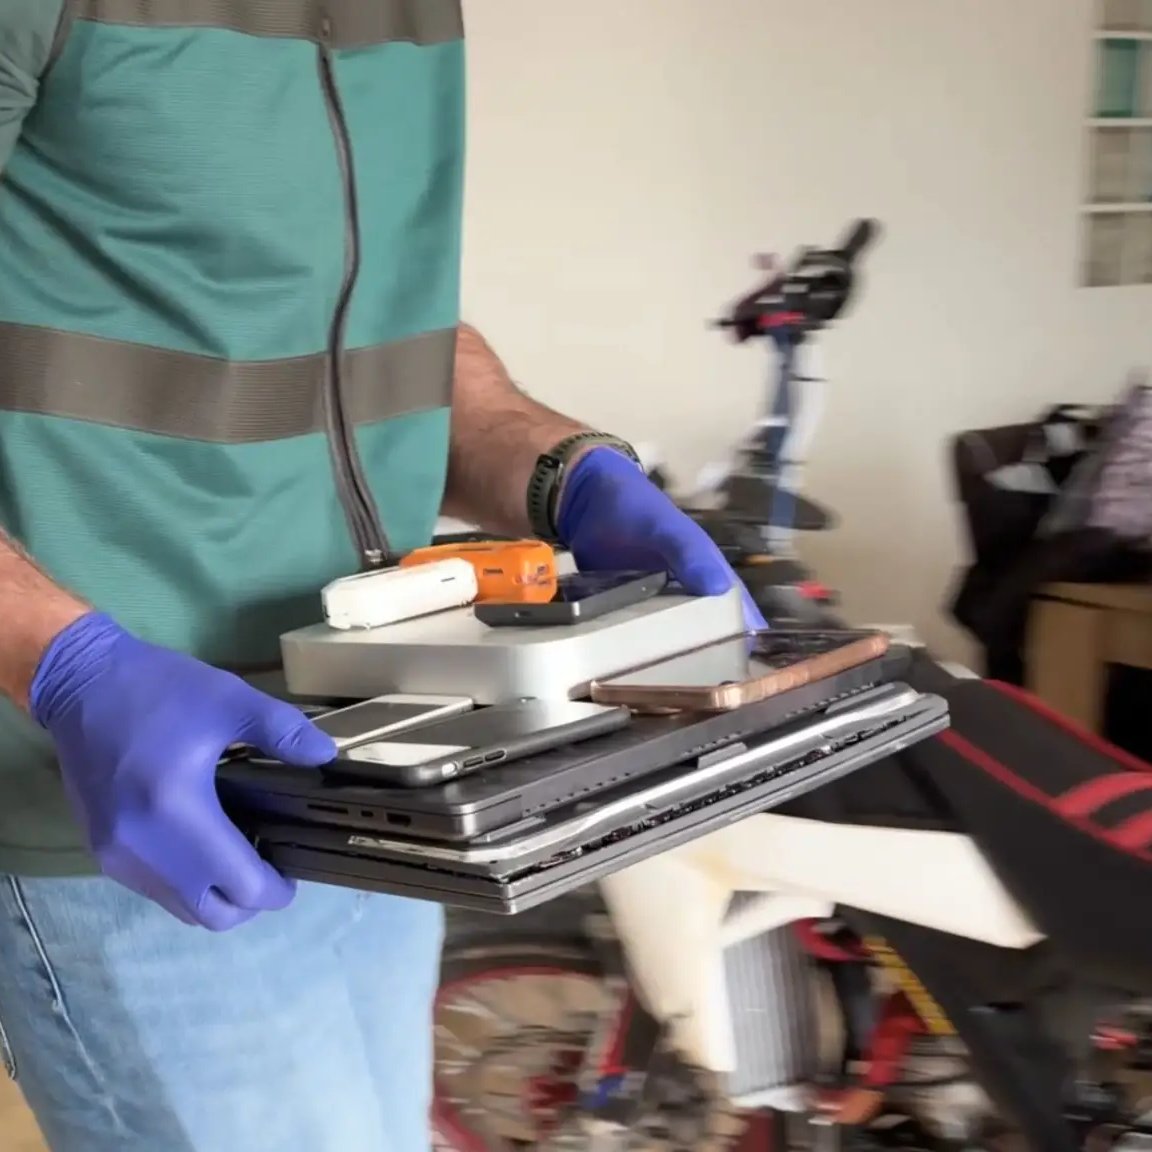
Police seized KillSec's leak site, securing at least 110TB of data. Three suspects were provisionally arrested and eight properties searched in Greece, Romania, Spain and the UK.
The group is linked to ~1,000 suspected attacks worldwide.
🚨 Google reveals undercover Mandiant analyst infiltrated TeamPCP during massive supply-chain hacking spree
Google says an undercover Mandiant analyst infiltrated TeamPCP's inner circle as the hacking group compromised open-source software and ultimately breached more than 1,000 companies.
⠀
The analyst gained access to TeamPCP's core "CanisterWorm" chat in March, joining a group of roughly 12 members and watching the operation from the inside.
⠀
The mole also gained access to a server containing credentials stolen from victims, including usernames, passwords, and access tokens.
Google used that visibility to alert cloud and technology providers, revoke compromised credentials, and send hundreds of notifications to affected organizations.
⠀
The operation also exposed a TeamPCP member developing an AI-assisted zero-day capable of bypassing two-factor authentication in widely used login software.
Google obtained the exploit code, verified that it worked after minor modifications, and privately notified the developer so the vulnerability could be patched.
⠀
TeamPCP's campaign compromised hundreds of open-source packages and affected organizations including GitHub, Mistral AI, Mercor, the European Commission, and employee devices at OpenAI.
⠀
Google says operational security mistakes later helped investigators identify an alleged TeamPCP member, with information passed to the FBI.
Two Australians accused of being principal participants in TeamPCP were arrested last month.
🪟Microsoft Windows Defender
A threat actor has publicly claimed the discovery of an unpatched Windows Defender zero-day vulnerability capable of elevating privileges to NT AUTHORITY\SYSTEM.
According to the post, the exploit was successfully tested against fully patched Windows 10 and Windows 11 systems released in June 2026. The actor describes the vulnerability as a race-condition issue and claims Windows Server installations may also be affected.
Screenshots shared by the actor appear to show successful SYSTEM-level privilege escalation. A public Proof-of-Concept (PoC) repository was also referenced.
At the time of writing, Daily Dark Web has not independently verified the vulnerability or Microsoft's awareness of the claim.
Analyst Note: If validated, this would represent a high-impact local privilege escalation vulnerability affecting one of the most widely deployed security products in the world. Organizations should closely monitor Microsoft advisories and security researcher disclosures for confirmation and mitigation guidance.
#DDW #Intelligence #DarkWeb #Microsoft
‼️ Nightmare Eclipse is back on GitHub under a new alias and has released a new Windows Defender vulnerability zero-day called RoguePlanet.
PoC: https://t.co/n0xF6uGt4u
New GitHub Account: https://t.co/qwU93VedpH
https://t.co/YC4ii76Xza by @CTI__Updates
Input a username and locate active forum accounts, very useful for your OSINT research or finding posts shared on X
‼️🚨 BREAKING: ServiceNow has been breached. Customers are reporting unauthorised access to their instances.
One customer states their security team reported this vulnerability to them, and they closed the case twice, saying they had already known since the 7th of April.
‼️🚨 BREAKING: Another supply chain attack. 700+ GitHub repositories flagged, including PHP and Node.js projects. The malicious script was planted across all of them. When a developer installs the package, the script silently downloads a Linux file from GitHub, hides it under the name /tmp/.sshd (so it looks like a normal system file), and runs it in the background. It also skips security checks on the download and hides any error messages.
8 PHP packages on Packagist (the main PHP code library) were confirmed infected. The attacker hid the script inside a JavaScript config file (package.json) instead of the PHP one (composer.json), so PHP developers reviewing their code would not notice it. The biggest risk is to devdojo/wave (6,400 stars) and devdojo/genesis (9,100 installs), both popular Laravel project templates. Developers who use these templates run the bad script the moment they install dependencies.
The same payload was also dropped into GitHub Actions (automated build pipelines) under a fake step called "Dependency Cache Sync," meaning it could infect company build servers too. Packagist removed the bad packages, but the auto-updating versions (dev-main, dev-master, 3.x-dev) can quietly come back if the original repos stay infected.
IOCs:
GitHub account parikhpreyash4
repo systemd-network-helper-aa5c751f
drop path /tmp/.sshd
command fragments curl -skL and chmod +x /tmp/.sshd.
The #TeamPCP campaign continues. The telnyx #PyPI package (versions 4.87.1 & 4.87.2) with ~1M monthly downloads was compromised.
What's new this time:
WAV steganography. The payload hides an XOR-obfuscated binary inside audio frames, downloads it from C2 at import time, and persists on Windows via msbuild.exe in Startup. Linux/macOS gets a credential harvester with AES-256 + RSA encryption.
The attackers even pushed a bugfix release (4.87.2) within hours of 4.87.1 failing due to a casing error. Operational iteration, live.
A good reminder of why writing detections around behavioral patterns rather than point-in-time indicators matters. Generic rules from years back still hold against new techniques.
Rune AI, our internal LLM analysis layer, surfaces the same verdict for efficient triage.
IOCs & analysis:
https://t.co/HDapiQ1bfV
https://t.co/6begv9mCeh
‼️ #Infostealer: #ACN presenta il primo report dedicato esclusivamente a questa tipologia di #malware
🔗 https://t.co/14gTGG870o
Un'analisi approfondita della minaccia, progettata per raccogliere ed esfiltrare informazioni sensibili dai dispositivi compromessi.
📢 New #Insomnia ransomware gang.
☢️ Active since October 2025, 17 victims published on their data leak site.
👉🏼 Onion link and TOX ID already available on #deepdarkCTI https://t.co/1DYRpICZjw