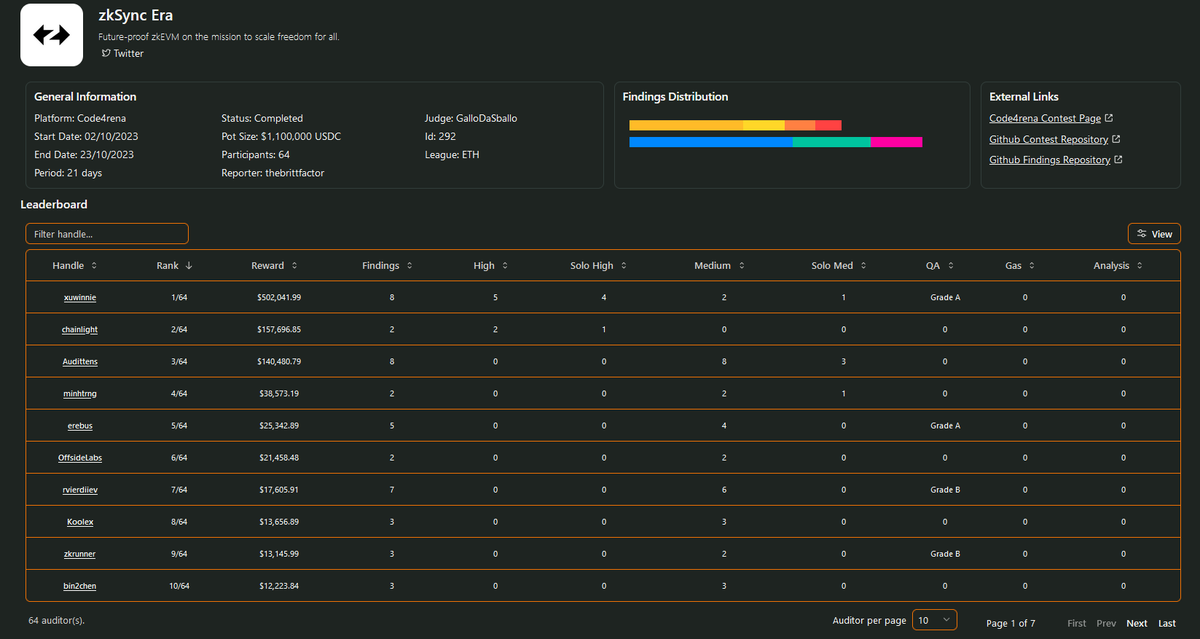
AuditHub New Functionality: Contests!
- Contest browsing
- Contest Details:
+ General Info & Findings Distribution
+ Leaderboard
+ Report
All in one place.
@skcrypto_X@KakarotZkEvm Have you tried to turn off your network, generate the proof, and then turn it back on once you've reached the submitting step ? 🤓
so now imagine all ethereum nodes where reth? unbelievable, because there is a client diversity awareness in ethereum
but guess what?
all zkEVM use revm and part of reth
all zkEVM use plonky3
all zkEVM use the same toolchain
and even some share the same source code (cc @YourBuddyConner)
5 months ago, we @KakarotZkEvm released our 100% orthogonal EVM prover and published https://t.co/jjpsYoE0O9
zk client diversity is a sine qua none condition for the beam chain
S-two unlocking real-time proving for everyday devices.
@KakarotZkEvm is building CairoM, a mobile-first ZK stack using M31 and S-two, to make client-side proving possible on laptops and smartphones.
Discover how Kakarot is leveraging S-two to bring ZK to your pocket 👇
Cairo M
New ZK-VM in 20 calendar days, from compiler to prover: 7 chads in the trenches
Mobile first
Not only a ZK-VM, also a demo app to locally prove, share and verify Cairo M proofs
exciting times to be part of @KakarotZkEvm 🥕
M is for Mobile.
Completely sick new feature for CairoM: p2p proof sharing and verification
Generate locally
Airdrop the proof
Verify elsewhere
No intermediate, no server, no cluster
Just p2p zk proof, as it should be
Wen fib war on @hyli_org ?
@guillaumeclaret@ClementWalter@worldnetwork@NoirLang I've compiled a main fib circuit (https://t.co/0q0ZJ8KQi8) and an empty main circuit, bytecodes are different.
diff in --print-acir:
+ return value indices : [_0]
+ EXPR [ (1, _0) -55 ]
Also, compiler warns that main return value, fib<N> is constrained as a constant
@guillaumeclaret@ClementWalter@worldnetwork@NoirLang There you go:
- Works on Field
- The fibonacci program is the same as this one: https://t.co/WY205ZcIfr
I believe the Noir compiler unfolds the loop as we benched similar proving time from fib(10) to fib(100k)
Not a Noir wizard yet, if there are opti tricks I'm not aware of, hmu
1/
🧠🤯 Brainfuck Blown !
Today we are releasing STWO Brainfuck ZK-VM, our research project demonstrating the power of STWO, the world’s fastest prover from @StarkWareLtd.
This is a crazy but important step on our mission to prove Ethereum in real time. See why below👇🧵